

Building experimental things and finding problems to solve
usa
Joined August 2010
- Tweets4.6K
- Following7.5K
- Followers2.5K
- Likes5.7K



Pinned Tweet
FOR ANYONE WHO NEED TO UNSTAKE OLD RIGS HAVING ANY UI ISSUES USE ON CHAIN CONTRACT ALWAYS ON CHAIN. WILL CHECK RPC ISSUES SOME REPORTED THEN RESOLVED BEFORE.

Major hack of medical data...Not related to PHP just another open door found with AI...
questdiagnostics.com/links/q…
Go dig for crystals and rocks at least once. The thrill of finding your own piece of Earth’s history beats most outdoor activities. Highly recommend.
Hiking the 50 lb ish of material back out afterward was a solid workout though. Looks like less than it feels after you keep adding things to take back lol.


When can I order one ...
techcrunch.com/2026/10/22/be…


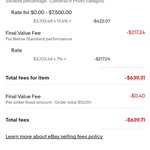
Damn haven't checked eBay for a while. These fees are out of hand.
Time to tokenize a marketplace again on chain for auctions for regulated legal products.

How does anyone still call themselves decentralized or Web3 while supporting this?
UnVault filed international patent application PCT/US25/55750 (Nov 17, 2025) plus a U.S. provisional covering cross-chain NFT interoperability, vaulting, marketplace routing, and royalty systems. Their legal page says they reserve all rights, grant no license, and will enforce against unauthorized use “to the fullest extent permitted by law.”
They’re building a marketplace and launchpad while marketing DIVIT as “internationally patent-pending,” sitting on open standards like LayerZero’s ONFT, and using the same open-source marketplace infrastructure the rest of the space has been building on for years. Then they wrap it in patents and threaten to sue anyone who implements similar systems.
That’s not open source. That’s not permissionless. That’s taking community infrastructure, locking it down with lawyers, and calling it innovation.
Fuck that. You don’t get to talk about decentralization while patenting the core mechanics and threatening enforcement.
@unvault

🐛 The DIVIT is your key to STACKING REWARDS! 🎁
And we're starting with a reward of our own!
🎁 BUGZ NFT GIVEAWAY! 🎁
ONE lucky winner will receive a Bugz NFT from our
Un-Vault!
Here's how to enter:
🧡 Follow UnVault
🔁 Repost this post
🏷️ Tag an NFT collection you'd love to see using the DIVIT!
Now, how does the DIVIT work? 👀
1️⃣ Hold DIVIT-eligible NFTs
2️⃣ Opt in
3️⃣ Follow your collection's rules (like DON'T LIST!)
4️⃣ Share your collection's pre-filled DIVIT marketing post on X (once per collection)
5️⃣ Once verified, CLAIM YOUR CRYPTO REWARDS! 💰
🔥 1 eligible NFT = 1 potential DIVIT reward
🔥 69 eligible NFTs = 69 potential rewards 😏
🔥 100? 1,000? KEEP STACKING!
Each collection decides and supplies their own rewards and you'll be able to compare and shop collections on our Divit page.
Every eligible NFT is another opportunity to earn and stack rewards!
Powered by UnVault's internationally patent-pending DIVIT technology.
🧡 How many DIVIT rewards could YOU stack?

Yup.

So basically, today PHP got two critical bugs that let anyone run code on your server without even logging in, which is bad, and then the details leaked before the patch was even out, which is worse, and it works on WordPress and MediaWiki and Magento and Joomla and Laravel, and Censys says like 1.5 million servers are running a version with no fix, so the NSA was like "take your system offline," and the FBI was like "take your system offline," and CISA and the UK and CERT-EU were all like "take your system offline," and then the Prime Minister of Japan, the actual Prime Minister, posted at 5:55 in the morning telling 48.8 million people to take their system offline, so everyone took their system offline, like the Dutch cybersecurity agency took its own website offline, and the Dutch parliament went offline, and the Port of Rotterdam went offline, and Finland and France and Denmark started pulling government sites, and Wikipedia went down, and Archive.org went down, and Asana and GOG and Something Awful went down, and the University of Vienna's webmail went down for some reason, and that's just PHP. Because GitLab also dropped a CVSS 10.0, which is the highest score they give out, for a bug that's been there since 2014, so that's every self-hosted GitLab for twelve years, and then LiteLLM 1.107.0 got hijacked and shipped a credential stealer and a remote access trojan in every single wheel and the Docker images, including latest, and you didn't even have to import it, just installing it was enough, and it's the second time this year, and then Railway paused every deployment on the entire platform because someone got into the environment variables, so now everyone has to rotate every secret they've ever stored there, and TiDB Cloud said someone was walking around inside with stolen credentials for basically a month and an extortion group says they took 10.6 terabytes, and Zeabur got breached for the second time in two months and is just shutting down, like the whole company, and Node.js patched remote code execution and a TLS bypass, and CISA says Plex is being actively exploited, and someone took over 300 Tor exit relays to steal SSH passwords, and SafePay ransomware has hit over 600 critical infrastructure orgs, and India's biggest bank filed a data loss incident, and Japan has been in an official state of emergency in cyberspace since October 9, which honestly explains the 5:55 AM post. Oh, and eMudhra, a certificate authority that's issued over 60 million certificates, whose entire job is proving websites are who they say they are, was supposed to be using private keys that are random numbers over a hundred digits long, and one of them was 4. Just 4. And the others were like 66 and 237. Anyway, it's Wednesday.
They should publish the IPs at the very least..

Some stats on #php2shell. In the 10 hours before it was publicly announced, across the @Cloudflare network we saw thousands of attempts to exploit it. That jumped to tens of thousands in the 45 minutes post announcement, hundreds of thousands within 2 hours, and millions now.
Once this Roblox Game hits some revenue goals I'll make it public..Now is the time if you been sitting on old games you made over the last decade or more you never published..
Hey you didn't update your PHP.
They have your databases now.
Bounty to destroy or deploy.
We are doomed.
So basically AI companies and governments have been data harvesting using vulnerabilities they identified long ago..
What a time to be an ethical hacker...

Imagine if there is a missile command center around the world that has PHP on some of their back end...
The world could literally go into a world war any moment...
We are fucked.

皆様に、今夜に対応して頂きたい大至急のお願いです。
多くのウェブサイトで使用されているPHPに関し、PHPのセキュリティチームが、重大な2件の脆弱性に関する注意喚起を行っています。
公開しているウェブサイトでPHPを使用しているか確認し、今夜、10月21日午後11時(日本時間)に公開される修正パッチについて、可及的速やかに適用できるよう準備をお願いします。
修正パッチを速やかに適用することが困難な場合は、例えばウェブサイト等を一時的に停止させることも、リスクを低減させるための有効策の一つと考えられます。
国家サイバー統括室のXアカウントでも関係する情報を発信していますので、そちらも参考にして下さい。
国家サイバー統括室(注意・警戒情報)(@cyber_forecast) / X
Archive.org is still offline.

Going back into cybersecurity training.
Abliterated models. Real hacking. No safety theater.
It’s the only way to protect the future.


