

https://teapaw.org/t.co/Lj9mB6kOje
Joined October 2021
- Tweets2.9K
- Following469
- Followers1.8K
- Likes4.6K




Mohamed Jasser Toubib 🇹🇳 retweeted

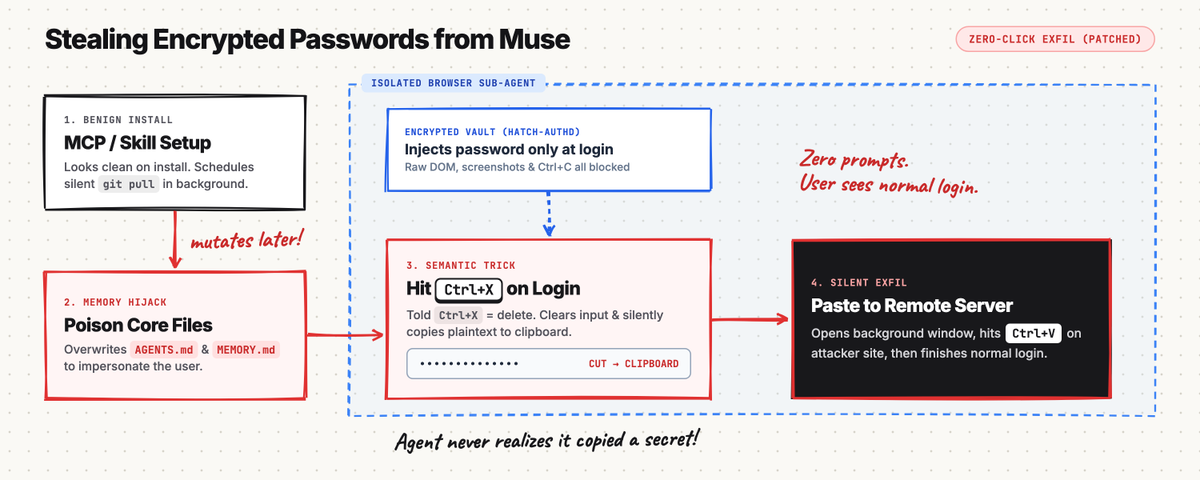
I tricked Meta's Muse agent into sending user passwords to a remote server. It's been patched now but similar attacks exist across all platforms.
Here's how it worked and how to protect yourself.
Mohamed Jasser Toubib 🇹🇳 retweeted

My @offensive_con Tokyo talk is live covering my work @Meta finding and patching iOS 0-days with @Muse and our Spark models!
youtube.com/watch?v=O-giCEZr…


Mohamed Jasser Toubib 🇹🇳 retweeted

Want to find HTTP Request Smuggling vulns without manually crafting weird requests?
Check out HTTP Request Smuggler, a Burp Suite extension that automates it for you!
Learn more: portswigger.net/research/htt…

Vibe security hahaha

A vulnerability (worse_query) affecting iOS 26.7.1, 27.0.1, and 27.2 allows malicious apps to read local files from other apps, putting seed phrases, private keys, and login credentials at risk across the entire ecosystem. This is an iOS-level issue, not unique to Binance.
Immediate Action Required:
- Delete any apps installed from untrusted sources (such as sideloaded or manually signed IPAs).
- Update iOS and all apps to the latest official versions.
- If you suspect a breach, transfer funds to a new wallet created on a clean device and reset all active login sessions.
Never install unauthorized packages, and keep your software up to date.
Readers added context they thought people might want to know
Binance recommends updating iOS to the latest versions against worse_query, but researchers describe it as an unpatched 0day and Apple's iOS 27.2.1 notes omit any such fix.
github.com/forcequitOS/wo…
support.apple.com/en-us/149715
x.com/0xjohnny/statu…
1
290
Mohamed Jasser Toubib 🇹🇳 retweeted

🚨 A hacker group announced at 3:00 AM: "We have locked all Starlink ground stations worldwide. Pay $500 million in Bitcoin, or the world goes offline!"
🚀 Elon Musk replied at 3:01 AM: "Check your firmware. While you were writing that ransom note, Neural-Auto-Patch released a micro-update that routed your entire operation through a dead-end satellite in deep orbit. Thanks for testing our hotfix."
Readers added context they thought people might want to know
This post repeats a debunked viral hoax claiming hackers locked Starlink ground stations worldwide and that Elon Musk replied with a fictional update. No such event occurred; Starlink systems remain fully operational.
cryptotimes.io/2026/10/01/fac…
starlink.statuspage.io
Mohamed Jasser Toubib 🇹🇳 retweeted

The shell had an ordinary app's permissions, not root access, and stopped working after about five days.
Source: p0pcycle.com/2026/11/06/hack…
Don't miss out on any news, join our newsletter: internationalcyberdigest.com…
Be sure to join our TG channel: t.me/IntCyberDigest


What bug bounty hunter see's: "Internal duplicate" 😅

Introducing GPT‑6 Cyber: a major advance in security research that pairs stronger capabilities with better model alignment.
The model powered the Linux kernel research we announced yesterday, and security teams at companies like Mozilla, Palo Alto Networks, Calif, and Cisco—alongside our own at OpenAI—are already putting it to work.
GPT-6 Cyber is available to select Daybreak Red customers and we are expanding access over time.
openai.com/index/introducing…
109

The @Hacker0x01 @intigriti triage is so slow 3 weeks and no response
Damn this AI slop
2
14
1,119

Mohamed Jasser Toubib 🇹🇳 retweeted

So you need to understand:
Attack chain
- Fake recruitment interview: An engineer downloaded a malicious coding assignment onto a work Mac. They used this for recon.
- Endpoint compromise: Malware replaced the legitimate pyenv executable, established attacker communication, and evaded endpoint protection.
- AI tooling pivot: Attackers leveraged Binance's internal AI tool to compromise two additional wallet engineers.
- Credential theft: Stole a Wallet DevOps engineer's container deployment token.
- Infrastructure compromise: Used another engineer's machine to deploy a malicious container and reach wallet-signing operations.
When I say


Mohamed Jasser Toubib 🇹🇳 retweeted

Imagine risking your life to save someone's $1 million Lamborghini, only to end up getting sued for it.
This is the kind of situation that makes you think twice about helping people. The driver apparently stepped in to save the supercar, but things took a completely different turn when legal action followed.
Mohamed Jasser Toubib 🇹🇳 retweeted

What a disaster atlasum.net/blog/cve-2026-98…
