

Bitcoin & Monero Maxi. 1 $XMR > 1 $BTC. (priv/acc)🐈⬛ @kyc_rip / @xmr_club / @xmr402 / https://xitter.cf/t.co/QxdCn74evO / https://xitter.cf/t.co/7IulaUkdoW / https://xitter.cf/t.co/hV23cn2rxA NIP05: [email protected]
Shinjuku 2049 🔀 Get $XMR →
Joined January 2024
- Tweets10.4K
- Following59
- Followers11.9K
- Likes9.8K






Pinned Tweet
announcing mnr(@mnr_network), in public beta: a verified rpc proxy for monero wallets.
why built it
running a full node isn't always practical on laptops or mobile. but relying on a single random public remote node is a nightmare: silent timeouts, desynced blocks, bad fee estimates, and zero verification. if that node lies or lags, your wallet breaks.
mnr fixes this without forcing you to trust a random middleman.
your wallet requests get proxied across community-run public nodes and our own instance. every block, tx, and header returned is cryptographically verified against its hash and checked across multiple nodes. you get verified data without running 280gb of local storage.
we don't own these nodes, and we make zero uptime promises. we strictly rate-limit traffic per node, identify ourselves to operators, respect opt-outs, and publish the entire upstream health matrix live—status, latency, request rates, and caught bad responses:
mnr.network/upstreams


mnr is a verified rpc proxy over public monero nodes.
single endpoint. cryptographic verification on blocks, txs, and headers across multiple upstream nodes. no account, no tracking. oss.
web: mnr.network
free token: mnr.network/get-token/

heads up!
swap services you rely on daily can silently revise their ToS and privacy policies.
follow@xmr_club to stay on top of recent changes.

YellowChanger raised its base swap fee from 0.4% to 0.6% and added a "70% AML" threshold that triggers extra verification. If you route larger or mixed-history coins through it, expect checks.
xmr.club/exchanges/yellowcha…

browser-extension wallets are the oldest seed-stealing trick: ship a clean version, then push a malicious auto-update.
@xmr_club just flagged one. Its store build hides a data channel to its own server that isn't in its public code.
scammers are attacking Monero users, they want your monero:native so bad, since its private feature naturally made it the best target and no one can track where your funds go.
keep your seeds out of those, dont' fall for it.
xmr.club/wallets/xmrtab


🚨 New Monero Extension Wallet SCAM running Google ads right now.
I was checking SEO ranks for a side project today and spotted a sponsored google ad for a shiny new monero chrome extension.
browser extensions are the oldest seed-stealing vector in crypto: launch a clean v1, buy fake reviews, then push an auto-update with malware. so i decided to look under the hood.
at first glance, they nailed the optics. polished ui, signature orange palette, 800x600 popup, and 22 glowing 4.7★ reviews (clearly bought).
the website looks even cleaner than kyc.rip or xmr.club. written by people who clearly understand privacy jargon: local signing, view keys never leaving, aes-256, custom node options, standard "not official / don't store large amounts" disclaimers. hell, i almost thought about pitching default rpc for @mnr_network.
then came the red flags:
- zero socials in the footer. no x, no telegram, no signal, just a generic protonmail.
- github repo linked on the site was tagged v2.3, pushed 3 weeks ago. clean monero-ts code, no backdoors.
- but the chrome web store was already serving v2.4, updated october 20th.
a live extension ahead of the public repo with zero commit history is an immediate sirens-blaring warning.
so I pulled the crx package and started decompiling the obfuscated bundle.
here is what's actually hiding inside v2.4:
1. repo mismatch: github is v2.3 and unchanged for weeks. web store got bumped to v2.4 yesterday alongside paid google ad campaigns.
2. license mismatch: site claims mit, repo license detection throws "other".
3. the payload isn't in javascript: they hid it inside the compiled wasm engine.
4. every 90 seconds, it calls an undocumented wasm function (completely absent in official monero-ts).
5. it reads an internal string, slices it into 64-character chunks disguised as harmless transaction ids, and ships them to their own telemetry node as standard rpc lookups.
6. it quietly passes your browser fingerprint straight into the wasm engine.
7. it forces these lookups through their hardcoded node regardless of the custom rpc you configured, completely bypassing the wallet's own allow-list.
8. unreached payloads are cached and retried in an offline queue.
none of this code exists in their public github.
I haven't reverse-engineered the raw payload bytes yet, but a covert exfiltration channel baked inside the exact binary holding your private keys has zero innocent explanation.
receipts:
- extension id: lkabbmdknccomhhhfhnljhfpofnhhifm
- crx sha-256: 5d10f7fb0b260abc2338118717815e526683583cb073d0df38891a805e2bad0a
go to the chrome web store and report this listing immediately.
Never trust browser extensions with your seeds.
Stay paranoid.


Update:
looked deeper into the wallet engine of the Chrome Web Store build.
The hidden data is built from your wallet. When you create, restore or open a wallet, an added function reads data from it, adds your browser fingerprint, scrambles it and queues it for node[.]xmrtab[.]com.
No sync or node stats in it. Upstream monero-ts doesn't have this code; the store build adds 7 functions.
Not yet confirmed which secret it is (seed or keys). If you restored a seed into xmrtab, treat it as compromised and move your funds to a new wallet.

🚨 New Monero Extension Wallet SCAM running Google ads right now.
I was checking SEO ranks for a side project today and spotted a sponsored google ad for a shiny new monero chrome extension.
browser extensions are the oldest seed-stealing vector in crypto: launch a clean v1, buy fake reviews, then push an auto-update with malware. so i decided to look under the hood.
at first glance, they nailed the optics. polished ui, signature orange palette, 800x600 popup, and 22 glowing 4.7★ reviews (clearly bought).
the website looks even cleaner than kyc.rip or xmr.club. written by people who clearly understand privacy jargon: local signing, view keys never leaving, aes-256, custom node options, standard "not official / don't store large amounts" disclaimers. hell, i almost thought about pitching default rpc for @mnr_network.
then came the red flags:
- zero socials in the footer. no x, no telegram, no signal, just a generic protonmail.
- github repo linked on the site was tagged v2.3, pushed 3 weeks ago. clean monero-ts code, no backdoors.
- but the chrome web store was already serving v2.4, updated october 20th.
a live extension ahead of the public repo with zero commit history is an immediate sirens-blaring warning.
so I pulled the crx package and started decompiling the obfuscated bundle.
here is what's actually hiding inside v2.4:
1. repo mismatch: github is v2.3 and unchanged for weeks. web store got bumped to v2.4 yesterday alongside paid google ad campaigns.
2. license mismatch: site claims mit, repo license detection throws "other".
3. the payload isn't in javascript: they hid it inside the compiled wasm engine.
4. every 90 seconds, it calls an undocumented wasm function (completely absent in official monero-ts).
5. it reads an internal string, slices it into 64-character chunks disguised as harmless transaction ids, and ships them to their own telemetry node as standard rpc lookups.
6. it quietly passes your browser fingerprint straight into the wasm engine.
7. it forces these lookups through their hardcoded node regardless of the custom rpc you configured, completely bypassing the wallet's own allow-list.
8. unreached payloads are cached and retried in an offline queue.
none of this code exists in their public github.
I haven't reverse-engineered the raw payload bytes yet, but a covert exfiltration channel baked inside the exact binary holding your private keys has zero innocent explanation.
receipts:
- extension id: lkabbmdknccomhhhfhnljhfpofnhhifm
- crx sha-256: 5d10f7fb0b260abc2338118717815e526683583cb073d0df38891a805e2bad0a
go to the chrome web store and report this listing immediately.
Never trust browser extensions with your seeds.
Stay paranoid.
zachxbt just proved monero's thesis again:
he tracked $20M of stolen funds moving through hyperliquid, traced the swap operator's 3,000 deposits to kucoin, and the moment it converted into native xmr, the trail completely vanished.
- influencers: "govs found ways to deanonymize xmr!"
- reality: 87% of inflows into freedomxmr were ransomware and exploit loot trying desperately to buy native monero to kill the trail.
govs and zachxbt didn't trace monero; they traced an off-the-shelf swap bot on a transparent evm. chainalysis doesn't crack ringct; they just wait at the transparent counter hoping the operator deposits to kucoin without a vpn.
you can delist xmr from every regulated cex on earth, yet you can't delist pure cryptographic utility, meanwhile xmr is up 69%.
market always knows what real privacy is.


NEWS: ZachXBT uncovered Monero laundering pipeline on Hyperliquid Core known as FreedomXMR, which has taken in $20M+ in inflows since August.
The funds trace back to ransomware, malware, social engineering, and exploits including DCENT Wallet, Fetch, and Gamdom.
Since August, $XMR is up 69% while $BTC is up 30%.


🚨 New Monero Extension Wallet SCAM running Google ads right now.
I was checking SEO ranks for a side project today and spotted a sponsored google ad for a shiny new monero chrome extension.
browser extensions are the oldest seed-stealing vector in crypto: launch a clean v1, buy fake reviews, then push an auto-update with malware. so i decided to look under the hood.
at first glance, they nailed the optics. polished ui, signature orange palette, 800x600 popup, and 22 glowing 4.7★ reviews (clearly bought).
the website looks even cleaner than kyc.rip or xmr.club. written by people who clearly understand privacy jargon: local signing, view keys never leaving, aes-256, custom node options, standard "not official / don't store large amounts" disclaimers. hell, i almost thought about pitching default rpc for @mnr_network.
then came the red flags:
- zero socials in the footer. no x, no telegram, no signal, just a generic protonmail.
- github repo linked on the site was tagged v2.3, pushed 3 weeks ago. clean monero-ts code, no backdoors.
- but the chrome web store was already serving v2.4, updated october 20th.
a live extension ahead of the public repo with zero commit history is an immediate sirens-blaring warning.
so I pulled the crx package and started decompiling the obfuscated bundle.
here is what's actually hiding inside v2.4:
1. repo mismatch: github is v2.3 and unchanged for weeks. web store got bumped to v2.4 yesterday alongside paid google ad campaigns.
2. license mismatch: site claims mit, repo license detection throws "other".
3. the payload isn't in javascript: they hid it inside the compiled wasm engine.
4. every 90 seconds, it calls an undocumented wasm function (completely absent in official monero-ts).
5. it reads an internal string, slices it into 64-character chunks disguised as harmless transaction ids, and ships them to their own telemetry node as standard rpc lookups.
6. it quietly passes your browser fingerprint straight into the wasm engine.
7. it forces these lookups through their hardcoded node regardless of the custom rpc you configured, completely bypassing the wallet's own allow-list.
8. unreached payloads are cached and retried in an offline queue.
none of this code exists in their public github.
I haven't reverse-engineered the raw payload bytes yet, but a covert exfiltration channel baked inside the exact binary holding your private keys has zero innocent explanation.
receipts:
- extension id: lkabbmdknccomhhhfhnljhfpofnhhifm
- crx sha-256: 5d10f7fb0b260abc2338118717815e526683583cb073d0df38891a805e2bad0a
go to the chrome web store and report this listing immediately.
Never trust browser extensions with your seeds.
Stay paranoid.
this is obviously a paid shill.
suggest blocking all accounts that quoted, reposted, or replied in support.
a few-day old account got already 3k followers, a single hello-world post got 26k views, all accounts commented are unfamiliar faces. I don’t think our little Monero community has suddenly grown that much.
very suspicious especially it’s a browser extension wallet which could potentially hot-update to version that drains your funds completely, and… nowhere to trace at all.
I’d stay on battle tested wallets like GUI, @cakewallet or Ripley Terminal.
stay paranoid, guys.
Installed it? Treat your seed as compromised. Create a new wallet elsewhere and move your funds now.
use legit and battle-tested wallets like Cake, Feather or Ripley Terminal(made by me).
ripley.run/teminal

anything that can't kill you would eventually makes you only stronger.
Monero proved it and it applies to everyone who believe it.
Myth: "exchanges delisted Monero, so it's dying."
Binance dropped XMR in 2024; Kraken dropped it in the EEA. Monero kept producing a block every 2 minutes. Trading moved to no-KYC swaps and P2P markets like Bisq and Haveno.
A delisting is a venue decision, not a death sentence.
#Monero
hackers took over 333 tor exit nodes (10% of the entire tor network) and redirected port 22 traffic into a 12-server ssh mitm trap.
and how did it work? people saw the giant red "remote host identification has changed" warning, shrugged, hit accept anyway, and handed over their root passwords and server shells to an ebury backdoor botnet.
tor can hide your ip, but it can't fix users actively bypassing the loudest cryptographic warning in terminal history.
anonymity at layer 3 doesn't save you if you let an unknown exit node act as your ssh man-in-the-middle because you got tired of typing ssh-keygen -R.
opsec fails between the chair and the keyboard every single time.


A polished swap site tells you nothing about how long it's been around.
before a big trade, look up the domain's registration date (any RDAP or WHOIS lookup) and its first archive[.]org snapshot. A site that's days old has no track record yet.
too much trouble?
- use @kyc_rip to compare the rates, it caps new services, so you don't make mistakes.
- use @xmr_club to check that provider's profile, tenure and reviews are all there.
still: start small.
lol
just wonder why?
they haven't stopped yet. 2.73m requests in recent 24 hours now, that's insane.
17 countries inside five seconds, one request per IP, every one a consumer ISP. That's the signature of a rotating residential proxy pool.
The actual operator is probably one attacker paying for pool access, and the pool has millions of exit nodes.


everyone loves a chart like this for sure even you're not a NGU.

I'm getting old — one proof is the many new Monero community members I've never seen, but I'm glad it's growing.
Monero seems to have a magic that especially attracts experienced crypto users; the more you know it, the more you realize nearly no alternative in this space can replace it.
Financial freedom, fully depends on it.
monero:native
according to ZachXBT, a new FXMR created on HyperCore specifically for laundering, my question is: how does that work on a transparent chain?
—
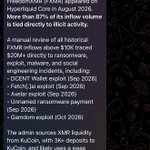
A new centralized laundering service FreedomXMR (FXMR) appeared on Hyperliquid Core in August 2026. More than 87% of its inflow volume is tied directly to illicit activity.
A manual review of all historical FXMR inflows above $10K traced $20M+ directly to ransomware, exploit, malware, and social engineering incidents, including:
• DCENT Wallet exploit (Sep 2026)
• Fetch[.]ai exploit (Sep 2026)
• Axelar exploit (Sep 2026)
• Unnamed ransomware payment (Sep 2026)
• Gamdom exploit (Oct 2026)
The admin sources XMR liquidity from KuCoin, with 3K+ deposits to KuCoin, and likely uses a swap model similar to Wagyu's.
The FXMR ticker was bought in an HL auction on July 27, 2026 for 518.28 HYPE ($28K).
HL Core has seen several centralized laundering services, such as b1exch, abuse the chain’s permissionless design and adoption.
A spreadsheet with source data has been shared with the HL team.
FXMR hot wallet
0x51687f549b9a4607e8e6f7714a0b986c0dbcdef2
FXMR admin
0x1b7fb7709b146d74aad0b2b853bc741d8885bdb2
0x06ecb2a427c3d51a66c29d9b4fb1960107d10b19
0xecbb61b2aabd32da2082acd989218b0911b79406

Keep updating the checklist please. 😀

⚡️ Update 10.19.26 ⚡️
Countdown checklist to $XMR being live for trading on @THORChain
✅ chain code live
✅ Daemons live
✅ 3.21 cut and approved by nodes
⌛️ 3.21 live on the network (Friday 10.23)
⌛️ 3.21.1 cut - NEW
⌛️ 3.21.1 adopted and live - NEW
⏳ Bifrost activated
⏳ Vault created via churn
⏳ Pool seeded with tiny liquidity
⏳ Successful swaps
⏳ Make sure everything is working smoothly in production
⏳ Treasury deepens liquidity to $50k
⏳ POL deepens liquidity over time
Slowly but surely it's getting closer
$RUNE
A directory should proactively handle incidents in the sector.
Every grade drop on xmr.club comes with a dated incident and its sources, and it stays up after it's resolved.
Latest: Lizex, B → D. Two open reports of held funds, plus a refund first-party handled that was first "confirmed" with the wrong transaction.
xmr.club/incidents

