

🇵🇱 https://xitter.cf/t.co/HerX32NWvo 🇬🇧 https://xitter.cf/t.co/m6h4mNhOBh | Self-educated specialist: PHP, CI/CD, QA automation, Docker, Gitlab and more 😎. Member of @PHPCSFixer team 🪶.
Joined April 2022
- Tweets8.3K
- Following373
- Followers1K
- Likes7.6K





Pinned Tweet
I am excited to announce that I joined @usoftware_ as a Senior Software Engineer and will provide services for @Printify in a Developer Enablement team 🤩! Looking forward for this new, great adventure - wish me luck 🤞☺️.
blog.codito.dev/2025/07/prin…

Greg Korba 🛠️🛹 Codito retweeted

Lot of #PHP snark going around right now from folks who've either never written software, or never done it in PHP (in the last 20 years).
I've architected, designed and hand-coded copious amounts of software in Java/Spring/Hibernate, .Net/C# Entity Framework and PHP/Symfony/Doctrine, applying very similar patterns and better practices of completely stack-agnostic concepts such as:
- Test-Driven Development (and given half-day and full-day hands-on live-coding workshops at conferences worldwide)
- Onion/Hexagonal Architecture
- Domain-Driven Design
- Data Mapper ORMs
Beyond workshops, I have spoken on these topics at conferences worldwide as well.
I might argue that I am not completely devoid of clue when it comes to these stacks' capabilities.
In fact, I have hired, coached and cross-trained engineers across these 3 stacks.
And I can assure you PHP shines within these paradigms, with an extremely vibrant, mature and robust ecosystem of Application Frameworks, Security Frameworks and Tools, and Open-Source Software Components and Libraries.
PHP is not WordPress. WordPress is not PHP. If you care about quality software, PHP is a great home for you. So is Java. So is C#. So are other languages. If you suck at software you'll suck in any stack. If you're good, each stack has strengths you can play to.
NOW let's talk about security.
This vulnerability, is the very first RCE to this level in PHP's history. It was reported back in August. AI did help. A lot. (Wiz claims one researcher did in a week what would previously have taken a team months)
Previous PHP RCEs had limited attack surfaces:
- 2024 - Windows CGI Only
- 2019 - One specific nginx setup
- 2012 - CGI only
None of which applied to reasonably-better practice typical Linux + Nginx + php-fpm deployments.
This right here was ... unique, I think even across any stack. The only language-runtime equivalent to it was probably Windows IIS Code Red.
That's not to say other stacks didn't have framework-level vulnerabilities with devastating impacts, if memory needs refreshed:
Ruby — Rails CVE-2013-0156: every Rails app, default config, pre-controller, botnet-exploited. The strongest analogue in any stack.
Java — Struts 2 CVE-2017-5638 (Equifax). Log4Shell needed the app to log attacker input; Spring4Shell needed WAR-on-Tomcat + JDK 9+ + POJO binding.
Node — React2Shell CVE-2025-55182 (Dec 2025, CVSS 10, CISA KEV): default create-next-app exploitable, but Express/Fastify/Nest untouched.
.NET — MS10-070 padding oracle (2010) leaked web.config/machineKey on every ASP (dot NET) site; RCE was a derived second step. Kestrel/ASP.NET Core has never had an RCE.
Look ... let's drop the snark. LLM-driven vulnerability research and breaching frameworks are about to humble the absolute heck out of all of us. They already have.
If you think your stack is not at risk, think again.
Greg Korba 🛠️🛹 Codito retweeted
If all the govs shutting down servers for a PHP update, all the hosters & enterprises terrified by the vuln, gave $100k, or just $50k a year to the PHP Foundation, things could look very differently. Go, make your employer sponsor *today* thephp.foundation/sponsor/ #php #phpc @ThePHPF

Probably the absolutely worst part of required checks in @github is inconsistency in what UI displays & what jobs' names actually look like... It depends on whether job comes from local, raw workflow or from reusable one, so you either have "<workflow> / <job>" or just "<job>".

I just hate @github approach for required checks (configured in settings). Conditional checks is one thing, but for repositories managed with #IaaC (#Terraform) this leads to code split, as required checks have to be defined outside of the repo where they run. Easy to forget.
Great discussion and problem/advantage storming about teaching juniors in AI times with @ziobrando at @KanDDDinsky 😊. A lot of interesting thoughts!

I proposed discussion about Code Quality in AI-driven development at @KanDDDinsky's OpenSpace (unconference). Meet me at Einstein II room at 12:15 and share your thoughts 😊.


For next 3 days I am at Berlin, attending @KanDDDinsky conference. If you're also here and would like to talk, reach me out 😊. Happy learning! – at Berlin, Germany

I was today's years old when I found out that `shivammathur/setup-php` action did not have Release Immutability enabled - not anymore! Starting from next release, immutability will be there, so pinning action by tag won't be prone to malicious attacks 😊.
github.com/shivammathur/setu…

I was today years old when I found out that Psalm defaults to 1(!!) CPU when it detects CI environment 🤯. Basically, if you run it on Github Actions, you have to opt-in for parallelism and reduce analysis time. It's such a waste of everyone's time!
github.com/vimeo/psalm/issue…


I am going to @KanDDDinsky in Berlin for the first time this year. Who will I be able to meet there 👀?


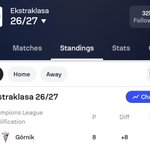
Piękny start sezonu, ale najważniejsze jest bym taki widok ujrzał po 34 kolejce 😁! To byłoby coś wspaniałego...
🤞 @GornikZabrzeSSA @Podolski10

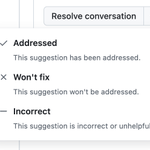
I am wondering why this really nice #GitHub feature is available only for Copilot's review comments, not for regular users' comments 🤔. I really like it, it provides meaningful feedback.


Is it only me, or the need to explicitly run `brew update` before `brew upgrade ...` is an awful DX? For example, I work with `gh` tool and I see there's a new version of it, so I run Brew upgrade, and I end up with the same version... only to call update and upgrade again 🙄.

Has anyone worked with Stacked Pull Requests in Github already 🤔? I mean the native feature (now in public beta). This is something that I've been using for years, handled manually (`rebase --onto` FTW), and I am curious what is the DX with GH's feature.
docs.github.com/en/pull-requ…


Hello Rīga, my old friend ❤️! This year the weather is soooooooo nice 😍. It's my last day here, tomorrow I fly back to Poland, so I am going to enjoy #FYUL's summer event to the fullest this evening!

But the go-karts were probably even better as we went all-in with my Polish friends 😅. I started at 3rd position and finished 1st, overtaking my friends once, and other drivers several times 🥰😁. Leading the race is really demanding, my friend sat on my tail all the time 🫨.
