

Principal @HuntressLabs | Former Detection & Response Principal @CrowdStrike | macOS Security Enthusiast
Australia
Joined May 2024
- Tweets235
- Following107
- Followers626
- Likes362






Pinned Tweet
I finally got around to blogging about this, and a separate bug (CVE-2024-44219). If you're interested in homedir TCC protections, enforcement via `sandboxd` or the sandbox kernel extension, I'd be pleased if you took a quick look!
rdowd.com/castles-made-of-sa…


I think I have figured which of my bugs was CVE-2026-112577.
I've no idea how this wasn't bundled into the TCC fixes introduced as part of CVE-2026-84589 (which itself appeared to be a culmination of several unique bugs in the framework).
Blogs coming shortly.



Ryan Dowd retweeted

Appreciate @jstrosch for the invite on the podcast! macOS malware is at an interesting place. Also, getting to talk about how reverse engineering workflows are changing with AI was fun/therapeutic. I wasn’t crying I promise. 😂

New episode of Behind the Binary is live!
🎙️Joined by @L0Psec to break down macOS security, ClickFix social engineering, InfoStealers (AMOS/MacSync), DPRK developer targeting, and the evolution of obfuscation.
Plus, we talk about how AI is shifting reverse engineering and the inevitable future state...
🎧 podcasts.apple.com/us/podcas…

Ryan Dowd retweeted

🍎🐛 I got Claude making this, maybe it's useful for others as well.
Every Apple security advisory since 2002 - parsed, indexed, charted. With links to writeups, POCs and presentations.
apple-cve.com/

Ryan Dowd retweeted

Apple just announced big changes to Full Disk Access in macOS!
When will it ship?
What will the new approval look like?
Will existing FDA approvals be affected?
What about existing MDM/PPPC profiles?
Will enterprise & security tools get different treatment from AI or other apps?

Ryan Dowd retweeted
CVE-2026-100754: ChatGPT's code-signing checks on macOS/Windows can be bypassed by (local, unprivileged) attackers, who then inherits the agent's trust:
💉 Inject prompts
👀 Read private chats
🔓 Access TCC-protected files
🍪 Steal cookies/auth tokens/browsing sessions


Security & privacy used to mean fighting malware and hackers
...now, we have to add "AI agents" to that threat model 🤖 😅
Mahalo to the @nytimes for spotlighting some of our recent ChatGPT research & bugs!
nytimes.com/2026/09/29/techn…

You have gotta love a conference run in the sun.
Only hanging at the back for the group photos, I swear! 😅
Thanks @mdowd for organising. @UnpromptedAU


A stand-out talk on the first day of @UnpromptedAU by @clearbluejar. Great insights and food for thought when it comes to finding 0day using frontier models.

It looks like these changes were reverted overnight. No official comm’s around what the initial issue was, however.
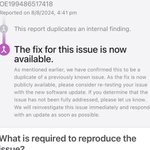
This report is long since resolved and is one of many marked a duplicate of an internal finding. A bounty was paid two years ago and CVE already issued in my name.
I hope Apple has an undo button available for the changes made to ASB overnight.


Ryan Dowd retweeted
Reminder: 🍎-security tools subscribing to ES AUTH_* events must respond before an ES deadline (~15s) or the kernel kills them ...& they stay ☠️
Privileged attacker? SIGSTOP the tool ...⏳💥😂
Mitigation (per @PeteMarkowsky) subscribe to/block signals!
docs.google.com/presentation…


Ryan Dowd retweeted

Come join our training in Budapest! As it stands we will be able to spend some quality time with the trainees, so if that's your jam there's still room left!

Our next training with @gergely_kalman will be in Budapest between the 12th and 15th of October. This is our only training in Europe for this year, and this is the only time we will teach the 4 day version of the training.
If you are looking getting into Apple vuln research then this is Your training. Although we don't do iOS here, many of the concepts we teach are applicable there as well.
macosvuln.training/


Ryan Dowd retweeted

Thrilled to announce I will be speaking in Sydney!
Hope to catch some of you out at @UnpromptedAU


Ok! The schedule is live as! Check it out: unprompted.au

Ryan Dowd retweeted

#PamStealer macOS infostealer · new JXA loader 🧐
🎭 fake CleanDev clones DevCleaner → cleandev[.]cc
⛓️ one char-code .js = whole kill-chain:
🎣 ClickFix → curl → osascript
🧬 self-decodes at runtime · Function('return') 👇 img
🕵️ gauntlet first → anti-VM · ptrace · SIP · CIS ×11
🔑 then RC4 → C2, env-keyed (cracked offline 🤷♂️)
📥 only now → stage-2 Mach-O
🥸 fake Finder[.app (real .icns) → com[.apple.finder.agent
🎬 fake "Installation failed" = already infected
📡 notification-portal[.]com
🎯 catch by @ValeryMarchive


So much knowledge and talent over 3 days.
This is going to be 🔥.
Just announced: talks for #OBTS v9 🥳
Stoked on an epic lineup of cutting-edge 🍎- security research, covering exploitation, malware, reversing, security tools, AI, & more!
Check out the full lineup:
objectivebythesea.org/v9/tal…
Which one(s) are you most looking forward to!? 🤔
