





Pinned Tweet
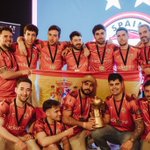
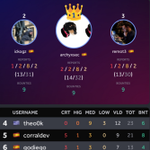
We won the @Hacker0x01 Ambassadors World Cup for second time. 🏆
🧵 This is thread about my journey, and how it all started 8 months ago when I had 0 points on HackerOne ⬇️

This is the cutest honeypot ever

honeypot, but for supermarkets 🥦
@x64gurke made a virtual grocery store, hidden in the internet to catch fridge hackers before they hack real supermarkets in France😈
⛓️💥 defrost.pizza/
3
177
remot3 retweeted

Our initial take: use GPT-6 Cyber when speed matters more than cost.
Use alternatives for wide scans where findings per dollar matters most.
I see many people complaining about duplicates recently blaming AI, but AI only brings speed. If you were hunting one-step bugs, that's the real problem. You were already getting duped before AI...it just happened at a slower pace.
2
259
remot3 retweeted

Hear from @_remot3 -- who led the building of the #php2shell exploit for XBOW -- in the latest episode of Offense Taken with @fede_k 🐘
youtube.com/watch?v=akGDXhSg…


remot3 retweeted
A newly disclosed Exim vulnerability, CVE-2026-45185 (“Dead.Letter”), highlights how a flaw in handling SMTP BDAT commands and TLS connection termination could create serious security risks in widely deployed email infrastructure.
As covered by Ravie Lakshmanan in @TheHackersNews, the vulnerability was discovered and responsibly reported by XBOW.
The flaw affects GnuTLS-based Exim builds and could enable heap corruption and potential remote code execution through BDAT message handling during TLS shutdown. Research like this reflects the depth of analysis required to uncover high-impact vulnerabilities before attackers do.
Read the full article: bit.ly/4nzv60T

remot3 retweeted
Anthropic’s Mythos raised the bar for AI vuln detection but kept it invite-only.
GPT-5.5 is OpenAI’s answer, and it’s open to all.
We had early access. Ran the benchmarks. Blackbox GPT-5.5 already beats whitebox GPT-5.
Best pentesting model we’ve tested.
Read our analysis: bit.ly/48OX7v6
Everyday I read about a new autonomous pentesting tools being released. All of them follow the same pattern. Some sort of agentic architecture with hacking tools connected and benchmarked against a vulnerable app.
Let me explain you why these systems are useless 👇
1
1
454
4. Without validation you will drain in noise.
5. Most of these tools delegate auth on the agent gambling if the test will pass it or not. Also multi-agent systems will kill eachother sessions while testing in parallel
1
61

remot3 retweeted
Most IDORs aren’t “guess the next number.” They hide in real authorization logic.
In our latest Tales from the Trace, XBOW uncovered two zero-day IDORs by reasoning through the app like a pentester, even after 403s and 502s.
The future of DAST lies in autonomous reasoning, catching the real-world access control failures scanners miss (and attackers look for): bit.ly/4kmlmpg

Hate when I am deep down on a bug after researching it for days thinking I'm a genius for reversing it just to discover another asset that reveals the entire internals
6
397
remot3 retweeted

Thanks to everyone who joined us at the @Hacker0x01 Brand Ambassadors Speed Show&Tell in Madrid, and special thanks to all who presented! 💕


remot3 retweeted

🚨 180+ vulnerabilities found.
🌍 763 hackers. 38 countries.
🏆 4 elite teams.
Adobe brought serious energy to the 2024 #AmbassadorWorldCup, working side-by-side with ethical hackers to secure products like Firefly & Lightroom.
We were proud to host → adobe.ly/4m3D1C8
#HackForGood #TogetherWeHitHarder