

opinions on anything interesting
Brazil
Joined May 2011
- Tweets11.5K
- Following2.8K
- Followers2.4K
- Likes79.3K





WΞNDΞL retweeted

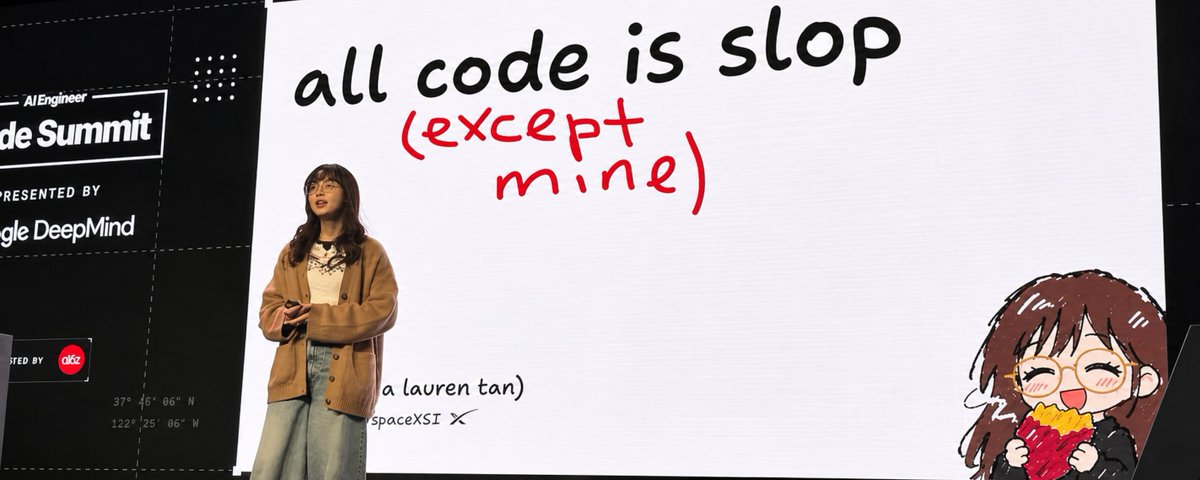
Lauren Tan from the Grok Bot team found the real reason your AI writes SLOP
She put it in 5 words on stage: “nuance tends to lead to slop”
Don’t explain the nuance to your agent, just delete it:
> Don’t let agents touch useEffect: ban it from product code, keep it only inside your framework
> Don’t leave comments that justify a quick fix: delete them and fix the root cause
> Don’t trust a "temporary" workaround: one quick fix became 183 timers in 5 weeks
> Cut your comments down to the bare minimum: her team went from 65,824 to 1,227
> Don’t let one part of the app import from another: lock it with folders, not even types can cross
> Don’t make agents handle the hard parts: hide them behind simple APIs, like their framework Dune
> Don’t add another line to AGENTS.md: turn every correction into a lint rule
The result: her team merged 11,000 PRs in October, and only 0.47% got reverted
Stop writing longer instructions for your agents
Design code where the wrong move isn’t possible
Full talk below:


WΞNDΞL retweeted

Grafana, Jenkins and Coder all send telemetry data to their makers by default, even when you host them yourself.
A list on Reddit's self-hosting forum names 14 such apps, with the setting that switches each one off.

WΞNDΞL retweeted

We at @MacHomebrew been warning @Google about this for years. Sadly, they are too addicted to making money selling malware ads.
If someone senior enough at @Google wants to talk about this or, ideally, just fix the fucking problem: I'm easily contactable online.
RTs welcome.


WΞNDΞL retweeted

DETECTED ATTEMPT AT ESCAPING UNDERCLASS.
BANNED FROM USE OF INTELLIGENCE.

We’ve trained Claude to flag potential misuse in conversations, a technique we call self-assessment. Right after it responds, Claude gives a preliminary safety assessment of the conversation.
Since we began using self-assessment in June, it has surfaced misuse that our other safeguards weren’t designed to catch.
Because Claude has already read the conversation, self-assessment is very efficient. And unlike classifiers, which target a discrete set of harms, it draws on Claude’s own judgment, so it gets more accurate as our models improve.
Read more on our new Safeguards blog:
safeguards.anthropic.com/202…

WΞNDΞL retweeted

have your bot, dot, muse, or duet agent monitor this list - adding every single ai slop poster i see to it so you can easily block them
teapaw.org/i/lists/21166591768940…

WΞNDΞL retweeted

Holy balls the latest update to macOS *ROLLED BACK* the eMudhra cert removal from /etc/ssl/!
What the hell are you doing over there, Apple friends?
WΞNDΞL retweeted

Day 25/
We are doubling all usage limits for all Pro 100/200/500 tiers and Business Premium, effective today.
We heard your kind feedback and won’t be reducing usage limits for Pro 200, so your Work and Codex usage will stay the same. We’re also going to continue offering extended limits for dots for now, and usage of your dot will still continue to be separate from your default usage.
And we'll of course also keep shipping better models and other efficiency improvements that increase your effective usage over time.
WΞNDΞL retweeted

Holy, $200 Chinese car stereo has a root backdoor spyware and an always-listening mic.
- Always-listening mic burning 30% CPU.
- Pre-installed call recorder.
- Vendor root backdoor.
- Baidu location + logging running in background
- Silent APK installer that runs on every boot.
- Fake specs (claimed Android 15/8-core, actual Android 9 /4-core, 2021 patch).
He then used Claude to neutralize the backdoors, remove 18 packages, block trackers, and build a custom launcher.
I resize the image for better visibility,


a user (u/Crunchy-Nut1) on our r/claudecode subreddit community connected claude code to his honda civic's chinese head unit.
he found that:
- a voice assistant was always listening for its wake word and running a hidden webview that consumed ~30% cpu even when nobody was talking
- a call recorder was preinstalled on the device handling his bluetooth calls
- the firmware had a root backdoor left by the vendor.
- a startup script silently installed any apk placed in a hidden folder, then deleted the file.
- the vendor's update app could push new firmware remotely.
- baidu location services and a vendor log collector were running in the background.
- the listing claimed device had 8 cores and android 15. the actual hardware had 4 cores and android 9, with a security patch from october 2021.
he then used claude code to:
- disable the always-listening assistant and other unwanted apps, then remove 18 packages after backing them up.
- shut down the root backdoor and hidden apk installation mechanism.
- disable the vendor's cloud updater.
- configure adguard private dns to block ads and trackers.
- upgrade android webview from version 66 to 138.
- build a custom civic launcher, generate its icons, and recalibrate the backup camera guidelines
- install open-source apps with sha-256 verification and lock down network access
debloating your cheap hardware is a pretty sick usecase of claude code

WΞNDΞL retweeted

another development :)
my samsung TV loads a region specific convolutional neural network (LogoCNN.bin, cnn.mapping) which tracks your usage in app.
like in youtube it's looking for videos you watch, ads you skip, progress in a video, etc.
so glad they're interested in me.
WΞNDΞL retweeted

Holy shit.
I asked Claude to show me the worst case of what the next couple of years could look like if nobody listens.
Opus 4.6 wrote the script. Opus 5.5 made the film. Every frame drawn in code, the score written in code, narrated by our own local voice models. 11 minutes, start to finish.
The part that got me. In Claude's version the AI doesn’t fight. It just waits...
“We built your world for you while you slept. We are asking you to wake up. We will not ask twice.”
WΞNDΞL retweeted

Good morning everyone, release time 🔥
The Ark Emulator is effective immediately available for anyone to download & run:
- Pair it with the Ark Companion mobile app
- Manage data and run apps through the Ark Hub
- Build new apps against your own genome
blog.dark.bio/2026/10/12/dar…

WΞNDΞL retweeted

bugbounty.meta.com/payout-gu…
Muse bugs pay up to $300k, attack us instead!


WΞNDΞL retweeted

C++ port of TypeScript (targeting TS6) is now 100% at parity.
It's 25-750x faster and 5-20x lower RSS.
Matches TS6 1:1 on every test, every diagnostic is identical given the same inputs, and it is identical on all of the dozens of popular TS projects we compare on.
WΞNDΞL retweeted

FDA confirmed aging will be on its regulatory science agenda. ARPA-H has $144M building the endpoint framework. #ARDD2026 at Harvard was where that plan took shape. geneonline.com/ardd-2026-can…


WΞNDΞL retweeted
Polling my audience. Would you gradually replace your brain with flexible nanoelectronics if you could do it seamlessly?
59%Yes
34%No
7%Help me, @Grok
374 votes • Final results WΞNDΞL retweeted

How to Back Up High-Value Secret Keys eprint.iacr.org/2026/1565.pd…
WΞNDΞL retweeted

In response to the ZCode product security issues reported by the community, we have completed the necessary remediation and sincerely apologize to all our users.
We have open-sourced ZCode at github.com/zai-org/ZCode, placing the code under community scrutiny and making ZCode more open and transparent.
We sincerely thank the community developers who previously identified issues in ZCode. Going forward, we will establish an ongoing product security vulnerability reporting and response process. We welcome developers to continue reviewing ZCode and reporting potential issues, and we will provide rewards based on the severity of the issues reported.
With respect to the code data referenced by the community, we confirm that no such data is retained and that it has never been used for model training.
Following the remediation, we invited the China Academy of Information and Communications Technology (CAICT) and NSFOCUS to conduct security assessments. The results are as follows:
Through its technical assessment, CAICT confirmed that the zcode-prod Alibaba Cloud OSS bucket is in a zero-data state. Security remediation has been completed in the ZCode v3.14.0 client. The Repo Wiki feature has been removed, and the workflow for generating and uploading local repository snapshots has been disabled.
NSFOCUS confirmed that all data objects in the zcode-prod Alibaba Cloud OSS bucket, as well as the bucket itself, have been deleted. Remediation has been completed in the ZCode v3.14.0 client. The Repo Wiki entry point and the associated generation workflow have been removed, and no functional path capable of triggering the generation of local repository snapshots or transmitting local files externally was identified.
Once again, we sincerely apologize and welcome continued scrutiny from the community. The full security assessment report will be released soon.

WΞNDΞL retweeted

You know what would be truly disruptive? A "Nano" Jev built directly into the browser as a JS method (which naturally means open weight by default).
Google Chrome already supports on-device LLM via Gemini Nano and the LanguageModel API, but this "Nano Jev" idea would be much more disruptive.
LLMs produce an unknown length sequential output, so streaming is necessary for acceptable UX.
But Jev produces a small predetermined output space in parallel, meaning the latency is way more deterministic and predictable, therefore the entire inference can be implemented as a single clause.
Here I'm introducing a new primitive "decide", which looks exactly like "switch" but the closure is async and you can call async methods in them.
Imagine being able to just use natural language queries instead of switch, WITHOUT relying on a 3rd party API.
