




Pinned Tweet
How $VRA quietly robbed you without putting a gun to your head:
1. VRA sent to exchanges (OKX, Kucoin, Gate, MEXC)
2. Those tokens are sold on open market creating sell pressure on price
3. The sales generate $USDT which is then sent back to a Verasity controlled wallet known as their hot wallets
4. The USDT is then passed through a forwarding wallet
5. Finally the USDT ends up in places like BitGo (a professional custodial service for converting to real world money)
All of this can be verified on chain. If you disagree you’re probably fucking illiterate.
Hot wallet: intel.arkm.com/explorer/addr…
Forwarder wallet: intel.arkm.com/explorer/addr…
So before you tell your mates mums sisters brother to ape in, remember:
VRA tokens
↓
Sent to exchanges (OKX, KuCoin, Gate, MEXC)
↓
Sold on market
↓
USDT received
↓
Verasity Hot Wallet (0x3b5)
↓
Forwarder (EIP-1167 proxy)
↓
BitGo WalletSimple (custodial)


Bob retweeted

Binance 14, the exploited signee, was the very First and Original funder of:
Binance 16
Binance 17
Binance 18
Binance 20
Crypto.c0m 6
Crypto.c0m Main address
Something you should know.


Hope you all took profit instead of waiting for $1000 $QNT 😂

Vibe coded 1000 simulated $QNT price paths erupting as luminous particle clouds in a 3D Monte Carlo fan chart!
It's up 9% today but price has shown weak synchrony with overledger success. My AI agents say median $200-280 by 2030, upside tail $800-2k possible 🤔👇
Bob retweeted

Lazarus hacks….
2017 NiceHash $64M
2018 Coincheck $530M
2019 Upbit $49M
2020 KuCoin $275M
2022 Ronin Network $625M
2022 Harmony Bridge $100M
2023 Atomic Wallet $100M
2023 Alphapo $60M
2023 CoinsPaid $37M
2023 Stake $41M
2024 DMM Bitcoin $305M
2024 WazirX $235M
2025 Bybit $1.5B
2025 Phemex $70M
2026 Drift Protocol $285M
2026 KelpDAO $292M
2026 Bitget $387.5M
2026 Binance $6B+


Bob retweeted

He’s right.
I always tell people you have to be a skill based human being. Acquire as much knowledge and as many skills as possible.
I honestly think the more skills you have the higher chance of making it anywhere you have.

Your job is to make as much money as possible by any means necessary. Don’t box yourself into roles. Don’t identify with your job. Nobody cares if you’re a software/ai/cloud/anything engineer, your knowledge might be obsolete in a few months and you could get laid off next year, who knows.
Build multiple income sources. Skill up. Try to escape the rat race. Play the system. Cheat. Commit fraud. Lie on your resume. Whatever. You’re not winning this game by staying a good, obedient employee.
Bob retweeted

Two critical vulnerabilities have been identified in PHP, a widely used programming language that powers websites and web applications. These vulnerabilities (CVE-2026-109618 and CVE-2026-109619) could allow malicious cyber actors to remotely execute code in PHP core, potentially compromising sensitive data and networks.
The FBI urges organizations to take the following steps now:
➡️ If an immediate update is not feasible it is recommended that organizations take the system offline until it can be fully mitigated.
➡️ Immediately update affected PHP installations following the guidance on php.net. Inventory where PHP runs in your environment, prioritizing internet-facing systems and vendor products that bundle PHP.
➡️ Monitor web servers for suspicious activity, including PHP processes unexpectedly launching command shells or downloading files. Ensure appropriate process-monitoring capabilities are in place to help identify potential exploitation.
➡️ If you find signs of compromise, isolate affected systems, preserve your web server and PHP logs, and report it to your local FBI field office or ic3.gov. Those reports help us identify the actors involved and warn other organizations before they become victims.
For the latest information, follow PHP’s announcement on php.net, CERT-EU Security Advisory 2026-018, and CISA’s Known Exploited Vulnerabilities catalog.

ALT Critical vulnerability alert for PHP Core with CVE-2026-109618 and CVE-2026-109619, CVSS score 9.2, urging immediate patch and threat hunting.

Bob retweeted
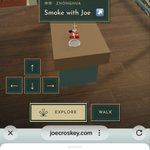
built a little shanghai apartment for my new website w @threejs
come in, put on some chet baker, have a martini w me, smoke a cig and see where the night takes you
joecroskey.com
Bob retweeted
New finding in $COTI investigation 🚨
On-chain data shows a structured mint → funnel → Binance pipeline that behaves like controlled exchange routing 🤔
Not proof of selling but a direct path from newly issued supply to exchange liquidity
Digging deeper! 🔔 🔛
My 2026 COTI On-Chain Deep Dive Answers The Big Question: ARE THE TEAM DUMPING?👇
Over the last few days I’ve been rigorously stress testing $COTI on-chain using; Cotiscan/Blockscout exports, Arkham Intel, Etherscan + cross-chain tracing, AND MULTIPLE independent AI agents to sanity-check conclusions:
Despite very high centralisation (genesis + treasury control a huge share of supply), current on-chain behaviour looks far more like minting + reallocation + distribution than sustained dumping and I stand with @shahafbg @COTInetwork
✅ What the data supports so far:
- Emissions are routed into protocol-controlled wallets and operational pipelines
- High transfer-volume wallets behave like distribution accounts (thousands of small transfers)
- Several “suspicious” wallets don’t accumulate, they act like bridge / liquidity routing hubs
- One major flagged flow path appears to cycle assets internally (routing loop behaviour), rather than cleanly exiting to exchanges
❌ What I have NOT found evidence for so far:
- Systematic “team dumping” patterns
- Persistent direct off-ramps to CEX deposit wallets at scale
This doesn’t mean COTI has no risks because centralisation is still a key risk factor, but the claim that “the team is dumping emissions into exchanges” is currently not supported by the flow structure we’re seeing.
Full deep dive soon: Wallet map + emission tracing + bridge flow analysis + exchange linkage verification.
