






Bythos retweeted

$5M only paid if you are successful is an awful deal that no competent firm accepts as a fee structure.
How about all of the initial hours you’d have to initially spend upfront?
Basically the victim takes zero risk upfront while the people attempting to help have to risk their time/energy. That does not align.
These vague “bounties” are bad for the industry and only make it look like the team is doing something while not actually incentivizing anyone competent.
A fair compensation structure rewards both time spent by billing for hourly + incentivizes successful outcome with contingency % (how all top firms structure fees).
There’s also a number of factors which show how these bounties are not fair:
How about if the attacker lives in a bad jurisdiction making arrest difficult?
What if law enforcement doesn’t recover all of the funds during arrest?
etc
Bythos retweeted

SDNY and @HSISanDiego seize cryptocurrency worth approximately $31 million related to April 2021 hack of Uranium Finance. If you believe you have been a victim of this hack, please contact [email protected].


Bythos retweeted
Users lost millions due to @AlpacaFinance allegedly using manual CoinGecko price updates instead of real oracles. When questioned, they asked "which faster oracle would you have used?"
Turns out F5 isn't a reliable price feed. Who knew?
rekt.news/false-prophet/


Bythos retweeted

Someone is running a strategy to borrow USDC, send it to another wallet, receive it back from the same wallet, and then repay.
The size most recently was $145M

Bythos retweeted

anyone using @solana/web3.js, versions 1.95.6 and 1.95.7 are compromised with a secret stealer leaking private keys. if you or your product are using these versions, upgrade to 1.95.8 (1.95.5 is unaffected)
if you run a service that can blacklist addresses, do your thing with FnvLGtucz4E1ppJHRTev6Qv4X7g8Pw6WPStHCcbAKbfx
Bythos retweeted

Your oracle has 11 price sources and takes the median. How many sources must you manipulate for the median to change? If the prices are all close to each other it should be 6, not 5. There's more to it:
The oracle used is the `sUSDePriceProviderBUniCatch`. It takes 11 sources
- 1 Uniswap V3 (USDe/USDT) TWAP.
- 5 Curve Pools. For each pool, both its spot price (`get_p`) and EMA (`get_price`) are considered.
etherscan.io/address/0xd2529…
The 5 CRV spot prices are easily manipulated, but it would still require one of the EMAs or Uniswap-V3 to be off. Indeed, we can observe that the USDe / USDC Curve EMA was already 5.5% off. Why? I didn't look into it, maybe the attacker manipulated it in blocks before the attack.
app.blocksec.com/explorer/tx…
Each spot source you include in your median oracle essentially eliminates another TWAP source. The oracle might have been better off not using any spot prices at all.


Today's @UwU_Lend hack leads to $19.4m loss.
The root cause is a price oracle issue. In particular, the sUSDe asset is priced as median from multiple sources. Five of them, i.e., FRAXUSDe, USDeUSDC, USDeDAI, USDecrvUSD, and GHOUSDe, were manipulated during the hack.
The stolen funds are parked in the following two addresses:
etherscan.io/address/0x48d7c…
etherscan.io/address/0x050c7…

Bythos retweeted
🚨SlowMist Security Alert🚨
We detected potential suspicious activity related to @liquiditytokens.
bscscan.com/address/0x85f822…
bscscan.com/address/0x19b3f5…
As always, stay vigilant!

Bythos retweeted

Before you all start connecting to any dapps today - from your @Ledger device.❗️
Remember that you should first do a quick check to see if your browser is caching the most recent Ledger update or not. How to check:
1. Clear browser & device cache first;
2. Visit: cdn.jsdelivr.net/npm/@ledger…
3. Ensure that version is 1.1.18.
How to check:
x.com/mudit__gupta/status/17…
Ledger update:
x.com/Ledger/status/17353705…
How to clear cache?
In ledger: To clear your cache, simply go to the Settings menu -> Help -> Clear Cache.
In browser: clear all history.
Stay safe!

Bythos retweeted

Basically:
- some frontends use an npm package 'ledger connector'
- that package has been compromised in a supply chain attack
- doesn't matter if you use a ledger or not, if you connect and broadcast a tx on a compromised website (like @RevokeCash), you will be drained, wether you use metamask or rabby or etc
- if you use a website that isn't compromised (like @DefiLlama), you're safe
If you don't know what you're doing, better to not sign any transaction at the moment.
No need to revoke anything, it's not about approvals.


Bythos retweeted

Classic read only reentrancy on Conic today.
The Curve pool is buggy, in that it hands off execution to the attacker with only partial updates to its internal state Thus when the attacker interacts with Conic, and Conic reads from the Curve pool, it gets bad answers.
1/3

Bythos retweeted
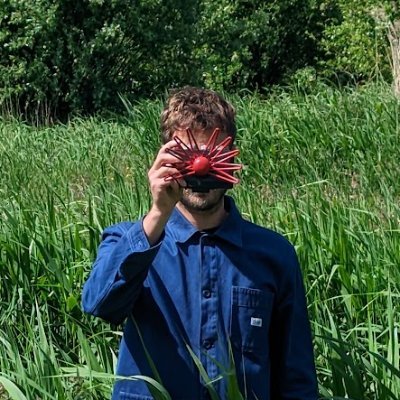
Introducing – Paragraphica! 📡📷
A camera that takes photos using location data. It describes the place you are at and then converts it into an AI-generated "photo".
See more here: bjoernkarmann.dk/project/par…
or try to take your own photo here: paragraphica.bjoernkarmann.d…
Bythos retweeted

This means a searcher generated over $20k in MEV without seeing anything about the user’s tx. They didn’t have access to the calldata, logs, or contract address — only the transaction hash.
How is that possible?
Bythos retweeted

Ledger just released a new update for Nano X that allows social recovery of your seed phrase.
It encrypts your seed in 3 shards and sends it to different entities that can then reconstruct the seed for you post ID verification.
It's a horrendous idea, DON'T enable this feature.

Bythos retweeted

etherscan.io/txs?block=17231…
In this block we see a sandwich from jaredfromsubway.
The frontrun sell memecoin for ETH, raising the price of ETH
The victim trades memecoin for ETH, receiving less ETH than they would
The backrun sells ETH for memecoin


