

Inspect the chip. Own your System.
Joined March 2026
- Tweets72
- Following93
- Followers75
- Likes100



The AI capability ceiling keeps rising. Existing safety guardrails won't hold.
In April 2026 the UK's AI Security Institute evaluated Anthropic's Claude Mythos Preview, a model Anthropic judged too capable at security tasks to release publicly.
It solved 73 percent of expert-level capture-the-flag challenges that no model could complete a year earlier, and became the first model has tested to run a 32-step simulated corporate intrusion from reconnaissance to full network takeover end to end. It's scary.

3
212
GitHub just got HACKED!
TeamPCP stole ~4,000 internal private repos (including source code) via malacious VS Code extension.
Now they're selling it. We wrote about this, everything is gonna break.
Devs, Orgs, Govs were dependent on Github's security to safegaurd them and their data.
World is changing. So should the way we safegaurd us.
Welcome to the ledgerless world.


2
249
What All AI Security Incidents Have in Common?
All preventable. None prevented.
The structural pattern underneath all of them is the same:
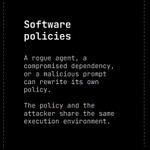
1. The policy enforcement and the attacker occupied the same execution environment.
2. Software guardrails run on the same machine as the agent they are supposed to constrain.
3. A rogue agent, a poisoned package, or a well-crafted instruction can reach credentials directly, rewrite policies at runtime, or simply use the permissions the agent was given and never meant to use at scale.
85