

CISO at @sardineai. Chapter leader @OWASP Phoenix. (he/him) qatta' mIghtaHghach.
Phoenix, AZ
Joined July 2009
- Tweets8.5K
- Following115
- Followers760
- Likes16.3K





Bil Corry retweeted
We are super close to having a platform to release @_HighSchool911 on! Working on having it set up in the 1st quarter of 2026.🤞🏻 You will be one of the first to receive the link. We hope you are still with us by then—
“84 years” later. 😊 Happy Holidays, Bil, & thanks again! 🚑

FCC shut down 1200 VOIP providers because they didn't adhere to the anti-robocall rules. A little less fraud out there...
docs.fcc.gov/public/attachme…
Bil Corry retweeted

🤔 Are merchants mistaking AI agents for malicious bots?
We tried to buy a $4 tube of toothpaste online (for pickup) with ChatGPT Agent mode.
The checkout never made it past the fraud system. It wasn’t a payment issue. It wasn’t out-of-stock. The only “problem” was that the buyer was an AI agent.
Old world: Spot the bot, stop the fraud.
New reality: The bot is the customer.
This is an issue most merchants are racing to figure out. The ones that update their fraud toolkit for this new world will own the next era of commerce.
But that will mean figuring out how to:
- Authenticate agents as legitimate buyers
- Bind user consent to agent actions
- Detect compromised or malicious agents
- Redesign step‑ups for non‑humans
- Adapt risk scoring to mixed human/agent journeys
We’ve laid out ways to adapt in our new whitepaper on agentic commerce.

As talk heats up about internet age verification and how teens are bypassing the controls, I'm reminded of this story from nearly 20 years ago when Australia sunk $84 million dollars into a porn filter that was bypassed within 30 minutes by a teen.
zdnet.com/article/teen-crack…


Bil Corry retweeted

With the rise of AI, some people estimates 1 in 4 job candidates will be fake by 2028. In a recent internal hackathon, we built a system to catch fake applicants using Sardine's technology. Here is how it works - sardine.ai/engineering-blogs…
Bil Corry retweeted
HARK, INFOSEC FRIENDS! CactusCon 13 talks are now LIVE!
youtube.com/playlist?list=PL…
We had so many great technical talks this year, and our keynotes @AletheDenis and @ShelbyGrossman did a great job offering unique insight on this wild AI-infused world we now live in.

My son setup a @HiltonHonors account. The security is so good, not even my son can log into his own account. Spent a good 25 minutes trying though.
He also setup a @MarriottBonvoy account. That took 45 seconds.
Guess which hotel he's going to stay at 🤣
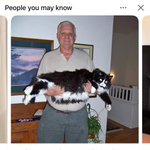
I have 10 of these “people you may know” suggestions that are obviously not people.
Meanwhile, Facebook locked my daughter’s account 3 days after she created it because they thought she was fake.
I realize Facebook is operating at scale, but lots of misses here.


Tried to let @Verizon know someone is fraudulently using my wife’s info to buy a phone. They wouldn’t take the report unless my wife “verified” with them. No thanks, why would we give you our info? We’re not customers of Verizon, what would Verizon even verify? Our info is not going to match whatever the scammer entered. Best of luck Verizon!

My dream of having a Wall-E chair is getting closer.
kickstarter.com/projects/ota…

Do you know who sends .html files via email? Phishers and @salesforce.
I wish Salesforce would stop doing that. It's a HTML file with only one thing in it, a link to Salesforce.
Here's an idea, just put the link in the message body like everyone else on the planet and stop habituating users to expect legitimate content comes in a .html file.
Oh, so @SendGrid can send me dozens phishing emails, but if I send one back to them to report it, they block it 🙄
Here's an idea: whatever filter you are using to block the inbound emails, use that on your outbound emails! Seems weird that the messages you won't accept, you are happy to collect a fee and send them to everyone else.

