






Pinned Tweet
Super happy to see our research ranking #3 in @PortSwigger Top Web Hacking Techniques of 2024! 🚀
This one was a wild ride!
Huge thanks to @_medusa_1_ & @sw33tLie for the amazing teamwork and to @Bugcrowd, who supported us! ❤️
What next? Keep tuned 👀🥷🏻
#BugBounty #Hacking

The results are in! We're proud to announce the Top ten web hacking techniques of 2024! portswigger.net/research/top…


bsysop retweeted

You can now perform content discovery at 100k requests per second with h3fuzz on http/3 hosts (fork of ffuf with http/3 support).
Tool here: github.com/assetnote/h3fuzz
Research post here: slcyber.io/research/how-prac…
To everyone who keeps expanding scope and raising bug bounty rewards in the AI era: Thank you.
You’re absolute badasses. 🤘
#BugBounty
Anything sweeter than an RCE? Multiple RCEs. 🤟🏻
GG @0xTeles 🔥

yo, just sharing my latest personal achievement. My biggest bug bounty yet, $30,000 from MSRC.
@bsysop and I uncovered RCE vulnerabilities affecting 100% of the Major Cloud providers.
Proud of the research. Even prouder of the impact.
We may share the technical deep dive in a future blog post.


bsysop retweeted
Remote code vulnerability found in Unitree robots and the scary part is that the exploit is wormable. That means one compromised robot could infect other vulnerable robots nearby, turning a single breach into a wide compromise. Could attackers then take control of entire fleets of humanoid robots? boschko.ca/unitree-go2-rce/

bsysop retweeted

The whitepaper is live! Read "Can AI Do Novel Security Research? Meet the HTTP Terminator" here ->
portswigger.net/research/htt…

Cool and really useful
Nice work @hahwul

GORI(고리) is now public!
A keyboard-native TUI proxy built for pentesters and hackers. Intercept, edit, and repeat traffic right in your terminal with pure muscle memory flow.
Happy Hacking in Terminal :)
Github: github.com/hahwul/gori
Install: gori.hahwul.com/getting-star…
As always impressive, congrats to @hash_kitten and the @assetnote team for the consistency! 🔥🚀

I reported a pre auth RCE in Wordpress - it can be exploited with no preconditions, patch your instances!
slcyber.io/research-center/w…
bsysop retweeted

Let’s talk about the tsunami of automated junk code hitting production. 🌊
The cloud-native landscape is mutating by the hour, and standard defense lines are bending under the weight. On August 6th at 5:00 PM, we’re teaming up with AWS Marketplace inside The Hive for a critical deep-dive 👇
Hacking in the Age of AI: What's Changed, What Hasn't. We’re swapping the standard abstract vendor pitches for a gritty, technical look at how elite researchers manipulate shared responsibility at scale.
🎤 Ads Dawson
🎤 @codingo_
Come see how the other side plays the game 😈
Claim your seat: bugcrowd.com/the-hive/
Massive thanks to @HPE, @trustvijil, Cytix, @Pi_Security_, and Manifold Security bringing this to life!

Spent the last days hacking at the @Bugcrowd event and had an absolute blast.
Big shoutout to Tatiana and the Bugcrowd team for the amazing event, and all the brilliant hackers for the impressive work. 🤟🏻
#BugBounty


bsysop retweeted

We’ve now seen at least four nginx RCEs that require non-default configs: nginx rift, nginx poolslip, and two of our own (including the one in the last tweet).
The configs involved are unusual, which raises the obvious question: do these attacks actually work in real-world deployments?
We asked Claude to download and analyze more than 4,000 nginx config files from GitHub.
The result was embarrassing: none of them were vulnerable to nginx rift or our own attacks. We can’t say anything about nginx poolslip yet, since it hasn’t been published.
So don't worry about your nginx yet.
Moral of the story: AI can generate FUD, but also help fight FUD. Embrace it!
bsysop retweeted

That's my chain — a full chain w/ logic bugs only! No memory corruption, no AI, and of course no collisions at all 😉

Confirmed! Orange Tsai (@orange_8361) of DEVCORE Research Team (@d3vc0r3) chained 4 logic bugs to achieve a sandbox escape on Microsoft Edge, earning $175,000 and 17.5 Master of Pwn points. Full win! #Pwn2Own #P2OBerlin

Free screenshot tool!! 🚨
The most advanced out there with features for all segments, but especially if you work with sensitive data.
- Automatic PII redaction
- Blur/Pixelate data
- Draw
- Picture to Text
And much more, go check it out.
🔥🚀🔥🚀
#BugBounty #BugBountyTips

I wanted a screenshot tool for macOS better than anything out there, so I built one with @claudeai
Native Swift. No Electron.
Annotate, record screen, scroll capture, auto-redact PII, beautify, upload to Drive & more — one flow.
Free & open source forever.
macshot 🔗👇
bsysop retweeted

if you've ever had to decompile hundreds of JARs/DLL just to find the 38 that actually matter
we built something for that 👀
Hyoketsu filters vendor dependencies out of your target before you even open your decompiler.
🪿 hash-matched against tens of millions of files.
👇

We got frustrated with dealing with vendor dependencies when reverse engineering large applications. @ITSecurityguard from @SLCyberSec’s Sec Research Team built Hyoktesu to solve this problem forever: github.com/assetnote/hyokets… - releasing this today! Blog: slcyber.io/research-center/h…
Brilliant, worth checking!!
#BugBounty

Added 3,600+ publicly disclosed HackerOne reports that paid a bounty to the MCP.
👇
github.com/PatrikFehrenbach/…
This should help Claude to decide where to focus on, what attack surface was looked at before, and where new vulnerabilities could be 👀 (in theory 😏)

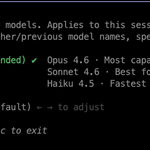
AI Tuning TIP:
Many people change the model but leave effort untouched, missing a big part of the tuning.
The effort setting controls how much reasoning the model applies.
Low -> faster responses
Medium -> balanced (default)
High -> better for complex problems
#AI #BugBounty

