

Faculty at CISPA - Helmholtz Center for Information Security
Germany
Joined May 2010
- Tweets645
- Following222
- Followers1.2K
- Likes655





Pinned Tweet
My research group @CISPA is hiring PhD students and PostDocs! Are you interested in network/software/system security? You'd start in an excellent research environment and enjoy complete academic freedom at ~52-61k EUR annual salary. Details: cispa.saarland/group/rossow/… -- please RT.

I am pleased to serve as the "Network Security" Track PC Chair at ACM CCS 2026. The conference (including all other tracks) seeks volunteers for the PC. Nominate yourself or others here: forms.gle/xFYauxEr6XaxMAaw6 -- Looking forward to hearing from you!
Christian Rossow (@[email protected]) retweeted

📣 The program for #ACSAC2024 is now online in its full glory: acsac.org/2024/program/
Once you have seen all the interesting papers, you will undoubtedly want to register for the conference, which is already possible, so go right ahead: acsac.org/2024/registration/
Christian Rossow (@[email protected]) retweeted

We have just published our call for faculty @CISPA (see jobs.cispa.saarland/jobs/det… for S&P and jobs.cispa.saarland/jobs/det… for AI/ML). Application deadline is December 2, AoE. Please spread the news and if you have questions, reach out, I'll be at @acm_ccs next week to chat!
Christian Rossow (@[email protected]) retweeted

Manuel Egele and I look forward to your submissions 🥳
#DIMVA25 will have two deadlines:
04 Dec 2024 & 12 Feb 2025
#DIMVA is a great venue for young researchers to network and exchange ideas! Mark your calendars: 9-11 July in Graz!!

The first #DIMVA25 deadline is on December 4.
Check out the CFP: dimva.org/dimva2025/
Christian Rossow (@[email protected]) retweeted

We have just published the CfP of EuroS&P 2025! Check out eurosp2025.ieee-security.org… and get your papers registered by October 21 and submitted by October 24. Also check out the change in rebuttal already after round 1 of reviews!
Hypervisors can't see the memory content of confidential (AMD SEV) VMs. This undermines memory forensics and its rootkit detection. @fa_schwarz will present 00SEVen at #usesec24, which re-enables forensics in confidential VMs *without* revealing memory to the cloud provider. 1/x

00SEVen leverages so-called VM Privilege Levels (VMPLs) in AMD SEV to execute a protected forensic agent inside the VM. Running at a higher VMPL than system software, even full-system compromises (e.g., kernel-level attackers) cannot tamper with the agent. 2/3
In 00SEVen, remote analysts can connect to the VM, remotely attest the forensic agent, and then perform libVMI-compatible forensic tasks such as memory & register inspection, or setting traps. Don't miss @fa_schwarz' talk @USENIXSecurity on Wed, 4:30pm, "Forensics" track. 3/3.
Don't miss @ypannap's #usesec24 talk on discovering loop #DoS vulnerabilities in network services! 2nd talk in Session I (Track: DDoS) on Wednesday. Great collaboration with Anna Ascheman, who did large chunks of this work during her @CISPA internship.

We @CISPA discovered that attackers could trigger infinite message loops at the application layer between servers of popular protocols such as DNS, FTP, or NTP. To trigger such an infinite loop, attackers just have to send a single (!) IP-spoofed trigger message. 1/4

Christian Rossow (@[email protected]) retweeted

With the #GhostWrite CPU vulnerability, all isolation boundaries are broken - sandbox/container/VM can't prevent GhostWrite from writing and reading arbitrary physical memory on affected RISC-V CPUs. Deterministic, fast, and reliable - no side channels. ghostwriteattack.com/

Christian Rossow (@[email protected]) retweeted

The list of RAID2024 accepted papers is now online! Check them out here! raid2024.github.io/accepted_…
Christian Rossow (@[email protected]) retweeted

Today, Felix is presenting our SoK paper on target selection for directed fuzzing at @ASIACCS2024. We analyzed 9 common selection methods on 1600 crashes, and guess what: simple software metrics still outperform all others. LLMs come in second only😲
mlsec.org/docs/2024c-asiaccs…

Christian Rossow (@[email protected]) retweeted
This is your reminder that we still solicit (self-)nominations for the 2025 EuroS&P PC. If you have published at top security, privacy, or crypto venues before, nominate yourself. If you know others who'd fit, nominate them. Nominations will be considered until end of July.

Next year's 10th EuroS&P is looking for new PC members! If you want to nominate yourself, please fill in the Google form: forms.gle/QVroyfqwxkRwWQqF8

Full support. Diversifying the conference locations raises fairness in *many* respects. Thanks for the visualization and comparison.

Some top tier conferences have a heavy geographical bias. Software engineering leads in diversity while security mostly sticks to the US. We need to start moving! @NDSSSymposium @IEEESSP @USENIXSecurity live map: nebelwelt.net/gannimo/conf_l…

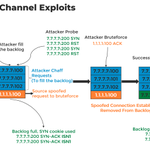
Traveling to #IEEESP2024 to present @ypannap's paper on TCP spoofing. Our @CISPA work shows how attackers can leverage IP-spoofed TCP connections to evade network-based access control (e.g., in firewalls, DBs, or SPF). We present two core ideas: (1/4)

2) We show that attackers can leak the server-chosen initial sequence number (ISN). The ISN is the only secret that prevents spoofing attackers from transmitting payloads over their IP-spoofed connections with accurate SEG.ACK numbers. (3/4)

Our talk will be Wed (May 22) afternoon (Track 1 / Session 12). Looking forward to your comments! Also, come and see our poster. Alas, @ypannap (PhD candidate in my group and main author) faced visa issues😐Paper preview: cispa.saarland/group/rossow/… (4/4)
Christian Rossow (@[email protected]) retweeted

Statement, signed by 250+ researchers, warning that the modifications of the Regulation to detect CSAM proposed by the EU presidency dont solve the issues pointed out by experts. It still introduces societal risks without solving the CSA problem.
csa-scientist-open-letter.or…