

OpenID Connect and OAuth 2.0 for fintech, verified identity providers, innovative startups and enterprises
Joined May 2011
- Tweets984
- Following100
- Followers405
- Likes236
Pinned Tweet
Type-safe Rich Authorization Request (RAR) support in v10.12 of the #OAuth 2.0 / #OIDC SDK connect2id.com/products/nimb…

The much anticipated STS API to ease federated logins with the @connect2id server is here
connect2id.com/blog/connect2…

The #OAuth 2.0 #JWT authZ grant (RFC 7523), somewhat of a mystery to developers, has great utility for backend services that need user-linked access tokens connect2id.com/products/serv…

Connect2id retweeted

The x.509 cert chain meets the #openid trust chain, @openidjp summit Tokyo 🇯🇵 2024
connect2id.com/blog/the-open…

Connect2id server 14.9 introduces automatic purge scan rate limiting for deployments with #AWS DynamoDB
connect2id.com/blog/connect2…

v11.5 of the #OpenID Connect SDK is now capable of resolving #OpenID Federation 1.0 trust chains with custom #HTTP clients connect2id.com/products/nimb…

But what is #OpenID Federation 1.0? connect2id.com/learn/openid-…
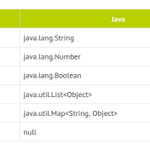
Every now and then developers ask us how the Nimbus JOSE+JWT library maps between JSON entities and Java classes connect2id.com/products/nimb…

The #Redis connector in the Connect2id server gets a sweeping update. The maximum concurrent session quota is per user is increased from 10 to 25.
connect2id.com/blog/connect2…
The #OAuth / #OpenID Connect SDK can now work with custom HTTP clients, such as #Apache HttpClient or OkHttp
connect2id.com/products/nimb…
You can now use #AWS CloudHSM to secure and verify JWTs with the HMAC-based HS256, HS384 and HS512 JWS algorithms. Credits Ulrich Winter connect2id.com/products/nimb…

v10.15 of the #OAuth / #OpenID Connect SDK received an important fix that affected client X.509 certificate extraction in Jakarta Servlet deployments. Credits Jesper Öst connect2id.com/products/nimb…
Another contribution in Nimbus JOSE+JWT 9.32 is EC JWS / JWT support for the Android biometric or PIN prompt. Credits Stian Svedenborg connect2id.com/products/nimb…
Thanks to the generous contribution of Egor Puzanov the Nimbus JOSE+JWT lib can how handle JSON Web Encryption (JWE) to multiple recipients connect2id.com/products/nimb…

The redirect_uri validation in the #OAuth SDK incorporates new lessons from the OAuth Security Workshop 2023
connect2id.com/products/nimb…


In #OAuth RAR the JSON objects that express the "authorization_details" have an explicit "type" to aid their parsing and validation. Connect2id server deployments can now check the RAR types in requests automatically, plugin code is no longer needed
connect2id.com/blog/connect2…

Preview of the upcoming public JWE to multiple recipients connect2id.com/products/nimb…
Examples show the new Nimbus JOSE+JWT facility for sourcing JWKs with rate-limiting, caching, retrial and outage support
connect2id.com/products/nimb…
One recognised drawback of refresh token rotation is that it can lead to false positives for legitimate OAuth 2.0 clients with a slow or poor network connection. How to mitigate that?
connect2id.com/blog/connect2…
