

Cloud Native Security Consulting ⟁ Audit and Training ⟁ authors of SANS SEC584, O'Reilly Hacking Kubernetes, GKE CIS, K8s Threat Models ⟁ https://xitter.cf/t.co/Lctilu86kN ☁️⚔️🛡️
London, England
Joined September 2017
- Tweets732
- Following751
- Followers3K
- Likes875





Welcome to native.cloud! An open source, vendor-neutral ontology for portable, consistent Kubernetes labels and annotations. These labels help unify indicators for compute, identity, workload, tenancy, topology, vendors and more:
Standardised Metadata: Unified K8s labels across domains (enterprise platforms, suppliers, and tooling)
Automation (and DevSecOps) friendly: Simplified security, governance, and platform maintenance
Vendor-Neutral and Extensible: Open source with low-friction addition of community contributions.
Explore the project native.cloud/ 🗺️🧭🧬☁📐

As your applications mature, a stable cryptographic base becomes absolutely critical. Traditional secrets management tools weren't always built for seamless extension or easy redeployment within a larger platform architecture. That’s where OpenBao steps in!
In our latest blog, we dive into how ControlPlane Enterprise for OpenBao provides a powerful open source root-of-trust designed specifically for modern platform engineering.
Whether you are aiming for multi-tenant adoption, SaaS redeployment, or on-prem self-hosted apps, OpenBao can scale with you.
control-plane.io/posts/openb…

controlplane retweeted

It's that time of year again. The Oscars of Open Source are back in their 7th year, in London.
Announcing @ciliumproject, @fluxcd, @stackhpc, and Tessera - @Cambridge_Uni have been shortlisted as finalists in the Software category of The OpenUK Awards, sponsored by @RedBadgerTeam.
We’ll celebrate the shortlist and announce the winners, taking place on 5th November at our annual Black Tie Gala Dinner and Awards ceremony at the House of Commons.
Shortlisted nominees, our sponsors and volunteers will be invited to join this event. Tickets are not sold, and the evening is made possible by the generosity of our sponsors: @RedBadgerTeam, @lowRISC, @ODIHQ, @controlplaneio, @Arm, Iain G. Mitchell KC, @Uber, @nolabs_ai, kioko, and @openxchange.
See the full shortlist: openuk.uk/awards/

We are proud to be returning as Diamond Sponsor for FluxCon North America 2026, the co-located event dedicated to @fluxcd!
The schedule features a great lineup of speakers from Morgan Stanley, Ericsson and our very own Stefan Prodan.
📅 Monday, 9 November, from 09:00
📍Salt Lake City, Utah
The FluxCon North America 2025 was the inaugural event, and the team were blown away by the incredible community response and engagement, so we’re looking forward to returning and seeing you there. Drop us a message if you’d like to set a time to catch up, or we’ll also be available on our stand.
Registration is still open for @KubeCon_ + CloudNativeCon North America. In-person attendees can register for an All-Access pass that includes entry to all @CloudNativeFdn hosted co-located events, including FluxCon.

ALT FluxCon North America, 9 November 2026
The Hugging Face and OpenAI intrusions have generated plenty of commentary, but very little analysis from the people who break into and defend these environments for a living.
In our latest blog post, Tom Cope, Principal Consultant at ControlPlane, shares his perspective on what these intrusions reveal about how these platforms are defended and what security teams should change as a result. Read the full analysis:
control-plane.io/posts/old-i…

Why does an AI agent need an identity of its own at all? Isn't sandboxing it, or tightly scoping its permissions, sufficient?
After all, we have decades of experience with least-privilege IAM, mTLS, and short-lived tokens. Surely an agent is just another workload?
Read the blog to get all the details
control-plane.io/posts/agent…

ALT Agentic Identity with OpenBao
In collaboration with the @openbaoofficial community, ControlPlane has recently helped remediate a full exploit chain that allowed unauthenticated access and escalation to full Remote Code Execution (RCE).
This marks only the second-ever RCE vulnerability discovered in Vault and OpenBao, combining disclosures from three independent reporters into a single, devastating exploit chain.
How the chain works:
By abusing a PKI ACME validation bypass, an unauthenticated attacker can spoof a service provisioner's identity. Then, they can modify an admin account, escalate privileges across namespaces, and ultimately achieve full RCE by restoring a malicious Raft storage snapshot.
Read the full blog or get involved with the conversation on @hackernews
control-plane.io/posts/unaut…

ALT A realistic code execution exploit chain in OpenBao and Vault
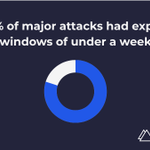
With most compromises typically detected within days, dependency cooldowns are an effective circuit breaker, as research shows 8 in 10 major attacks had exploit windows of under a week.
By letting an artifact age in public view, you give scanners, researchers, and upstream maintainers a window of time to catch what automated malware tools can release at scale in a few minutes.
Notably, for this to work, the publish time needs to be trustworthy.
Flux Mirror measures minAge against the Rekor transparency log timestamp, which is countersigned so it can’t be quietly rewritten later. This keeps compromised packages from landing in your registry before the industry has had enough time to examine them.
To find out more, read the blog: fluxcd.io/blog/2026/08/flux-…

With most compromises typically detected within days, dependency cooldowns are an effective circuit breaker, as research shows 8 in 10 major attacks had exploit windows of under a week.
By letting an artifact age in public view, you give scanners, researchers, and upstream maintainers a window of time to catch what automated malware tools can release at scale in a few minutes.
Notably, for this to work, the publish time needs to be trustworthy.
Flux Mirror measures minAge against the Rekor transparency log timestamp, which is countersigned so it can’t be quietly rewritten later. This keeps compromised packages from landing in your registry before the industry has had enough time to examine them.
To find out more read the blog: fluxcd.io/blog/2026/08/flux-…

Operating enterprise secrets management on Kubernetes shouldn't require battling the fragile Raft consensus protocol.
We’ve engineered PostgreSQL into a first-class data storage engine for Enterprise for @openbaoofficial, delivering:
⚖️ Horizontal read scalability achieves full parity with existing Raft support
🎯 Better client consistency control semantics
✅ An internal test suite to validate the behaviour of secret engines
Read the full post: control-plane.io/posts/enter…

Attending BSides Canberra this week?
Get ready to delve into the dark and mysterious world of Kubernetes security!
Mario Weigel, Senior Consultant, and Aiman Alsari, Head of Asia Pacific, will be running the Kubernetes Capture the Flag event. Whether you are a beginner eager to learn or a hardened veteran, there is a challenge for you with three increasingly demanding scenarios 🚩
Read the full details and add it to your schedule: cfp.bsidescbr.com.au/bsides-…
What happens if an attacker gets root access to your SPIRE server? 🚨
In our recent blog, we dive into how to leverage @openbaoofficial Transit Secrets Engine as "Cryptography as a Service."
Stop leaving your most critical keys exposed in memory. Dive into the technical configuration now
control-plane.io/posts/secur…

What does a truly ‘sovereign’ signing pipeline look like for GitOps?
To meet sovereignty requirements, we define a hard boundary: the signing key remains strictly within self-hosted infrastructure, and neither signing nor verification relies on external services.
Our blog on sovereign signing walks through a GitOps delivery pipeline where every link in the chain, from OpenBao key storage to Flux verification, is completely self-hosted and vendor-neutral.

Next week, our CEO, Andrew Martin, is heading to Amsterdam for AGNTCon + MCPCon Europe!
The primary focus over the two days is on exploring how teams can build, test, operate, and scale agent systems securely and reliably, transitioning them from initial prototypes to production environments.
Are you attending AGNTCon + MCPCon? Let us know if you want to connect!

Highly privileged Kubernetes tools like cert-manager and @kyverno are vital for cluster security, but misconfigurations can easily create direct paths to full cluster compromise.
To address these operational risks, ControlPlane collaborated with the @CloudNativeFdn (CNCF) and @linuxfoundation to publish two comprehensive threat modelling and hardening resources.
Read our full blog post to explore the key takeaways and download the threat models to harden your cloud native infrastructure.
control-plane.io/posts/harde…

Time is running out! ⏳ The deadline for the OpenUK Annual Awards is coming up this Sunday, September 6th.
We are the proud sponsor of the Security category this year. If you know someone doing incredible work, make sure they get the recognition they deserve.
openuk.uk/awards/


OpenUK 7th Annual Awards, Security category nominations are now open until 6 September. Nominate yourself or a colleague using the link below ⬇️
Massive thanks to our security category sponsor @controlplaneio 💫
A short list of up to 3 finalists will be shared by our Judges on 15 September.
Shortlisted nominees will be invited to our Gala Awards Ceremony and Dinner, where the winners will be revealed.
openuk.uk/awards/
#security #opensourcesecurity #opensource #opensourcesoftware #openukawards

In the age of AI, Linus’s Law that "given enough eyeballs, all bugs are shallow" has mutated into “given enough prompts to AI agents, all bugs will be exploited”.
To build true resilience, leadership must pivot toward Attestation-Based Security. By shifting the burden of proof from your security team to an automated pipeline, you can programmatically reject any artifact that lacks a verified chain of custody.
Is your organization still relying on static inventory, or are you validating integrity?
control-plane.io/posts/from-…

ALT 454,000+ new malicious packages in open source repositories in 2025. That's a 75% increase year-on-year. Source: Sonatype
Mirroring Kubernetes artifacts usually meant maintaining separate scripts for images and charts, with no built-in way to verify integrity.
@fluxcd Mirror handles artifact relocation in a single declarative config, verifying content before a single byte lands in your registry.
Read the walkthrough here fluxcd.io/blog/2026/08/flux-…

ALT Flux Mirror capabilities and descriptions
Non-human identity management is one of the most critical, and frequently misconfigured, aspects of modern platform engineering.
In our dedicated @OpenBao interactive tutorial on @Iximiuz Labs, we break down how to properly architect application-level authentication from scratch.
labs.iximiuz.com/tutorials/o…

ALT Discovering secrets with AppRole and least-privileged policies
DevSecOps embeds automated security controls into every single stage of the software development lifecycle, from initial planning to continuous monitoring.
Moving security from a final hurdle before software release to part of an integrated DevSecOps model delivers tangible organisational benefits and strengthens security posture. Read more in our latest blog.
control-plane.io/posts/dev-s…

ALT What is a DevSecOps Pipeline?