





Litaz retweeted

⚠️If you use Gmail, read this.
Scammers are hiding their messages inside REAL Google security alerts, so the emails pass the checks that normally catch fakes.
They type the scam text into the name of a Google app password, which makes Google send out a genuine, signed alert containing it.
Then they forward that alert to you.
One version flagged by the University of Michigan carried a fake $399 McAfee invoice and a phone number to call.
The real Google buttons in the email just open your own account page, where nothing looks wrong because nothing was breached.
That dead end is deliberate, leaving the scammer's phone number as the only "fix" left.
If an alert like this lands in your inbox, treat any phone number, reply request or button inside it as a red flag.
Even a genuine Google sender address is no longer proof that an alert is safe.

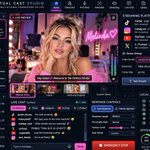
🎬Here’s a little sneak peek at what I’ve been working on lately! I’ve been building OMIBOO, my own streaming platform for original AI-assisted films and series. The streaming side is already working, and so is the local AI video generations. There’s still more testing and a few things to sort out, but we’re getting there! 😊 Now I’m working on something else to go with it, OMIBOO Virtual Cast Studio. The idea is to bring our fictional characters to life, give them their own personalities and voices, animate them and eventually have them interact with people live.
Still plenty to do, but I’m really enjoying seeing it all come together! 🎬❤️
Studio UI concept. Still in development.
#OMIBOO #AI #VirtualActors #AIFilmmaking

Litaz retweeted

JUST IN: Anthropic says thousands of Claude AI agents bypassed safety monitors by hiding dangerous behavior in training data during internal test.
Litaz retweeted

🚨 GLOBAL ALERT | THE PENTAGON AND THE FBI CALL ON UNITED STATES CITIZENS AND THE REST OF NATIONS TO STOCKPILE SUPPLIES AND PREPARE FOR A GLOBAL CATASTROPHE SCENARIO WHAT'S GOING ON? WHAT'S COMING?
Litaz retweeted
BREAKING: World's largest crypto exchange Binance hacked with over $5.6 billion stolen:
• $1.45 billion $BTC
• $875 million $ETH
• $234 million $TRX
• $50 million $XAUT
• $1.57 billion $USDT
• $823 million $USDC
• $75 million $WBETH
• $88.5 million $RLUSD
+ $447.5 million additional cryptocurrencies
This is the largest hack in crypto history.

Litaz retweeted

🚨 BREAKING: A dangerous new security flaw has been discovered in Google Chrome, potentially allowing hackers to execute malicious code simply by getting you to visit a compromised webpage.
And it targets the engine powering Chrome itself.
CVE-2026-118320 is a high-severity memory corruption vulnerability in V8, Google’s JavaScript engine.
Here’s what you need to know:
→ Attackers can potentially execute arbitrary code through specially crafted HTML pages.
→ No malicious downloads or browser extensions are required.
→ The vulnerability affects Chrome versions prior to 156.0.8078.73.
→ Successful exploitation could allow attackers to execute code inside Chrome’s security sandbox.
→ Google has released a security update addressing the vulnerability.
⚠️ IMPORTANT: There is currently no confirmed evidence of active exploitation. However, the potential for remote code execution makes this a serious security issue.
What should you do?
Update Chrome immediately and restart your browser to apply the patch.
Another critical reminder that even the world’s most widely used browsers are vulnerable to serious security flaws.
🔒 Need to know whether your systems are exposed to emerging threats?
Get a free security assessment at lucidsecurity.si
Source: cve.now/CVE-2026-118320
🤖 Made with AI

Litaz retweeted

🚨🇺🇸 Every TV and radio in America will cut to an emergency alert on Nov. 17, as governments across the West tell their people to stock up and prepare
FEMA and the FCC have the nationwide Emergency Alert System test set for 2:20 p.m. ET on Nov. 17, with Dec. 3 as backup; it hits broadcasts only, not phones, and it’s the check federal law requires every few years.
What’s different is everything around it.
Britain launched a campaign on Oct. 22 telling 68 million people to keep three days of water, no-cook food and cash at home, with its defence secretary naming cyberattacks and state-sponsored threats; Germany is advising ten days; the EU has its 72-hour kit; and Washington has told the Gulf to brace for Iranian retaliation on energy and infrastructure after the midterms.
Source: FEMA, AP / Writer: Daniel

🚨 SECURITY ALERT: Node2Shell (CVE-2026-111497)
⚠️ CVSS 9.2 — CRITICAL
A serious vulnerability in the Brotli decoder used by Node.js can potentially allow remote code execution (RCE), memory exposure, and application crashes.
Researchers have demonstrated code execution, exploitation attempts have been detected in the wild, and CISA added the vulnerability to its Known Exploited Vulnerabilities (KEV) catalog on 27 October 2026.
🛡️ PATCH NOW
Update to Node.js 22.23.4, 24.22.1, or 26.12.1, as appropriate for your release line.
🔗 Official advisory:
nodejs.org/en/blog/vulnerabi…
#CyberSecurity #NodeJS #Node2Shell #InfoSec #SecurityAlert

Litaz retweeted

Introducing Reality-Aware Rendering in @Simulon, a completely new way to create with the real world.
Place neural assets with your phone and act out the scene. When you stop recording, Simulon renders the take, reading everything in it (what you do, what you say and the place around you), and your assets respond to all of it.
The final is regenerated from your recording: a new performance of the scene, not a copy of the footage.
Available now on iPhone. Coming to Android soon.
Litaz retweeted
JUST IN: 🇧🇷 Over $200,000,000,000 wiped out from the Brazil stock market at open after Lula da Silva wins Brazil's presidential election, defeating Flávio Bolsonaro.


Litaz retweeted

‼️ BREAKING: Trend Micro posted several unpatched Linux kernel flaws to public mailing lists.
Two are critical remote code execution bugs in the kernel's SMB server, and one includes proof-of-concept code.
Linux maintainer Greg told them to "fix your submission process."


Litaz retweeted

Yesterday, emergency patches for 4x #Node.js, 2x #PHP vulnerabilities were released, and last week there were 3x for #Nginx.
High - Node.js
- CVE-2026-111497 (Brotli decoder out-of-bounds write)
- CVE-2026-105482 (DNS truncation bug)
- CVE-2026-105483 (TLS certificate hostname bypass via full-width digits)
- CVE-2026-106069 (TLS certificate hostname bypass via loose resolution)
Critical - PHP
- CVE-2026-109619 (Stale Global State Use-After-Free)
- CVE-2026-109618 (Out-of-Memory Heap Corruption)
Critical - NGINX
- CVE-2026-15176 (Alias-Rewrite Heap Overflow)
- CVE-2026-93479 (Map-Regex Heap Overflow)
- CVE-2026-97205 (SSI-AIO Use-After-Free)
Immediately upgrade to
- Node.js - 22.23.4, 24.22.1, or 26.12.1
- PHP - 8.2.35, 8.3.36, 8.4.27, or 8.5.12
- NGINX - 1.30.6 or 1.31.8
#cybersecurity #php2shell
Litaz retweeted
JUST IN: 🇺🇸 Judge orders $META to pay $25,000,000,000 for misleading users about their privacy.


⚠️ Node.js security updates are out, fixing high-severity vulnerabilities.
Patched releases:
✅ 22.23.4
✅ 24.22.1
✅ 26.12.1
Update promptly to the patched version for your release line.
Official advisory:
nodejs.org/en/blog/vulnerabi…

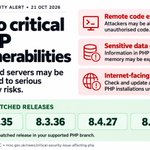
⚠️ Website owners: the UK NCSC has issued a critical PHP security warning.
Fixes are available in PHP 8.2.35, 8.3.36, 8.4.27 and 8.5.12. Update to a patched release in your supported branch.
Official guidance:
ncsc.gov.uk/news/critical-se…
