
Security Consultant @semperistech . Independent Security Researcher. Cyclist & Scubadiver. MSRC MVR 2022. "So di non sapere"
Joined May 2009
- Tweets1.9K
- Following323
- Followers9.4K
- Likes1.6K
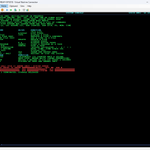



Tiny OS from scratch. Console looks like an IBM 3270 running TSO. Divide by zero? ABEND S0C9. READY
😅


Andrea P retweeted

In July, Microsoft fixed CVE-2026-50343, a Windows privilege escalation bug reported by Calif and 9 others, dubbed “Dark Elevator”.
But was it really fixed?
Ask @tiraniddo
projectzero.google/2026/09/w…


Andrea P retweeted

Been digging deep into the Windows Endpoint Security Platform (WESP) in Win11 25H2, definitely one of the most fascinating security features Microsoft has built in a while.
The concept is neat: compile rules to decision graphs in user mode, hand them to wesp.sys, and let the kernel evaluate them in-path while telemetry streams asynchronously in the background.
I did an AI-assisted reverse engineering dive into the whole stack (wesp.sys, espclient.dll, and wesp_elam.sys), documented the wire protocols, disposition tables, and the enforcement gate, and built esptool, a research harness with 118 XML rule docs so anyone can test live telemetry and in-kernel blocking.
Repo: github.com/marcosd4h/wesp_re…
Tech doc: github.com/marcosd4h/wesp-re…
Thanks to @yarden_shafir for putting this on my radar

AI may eventually become the new Cold War: everyone keeps building more powerful systems because they can’t afford to let the other side get ahead. Chip manufacturers may become the equivalent of uranium supplier controlling access to the resource that makes the race possible
Andrea P retweeted

askWAM - Requests Microsoft Entra access tokens silently through Windows Web Account Manager (WAM) by @_dirkjan
github.com/dirkjanm/askWAM


Super cool research from my colleague Shai Laron on new attack paths to Active Directory that can lead to full domain takeover 😜 . It was presented at Black Hat and he will be speaking again at DEF CON this weekend.
Don't miss this 💪 :
semperis.com/blog/identity-c…

Although this is a well-known topic, it's still one of my favorites. I put together a concise reference covering the most dangerous Windows privileges, how they can be abused, and why you should think twice before assigning them 👉 semperis.com/blog/windows-pr…


Andrea P retweeted

I just wrote a new blog on bypassing CA policies in Entra ID that have a resource exclusion, and why you probably want to enable baseline enforcement if you have such policies. Enjoy!
dirkjanm.io/bypassing-condit…
Andrea P retweeted

Regarding Active Directory permissions, most people assume that a Deny ACE always wins. It doesn't!
Windows stops the access check the moment enough rights are granted — any ACE after that point is never evaluated.
New post: managedpriv.com/blog/acl-can…

Turns out that the fix for the CVE-2020-17103 , the Cloud Filter HsmOsBlockPlaceholderAccess driver bug reported by @tiraniddo was never ported to Windows 11 / Server 2025 and still not fixed. LPE from user to SYSTEM 🤦♂️

I published a new "security research" post, and for once, it’s not about Windows 😅
This time I took a look at the myAudi connected vehicle platform and its APIs..🤓
Curiosity drives security research, no matter the target
Read it here 👇
decoder.cloud/2026/05/08/oh-…
