He/Him Content Creator Engineer, @codemod Core team, @solid_js Core team, @ripple_ts https://xitter.cf/t.co/bqdpqbi9T3 https://xitter.cf/t.co/TyM2hVeVuJ
Wichita, KS
Joined December 2012
- Tweets20.1K
- Following1.6K
- Followers15.8K
- Likes67.3K







Pinned Tweet
Everyone wants to do Code Mode agents
No one is truly embracing Code Mode
So I made a new agent with Code Mode as the foundation
Meet OC++ (a fork of @opencode)
youtu.be/RTJZRF2sotg?si=r9fC…


Dev Agrawal retweeted

I am here once again to say “put up or shut up”
One million to open source this year, as we continue to give back to the ecosystem via the pledge.
More than half has gone directly to your favorite open source developers.
blog.sentry.io/another-year-…


best part about migrations like this, they help us catch and fix a bunch of issues
pointed opus to openclaw's solid migration PRs and it already found atleast 7 issues that can be fixed in the framework and documentation to make this sort of work even smoother.

Two weeks ago I kicked off a loop to move OpenClaw's Lit-based Web frontend to Solid 2.0.
Took ~6 days until we could remove Lit, and another week to move patterns to idiomatic Solid.
I checked in with the session every other day, overall the process was mostly automatic. Took about ~600 PRs.
Result: Smaller JS and CSS footprint and much more fine-grained update control. Everything feeling more snappy and responsive. team.openclaw.ai/chat/robocl…


“Would I still choose Solid for this UI?
Yes—because of architectural fit and predictable update scope.”
I love this new world where you don’t need to know why Solid is better for your app, your agents already know and can help you make that choice
Two weeks ago I kicked off a loop to move OpenClaw's Lit-based Web frontend to Solid 2.0.
Took ~6 days until we could remove Lit, and another week to move patterns to idiomatic Solid.
I checked in with the session every other day, overall the process was mostly automatic. Took about ~600 PRs.
Result: Smaller JS and CSS footprint and much more fine-grained update control. Everything feeling more snappy and responsive. team.openclaw.ai/chat/robocl…
Turns out good abstractions are beneficial for agents
You are doing your agents a disservice by not giving them the best tools available today
Two weeks ago I kicked off a loop to move OpenClaw's Lit-based Web frontend to Solid 2.0.
Took ~6 days until we could remove Lit, and another week to move patterns to idiomatic Solid.
I checked in with the session every other day, overall the process was mostly automatic. Took about ~600 PRs.
Result: Smaller JS and CSS footprint and much more fine-grained update control. Everything feeling more snappy and responsive. team.openclaw.ai/chat/robocl…
Dev Agrawal retweeted

Openbot is 100% written in @solid_js 2
thank you @RyanCarniato for saving me billions of tokens on broken useEffect
the fact that big ai labs called it a "distillation attack" has caused so much confusion among people
DISTILLATION IS NOT A FORM OF "ATTACK"
distillation is an ML technique used to transfer knowledge from a larger model into a smaller model
the only reason labs suffix it with "attack" is because of some misguided idea that no one should use data from their models (that people pay for) to train their own models. it has literally nothing to do with cybersecurity and everything to do with labs playing dirty tricks to keep their competitive edge just a little bit longer
distillation is not something you do to hack into someone's servers.

> Distillation attacks from godless commies provides a bit of sympathy
no it doesn't, why do people keep saying that


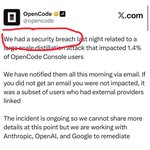
The first 5 words of the announcement are “We had a security breach”
The utter lack of reading comprehension is insane

"A large scale distillation attack". Yeah, sure. Come on guys.
This is a security breach. Call things by their names. @thdxr what are you doing? You are good guys. Dont do this corporate bullshit. We all understand.
OpenCode had a breach. Stored OpenAI, Anthropic and Google keys of 1.4% of Console users were exposed, and people are posting drained balances. $400 overnight, $1,700 for another guy.
This is not distillation. Someone got into your system and took peoples keys.
But "distillation" is the scary word of the year, so now every bad thing gets that label. Stolen keys, bans, export controls, all of it.
My local models dont have an API key. There is nothing on my rig to drain.
Some folks really need to learn to have some patience and empathy towards folks going through ongoing incidents at scale
(I had to as well, courtesy of @tweetsbycolin)
Including the rando startups that are so confidently posting “tHiS is wHy yOu sHouLd uSe Us” as if they have completely bulletproof security
If a company hasn’t been hacked yet it’s either because they have an army of security engineers or because they have no users

Dev Agrawal retweeted

It’s incredible how professional this group is (especially based on how much they shit post). There might not be a denser group of talent on a team who are also adults.

We had a security breach last night related to a large scale distillation attack that impacted 1.4% of OpenCode Console users
We have notified them all this morning via email. If you did not get an email you were not impacted, it was a subset of users who had external providers linked
The incident is ongoing so we cannot share more details at this point but we are working with Anthropic, OpenAI, and Google to remediate
