

Eigenaar Mediativity®, Stadsregisseur Wijk bij Duurstede, Adviseur Anna’s Smaakatelier, co-auteur Dwarsdenkers. #teampositief #teamtaart
Wijk bij Duurstede, Nederland
Joined November 2009
- Tweets57.7K
- Following957
- Followers1.2K
- Likes31K




Pinned Tweet
Boek Dwarsdenkers succesvol gelanceerd: ondernemersboek zet positieve verandering in beweging
destadamersfoort.nl/lokaal/z… @StadAmersfoort Te bestellen via: boekdwarsdenkers.nl

De verschillen op deze aspecten zijn kleiner dan ik dacht. Verschillen in verhitting na fermentatie, aantal levende yoghurtbacteriën en lactosegehalte blijven onduidelijk. Geen van beide merken publiceert alle gegevens die nodig zijn voor een goede wetenschappelijke vergelijking.
🤖 Made with AI

Dodoni vs. AH huismerk Griekse yoghurt (10% vet). Wat zit erin?
Dodoni: melk, room, yoghurtculturen.
AH: volle yoghurt.
Beide zonder toegevoegde suiker. Maar per 100 gram bevat Dodoni 5,9 g eiwit tegenover 4,5 g bij AH. Meer eiwit dus, maar rechtvaardigt dat het prijsverschil?
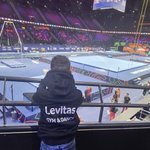
Liefde is…
samen WK Turnen kijken op TV en content posten op het Instagram account van turnvereniging Levitas Gym & Dance.
levitasgymdance.nl

Een eigen appartement voor €196.000? Jazeker, het kan nog! In Enschede staat er eentje te koop. Voor dat bedrag vind je tegenwoordig bijna nergens meer een eigen plek. Ideaal voor starters! Wie grijpt deze kans?
funda.nl/detail/koop/ensched…
#Enschede #TeKoop #Starterswoning
Goed verhaal. Lekker kort.

So basically, today PHP got two critical bugs that let anyone run code on your server without even logging in, which is bad, and then the details leaked before the patch was even out, which is worse, and it works on WordPress and MediaWiki and Magento and Joomla and Laravel, and Censys says like 1.5 million servers are running a version with no fix, so the NSA was like "take your system offline," and the FBI was like "take your system offline," and CISA and the UK and CERT-EU were all like "take your system offline," and then the Prime Minister of Japan, the actual Prime Minister, posted at 5:55 in the morning telling 48.8 million people to take their system offline, so everyone took their system offline, like the Dutch cybersecurity agency took its own website offline, and the Dutch parliament went offline, and the Port of Rotterdam went offline, and Finland and France and Denmark started pulling government sites, and Wikipedia went down, and Archive.org went down, and Asana and GOG and Something Awful went down, and the University of Vienna's webmail went down for some reason, and that's just PHP. Because GitLab also dropped a CVSS 10.0, which is the highest score they give out, for a bug that's been there since 2014, so that's every self-hosted GitLab for twelve years, and then LiteLLM 1.107.0 got hijacked and shipped a credential stealer and a remote access trojan in every single wheel and the Docker images, including latest, and you didn't even have to import it, just installing it was enough, and it's the second time this year, and then Railway paused every deployment on the entire platform because someone got into the environment variables, so now everyone has to rotate every secret they've ever stored there, and TiDB Cloud said someone was walking around inside with stolen credentials for basically a month and an extortion group says they took 10.6 terabytes, and Zeabur got breached for the second time in two months and is just shutting down, like the whole company, and Node.js patched remote code execution and a TLS bypass, and CISA says Plex is being actively exploited, and someone took over 300 Tor exit relays to steal SSH passwords, and SafePay ransomware has hit over 600 critical infrastructure orgs, and India's biggest bank filed a data loss incident, and Japan has been in an official state of emergency in cyberspace since October 9, which honestly explains the 5:55 AM post. Oh, and eMudhra, a certificate authority that's issued over 60 million certificates, whose entire job is proving websites are who they say they are, was supposed to be using private keys that are random numbers over a hundred digits long, and one of them was 4. Just 4. And the others were like 66 and 237. Anyway, it's Wednesday.
Ik zie ‘t voor me. 🙈

Security called me at 6:12 AM today.
"Patch every PHP server immediately."
I asked what happened.
"Two critical vulnerabilities. Remote code execution. No authentication required."
Cool.
How many PHP servers do we have?
According to inventory: 12
According to reality:
Nobody knows.
We found one running WordPress.
Three running old internal tools.
One under someone's desk.
Two inside vendor appliances.
A forgotten employee directory from 2016.
And a server named:
PHP-OLD-DO-NOT-TOUCH
Naturally, that one runs payroll exports.
Then we found a PHP 5.6 box.
I asked who owned it.
The documentation said:
BRIAN.
Brian left in 2019.
We called Brian.
He said:
"Oh wow, that's still running?"
Excellent.
By 8 AM, leadership joined the incident call.
CEO:
"Can hackers actually get in?"
Security:
"Potentially yes."
CEO:
"Without a password?"
Security:
"Yes."
CEO:
"Then why do WE need passwords?"
Not the lesson.
Finance asked if we could wait until the weekend to patch because downtime affects revenue.
Security explained that the alternative was letting strangers execute code on our servers.
Finance asked for a cost comparison.
At 9:17, someone suggested temporarily taking the vulnerable websites offline.
Marketing refused.
"Our campaign is live."
So for the next hour, the company officially decided maintaining a landing page for 20% off webinar registration was more important than preventing remote server takeover.
We finally patched everything we could find.
Then our scanner discovered another PHP server.
Hostname:
TEMP-PHP-2014
Uptime:
4,512 days.
Nobody knows what it does.
Nobody owns it.
Nobody can shut it down.
But every time we block network access, the warehouse stops printing shipping labels.
Security has classified it as critical infrastructure.
It is running PHP 5.4.
The vulnerability has existed longer than half our employees.
The emergency patch took four hours.
Finding out what PHP actually runs took eleven.
The internet isn't held together with code.
It's held together with servers everyone is afraid to turn off.
Tejo. retweeted

PHP changes are live. Start patching. php.net/archive/2026.php#202…
Huge thanks to coordinated work by @ThePHPF!


PHP sites behind Cloudflare already have an initial set of WAF rules deployed for the known exploit vectors in these vulnerabilities. The rules are available to all customers, including free.
We are seeing early attacks emerging and are updating mitigations as new vectors show up.
This is a STOPGAP only. Patch as soon as @ThePHPF releases the update at 14:00 UTC today.

Vers uit Amersfoort: Oma’s Appeltaart van Anna’s Smaakatelier. Maakt van een gewone woensdag een feestdag!
annasmaakatelier.nl/webshop/…
#appeltaart #teamtaart #amersfoort #annasmaakatelier


Ik dacht dat ik vanmorgen de camping opreed, maar ik reed Amersfoort binnen waar je tegenwoordig 30km/u moet. 🙈
Deze gast is zo grappig!
Phil Rosenthal bezoekt Amsterdam in het 8ste seizoen van de Netflix-serie Somebody Feed Phil.
philrosenthalworld.com/citie…


“Huize Soria bleek geen vergunning te hebben voor het leveren van jeugdzorg in Spanje. Geen van de organisaties die er jongeren plaatsten, controleerde dat.” 😢

Vreselijk dit! @lisawesterveld al onze steun bij haar jarenlange strijd voor verbetering van de jeugdzorg!
nos.nl/l/2635898
