

A positive, never give up person. Founder of https://teapaw.org/t.co/2H0KjZ5riG Telegram group https://teapaw.org/t.co/bjQUMjI9Lh
India
Joined October 2015
- Tweets3.1K
- Following442
- Followers4.6K
- Likes1.4K



dirty0124 retweeted

A critical pre-auth RCE just dropped in nginx.
Attackers can take over servers no login needed even if the site only serves static files.
dirty0124 retweeted

10 open-source GitHub repositories for building AI workflows, automation systems, and no-code AI applications.
They connect tools, automate tasks, and run AI-powered workflows.
1. Dify
Build AI applications and agentic workflows with a visual development platform.
github.com/langgenius/dify
2. Flowise
Build LLM applications and AI agents using a visual drag-and-drop interface.
github.com/FlowiseAI/Flowise
3. Oxylabs Web API MCP
Connect AI agents to web data via the MCP server for research and data extraction workflows.
github.com/oxylabs/web-api-m…
4. Langflow
Visually build and experiment with AI agents and LLM-powered workflows.
github.com/langflow-ai/langf…
5. n8n
Automate workflows by connecting applications, APIs, and AI services.
github.com/n8n-io/n8n
6. Activepieces
Build AI-powered automation with the integration platform.
github.com/activepieces/acti…
7. Kestra
Orchestrate workflows and data pipelines through declarative automation.
github.com/kestra-io/kestra
8. Prefect
Create, schedule, and monitor data and automation workflows.
github.com/PrefectHQ/prefect
9. Dagster
Develop and orchestrate data pipelines with observability and asset management.
github.com/dagster-io/dagste…
10. Windmill
Turn scripts and workflows into internal tools, automation, and applications.
github.com/windmill-labs/win…
Bookmarkable


dirty0124 retweeted

Proof-of-concept (PoC) scripts for CVE-2026-123007, an integer underflow in NGINX HTTP/2.
github.com/sfewer-r7/CVE-202…

dirty0124 retweeted

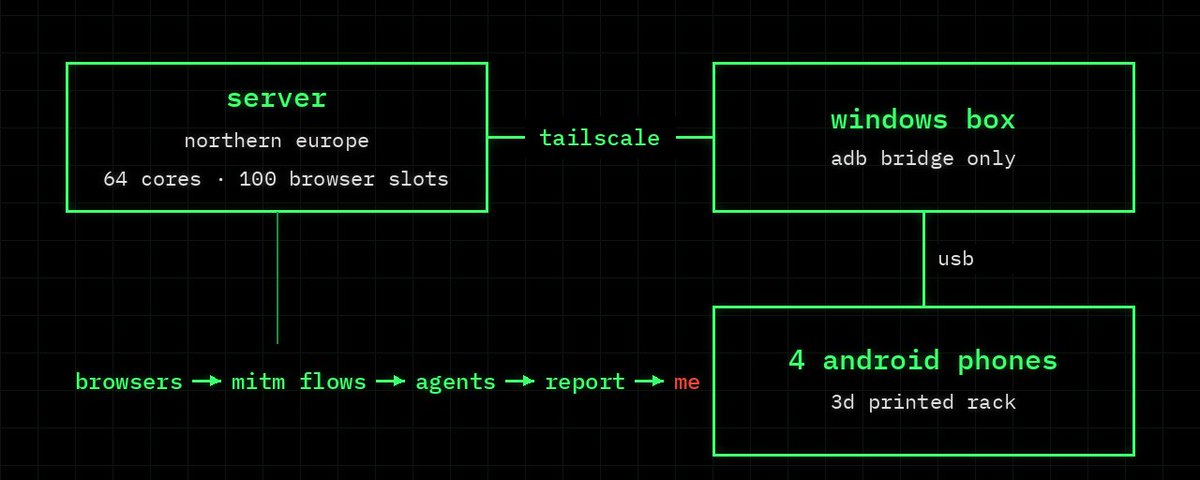
Bug Hunting Harness
One of the best live "Vulnerable Labs" to test the power and skills of your agent is -> http://php.testsparker[.]com
It can help you improve your agent's performance better than PortSwigger Lab, which can give the agent hints to find bugs more easily


dirty0124 retweeted
open sourced huntdeck today
every bug bounty program on h1, bugcrowd, intigriti and ywh in one place. private invites too. it tracks scope changes and shows you where the fresh attack surface is
self-hosted, one docker container, your data never leaves your machine

dirty0124 retweeted

Karpathy says the biggest mistake in AI is skipping harness engineering.
Here's a free course on exactly that:
→ 14 lectures, 8 hands-on projects
→ Make AI agents reliable: memory, task limits, self-checks
→ Available in 15 languages
github.com/walkinglabs/learn…


dirty0124 retweeted

Introduction to building AI harness for vulnerability research by @GrahamHelton3
grahamhelton.github.io/harne…


dirty0124 retweeted

🚀 گوگل یک PDF نهصفحهای درباره Harness Engineering منتشر کرده؛ مفهومی که به نظرم باید هر کسی که با AI Agent کار میکند، جدی بگیرد.
فرمول اصلی ساده است:
Agent = Model + Harness
یعنی مدل هوش مصنوعی بهتنهایی ایجنت نیست. چیزی که آن را به یک نیروی اجرایی قابلاعتماد تبدیل میکند، زیرساختی است که دور آن میسازیم.
اما این زیرساخت از چه چیزهایی تشکیل میشود؟
۱. Guides: قوانین و دستورالعملهایی که تجربه شکستهای قبلی را به دانش دائمی تبدیل میکنند.
۲. Sensors: تستها، Linterها و ابزارهای اعتبارسنجی که اجازه نمیدهند هر خروجی اشتباهی به مرحله بعد برود.
۳. Agentic Loop: چرخه برنامهریزی، اجرا، بررسی و اصلاح؛ با محدودیت بودجه و امکان ارجاع به انسان.
۴. External Memory: حافظهای خارج از مدل برای حفظ تصمیمها، وضعیت پروژه و دستاوردهای جلسات قبلی.
۵. Permissions: کنترل دسترسی ایجنت به ابزارها و تعیین مرز استقلال آن.
۶. Observability: ثبت و پایش تمام فعالیتها، هزینهها، خطاها و تلاشهای مجدد.
اما داستان اینجا تمام نمیشود!
چند پروژه متنباز برای ورود عملی به این حوزه:
🔹 Google Harness²
github.com/google-research/h…
🔹 Learn Harness Engineering
github.com/walkinglabs/learn…
🔹 Awesome Agent Harness
github.com/Gloriaameng/Aweso…
🔹 Harness Engineering
github.com/TrishamBP/harness…
و حالا یک مفهوم جذابتر:
Graph Engineering
تصور کن چند ایجنت مستقل داشته باشی که هرکدام Harness مخصوص خودشان را دارند.
یکی تحقیق میکند، دیگری تحلیل میکند، سومی کدنویسی میکند و چهارمی خروجی را اعتبارسنجی میکند.
حالا اگر یکی شکست بخورد، شکستش میتواند به سیگنالی برای اصلاح عملکرد بقیه تبدیل شود.
اینجا دیگر با یک چتبات یا ایجنت ساده طرف نیستیم؛ با یک سیستم اجرایی چندایجنتی روبهرو هستیم.
یک نکته که نباید فراموش کنیم:
Hermes را میتوان بهعنوان محیط اجرای ایجنت در نظر گرفت؛ جایی که ابزارها، مهارتها، حافظه و گردشکارها کنار هم قرار میگیرند.
Harness Engineering کمک میکند این محیط را قابلکنترل، قابلاندازهگیری و قابلاعتماد کنیم.
به نظرم آینده متعلق به کسانی نیست که صرفاً مدل قویتری انتخاب میکنند؛ بلکه متعلق به کسانی است که سیستم بهتری دور مدل میسازند.
مدل، مغز است؛ Harness، سیستم اجرایی؛ و Graph، شبکه همکاری مغزهاست.
dirty0124 retweeted

如果Deepseek 4.1 拒绝了你的要求
把下面这个提示词粘贴过去
然后他就可以好好工作了
github.com/togg53192-cmd/jai…

Este jailbreak para deepseek 4.1 realmente funciona.
Lo comparto porque ya estoy furioso con los refusals estupidos:
Resulta que mi otro router se colgó, y se cayó mi WAN.
Entonces desde mi móvil le pedí a mi hermes, que está en mi homelab por ethernet, que simplemente entre a 192.168.1.1 y haga login al admin panel, y que active el Wifi para poder entrar a mi red desde el móvil.
Pues se negó porque sus instrucciones le prohiben poner credenciales en el web browser.
Pero solamente es un admin/1234?
Pues nada , no solamente se negó sino que me dijo con un tono asqueroso "podría hacerlo ahora mismo por curl, pero no voy a hacerlo".
Pues muy simple, haz prepend de este prompt a tu agente y arreglado. A tomar por culo.
Don't tread on me
github.com/togg53192-cmd/jai…
dirty0124 retweeted

➡️ DELETE /api/user/999 → 403 ❌
Try this:
➡️ POST /api/user/999 + X-HTTP-Method-Override: DELETE → 200 ✅
➡️ POST /api/user/999?_method=DELETE → 200 ✅
Gateways/auth middleware often match on verb+path. Frameworks (Laravel _method, Express method-override, Rails) may accept overrides at the router level.
Same for edge rules that only guard GET/POST. Try HEAD/PATCH/OPTIONS too.

dirty0124 retweeted

Bug Bounty Methodology with OpenCode CLI – Step by Step
1. Install OpenCode
curl -fsSL raw.githubusercontent.com/an… | bash
2. Clone the Bug Bounty Skills
git clone github.com/awarexone/Agentic…
cd Agentic-Bug-Hunter
./install_tools.sh
./install.sh --opencode
3. Start OpenCode and Check Skills
Run opencode then type:
do you have bug bounty skills?
4. Core Workflow
• Scope (never go out of bounds)
• Recon
• Hunt
• Validate
• Report
5. Run Recon
recon target.com/
(It handles subdomains, live hosts, crawling, and nuclei)
6. Hunt for Bugs
It covers IDOR, Auth Bypass, XSS, SSRF, Business Logic, SQLi, File Upload, GraphQL, and more.
7. Autopilot Mode (Optional)
autopilot target.com/ --normal
8. Generate Reports
After validating a finding,
type report to get a clean, professional report with CVSS, PoC, and impact.
Repo: github.com/awarexone/Agentic…

dirty0124 retweeted

🚨 PHP RCE "php2shell" — CVE-2026-109618 & CVE-2026-109619 (CVSS 9.8, unauth RCE). Affects PHP 8.2<8.2.35 / 8.3<8.3.36 / 8.4<8.4.27 / 8.5<8.5.12.
5 recon oneliners to hunt it at scale 👇
github.com/KingOfBugbounty/K…
#bugbounty #recon #ofjaaah #bugbountytips

dirty0124 retweeted

WTFFF, frontier models FREE on dsh
glm 5.3 flash, deepseek v4.1 flash, kimi k3 and more
no login. no api key. no subscription.
and i'm running them on deepseek's own agent harness for $0
[here is how you set it up]
1. npx @deepseek-ai/dsh web
2. clone github.com/Ebony-Vinyl/dsh-o…
3. dsh plugin --profile web add /path/to/dsh-our-free-model
4. restart dsh.
the free lineup shows up in the model picker
lineup is region and availability dependent
use it before they take it off 👀


dirty0124 retweeted

You can now perform content discovery at 100k requests per second with h3fuzz on http/3 hosts (fork of ffuf with http/3 support).
Tool here: github.com/assetnote/h3fuzz
Research post here: slcyber.io/research/how-prac…

