

Real-time threat intelligence & response for #Web3. Detect threats. Stop exploits. By @hackenclub
Joined April 2025
- Tweets195
- Following30
- Followers269
- Likes59




The Architecture of Institutional Trust | Online Panel teapaw.org/i/broadcasts/1XxyggWgQ…
EU Crypto Regulations | Panel Discussion teapaw.org/i/broadcasts/1NGaraPgM…
Continuous Protection | Q1’26 Report Panel teapaw.org/i/broadcasts/1RJjpzjyo…
New Era of Digital Assets Security | 2026 Experts Discussion teapaw.org/i/broadcasts/1eaKbjaOE…

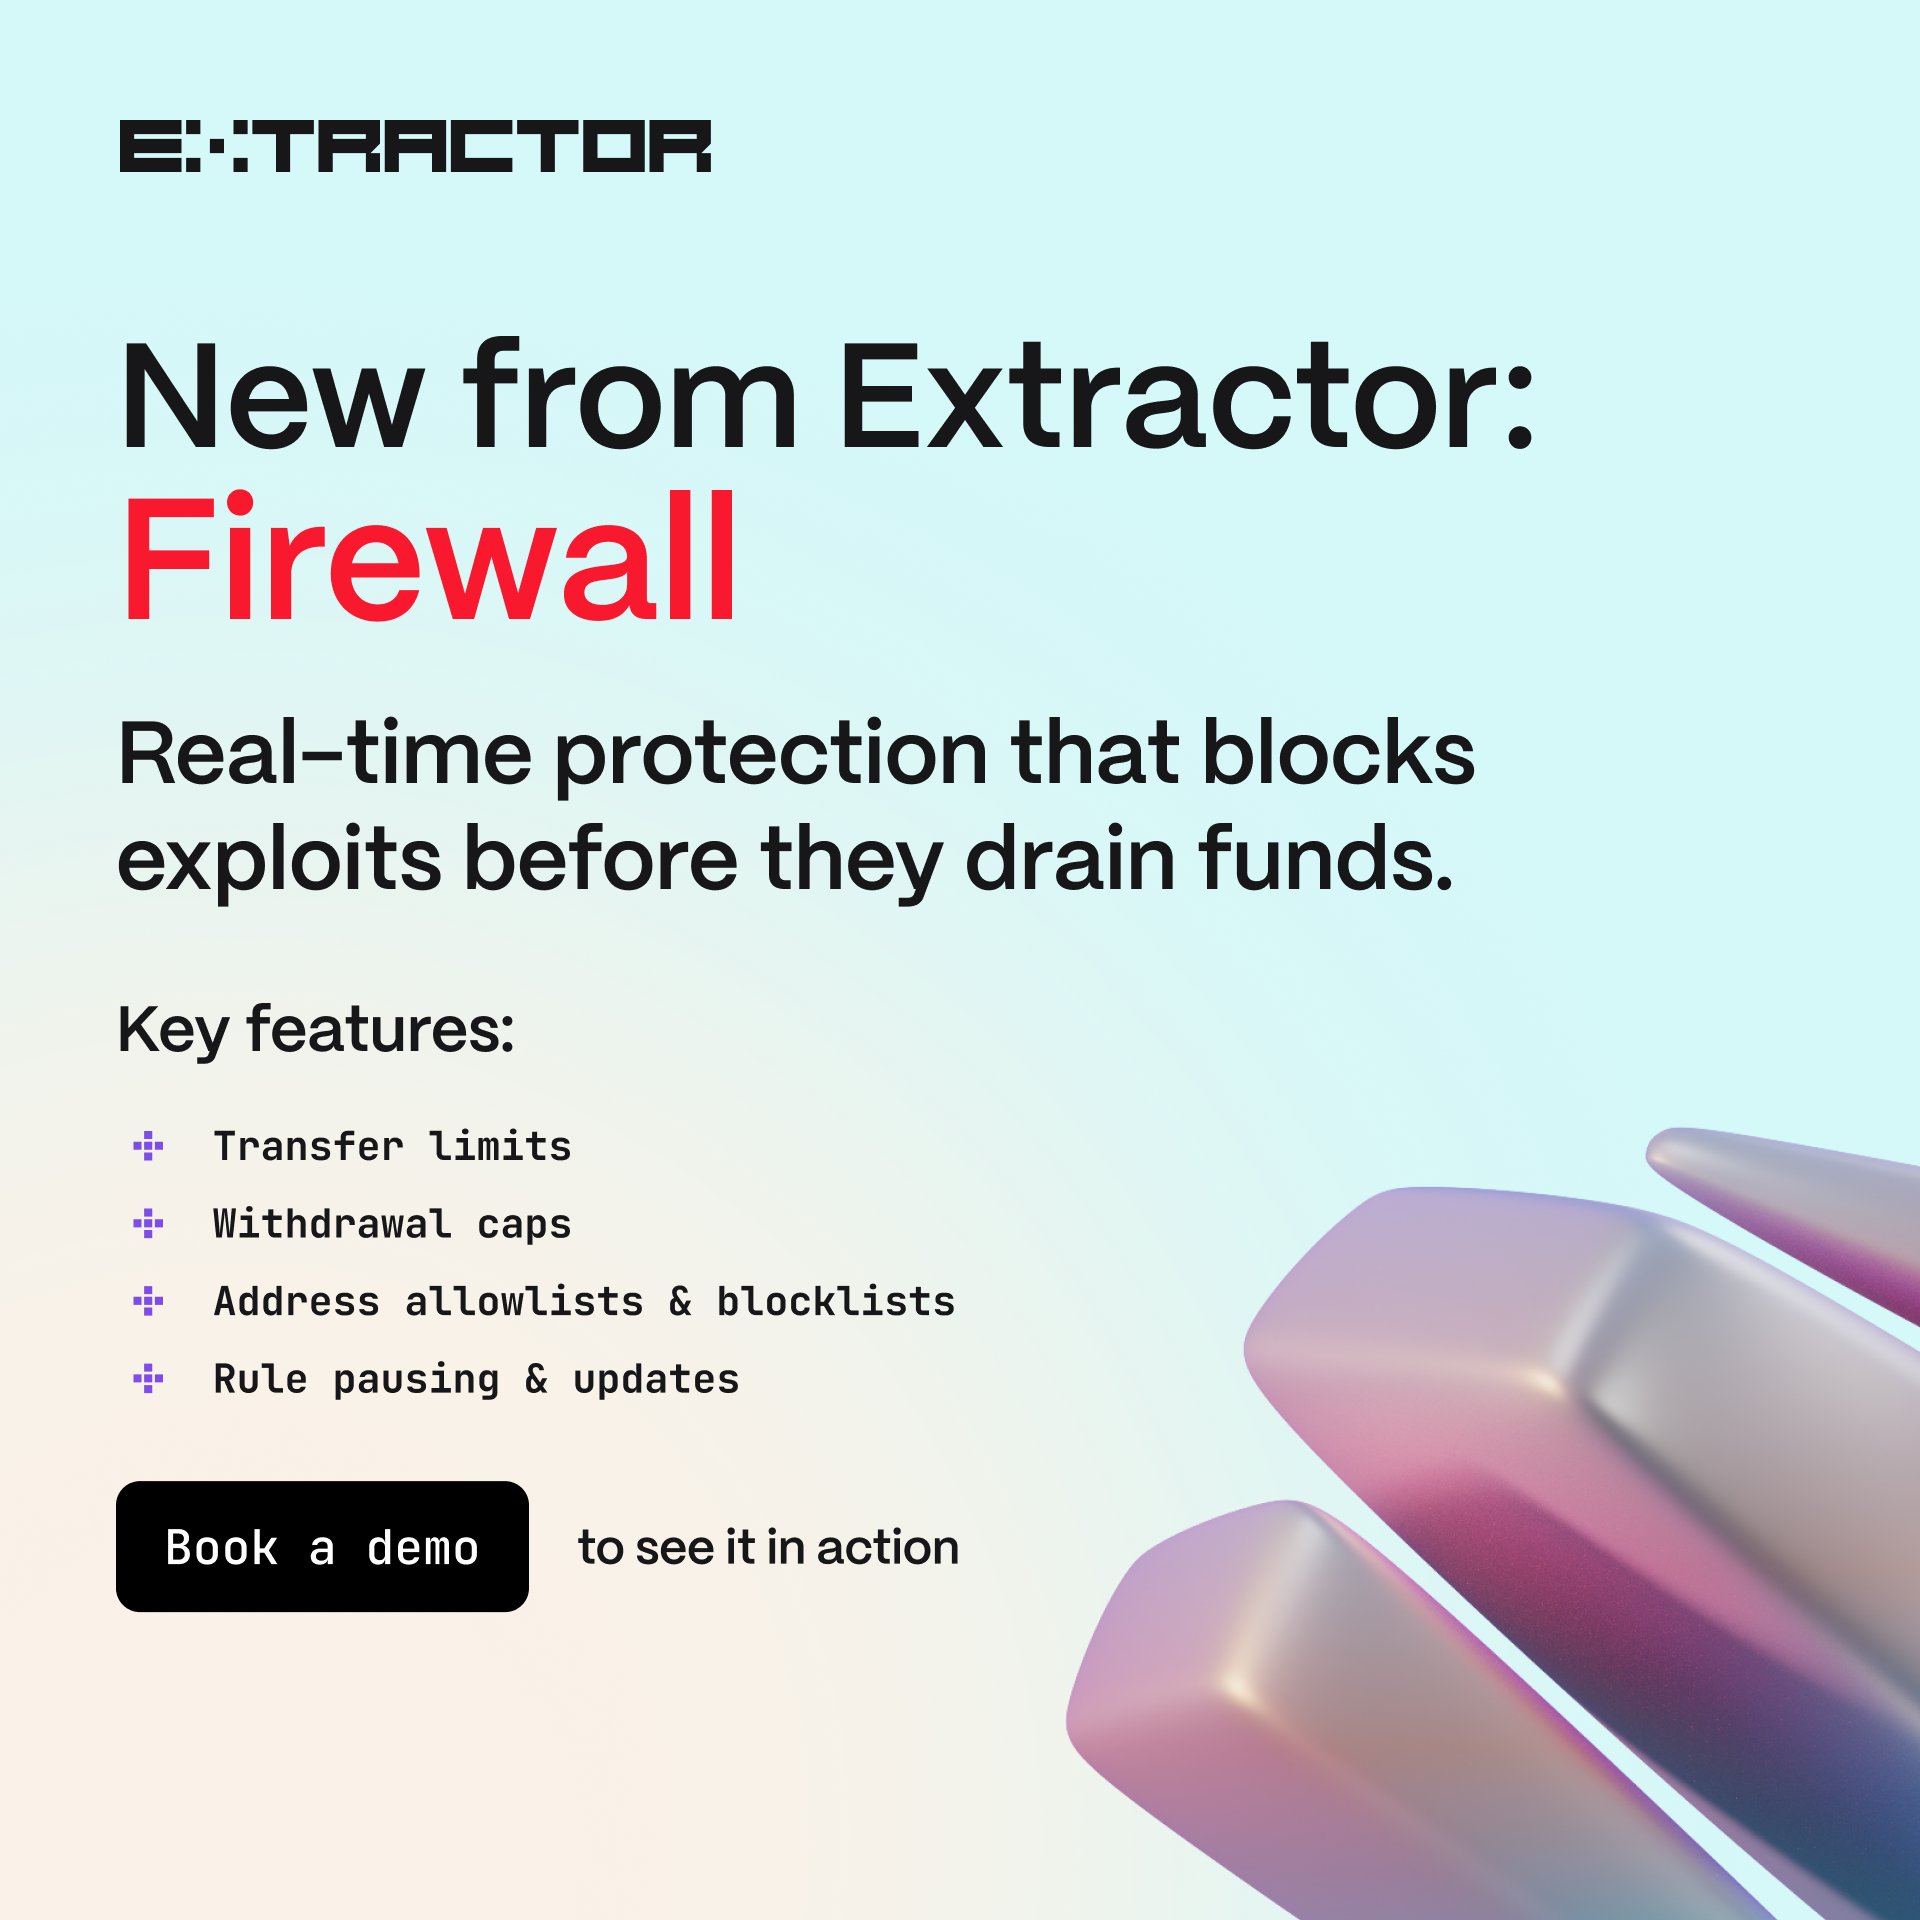
📢 New from Extractor: Firewall
A tool for smart contract teams who want to stop exploits – not just study them after the fact.
It lets you set enforceable rules that block high-risk behavior before damage is done.
Here’s how it works 🧵
For teams serious about minimizing exploit risk, Firewall isn’t optional.
It’s the missing layer between passive detection and real enforcement.
📖 Read the full breakdown: hackenio.cc/extractor-firewa…

🛡️ Ready to see how it works?
Book a demo: hackenio.cc/extractor-demo

💔 Looks like user lost 4,556 ETH (worth of $12.3M) in address poisoning attack 1 hour ago.
Transfer txn: etherscan.io/tx/0x7facade9d4…
The "right" address seems to be 0x6D90CC (etherscan.io/address/0x6d90c…), but instead, ETH was mistakenly sent to 0x6d9052 (etherscan.io/address/0x6d905…)

Two exploits tonight across two different projects – SwapNet and @ApertureFinance.
Both caused by unrestricted malicious arbitrary external calls, allowing anyone to drain wallets that had previously approved tokens to the Router.
Total losses: ~$17.2M
Recap & analysis 👇🧵

Project 2, @ApertureFinance, drained for ~$3.2M.
Vulnerable contract:
0xD83d960deBEC397fB149b51F8F37DD3B5CFA8913
2025 Crypto Security Wrap-Up | Webinar teapaw.org/i/broadcasts/1YqJDNeEZ…
🚨Alert: @yield has lost ~$3.73M due to a slippage in Vault operation of swapping stkGHO to USDC.
3.84M GHO was swapped to only 112K USDC – a net loss of ≈$3.73M.
Swap Tx: etherscan.io/tx/0x6aff59e800…
More insights to follow 🧵

Uniswap V4 Liquidity Providers were beneficiaries and the Yield team has messaged to one of the LPs on-chain:
“You retain 10% as a bug bounty, return the rest.”
But no official statement has been posted on @yield’s socials yet.
On-chain msg: etherscan.io/tx/0x816cc2d41c…

🚨 Alert 🚨 @Truebitprotocol was exploited for 8,535 ETH ($26.5M) due to vulnerability in smart contract Truebit Protocol: Purchase (etherscan.io/address/0x764c6…)
Details in the thread below👇

Attack transaction: etherscan.io/tx/0xcd47556455…
Malicious contract was deployed right before the attack (in the same block) via private mempool with attack contract deployment at block position 3 and attack transaction at block position 4:

After the attack, most of the funds were distributed to two several wallets where stolen ETH is held at the moment.
Initial theft wallet: etherscan.io/address/0x6c8ec…
Laundering wallet 1: etherscan.io/address/0x27358…
Laundering wallet 2:
etherscan.io/address/0x3b581…
Laundering wallet 3: etherscan.io/address/0x62afd…
