

Senior Security Engineer | Cloud Security (Azure) · DevSecOps · ISO 27001 · ISO 22301 · ISO 20000 · PCI DSS · SWIFT CSP | Securing Cross-Border Payments
Nigeria
Joined December 2019
- Tweets1.6K
- Following1.5K
- Followers735
- Likes1.3K




Careers: certificates open interviews, but projects pass them. Bring something you built, tested and can explain.
Question: what do you want more of here in November: quick fixes, attack walkthroughs, AI app security, or career advice?
Myth: "Security slows us down." Fact: rework after an incident slows you down far more. Small checks during development are the fast option.
Code review: search for verify=False, rejectUnauthorized: false and InsecureSkipVerify. Switched-off certificate checks tend to survive into production.
Founder checklist: staff use a company password manager, and you can remove someone's access to every shared password in one step.
Cloud: look for access keys older than 90 days. Rotate them, or better, replace them with roles that need no long-lived keys.
Walkthrough: the OTP is checked in the app, not on the server. Change the response to "valid": true and you are in. Fix: verify every OTP on the server.
Security awareness training: 45 minutes.
Time until someone reads a password out on a call "because it's faster": 46 minutes.
AI apps: treat model output like user input. If it ends up in HTML, SQL or a shell command, encode or validate it first.
Fintech: make sure sandbox keys can never move real money, and live keys never appear in test environments.
API tip: GraphQL needs limits on query depth and size, and introspection off in production unless you really need it.
Sunday fix: check your email forwarding rules. Someone who gets into a mailbox often adds a quiet rule that copies everything out.
Plain words: "zero trust" means no device or user is trusted just because it is on the office network. Every request proves who it is.
Sunday nudge: back up your phone's photos and documents somewhere you control. A lost phone hurts less with a backup.
Saturday reflection: security gets easier when you stop trying to fix everything and fix the top three properly.
OWASP in plain words: Authentication failures. Weak passwords allowed, no brute-force limits, sessions that never expire. The login is your front door, so test it like one.
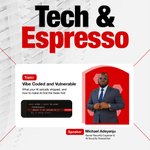
Speaking at Tech & Espresso next Saturday ☕
“Vibe Coded and Vulnerable”: the holes AI keeps shipping, and how to make AI find them first.
📅 Sat 14 Nov, 2PM
📍 Café One Yaba, Lagos
Free, limited seats 👇
cafeone.ng/events/tech-espre…

Explaining AppSec at a family gathering:
"I find weak spots in apps before criminals do."
Aunty: "So you are a hacker."
"A good one."
Aunty: "Fix my WhatsApp."