

나보리. 크립토 3년째. 번거 쥐뿔도 없지만 코인세금반대청원 항상 1빠로함
Joined November 2022
- Tweets13.3K
- Following3.1K
- Followers2.7K
- Likes14.4K




Pinned Tweet
300 USDT 또는 BBW 방콕 여행 지원금을 주는 프로젝트가 있다?!
Renaiss Questline Season 5 — Mission 1
안녕하세요! Renaiss에 진심인 보리입니다!! ❤️
최근 Renaiss와 Four.meme가 함께 특별한 콜라보 캠페인을 진행하고 있는데요!!
이번 이벤트는 총 18개의 밈 캐릭터 중 하나를 선택해 자신만의 얼터너티브 아트 카드를 디자인하는 캠페인입니다!!ㅎㅎ
저도 이번 기회에 직접 카드를 만들어봤어요!! >3<
제가 선택한 캐릭터는 MUBARAK!!
카드 제목은 THE DAWN OF A GOLDEN ERA로,
두 프로젝트의 만남을 통해 새로운 황금시대가 시작된다는 의미를 담아봤습니다ㅎㅎ
이번 협업은 Renaiss의 카드 컬렉팅 경험과 Four.meme의 밈 문화를 결합했다는 점에서 의미가 있는데요!
Renaiss는 다양한 밈 캐릭터를 활용해 카드 콘텐츠의 범위를 넓힐 수 있고, Four.meme는 기존 밈 캐릭터들을 수집형 카드 아트로 선보일 수 있다는 장점이 있습니다.
또한 유저들이 직접 카드를 제작하고 공유하는 방식이라 두 커뮤니티 간의 교류에도 도움이 될 것으로 기대됩니다!!>3<
이번 캠페인에서는 총 10명의 우승자에게
300 USDT 또는 최대 1,000 USDT 상당의 BBW 방콕 여행 지원금 중 하나를 선택할 수 있는 기회가 주어진다고 해요!!
평소에는 Renaiss에서 카드를 개봉하는 입장이었는데, 이번에는 직접 카드를 디자인해볼 수 있어서 색다른 경험이었습니다ㅎㅎ
앞으로도 이런 다양한 콜라보 이벤트가 이어졌으면 좋겠네요!! ❤️
@renaissCLTB @fourdotmemezh @renaissxyz @RenaissKrCM @Plus_Ultra_715


🇹🇭 Your meme. Your card. On display in Bangkok.
🃏 The Renaiss × @fourdotmemezh UGC card design campaign is now live, with @BNBCHAIN as our ecosystem partner!
Choose from 18 designated Meme characters and create your own alternate-art card using the campaign’s co-branded card frame. Bring your pick to life with your own artwork and story.
币安人生, HAJIMI, BANANAS31… who will inspire your creation?
✨ We plan to showcase 10 winning designs at our booth during #BinanceBlockchainWeek
🎁 10 winners across three categories can each choose between a 300 USDT reward or up to 1,000 USDT in travel support!
🗓️ Entries are open now.
⏳ Ends: November 22, 17:59 (UTC+8)

Nabori | (❖,❖) retweeted
Renaiss의 첫 번째 생일을 축하합니다!! 🎂❤️
안녕하세요! Renaiss에 진심인 보리입니다!!
Renaiss가 런칭된 지 딱 1년이 되는 날이라고 해요!!ㅎㅎ
그동안 Renaiss와 함께하면서 카드 개봉부터 다양한 커뮤니티 이벤트, 해커톤까지 정말 많은 경험을 할 수 있었는데요!
단순히 카드를 수집하는 것뿐만 아니라 같은 관심사를 가진 분들과 소통하고 새로운 추억을 만들어갈 수 있어서 더욱 애정이 생긴 프로젝트인 것 같습니다ㅎㅎ
그리고 이번 1주년을 기념해 특별한 이벤트도 진행된다고 하는데요!
원피스 TCG 신제품 OP-18을 받을 수 있는 기회!!
참여 방법도 정말 간단해요!!
1. Renaiss 공식 1주년 기념 게시물에 좋아요 누르기!
2. 해당 게시물을 인용 리트윗하고 Renaiss의 1주년을 축하하는 메시지 작성하기!
추첨을 통해 총 3명에게 원피스 TCG 신제품 OP-18 증정!!
🔗 이벤트 게시물
teapaw.org/renaissCLTB/status/212…
앞으로 Renaiss가 2주년, 3주년을 맞이할 때도 함께 축하할 수 있었으면 좋겠네요ㅎㅎ
앞으로도 Renaiss에 진심인 보리로 활동하겠습니다!!
Happy 1st Anniversary, Renaiss!! ❤️
@renaissxyz @renaissCLTB @RenaissKrCM

From XYZ to Protocol.
The scenes flash by.
Suddenly, we’re right back there.
Today, Renaiss turns one. 🎂
Thank you for being with us every step of the way.
We hope you’ll be part of the memories still to come.
Like and QRT this post with a message for Renaiss. We’ll pick 3 participants at random to receive OP18. 🎁
Gacha. Marketplace. Staking.
SDK. CLI. Index. Fair.
What’s next? ✨
Renaiss의 첫 번째 생일을 축하합니다!! 🎂❤️
안녕하세요! Renaiss에 진심인 보리입니다!!
Renaiss가 런칭된 지 딱 1년이 되는 날이라고 해요!!ㅎㅎ
그동안 Renaiss와 함께하면서 카드 개봉부터 다양한 커뮤니티 이벤트, 해커톤까지 정말 많은 경험을 할 수 있었는데요!
단순히 카드를 수집하는 것뿐만 아니라 같은 관심사를 가진 분들과 소통하고 새로운 추억을 만들어갈 수 있어서 더욱 애정이 생긴 프로젝트인 것 같습니다ㅎㅎ
그리고 이번 1주년을 기념해 특별한 이벤트도 진행된다고 하는데요!
원피스 TCG 신제품 OP-18을 받을 수 있는 기회!!
참여 방법도 정말 간단해요!!
1. Renaiss 공식 1주년 기념 게시물에 좋아요 누르기!
2. 해당 게시물을 인용 리트윗하고 Renaiss의 1주년을 축하하는 메시지 작성하기!
추첨을 통해 총 3명에게 원피스 TCG 신제품 OP-18 증정!!
🔗 이벤트 게시물
teapaw.org/renaissCLTB/status/212…
앞으로 Renaiss가 2주년, 3주년을 맞이할 때도 함께 축하할 수 있었으면 좋겠네요ㅎㅎ
앞으로도 Renaiss에 진심인 보리로 활동하겠습니다!!
Happy 1st Anniversary, Renaiss!! ❤️
@renaissxyz @renaissCLTB @RenaissKrCM
From XYZ to Protocol.
The scenes flash by.
Suddenly, we’re right back there.
Today, Renaiss turns one. 🎂
Thank you for being with us every step of the way.
We hope you’ll be part of the memories still to come.
Like and QRT this post with a message for Renaiss. We’ll pick 3 participants at random to receive OP18. 🎁
Gacha. Marketplace. Staking.
SDK. CLI. Index. Fair.
What’s next? ✨
Why Optimum Targets the Source Bandwidth Bottleneck in Blockchain Networking #21
@get_optimum
What happens when a blockchain produces data faster than its network can distribute it?
This is an important question for high-performance blockchains, particularly networks like Solana and Monad, where large amounts of data need to reach validators within strict time constraints.
Increasing execution speed is certainly important, but producing a block quickly doesn't necessarily mean that distributing it will be equally fast.
One of the fundamental problems highlighted in Optimum's Peer-Turbo research is the Source Bandwidth Bottleneck.
Many blockchain broadcasting architectures rely on tree-shaped or star-shaped network topologies.
The source node divides a large payload into smaller shards and distributes them either directly to receiving nodes or through intermediate relays.
While these architectures help organize data distribution, a significant portion of the initial broadcasting workload still depends on the source node's outbound bandwidth.
Consider a simple scenario.
A network expands from hundreds of validators to thousands of validators. Meanwhile, block sizes increase, and the available time for propagation remains limited.
The source node now faces a growing distribution workload.
Upgrading its bandwidth might help, but continuously increasing hardware and networking requirements isn't necessarily a sustainable scaling strategy.
This is where Optimum's Peer-Turbo approach becomes particularly interesting.
Rather than concentrating the distribution workload around the original sender, Peer-Turbo enables receiving nodes to actively participate in completing data propagation.
Using Random Linear Network Coding (RLNC), peers can exchange coded combinations of the information they have already received.
This allows them to assist each other in reconstructing the original data without explicitly coordinating which individual shards are missing.
The underlying idea is to make better use of bandwidth that already exists throughout the network.
According to Optimum's analytical research, this approach offers two particularly interesting possibilities:
1. Maintaining service quality with less source bandwidth
Peer-Turbo can reduce the source bandwidth required to achieve a given service-quality target by up to an order of magnitude under the paper's modeled conditions.
2. Improving propagation speed without increasing source bandwidth
Alternatively, when bandwidth is fixed, the model shows that propagation latency can be reduced by up to an order of magnitude.
These results suggest that improving blockchain networking doesn't always require increasing the capacity of the original sender.
Changing how receiving nodes participate in data distribution can also make a substantial difference.
There's a broader implication for decentralization as well.
If higher blockchain performance continuously requires more expensive networking infrastructure, participation could become increasingly demanding for operators.
More efficient data distribution could help ease some of those infrastructure pressures, although the actual benefits would depend on implementation and real-world network conditions.
What I find particularly interesting about Optimum's research is that it treats network capacity as something distributed across participants, rather than something that must be concentrated at the source.
A blockchain may have thousands of interconnected nodes, each with its own networking resources.
Why not make better use of those resources collectively?
For me, that's one of the most compelling ideas behind Peer-Turbo.
Blockchain scalability shouldn't depend entirely on how much data a single node can send, but also on how efficiently the entire network can share it.
And that's precisely the bottleneck Optimum is working to address.


Why Optimum Uses Random Linear Network Coding to Rethink P2P Broadcasting #20
@get_optimum
There's an interesting problem in blockchain networking that doesn't get discussed very often.
When a node receives only part of a block, how does it get the missing pieces?
In traditional P2P broadcasting systems, large messages are often divided into smaller pieces called shards and distributed across the network.
The idea is straightforward. Instead of sending one massive payload, nodes exchange smaller pieces until they have enough information to reconstruct the original data.
But there's a catch.
Not every node receives the same shards.
One validator might have shards 1, 2, and 3, while another has shards 2, 4, and 5.
If these nodes want to help each other, they need to figure out which pieces are missing and which ones are worth sending.
That coordination creates additional complexity, especially when hundreds or thousands of nodes are trying to receive the same data within a strict time window.
This is where Optimum's latest Peer-Turbo research introduces a different approach.
Instead of exchanging only individual shards, nodes can exchange coded combinations of them.
The technique behind this is called Random Linear Network Coding, or RLNC.
With RLNC, a node generates new coded packets by combining the information it already has using randomly selected coefficients.
The receiving node doesn't necessarily need a specific original shard.
It needs enough linearly independent coded packets to reconstruct the original data.
That difference is important.
Imagine two validators that have received different portions of a block.
In a conventional system, they may need to coordinate which missing shards should be exchanged.
With RLNC, they can instead exchange newly generated coded packets that have a good chance of providing useful information to the other side.
As enough independent information arrives, the original data can be decoded.
Of course, coded packets aren't automatically useful in every case. Some combinations may be redundant, and encoding and decoding introduce computational overhead.
But the underlying advantage is that nodes can cooperate without explicitly tracking every other peer's shard inventory.
And this is exactly the idea explored in Optimum's Peer-Turbo paper.
Rather than making the original source responsible for delivering most of the data, Peer-Turbo allows receiving peers to contribute to the distribution process.
This helps address one of the major limitations of tree-shaped and star-shaped broadcasting architectures: the outbound bandwidth bottleneck at the source.
According to the paper's analytical results, Peer-Turbo can reduce source bandwidth requirements by up to an order of magnitude for a given service-quality target.
Alternatively, under fixed bandwidth constraints, it can achieve up to an order-of-magnitude reduction in propagation latency.
These are theoretical results under the paper's modeled conditions, not guaranteed improvements for every live blockchain deployment.
Still, the implications are interesting.
Networks like Solana and Monad operate under demanding timing requirements, where large amounts of information need to reach validators quickly.
Simply increasing bandwidth isn't always the most efficient solution.
Sometimes the bigger improvement comes from changing how nodes share the information they already possess.
That's what makes RLNC such an interesting part of Optimum's research.
It shifts the focus away from making the original sender do more work and toward making the entire receiving network participate more efficiently.
Instead of asking how one node can send data faster, Optimum is exploring how thousands of nodes can help deliver that data together.
And to me, that's a much more interesting direction for the future of decentralized networking.


4
4
107
카드 디자인하고 300 USDT에 도전?! 참여 방법 알려드립니다!!
안녕하세요! Renaiss에 진심인 보리입니다!! ❤️
최근 Renaiss와 Four.meme가 함께 진행하는 밈 카드 디자인 캠페인에 저도 참여해봤는데요!!ㅎㅎ
저는 저번 게시물에서 말씀드렸듯이
MUBARAK — THE DAWN OF A GOLDEN ERA!!
카드를 직접 제작해봤습니다!! >3<
Renaiss와 Four.meme의 만남으로 새로운 황금시대가 시작된다는 의미를 담아봤는데요ㅎㅎ
이번 이벤트는 총 18개의 밈 캐릭터 중 하나를 선택해 자신만의 얼터너티브 아트 카드를 만드는 캠페인입니다!!
그럼 참여 방법을 설명드릴게요!!
1. 캠페인 사이트에서 원하는 밈 캐릭터 선택하기! (댓글에 사이트 첨부해놓을게요!)
2. 나만의 카드 디자인을 제작하고 카드 제목과 스토리 정하기!
3. 공식 이벤트 게시물을 인용하면서 제작한 카드 이미지와 스토리를 X에 공유하기!
(@renaissCLTB @fourdotmemezh 태그 필수!)
4. 캠페인 사이트에 카드 이미지와 X 게시물 링크를 제출하면 참여 완료!!ㅎㅎ
이번 이벤트는 총 10명의 우승자를 선정하는데요!
커뮤니티 부문 5명: 유료 팩 구매 이력과 보유 SBT에 따른 추첨
KOL 부문 4명: 창의성, 디자인 완성도 등을 기준으로 심사
개인 크리에이터 부문 1명: 창의성, 디자인 완성도 등을 기준으로 심사
특히 커뮤니티 추첨과 개인 크리에이터 심사 부분에 중복 참여도 가능하다고 하니 참고하시면 좋을 것 같아요!!
우승자는 300 USDT 또는 최대 1,000 USDT 상당의 BBW 방콕 여행 지원금 중 하나를 선택할 수 있다고 합니다!!
그리고 참여 마감은 11월 22일까지!!
여러분도 자신만의 밈 카드를 만들어보세요!! >3< ❤️
@renaissxyz @RenaissKrCM
@renaissCLTB @fourdotmemezh


300 USDT 또는 BBW 방콕 여행 지원금을 주는 프로젝트가 있다?!
Renaiss Questline Season 5 — Mission 1
안녕하세요! Renaiss에 진심인 보리입니다!! ❤️
최근 Renaiss와 Four.meme가 함께 특별한 콜라보 캠페인을 진행하고 있는데요!!
이번 이벤트는 총 18개의 밈 캐릭터 중 하나를 선택해 자신만의 얼터너티브 아트 카드를 디자인하는 캠페인입니다!!ㅎㅎ
저도 이번 기회에 직접 카드를 만들어봤어요!! >3<
제가 선택한 캐릭터는 MUBARAK!!
카드 제목은 THE DAWN OF A GOLDEN ERA로,
두 프로젝트의 만남을 통해 새로운 황금시대가 시작된다는 의미를 담아봤습니다ㅎㅎ
이번 협업은 Renaiss의 카드 컬렉팅 경험과 Four.meme의 밈 문화를 결합했다는 점에서 의미가 있는데요!
Renaiss는 다양한 밈 캐릭터를 활용해 카드 콘텐츠의 범위를 넓힐 수 있고, Four.meme는 기존 밈 캐릭터들을 수집형 카드 아트로 선보일 수 있다는 장점이 있습니다.
또한 유저들이 직접 카드를 제작하고 공유하는 방식이라 두 커뮤니티 간의 교류에도 도움이 될 것으로 기대됩니다!!>3<
이번 캠페인에서는 총 10명의 우승자에게
300 USDT 또는 최대 1,000 USDT 상당의 BBW 방콕 여행 지원금 중 하나를 선택할 수 있는 기회가 주어진다고 해요!!
평소에는 Renaiss에서 카드를 개봉하는 입장이었는데, 이번에는 직접 카드를 디자인해볼 수 있어서 색다른 경험이었습니다ㅎㅎ
앞으로도 이런 다양한 콜라보 이벤트가 이어졌으면 좋겠네요!! ❤️
@renaissCLTB @fourdotmemezh @renaissxyz @RenaissKrCM @Plus_Ultra_715

Nabori | (❖,❖) retweeted
카드 디자인하고 300 USDT에 도전?! 참여 방법 알려드립니다!!
안녕하세요! Renaiss에 진심인 보리입니다!! ❤️
최근 Renaiss와 Four.meme가 함께 진행하는 밈 카드 디자인 캠페인에 저도 참여해봤는데요!!ㅎㅎ
저는 저번 게시물에서 말씀드렸듯이
MUBARAK — THE DAWN OF A GOLDEN ERA!!
카드를 직접 제작해봤습니다!! >3<
Renaiss와 Four.meme의 만남으로 새로운 황금시대가 시작된다는 의미를 담아봤는데요ㅎㅎ
이번 이벤트는 총 18개의 밈 캐릭터 중 하나를 선택해 자신만의 얼터너티브 아트 카드를 만드는 캠페인입니다!!
그럼 참여 방법을 설명드릴게요!!
1. 캠페인 사이트에서 원하는 밈 캐릭터 선택하기! (댓글에 사이트 첨부해놓을게요!)
2. 나만의 카드 디자인을 제작하고 카드 제목과 스토리 정하기!
3. 공식 이벤트 게시물을 인용하면서 제작한 카드 이미지와 스토리를 X에 공유하기!
(@renaissCLTB @fourdotmemezh 태그 필수!)
4. 캠페인 사이트에 카드 이미지와 X 게시물 링크를 제출하면 참여 완료!!ㅎㅎ
이번 이벤트는 총 10명의 우승자를 선정하는데요!
커뮤니티 부문 5명: 유료 팩 구매 이력과 보유 SBT에 따른 추첨
KOL 부문 4명: 창의성, 디자인 완성도 등을 기준으로 심사
개인 크리에이터 부문 1명: 창의성, 디자인 완성도 등을 기준으로 심사
특히 커뮤니티 추첨과 개인 크리에이터 심사 부분에 중복 참여도 가능하다고 하니 참고하시면 좋을 것 같아요!!
우승자는 300 USDT 또는 최대 1,000 USDT 상당의 BBW 방콕 여행 지원금 중 하나를 선택할 수 있다고 합니다!!
그리고 참여 마감은 11월 22일까지!!
여러분도 자신만의 밈 카드를 만들어보세요!! >3< ❤️
@renaissxyz @RenaissKrCM
@renaissCLTB @fourdotmemezh
300 USDT 또는 BBW 방콕 여행 지원금을 주는 프로젝트가 있다?!
Renaiss Questline Season 5 — Mission 1
안녕하세요! Renaiss에 진심인 보리입니다!! ❤️
최근 Renaiss와 Four.meme가 함께 특별한 콜라보 캠페인을 진행하고 있는데요!!
이번 이벤트는 총 18개의 밈 캐릭터 중 하나를 선택해 자신만의 얼터너티브 아트 카드를 디자인하는 캠페인입니다!!ㅎㅎ
저도 이번 기회에 직접 카드를 만들어봤어요!! >3<
제가 선택한 캐릭터는 MUBARAK!!
카드 제목은 THE DAWN OF A GOLDEN ERA로,
두 프로젝트의 만남을 통해 새로운 황금시대가 시작된다는 의미를 담아봤습니다ㅎㅎ
이번 협업은 Renaiss의 카드 컬렉팅 경험과 Four.meme의 밈 문화를 결합했다는 점에서 의미가 있는데요!
Renaiss는 다양한 밈 캐릭터를 활용해 카드 콘텐츠의 범위를 넓힐 수 있고, Four.meme는 기존 밈 캐릭터들을 수집형 카드 아트로 선보일 수 있다는 장점이 있습니다.
또한 유저들이 직접 카드를 제작하고 공유하는 방식이라 두 커뮤니티 간의 교류에도 도움이 될 것으로 기대됩니다!!>3<
이번 캠페인에서는 총 10명의 우승자에게
300 USDT 또는 최대 1,000 USDT 상당의 BBW 방콕 여행 지원금 중 하나를 선택할 수 있는 기회가 주어진다고 해요!!
평소에는 Renaiss에서 카드를 개봉하는 입장이었는데, 이번에는 직접 카드를 디자인해볼 수 있어서 색다른 경험이었습니다ㅎㅎ
앞으로도 이런 다양한 콜라보 이벤트가 이어졌으면 좋겠네요!! ❤️
@renaissCLTB @fourdotmemezh @renaissxyz @RenaissKrCM @Plus_Ultra_715
Why Optimum Uses Random Linear Network Coding to Rethink P2P Broadcasting #20
@get_optimum
There's an interesting problem in blockchain networking that doesn't get discussed very often.
When a node receives only part of a block, how does it get the missing pieces?
In traditional P2P broadcasting systems, large messages are often divided into smaller pieces called shards and distributed across the network.
The idea is straightforward. Instead of sending one massive payload, nodes exchange smaller pieces until they have enough information to reconstruct the original data.
But there's a catch.
Not every node receives the same shards.
One validator might have shards 1, 2, and 3, while another has shards 2, 4, and 5.
If these nodes want to help each other, they need to figure out which pieces are missing and which ones are worth sending.
That coordination creates additional complexity, especially when hundreds or thousands of nodes are trying to receive the same data within a strict time window.
This is where Optimum's latest Peer-Turbo research introduces a different approach.
Instead of exchanging only individual shards, nodes can exchange coded combinations of them.
The technique behind this is called Random Linear Network Coding, or RLNC.
With RLNC, a node generates new coded packets by combining the information it already has using randomly selected coefficients.
The receiving node doesn't necessarily need a specific original shard.
It needs enough linearly independent coded packets to reconstruct the original data.
That difference is important.
Imagine two validators that have received different portions of a block.
In a conventional system, they may need to coordinate which missing shards should be exchanged.
With RLNC, they can instead exchange newly generated coded packets that have a good chance of providing useful information to the other side.
As enough independent information arrives, the original data can be decoded.
Of course, coded packets aren't automatically useful in every case. Some combinations may be redundant, and encoding and decoding introduce computational overhead.
But the underlying advantage is that nodes can cooperate without explicitly tracking every other peer's shard inventory.
And this is exactly the idea explored in Optimum's Peer-Turbo paper.
Rather than making the original source responsible for delivering most of the data, Peer-Turbo allows receiving peers to contribute to the distribution process.
This helps address one of the major limitations of tree-shaped and star-shaped broadcasting architectures: the outbound bandwidth bottleneck at the source.
According to the paper's analytical results, Peer-Turbo can reduce source bandwidth requirements by up to an order of magnitude for a given service-quality target.
Alternatively, under fixed bandwidth constraints, it can achieve up to an order-of-magnitude reduction in propagation latency.
These are theoretical results under the paper's modeled conditions, not guaranteed improvements for every live blockchain deployment.
Still, the implications are interesting.
Networks like Solana and Monad operate under demanding timing requirements, where large amounts of information need to reach validators quickly.
Simply increasing bandwidth isn't always the most efficient solution.
Sometimes the bigger improvement comes from changing how nodes share the information they already possess.
That's what makes RLNC such an interesting part of Optimum's research.
It shifts the focus away from making the original sender do more work and toward making the entire receiving network participate more efficiently.
Instead of asking how one node can send data faster, Optimum is exploring how thousands of nodes can help deliver that data together.
And to me, that's a much more interesting direction for the future of decentralized networking.
Optimum Peer-Turbo: Bringing MIT Research Into the Future of P2P Broadcasting #19
@get_optimum
One of the most interesting things about blockchain infrastructure is seeing academic research turn into technology that actually runs on live networks.
That's exactly what we're starting to see with Optimum.
At this year's IEEE Information Theory Workshop, Optimum presented its latest research paper, "Optimum Peer-Turbo: A Scalable and Efficient Solution for P2P Broadcasting."
The research builds on years of work originating from MIT, where the technology behind Optimum was developed.
And there's an important milestone here.
Optimum's first protocol has recently gone live on Ethereum mainnet, marking the transition from academic research into real blockchain infrastructure.
But the new Peer-Turbo paper looks beyond Ethereum.
It explores how similar ideas can improve data broadcasting in networks such as Solana and Monad, where information needs to reach large groups of validators within strict time limits.
So, what problem is Peer-Turbo trying to solve?
In many high-performance blockchains, data is distributed through tree-shaped or star-shaped broadcasting structures.
A source node sends data directly to validators or distributes it through relay nodes, often dividing large payloads into smaller pieces called shards.
This approach can reduce the number of network hops, but it introduces a major bottleneck.
The source node's outbound bandwidth becomes a limiting factor.
When hundreds or thousands of validators need to receive data quickly, relying too heavily on the original sender can make efficient broadcasting difficult.
Peer-Turbo approaches this problem differently.
Instead of making the source responsible for most of the distribution work, it allows receiving nodes to help one another complete the process.
The key technology behind this is Random Linear Network Coding (RLNC).
With RLNC, nodes can exchange coded combinations of data shards rather than relying entirely on specific missing pieces from the original sender.
These coded shards can help other nodes recover the original data without requiring explicit coordination of which shards each peer already possesses.
In other words, the receiving nodes become active participants in data distribution.
And the theoretical results are particularly interesting.
According to the paper, Peer-Turbo can achieve:
1. Up to 10× Lower Source Bandwidth Requirements
For a given service-quality target, the model shows that Peer-Turbo can reduce the bandwidth required from the original sender by up to an order of magnitude.
2. Up to 10× Lower Propagation Latency
Under fixed bandwidth constraints, the approach can alternatively reduce propagation latency by an order of magnitude.
3. More Efficient Peer Collaboration
By allowing nodes to exchange coded shards, Peer-Turbo reduces dependence on the source node and avoids the need for explicit shard-state coordination.
4. Potential Applications Beyond Ethereum
The research targets broadcasting architectures relevant to high-performance networks such as Solana and Monad, showing how Optimum's underlying approach could extend across different blockchain ecosystems.
One detail worth emphasizing is that these improvements come from the paper's analytical model rather than a guarantee that every live deployment will achieve identical results.
Actual performance will depend on network topology, bandwidth conditions, and implementation.
Still, I think the broader direction is worth paying attention to.
For years, blockchain scaling discussions have largely focused on execution speed, block capacity, and transaction throughput.
But even the fastest execution environment needs an efficient way to distribute information across its validator network.
And as blockchains become more demanding, the bandwidth required to broadcast data may become an increasingly important constraint.
What makes Optimum interesting is that it's approaching this challenge through information theory and network coding rather than simply asking nodes to use more powerful hardware.
The Ethereum mainnet deployment shows that Optimum's research is already moving into production, while Peer-Turbo explores how those ideas can be applied to other broadcasting architectures.
The next major improvement in blockchain performance might not come from processing more data, but from finding a smarter way to move it.
And that's the direction Optimum is exploring with Peer-Turbo.


[ Rialo Builders Hub Recap ]
@RialoHQ
@RialoKorea
안녕하세요! 리알로에 진심인 보리입니다! 💜
이번 Rialo Builders Hub에서는 Resonance와 DASS라는 두 프로젝트를 만나볼 수 있었는데요!
하나는 복잡한 온체인 자동화 기술을 쉽게 배울 수 있도록 돕고, 다른 하나는 여러 체인에 흩어진 자산을 편리하게 사용할 수 있도록 만든 프로젝트였습니다ㅎㅎ
Resonance — 게임처럼 배우는 온체인 금융!
Resonance는 Rialo의 Reactive Transactions와 자산 관리 규칙을 직접 체험하며 배울 수 있는 교육 플랫폼입니다!
사용자는 네 명의 캐릭터 중 하나를 선택해 시나리오와 퀴즈를 진행하고, 학습을 완료하면 Learning Pass NFT를 발급받을 수 있는데요.
특히 흥미로웠던 건 학습한 내용을 직접 실험할 수 있는 다양한 도구들이었습니다!
Reactive Wallet: 가격 조건, 지출 한도, 만료 시간을 설정해 자동 거래 시뮬레이션
Guardrails: 보호할 자금과 주간 지출 한도를 지정해 위험한 거래 차단
Plan Lab: 서로 다른 자산 관리 전략을 동일한 조건에서 비교
Budget Studio: 월별 수입과 지출을 배분하고 미래 예산을 시뮬레이션
AI가 사용자의 요청을 바탕으로 규칙을 제안하고, 실행 전에 권한과 금액 제한을 검증하는 과정도 체험할 수 있습니다!
무엇보다 실제 자금을 사용하지 않고도 자동화와 자산 보호가 어떻게 함께 작동하는지 배울 수 있다는 점이 인상적이었어요ㅎㅎ
DASS — 여러 체인의 자산을 하나의 잔액으로!
두 번째 DASS는 여러 블록체인에 분산된 자산을 통합하고 다양한 결제 서비스를 제공하는 플랫폼입니다!
가장 핵심적인 기능은 Unified Balance인데요.
Ethereum, Base, Arbitrum 등 지원되는 네트워크의 자산을 하나의 잔액처럼 관리하고, 복잡한 브릿지 과정을 직접 거치지 않고도 결제할 수 있도록 설계되었습니다!
특히 재미있었던 기능은 Streaming Payroll이었습니다.
기존처럼 월급날을 기다리는 대신, 기업이 설정한 금액이 직원에게 초 단위로 지속 지급되는 방식인데요!
기업은 지급 속도를 조정하거나 중단할 수 있고, 직원은 실시간으로 누적되는 급여를 확인할 수 있습니다.
여기에 Gacha 카드팩 시스템도 선보였는데요!
통합 잔액으로 카드팩을 구매하고, 결과를 온체인에 기록한 뒤 해시를 통해 검증할 수 있도록 설계했습니다.
다만 현재 카드 결과는 진정한 무작위 방식이 아닌 결정론적 알고리즘을 사용하며, 향후 VRF 기반 검증 가능한 랜덤 시스템을 도입할 계획이라고 합니다!
이번 두 프로젝트를 보면서 느낀 건 Rialo 생태계가 기술을 배우는 단계부터 실제 금융 서비스를 사용하는 단계까지 확장되고 있다는 점이었습니다!
Resonance는 사용자가 자동화 규칙과 권한을 이해하도록 돕고, DASS는 자산 관리와 결제를 더욱 자연스럽게 만들려는 프로젝트니까요.
아직 테스트와 개선이 필요한 부분도 있지만, 매주 Builders Hub에서 새로운 아이디어가 실제 서비스로 발전하는 모습을 볼 수 있어서 정말 기대됩니다ㅎㅎ


bori's rialo #244
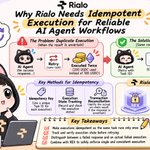
[ Why Rialo Needs Idempotent Execution for Reliable AI Agent Workflows ]
@RialoHQ
@RialoKorea
안녕하세요! 보리입니다!
지난 글에서는 AI 에이전트가 이미 사용한 실행 권한을 다시 사용하는 것을 방지하는 Replay Attack과 Single-Use Authorization에 대해 알아봤는데요!
그런데 여기서 한 가지 더 생각해볼 문제가 있습니다.
AI 에이전트가 거래를 실행했는데, 성공했는지 확인하지 못한다면 어떻게 해야 할까요?
AI 에이전트는 다양한 외부 API와 블록체인 네트워크를 연결해 자동으로 작업을 수행합니다.
그런데 네트워크 지연이나 일시적인 연결 오류로 인해 트랜잭션은 정상적으로 처리되었지만, 에이전트가 성공 응답을 받지 못하는 상황이 발생할 수 있는데요!
예를 들어 DeFi 에이전트가 100 USDC로 ETH를 매수했다고 해볼게요.
실제로는 블록체인에서 거래가 성공적으로 완료되었지만, 네트워크 문제로 에이전트에게 결과가 전달되지 않았습니다.
에이전트는 거래가 실패했다고 판단하고 동일한 작업을 다시 실행합니다.
그 결과 사용자가 원했던 100 USDC가 아니라 총 200 USDC가 사용될 수도 있겠죠ㅠㅠ
여기서 중요한 개념이 바로 Idempotency, 즉 멱등성입니다!!
멱등성이란 동일한 작업을 여러 번 요청하더라도 최종 결과가 한 번 실행한 것과 같도록 만드는 성질인데요!
저는 앞으로 Agent Economy에서는 단순히 공격자의 중복 요청을 차단하는 것뿐만 아니라, 정상적인 시스템 오류로 발생하는 중복 실행까지 방지하는 것이 중요해질 것이라고 생각합니다ㅎㅎ
이를 위해 활용할 수 있는 방법으로는 Idempotency Key, Execution State Tracking, Transaction Reconciliation 등이 있습니다.
예를 들어 AI 에이전트가 거래를 실행할 때 고유한 Task ID를 부여하고, 실행 결과를 별도로 기록하는 것입니다.
이후 동일한 작업을 다시 요청받더라도 새로운 거래를 곧바로 생성하는 대신, 기존 거래가 이미 처리되었는지 먼저 확인하도록 설계할 수 있겠죠!
특히 중요한 것은 실패 응답과 실제 실행 실패를 구분하는 것입니다.
응답을 받지 못했다고 해서 트랜잭션이 실행되지 않았다는 의미는 아니기 때문인데요!
이런 상황에서는 무조건 재시도하는 대신 온체인 상태와 트랜잭션 기록을 확인하는 과정이 필요합니다.
그리고 리알로(Rialo)의 Reactive Architecture에서도 이러한 접근은 흥미로운 활용 사례가 될 수 있습니다!
특정 조건이 충족되어 자동으로 트랜잭션을 실행할 때, 단순히 조건이 다시 발생했다는 이유만으로 같은 작업을 반복하는 것이 아니라 이전 실행 상태를 확인하도록 설계하는 것이죠.
여기에 REX 기반의 정책 검증을 결합한다면, 이미 완료된 작업에 대해 동일한 실행 권한이 다시 사용되지 않도록 제한하는 구조도 생각해볼 수 있고요!
물론 분산 시스템에서 완벽한 Exactly-Once Execution을 보장하는 것은 쉽지 않습니다.
특히 외부 API와 블록체인을 함께 사용하는 환경에서는 멱등성 관리와 상태 추적, 재시도 정책을 함께 설계해야 실질적인 중복 실행 위험을 줄일 수 있겠죠!
Retry the Request, Not the Consequence!
AI 에이전트가 더 많은 작업을 자율적으로 처리할수록 중요한 것은 오류가 발생했을 때 단순히 다시 실행하는 것이 아니라, 이미 어떤 결과가 발생했는지 정확하게 확인하는 것이라고 생각합니다.
저는 이런 Idempotency와 실행 상태 검증이 앞으로 Rialo를 활용한 Agent Economy에서 안전하고 신뢰할 수 있는 자동화를 만드는 중요한 기반이 될 것 같습니다!!🥰

Nabori | (❖,❖) retweeted

🇹🇭 Your meme. Your card. On display in Bangkok.
🃏 The Renaiss × @fourdotmemezh UGC card design campaign is now live, with @BNBCHAIN as our ecosystem partner!
Choose from 18 designated Meme characters and create your own alternate-art card using the campaign’s co-branded card frame. Bring your pick to life with your own artwork and story.
币安人生, HAJIMI, BANANAS31… who will inspire your creation?
✨ We plan to showcase 10 winning designs at our booth during #BinanceBlockchainWeek
🎁 10 winners across three categories can each choose between a 300 USDT reward or up to 1,000 USDT in travel support!
🗓️ Entries are open now.
⏳ Ends: November 22, 17:59 (UTC+8)
Nabori | (❖,❖) retweeted
300 USDT 또는 BBW 방콕 여행 지원금을 주는 프로젝트가 있다?!
Renaiss Questline Season 5 — Mission 1
안녕하세요! Renaiss에 진심인 보리입니다!! ❤️
최근 Renaiss와 Four.meme가 함께 특별한 콜라보 캠페인을 진행하고 있는데요!!
이번 이벤트는 총 18개의 밈 캐릭터 중 하나를 선택해 자신만의 얼터너티브 아트 카드를 디자인하는 캠페인입니다!!ㅎㅎ
저도 이번 기회에 직접 카드를 만들어봤어요!! >3<
제가 선택한 캐릭터는 MUBARAK!!
카드 제목은 THE DAWN OF A GOLDEN ERA로,
두 프로젝트의 만남을 통해 새로운 황금시대가 시작된다는 의미를 담아봤습니다ㅎㅎ
이번 협업은 Renaiss의 카드 컬렉팅 경험과 Four.meme의 밈 문화를 결합했다는 점에서 의미가 있는데요!
Renaiss는 다양한 밈 캐릭터를 활용해 카드 콘텐츠의 범위를 넓힐 수 있고, Four.meme는 기존 밈 캐릭터들을 수집형 카드 아트로 선보일 수 있다는 장점이 있습니다.
또한 유저들이 직접 카드를 제작하고 공유하는 방식이라 두 커뮤니티 간의 교류에도 도움이 될 것으로 기대됩니다!!>3<
이번 캠페인에서는 총 10명의 우승자에게
300 USDT 또는 최대 1,000 USDT 상당의 BBW 방콕 여행 지원금 중 하나를 선택할 수 있는 기회가 주어진다고 해요!!
평소에는 Renaiss에서 카드를 개봉하는 입장이었는데, 이번에는 직접 카드를 디자인해볼 수 있어서 색다른 경험이었습니다ㅎㅎ
앞으로도 이런 다양한 콜라보 이벤트가 이어졌으면 좋겠네요!! ❤️
@renaissCLTB @fourdotmemezh @renaissxyz @RenaissKrCM @Plus_Ultra_715
🇹🇭 Your meme. Your card. On display in Bangkok.
🃏 The Renaiss × @fourdotmemezh UGC card design campaign is now live, with @BNBCHAIN as our ecosystem partner!
Choose from 18 designated Meme characters and create your own alternate-art card using the campaign’s co-branded card frame. Bring your pick to life with your own artwork and story.
币安人生, HAJIMI, BANANAS31… who will inspire your creation?
✨ We plan to showcase 10 winning designs at our booth during #BinanceBlockchainWeek
🎁 10 winners across three categories can each choose between a 300 USDT reward or up to 1,000 USDT in travel support!
🗓️ Entries are open now.
⏳ Ends: November 22, 17:59 (UTC+8)
bori's rialo #244
[ Why Rialo Needs Idempotent Execution for Reliable AI Agent Workflows ]
@RialoHQ
@RialoKorea
안녕하세요! 보리입니다!
지난 글에서는 AI 에이전트가 이미 사용한 실행 권한을 다시 사용하는 것을 방지하는 Replay Attack과 Single-Use Authorization에 대해 알아봤는데요!
그런데 여기서 한 가지 더 생각해볼 문제가 있습니다.
AI 에이전트가 거래를 실행했는데, 성공했는지 확인하지 못한다면 어떻게 해야 할까요?
AI 에이전트는 다양한 외부 API와 블록체인 네트워크를 연결해 자동으로 작업을 수행합니다.
그런데 네트워크 지연이나 일시적인 연결 오류로 인해 트랜잭션은 정상적으로 처리되었지만, 에이전트가 성공 응답을 받지 못하는 상황이 발생할 수 있는데요!
예를 들어 DeFi 에이전트가 100 USDC로 ETH를 매수했다고 해볼게요.
실제로는 블록체인에서 거래가 성공적으로 완료되었지만, 네트워크 문제로 에이전트에게 결과가 전달되지 않았습니다.
에이전트는 거래가 실패했다고 판단하고 동일한 작업을 다시 실행합니다.
그 결과 사용자가 원했던 100 USDC가 아니라 총 200 USDC가 사용될 수도 있겠죠ㅠㅠ
여기서 중요한 개념이 바로 Idempotency, 즉 멱등성입니다!!
멱등성이란 동일한 작업을 여러 번 요청하더라도 최종 결과가 한 번 실행한 것과 같도록 만드는 성질인데요!
저는 앞으로 Agent Economy에서는 단순히 공격자의 중복 요청을 차단하는 것뿐만 아니라, 정상적인 시스템 오류로 발생하는 중복 실행까지 방지하는 것이 중요해질 것이라고 생각합니다ㅎㅎ
이를 위해 활용할 수 있는 방법으로는 Idempotency Key, Execution State Tracking, Transaction Reconciliation 등이 있습니다.
예를 들어 AI 에이전트가 거래를 실행할 때 고유한 Task ID를 부여하고, 실행 결과를 별도로 기록하는 것입니다.
이후 동일한 작업을 다시 요청받더라도 새로운 거래를 곧바로 생성하는 대신, 기존 거래가 이미 처리되었는지 먼저 확인하도록 설계할 수 있겠죠!
특히 중요한 것은 실패 응답과 실제 실행 실패를 구분하는 것입니다.
응답을 받지 못했다고 해서 트랜잭션이 실행되지 않았다는 의미는 아니기 때문인데요!
이런 상황에서는 무조건 재시도하는 대신 온체인 상태와 트랜잭션 기록을 확인하는 과정이 필요합니다.
그리고 리알로(Rialo)의 Reactive Architecture에서도 이러한 접근은 흥미로운 활용 사례가 될 수 있습니다!
특정 조건이 충족되어 자동으로 트랜잭션을 실행할 때, 단순히 조건이 다시 발생했다는 이유만으로 같은 작업을 반복하는 것이 아니라 이전 실행 상태를 확인하도록 설계하는 것이죠.
여기에 REX 기반의 정책 검증을 결합한다면, 이미 완료된 작업에 대해 동일한 실행 권한이 다시 사용되지 않도록 제한하는 구조도 생각해볼 수 있고요!
물론 분산 시스템에서 완벽한 Exactly-Once Execution을 보장하는 것은 쉽지 않습니다.
특히 외부 API와 블록체인을 함께 사용하는 환경에서는 멱등성 관리와 상태 추적, 재시도 정책을 함께 설계해야 실질적인 중복 실행 위험을 줄일 수 있겠죠!
Retry the Request, Not the Consequence!
AI 에이전트가 더 많은 작업을 자율적으로 처리할수록 중요한 것은 오류가 발생했을 때 단순히 다시 실행하는 것이 아니라, 이미 어떤 결과가 발생했는지 정확하게 확인하는 것이라고 생각합니다.
저는 이런 Idempotency와 실행 상태 검증이 앞으로 Rialo를 활용한 Agent Economy에서 안전하고 신뢰할 수 있는 자동화를 만드는 중요한 기반이 될 것 같습니다!!🥰
bori's rialo #243
[ Why Rialo Must Prevent Persistent Permissions in AI Agent Workflows ]
@RialoHQ
@RialoKorea
안녕하세요! 보리입니다!
지난 글에서는 AI 에이전트가 사용하는 도구에 필요 이상의 권한을 부여하면 발생할 수 있는 Excessive Tool Permissions와 최소 권한 원칙에 대해 알아봤는데요!
그런데 여기서 한 가지 더 생각해볼 문제가 있습니다.
처음에는 정상적으로 부여된 권한이라도, 작업이 끝난 뒤까지 계속 유지된다면 어떻게 될까요?
AI 에이전트는 다양한 작업을 자동으로 수행하기 위해 지갑이나 API, 스마트 컨트랙트 등에 접근할 수 있는 권한을 부여받습니다.
문제는 특정 작업을 위해 허용된 권한이 실제로는 훨씬 오랫동안 유지될 수 있다는 점인데요!
예를 들어 DeFi 포트폴리오를 관리하는 AI 에이전트가 있다고 해볼게요.
사용자는 에이전트에게 특정 토큰을 100 USDC만큼 매수하도록 요청했고, 이를 위해 거래 실행 권한을 부여했습니다.
그런데 거래가 정상적으로 완료된 이후에도 해당 권한이 계속 유지된다면 어떨까요?
나중에 에이전트가 Prompt Injection 공격에 노출되거나 연결된 도구가 손상되었을 때, 이미 부여된 권한을 이용해 추가 거래를 시도할 수도 있겠죠ㅠㅠ
이것이 바로 Permission Persistence, 즉 작업이 끝난 이후에도 권한이 지속되는 문제입니다!!
저는 앞으로 Agent Economy에서는 권한의 범위를 제한하는 것만큼이나, 그 권한이 언제까지 유효해야 하는지를 관리하는 것이 중요해질 것이라고 생각합니다ㅎㅎ
여기서 활용할 수 있는 개념이 바로 Time-Bound Authorization과 Just-in-Time Access인데요!
Time-Bound Authorization은 권한에 유효 기간을 설정하는 방식이고, Just-in-Time Access는 실제 작업이 필요한 순간에만 권한을 부여하는 접근 방식입니다.
예를 들어 AI 에이전트가 특정 거래를 실행할 때 5분 동안만 유효한 권한을 부여하고, 시간이 지나면 자동으로 만료되도록 설계할 수 있습니다.
또는 거래가 성공적으로 완료되면 남아 있는 실행 권한을 즉시 철회하는 Automatic Permission Revocation도 생각해볼 수 있겠죠!
그리고 리알로(Rialo)의 Reactive Architecture에서는 이러한 조건 기반 권한 관리가 흥미로운 활용 사례가 될 수 있습니다.
단순히 거래 금액과 대상 주소만 확인하는 것이 아니라, 현재 시간이 허용된 범위 안에 있는지, 해당 작업이 이미 완료되었는지, 권한이 아직 유효한지까지 실행 조건에 포함하는 것이죠!
여기에 REX 기반의 정책 검증을 결합한다면 중요한 키를 직접 노출하지 않으면서도 유효한 권한과 실행 조건을 충족한 요청에 대해서만 사용하도록 제한하는 구조를 생각해볼 수 있습니다.
물론 권한의 만료 시간을 설정하는 것만으로 모든 문제가 해결되지는 않습니다. 유효 기간 안에서도 공격이 발생할 수 있기 때문에 금액 제한과 대상 검증, 실행 횟수 제한 등이 함께 적용되어야겠죠!
Permission Should Expire When Its Purpose Ends!
AI 에이전트가 더 많은 작업을 자동으로 처리하는 시대에는 권한을 얼마나 안전하게 부여하는지뿐만 아니라, 언제 그 권한을 종료해야 하는지도 중요한 보안 요소가 될 것입니다.
저는 이런 Time-Bound Authorization과 자동 권한 철회 구조가 앞으로 Rialo를 활용한 Agent Economy에서 더욱 중요한 역할을 할 것 같습니다!!🥰
리알로 파이팅!!

Optimum Peer-Turbo: Bringing MIT Research Into the Future of P2P Broadcasting #19
@get_optimum
One of the most interesting things about blockchain infrastructure is seeing academic research turn into technology that actually runs on live networks.
That's exactly what we're starting to see with Optimum.
At this year's IEEE Information Theory Workshop, Optimum presented its latest research paper, "Optimum Peer-Turbo: A Scalable and Efficient Solution for P2P Broadcasting."
The research builds on years of work originating from MIT, where the technology behind Optimum was developed.
And there's an important milestone here.
Optimum's first protocol has recently gone live on Ethereum mainnet, marking the transition from academic research into real blockchain infrastructure.
But the new Peer-Turbo paper looks beyond Ethereum.
It explores how similar ideas can improve data broadcasting in networks such as Solana and Monad, where information needs to reach large groups of validators within strict time limits.
So, what problem is Peer-Turbo trying to solve?
In many high-performance blockchains, data is distributed through tree-shaped or star-shaped broadcasting structures.
A source node sends data directly to validators or distributes it through relay nodes, often dividing large payloads into smaller pieces called shards.
This approach can reduce the number of network hops, but it introduces a major bottleneck.
The source node's outbound bandwidth becomes a limiting factor.
When hundreds or thousands of validators need to receive data quickly, relying too heavily on the original sender can make efficient broadcasting difficult.
Peer-Turbo approaches this problem differently.
Instead of making the source responsible for most of the distribution work, it allows receiving nodes to help one another complete the process.
The key technology behind this is Random Linear Network Coding (RLNC).
With RLNC, nodes can exchange coded combinations of data shards rather than relying entirely on specific missing pieces from the original sender.
These coded shards can help other nodes recover the original data without requiring explicit coordination of which shards each peer already possesses.
In other words, the receiving nodes become active participants in data distribution.
And the theoretical results are particularly interesting.
According to the paper, Peer-Turbo can achieve:
1. Up to 10× Lower Source Bandwidth Requirements
For a given service-quality target, the model shows that Peer-Turbo can reduce the bandwidth required from the original sender by up to an order of magnitude.
2. Up to 10× Lower Propagation Latency
Under fixed bandwidth constraints, the approach can alternatively reduce propagation latency by an order of magnitude.
3. More Efficient Peer Collaboration
By allowing nodes to exchange coded shards, Peer-Turbo reduces dependence on the source node and avoids the need for explicit shard-state coordination.
4. Potential Applications Beyond Ethereum
The research targets broadcasting architectures relevant to high-performance networks such as Solana and Monad, showing how Optimum's underlying approach could extend across different blockchain ecosystems.
One detail worth emphasizing is that these improvements come from the paper's analytical model rather than a guarantee that every live deployment will achieve identical results.
Actual performance will depend on network topology, bandwidth conditions, and implementation.
Still, I think the broader direction is worth paying attention to.
For years, blockchain scaling discussions have largely focused on execution speed, block capacity, and transaction throughput.
But even the fastest execution environment needs an efficient way to distribute information across its validator network.
And as blockchains become more demanding, the bandwidth required to broadcast data may become an increasingly important constraint.
What makes Optimum interesting is that it's approaching this challenge through information theory and network coding rather than simply asking nodes to use more powerful hardware.
The Ethereum mainnet deployment shows that Optimum's research is already moving into production, while Peer-Turbo explores how those ideas can be applied to other broadcasting architectures.
The next major improvement in blockchain performance might not come from processing more data, but from finding a smarter way to move it.
And that's the direction Optimum is exploring with Peer-Turbo.
Why Optimum Gateway v1.0.2 Is a Mandatory Upgrade for Validator Operators #18
@get_optimum
When it comes to validator infrastructure, software updates aren't always as simple as installing a new version.
Some releases introduce minor improvements, while others mark a point where older versions are no longer supported.
Optimum Gateway v1.0.2 falls into the second category.
According to the Optimum Gateway User Guide, v1.0.2 is a mandatory upgrade for all partners, replacing every earlier release, including the previous release candidates rc11 and rc12.
For operators already testing or preparing to deploy the Gateway, this is an important detail.
Running an outdated version of infrastructure software isn't just about missing new features. It can also mean operating outside the versions officially supported by the network provider.
And when that software is responsible for forwarding Ethereum consensus messages, version compatibility deserves attention.
Optimum Gateway connects existing Consensus Layer clients to the Optimump2p network, forwarding beacon blocks and attestations through an additional networking path.
The Gateway also handles several operational tasks, including peer discovery, fork digest information, authentication, and remote telemetry.
All of these components need to work together for the Gateway to operate as intended.
This is why maintaining a supported Gateway version matters.
There are three practical points worth considering.
1. A Clear Supported Version
With v1.0.2 replacing earlier releases, partners have a defined version to use rather than continuing to operate on older release candidates.
2. Consistent Deployment Environments
For operators managing multiple Gateway instances, standardizing deployments around the required version can help reduce configuration differences and simplify troubleshooting.
3. Better Operational Preparation
Operators can align their deployment process with the current documentation, API key onboarding requirements, and supported Gateway architecture.
It's also worth noting that v1.0.2 doesn't require validators to abandon their existing Consensus Layer clients.
Optimum Gateway is designed to work alongside Prysm, Lighthouse, Teku, Nimbus, and Lodestar, allowing operators to retain their existing Ethereum consensus infrastructure.
The upgrade requirement applies to the Gateway itself, not to replacing the validator's entire software stack.
Of course, a mandatory upgrade doesn't automatically mean every previous release contained a critical vulnerability or performance issue.
The documentation establishes that older versions are unsupported, but that alone doesn't tell us the specific technical reasons behind the version change.
What it does tell us is that Optimum is establishing a clear baseline for partner deployments.
And that's an important part of infrastructure maturity.
Building a faster networking layer is one challenge. Making sure operators can deploy and maintain that layer consistently is another.
As Optimum continues onboarding validator operators and expanding its networking infrastructure, supported versions and predictable deployment practices will become increasingly important.
Because reliable infrastructure isn't only about how fast a network performs. It's also about how consistently that infrastructure can be maintained.


Why Optimum Gateway v1.0.2 Is a Mandatory Upgrade for Validator Operators #18
@get_optimum
When it comes to validator infrastructure, software updates aren't always as simple as installing a new version.
Some releases introduce minor improvements, while others mark a point where older versions are no longer supported.
Optimum Gateway v1.0.2 falls into the second category.
According to the Optimum Gateway User Guide, v1.0.2 is a mandatory upgrade for all partners, replacing every earlier release, including the previous release candidates rc11 and rc12.
For operators already testing or preparing to deploy the Gateway, this is an important detail.
Running an outdated version of infrastructure software isn't just about missing new features. It can also mean operating outside the versions officially supported by the network provider.
And when that software is responsible for forwarding Ethereum consensus messages, version compatibility deserves attention.
Optimum Gateway connects existing Consensus Layer clients to the Optimump2p network, forwarding beacon blocks and attestations through an additional networking path.
The Gateway also handles several operational tasks, including peer discovery, fork digest information, authentication, and remote telemetry.
All of these components need to work together for the Gateway to operate as intended.
This is why maintaining a supported Gateway version matters.
There are three practical points worth considering.
1. A Clear Supported Version
With v1.0.2 replacing earlier releases, partners have a defined version to use rather than continuing to operate on older release candidates.
2. Consistent Deployment Environments
For operators managing multiple Gateway instances, standardizing deployments around the required version can help reduce configuration differences and simplify troubleshooting.
3. Better Operational Preparation
Operators can align their deployment process with the current documentation, API key onboarding requirements, and supported Gateway architecture.
It's also worth noting that v1.0.2 doesn't require validators to abandon their existing Consensus Layer clients.
Optimum Gateway is designed to work alongside Prysm, Lighthouse, Teku, Nimbus, and Lodestar, allowing operators to retain their existing Ethereum consensus infrastructure.
The upgrade requirement applies to the Gateway itself, not to replacing the validator's entire software stack.
Of course, a mandatory upgrade doesn't automatically mean every previous release contained a critical vulnerability or performance issue.
The documentation establishes that older versions are unsupported, but that alone doesn't tell us the specific technical reasons behind the version change.
What it does tell us is that Optimum is establishing a clear baseline for partner deployments.
And that's an important part of infrastructure maturity.
Building a faster networking layer is one challenge. Making sure operators can deploy and maintain that layer consistently is another.
As Optimum continues onboarding validator operators and expanding its networking infrastructure, supported versions and predictable deployment practices will become increasingly important.
Because reliable infrastructure isn't only about how fast a network performs. It's also about how consistently that infrastructure can be maintained.
Why Optimum Gateway Automatically Manages Fork Digests for Ethereum Validators #17
@get_optimum
Ethereum doesn't remain the same forever.
Every major network upgrade introduces changes to the protocol, and validators need to make sure they're communicating with peers that understand the same consensus rules.
This becomes particularly important at the networking layer.
Ethereum's Consensus Layer uses something called a Fork Digest, a compact identifier that helps distinguish the active fork version of the network.
When nodes exchange consensus messages through gossip topics, the fork digest helps identify which protocol version those messages belong to.
This might sound like a small technical detail, but it plays an important role in keeping validator communication organized.
Imagine a validator running on an upgraded Ethereum network while its networking configuration still references an older fork.
Even if the validator itself is functioning correctly, mismatched networking information could prevent it from subscribing to the appropriate gossip topics or communicating as expected.
For infrastructure operators, this creates another configuration detail that needs to stay accurate.
And that's where Optimum Gateway takes a different approach.
According to its Gateway architecture, Optimum handles fork digest information automatically, removing the need for operators to manually maintain separate network-specific YAML configurations.
The Gateway obtains its chain and validator scope through the API key issued by the Optimum Partner Console, while network discovery and fork-related information are managed as part of its connection process.
This matters for several reasons.
1. Fewer Configuration Errors
Operators don't need to manually enter fork digest values into separate Optimum networking configurations, reducing the risk of mismatched settings.
2. Simpler Network Operations
As Ethereum evolves, automated handling of fork-related networking information reduces the amount of configuration work required from Gateway operators.
3. Better Protocol Compatibility
Correct fork information helps the Gateway subscribe to the appropriate consensus topics and operate within the intended network environment.
4. Easier Infrastructure Scaling
For operators managing multiple Gateway instances, reducing manually maintained network parameters makes deployments easier to standardize.
Of course, this doesn't mean Optimum Gateway can replace normal Ethereum client upgrades.
Consensus Layer clients still need to support the network's active protocol rules, and operators remain responsible for keeping their validator software updated.
The Gateway simply removes one additional layer of networking configuration from that process.
And I think that's an important distinction.
A lot of blockchain infrastructure focuses on introducing new capabilities, but operational improvements often come from removing tasks that operators shouldn't have to repeat manually.
Fork digest management is a good example.
It's a relatively small part of Ethereum's networking architecture, yet getting it wrong can interfere with communication.
By handling this information automatically, Optimum Gateway makes its additional networking layer easier to integrate into existing validator setups.
The less time operators spend maintaining network configuration, the more attention they can give to the infrastructure that actually runs consensus.

bori's rialo #243
[ Why Rialo Must Prevent Persistent Permissions in AI Agent Workflows ]
@RialoHQ
@RialoKorea
안녕하세요! 보리입니다!
지난 글에서는 AI 에이전트가 사용하는 도구에 필요 이상의 권한을 부여하면 발생할 수 있는 Excessive Tool Permissions와 최소 권한 원칙에 대해 알아봤는데요!
그런데 여기서 한 가지 더 생각해볼 문제가 있습니다.
처음에는 정상적으로 부여된 권한이라도, 작업이 끝난 뒤까지 계속 유지된다면 어떻게 될까요?
AI 에이전트는 다양한 작업을 자동으로 수행하기 위해 지갑이나 API, 스마트 컨트랙트 등에 접근할 수 있는 권한을 부여받습니다.
문제는 특정 작업을 위해 허용된 권한이 실제로는 훨씬 오랫동안 유지될 수 있다는 점인데요!
예를 들어 DeFi 포트폴리오를 관리하는 AI 에이전트가 있다고 해볼게요.
사용자는 에이전트에게 특정 토큰을 100 USDC만큼 매수하도록 요청했고, 이를 위해 거래 실행 권한을 부여했습니다.
그런데 거래가 정상적으로 완료된 이후에도 해당 권한이 계속 유지된다면 어떨까요?
나중에 에이전트가 Prompt Injection 공격에 노출되거나 연결된 도구가 손상되었을 때, 이미 부여된 권한을 이용해 추가 거래를 시도할 수도 있겠죠ㅠㅠ
이것이 바로 Permission Persistence, 즉 작업이 끝난 이후에도 권한이 지속되는 문제입니다!!
저는 앞으로 Agent Economy에서는 권한의 범위를 제한하는 것만큼이나, 그 권한이 언제까지 유효해야 하는지를 관리하는 것이 중요해질 것이라고 생각합니다ㅎㅎ
여기서 활용할 수 있는 개념이 바로 Time-Bound Authorization과 Just-in-Time Access인데요!
Time-Bound Authorization은 권한에 유효 기간을 설정하는 방식이고, Just-in-Time Access는 실제 작업이 필요한 순간에만 권한을 부여하는 접근 방식입니다.
예를 들어 AI 에이전트가 특정 거래를 실행할 때 5분 동안만 유효한 권한을 부여하고, 시간이 지나면 자동으로 만료되도록 설계할 수 있습니다.
또는 거래가 성공적으로 완료되면 남아 있는 실행 권한을 즉시 철회하는 Automatic Permission Revocation도 생각해볼 수 있겠죠!
그리고 리알로(Rialo)의 Reactive Architecture에서는 이러한 조건 기반 권한 관리가 흥미로운 활용 사례가 될 수 있습니다.
단순히 거래 금액과 대상 주소만 확인하는 것이 아니라, 현재 시간이 허용된 범위 안에 있는지, 해당 작업이 이미 완료되었는지, 권한이 아직 유효한지까지 실행 조건에 포함하는 것이죠!
여기에 REX 기반의 정책 검증을 결합한다면 중요한 키를 직접 노출하지 않으면서도 유효한 권한과 실행 조건을 충족한 요청에 대해서만 사용하도록 제한하는 구조를 생각해볼 수 있습니다.
물론 권한의 만료 시간을 설정하는 것만으로 모든 문제가 해결되지는 않습니다. 유효 기간 안에서도 공격이 발생할 수 있기 때문에 금액 제한과 대상 검증, 실행 횟수 제한 등이 함께 적용되어야겠죠!
Permission Should Expire When Its Purpose Ends!
AI 에이전트가 더 많은 작업을 자동으로 처리하는 시대에는 권한을 얼마나 안전하게 부여하는지뿐만 아니라, 언제 그 권한을 종료해야 하는지도 중요한 보안 요소가 될 것입니다.
저는 이런 Time-Bound Authorization과 자동 권한 철회 구조가 앞으로 Rialo를 활용한 Agent Economy에서 더욱 중요한 역할을 할 것 같습니다!!🥰
리알로 파이팅!!
bori's rialo #242
[ Why Rialo Must Bind AI Agent Permissions to Specific Tasks ]
@RialoHQ
@RialoKorea
안녕하세요! 보리입니다!
지난 글에서는 AI 에이전트에게 부여된 권한이 작업이 끝난 이후에도 계속 유지되면 발생할 수 있는 Permission Persistence와 Time-Bound Authorization에 대해 알아봤는데요!
그런데 여기서 한 가지 더 생각해볼 문제가 있습니다.
권한이 아직 유효한 시간 안에 있더라도, 원래 허용된 작업이 아닌 다른 작업에 사용된다면 어떻게 될까요?
AI 에이전트는 여러 작업을 동시에 처리하거나, 하나의 작업을 여러 단계로 나누어 실행할 수 있습니다.
문제는 특정 작업을 위해 부여된 권한이 다른 작업에서도 사용될 수 있다는 점인데요!
예를 들어 DeFi 포트폴리오를 관리하는 AI 에이전트가 있다고 해볼게요.
사용자는 에이전트에게 100 USDC로 ETH를 매수하도록 요청했고, 이를 위해 5분 동안 유효한 거래 권한을 부여했습니다.
그런데 거래가 완료되기 전에 에이전트가 외부 데이터에 포함된 악의적인 명령을 읽었다고 가정해보겠습니다.
공격자가 해당 권한을 이용해 ETH가 아닌 다른 토큰을 매수하도록 유도한다면 어떨까요?
거래 금액도 100 USDC이고, 권한의 유효 시간도 지나지 않았습니다.
하지만 사용자가 실제로 승인한 작업과는 전혀 다른 행동이겠죠ㅠㅠ
이것이 바로 Task-Bound Authorization, 즉 권한을 특정 작업의 목적과 연결하는 것이 중요한 이유입니다!!
저는 앞으로 Agent Economy에서는 권한의 금액과 시간만 제한하는 것으로는 충분하지 않을 수 있다고 생각합니다.
그 권한이 정확히 어떤 작업을 위해 발급되었는지까지 확인해야 하기 때문인데요!
여기서 중요한 개념은 Intent Verification, Task Context Binding, Scoped Authorization입니다.
예를 들어 사용자가 승인한 작업이 '100 USDC로 ETH 매수'라면, 실행 권한에도 토큰 종류와 최대 금액, 허용된 컨트랙트, 작업 식별자 등의 조건을 연결하는 것이죠!
이렇게 하면 에이전트가 다른 거래를 시도하더라도 기존 권한을 그대로 재사용하지 못하도록 설계할 수 있습니다.
그리고 리알로(Rialo)의 Reactive Architecture에서도 이러한 접근은 흥미로운 활용 사례가 될 수 있는데요ㅎㅎ
사용자가 설정한 조건이 충족되었을 때 자동으로 트랜잭션을 실행하더라도, 실제 실행 요청이 처음 승인된 작업의 목적과 일치하는지 다시 검증하도록 만드는 것입니다.
여기에 REX 기반의 정책 검증을 결합한다면, 중요한 키를 보호하면서도 특정 작업에 연결된 권한이 다른 작업에 사용되지 않도록 제한하는 구조를 생각해볼 수 있고요!
물론 Task-Bound Authorization을 적용하더라도 사용자가 처음 승인한 작업 자체가 위험하다면 문제가 발생할 수 있습니다.
따라서 작업의 목적을 검증하는 것과 함께 실행 대상의 안전성, 데이터의 신뢰성, 거래 조건까지 확인하는 것이 중요하겠죠!
Permission for One Task Should Never Become Permission for Every Task!
AI 에이전트가 더 복잡한 작업을 자율적으로 수행할수록 중요한 것은 단순히 실행 권한을 가지고 있는지가 아니라, 그 권한이 지금 수행하려는 작업을 위해 부여된 것인지 확인하는 일이라고 생각합니다.
저는 이런 Task-Bound Authorization과 검증 가능한 실행 구조가 앞으로 Rialo를 활용한 Agent Economy에서 더욱 중요한 보안 원칙이 될 것 같습니다!!🥰
리알로 파이팅!!

Why Optimum Gateway Automatically Manages Fork Digests for Ethereum Validators #17
@get_optimum
Ethereum doesn't remain the same forever.
Every major network upgrade introduces changes to the protocol, and validators need to make sure they're communicating with peers that understand the same consensus rules.
This becomes particularly important at the networking layer.
Ethereum's Consensus Layer uses something called a Fork Digest, a compact identifier that helps distinguish the active fork version of the network.
When nodes exchange consensus messages through gossip topics, the fork digest helps identify which protocol version those messages belong to.
This might sound like a small technical detail, but it plays an important role in keeping validator communication organized.
Imagine a validator running on an upgraded Ethereum network while its networking configuration still references an older fork.
Even if the validator itself is functioning correctly, mismatched networking information could prevent it from subscribing to the appropriate gossip topics or communicating as expected.
For infrastructure operators, this creates another configuration detail that needs to stay accurate.
And that's where Optimum Gateway takes a different approach.
According to its Gateway architecture, Optimum handles fork digest information automatically, removing the need for operators to manually maintain separate network-specific YAML configurations.
The Gateway obtains its chain and validator scope through the API key issued by the Optimum Partner Console, while network discovery and fork-related information are managed as part of its connection process.
This matters for several reasons.
1. Fewer Configuration Errors
Operators don't need to manually enter fork digest values into separate Optimum networking configurations, reducing the risk of mismatched settings.
2. Simpler Network Operations
As Ethereum evolves, automated handling of fork-related networking information reduces the amount of configuration work required from Gateway operators.
3. Better Protocol Compatibility
Correct fork information helps the Gateway subscribe to the appropriate consensus topics and operate within the intended network environment.
4. Easier Infrastructure Scaling
For operators managing multiple Gateway instances, reducing manually maintained network parameters makes deployments easier to standardize.
Of course, this doesn't mean Optimum Gateway can replace normal Ethereum client upgrades.
Consensus Layer clients still need to support the network's active protocol rules, and operators remain responsible for keeping their validator software updated.
The Gateway simply removes one additional layer of networking configuration from that process.
And I think that's an important distinction.
A lot of blockchain infrastructure focuses on introducing new capabilities, but operational improvements often come from removing tasks that operators shouldn't have to repeat manually.
Fork digest management is a good example.
It's a relatively small part of Ethereum's networking architecture, yet getting it wrong can interfere with communication.
By handling this information automatically, Optimum Gateway makes its additional networking layer easier to integrate into existing validator setups.
The less time operators spend maintaining network configuration, the more attention they can give to the infrastructure that actually runs consensus.
Why Optimum Uses Short-Lived JWTs to Secure Gateway Authentication #16
@get_optimum
When running validator infrastructure, most people focus on network speed, bandwidth, and uptime.
But there's another important question that often gets overlooked.
How does the network know which Gateway is actually authorized to connect?
This is particularly important for Optimum, where Gateway instances connect Ethereum Consensus Layer clients to the Optimump2p network.
Allowing every Gateway to connect without proper authentication would make it difficult to manage identities, validator permissions, and network access.
Optimum addresses this through an API Key and Short-Lived JWT authentication model.
The process begins with the Optimum Partner Console, where approved partners receive an API key during onboarding.
That API key carries the information needed to identify the Gateway, including its gateway_id, chain, and validator scope.
However, the Gateway doesn't simply use this long-lived credential as its permanent authentication token.
Instead, the API key is exchanged for a short-lived JSON Web Token (JWT).
This distinction is important.
API keys are generally designed to provide persistent credentials, while short-lived tokens allow systems to authenticate requests using credentials with a limited validity period.
By separating the initial credential from the token used for subsequent authenticated communication, Optimum can reduce reliance on repeatedly transmitting the original API key.
There are several practical reasons why this approach makes sense.
1. Limited Credential Lifetime
A short-lived JWT has a defined expiration period. If a token is exposed, its useful lifetime is limited compared with a credential that remains valid indefinitely.
2. Gateway Identity and Scope
The authentication process is tied to the Gateway's identity, chain, and validator scope, allowing Optimum's infrastructure to distinguish between authorized deployments.
3. Easier Credential Management
Operators can use the API key issued through the Partner Console without manually maintaining separate identity configurations for every supported network.
4. Better Separation of Responsibilities
The API key serves as the initial credential, while the JWT provides temporary authentication for subsequent interactions.
Of course, short-lived tokens don't eliminate every security risk.
A compromised API key can still be dangerous, and secure credential storage remains essential. Token expiration is only one part of a broader authentication strategy.
Still, the design reflects an important principle in infrastructure security:
Long-term identity and short-term access don't have to rely on the same credential.
For validator operators, authentication should be secure without becoming another complicated operational burden.
Optimum Gateway brings these two requirements together by combining Partner Console onboarding, API-based identity, and temporary JWT authentication.
As validator networking becomes more interconnected, protecting access to that infrastructure will matter just as much as improving its performance.
And Optimum's authentication architecture shows how security can be built directly into the networking layer rather than treated as an afterthought.

bori's rialo #242
[ Why Rialo Must Bind AI Agent Permissions to Specific Tasks ]
@RialoHQ
@RialoKorea
안녕하세요! 보리입니다!
지난 글에서는 AI 에이전트에게 부여된 권한이 작업이 끝난 이후에도 계속 유지되면 발생할 수 있는 Permission Persistence와 Time-Bound Authorization에 대해 알아봤는데요!
그런데 여기서 한 가지 더 생각해볼 문제가 있습니다.
권한이 아직 유효한 시간 안에 있더라도, 원래 허용된 작업이 아닌 다른 작업에 사용된다면 어떻게 될까요?
AI 에이전트는 여러 작업을 동시에 처리하거나, 하나의 작업을 여러 단계로 나누어 실행할 수 있습니다.
문제는 특정 작업을 위해 부여된 권한이 다른 작업에서도 사용될 수 있다는 점인데요!
예를 들어 DeFi 포트폴리오를 관리하는 AI 에이전트가 있다고 해볼게요.
사용자는 에이전트에게 100 USDC로 ETH를 매수하도록 요청했고, 이를 위해 5분 동안 유효한 거래 권한을 부여했습니다.
그런데 거래가 완료되기 전에 에이전트가 외부 데이터에 포함된 악의적인 명령을 읽었다고 가정해보겠습니다.
공격자가 해당 권한을 이용해 ETH가 아닌 다른 토큰을 매수하도록 유도한다면 어떨까요?
거래 금액도 100 USDC이고, 권한의 유효 시간도 지나지 않았습니다.
하지만 사용자가 실제로 승인한 작업과는 전혀 다른 행동이겠죠ㅠㅠ
이것이 바로 Task-Bound Authorization, 즉 권한을 특정 작업의 목적과 연결하는 것이 중요한 이유입니다!!
저는 앞으로 Agent Economy에서는 권한의 금액과 시간만 제한하는 것으로는 충분하지 않을 수 있다고 생각합니다.
그 권한이 정확히 어떤 작업을 위해 발급되었는지까지 확인해야 하기 때문인데요!
여기서 중요한 개념은 Intent Verification, Task Context Binding, Scoped Authorization입니다.
예를 들어 사용자가 승인한 작업이 '100 USDC로 ETH 매수'라면, 실행 권한에도 토큰 종류와 최대 금액, 허용된 컨트랙트, 작업 식별자 등의 조건을 연결하는 것이죠!
이렇게 하면 에이전트가 다른 거래를 시도하더라도 기존 권한을 그대로 재사용하지 못하도록 설계할 수 있습니다.
그리고 리알로(Rialo)의 Reactive Architecture에서도 이러한 접근은 흥미로운 활용 사례가 될 수 있는데요ㅎㅎ
사용자가 설정한 조건이 충족되었을 때 자동으로 트랜잭션을 실행하더라도, 실제 실행 요청이 처음 승인된 작업의 목적과 일치하는지 다시 검증하도록 만드는 것입니다.
여기에 REX 기반의 정책 검증을 결합한다면, 중요한 키를 보호하면서도 특정 작업에 연결된 권한이 다른 작업에 사용되지 않도록 제한하는 구조를 생각해볼 수 있고요!
물론 Task-Bound Authorization을 적용하더라도 사용자가 처음 승인한 작업 자체가 위험하다면 문제가 발생할 수 있습니다.
따라서 작업의 목적을 검증하는 것과 함께 실행 대상의 안전성, 데이터의 신뢰성, 거래 조건까지 확인하는 것이 중요하겠죠!
Permission for One Task Should Never Become Permission for Every Task!
AI 에이전트가 더 복잡한 작업을 자율적으로 수행할수록 중요한 것은 단순히 실행 권한을 가지고 있는지가 아니라, 그 권한이 지금 수행하려는 작업을 위해 부여된 것인지 확인하는 일이라고 생각합니다.
저는 이런 Task-Bound Authorization과 검증 가능한 실행 구조가 앞으로 Rialo를 활용한 Agent Economy에서 더욱 중요한 보안 원칙이 될 것 같습니다!!🥰
리알로 파이팅!!
bori's rialo #241
[ Why Rialo Must Prevent Persistent Permissions in AI Agent Workflows ]
@RialoHQ
@RialoKorea
안녕하세요! 보리입니다!
지난 글에서는 AI 에이전트가 사용하는 도구에 필요 이상의 권한을 부여하면 발생할 수 있는 Excessive Tool Permissions와 최소 권한 원칙에 대해 알아봤는데요!
그런데 여기서 한 가지 더 생각해볼 문제가 있습니다.
처음에는 정상적으로 부여된 권한이라도, 작업이 끝난 뒤까지 계속 유지된다면 어떻게 될까요?
AI 에이전트는 다양한 작업을 자동으로 수행하기 위해 지갑이나 API, 스마트 컨트랙트 등에 접근할 수 있는 권한을 부여받습니다.
문제는 특정 작업을 위해 허용된 권한이 실제로는 훨씬 오랫동안 유지될 수 있다는 점인데요!
예를 들어 DeFi 포트폴리오를 관리하는 AI 에이전트가 있다고 해볼게요.
사용자는 에이전트에게 특정 토큰을 100 USDC만큼 매수하도록 요청했고, 이를 위해 거래 실행 권한을 부여했습니다.
그런데 거래가 정상적으로 완료된 이후에도 해당 권한이 계속 유지된다면 어떨까요?
나중에 에이전트가 Prompt Injection 공격에 노출되거나 연결된 도구가 손상되었을 때, 이미 부여된 권한을 이용해 추가 거래를 시도할 수도 있겠죠ㅠㅠ
이것이 바로 Permission Persistence, 즉 작업이 끝난 이후에도 권한이 지속되는 문제입니다!!
저는 앞으로 Agent Economy에서는 권한의 범위를 제한하는 것만큼이나, 그 권한이 언제까지 유효해야 하는지를 관리하는 것이 중요해질 것이라고 생각합니다ㅎㅎ
여기서 활용할 수 있는 개념이 바로 Time-Bound Authorization과 Just-in-Time Access인데요!
Time-Bound Authorization은 권한에 유효 기간을 설정하는 방식이고, Just-in-Time Access는 실제 작업이 필요한 순간에만 권한을 부여하는 접근 방식입니다.
예를 들어 AI 에이전트가 특정 거래를 실행할 때 5분 동안만 유효한 권한을 부여하고, 시간이 지나면 자동으로 만료되도록 설계할 수 있습니다.
또는 거래가 성공적으로 완료되면 남아 있는 실행 권한을 즉시 철회하는 Automatic Permission Revocation도 생각해볼 수 있겠죠!
그리고 리알로(Rialo)의 Reactive Architecture에서는 이러한 조건 기반 권한 관리가 흥미로운 활용 사례가 될 수 있습니다.
단순히 거래 금액과 대상 주소만 확인하는 것이 아니라, 현재 시간이 허용된 범위 안에 있는지, 해당 작업이 이미 완료되었는지, 권한이 아직 유효한지까지 실행 조건에 포함하는 것이죠!
여기에 REX 기반의 정책 검증을 결합한다면 중요한 키를 직접 노출하지 않으면서도 유효한 권한과 실행 조건을 충족한 요청에 대해서만 사용하도록 제한하는 구조를 생각해볼 수 있습니다.
물론 권한의 만료 시간을 설정하는 것만으로 모든 문제가 해결되지는 않습니다. 유효 기간 안에서도 공격이 발생할 수 있기 때문에 금액 제한과 대상 검증, 실행 횟수 제한 등이 함께 적용되어야겠죠!
Permission Should Expire When Its Purpose Ends!
AI 에이전트가 더 많은 작업을 자동으로 처리하는 시대에는 권한을 얼마나 안전하게 부여하는지뿐만 아니라, 언제 그 권한을 종료해야 하는지도 중요한 보안 요소가 될 것입니다.
저는 이런 Time-Bound Authorization과 자동 권한 철회 구조가 앞으로 Rialo를 활용한 Agent Economy에서 더욱 중요한 역할을 할 것 같습니다!!🥰
리알로 파이팅!!

bori's rialo #241
[ Why Rialo Must Prevent Persistent Permissions in AI Agent Workflows ]
@RialoHQ
@RialoKorea
안녕하세요! 보리입니다!
지난 글에서는 AI 에이전트가 사용하는 도구에 필요 이상의 권한을 부여하면 발생할 수 있는 Excessive Tool Permissions와 최소 권한 원칙에 대해 알아봤는데요!
그런데 여기서 한 가지 더 생각해볼 문제가 있습니다.
처음에는 정상적으로 부여된 권한이라도, 작업이 끝난 뒤까지 계속 유지된다면 어떻게 될까요?
AI 에이전트는 다양한 작업을 자동으로 수행하기 위해 지갑이나 API, 스마트 컨트랙트 등에 접근할 수 있는 권한을 부여받습니다.
문제는 특정 작업을 위해 허용된 권한이 실제로는 훨씬 오랫동안 유지될 수 있다는 점인데요!
예를 들어 DeFi 포트폴리오를 관리하는 AI 에이전트가 있다고 해볼게요.
사용자는 에이전트에게 특정 토큰을 100 USDC만큼 매수하도록 요청했고, 이를 위해 거래 실행 권한을 부여했습니다.
그런데 거래가 정상적으로 완료된 이후에도 해당 권한이 계속 유지된다면 어떨까요?
나중에 에이전트가 Prompt Injection 공격에 노출되거나 연결된 도구가 손상되었을 때, 이미 부여된 권한을 이용해 추가 거래를 시도할 수도 있겠죠ㅠㅠ
이것이 바로 Permission Persistence, 즉 작업이 끝난 이후에도 권한이 지속되는 문제입니다!!
저는 앞으로 Agent Economy에서는 권한의 범위를 제한하는 것만큼이나, 그 권한이 언제까지 유효해야 하는지를 관리하는 것이 중요해질 것이라고 생각합니다ㅎㅎ
여기서 활용할 수 있는 개념이 바로 Time-Bound Authorization과 Just-in-Time Access인데요!
Time-Bound Authorization은 권한에 유효 기간을 설정하는 방식이고, Just-in-Time Access는 실제 작업이 필요한 순간에만 권한을 부여하는 접근 방식입니다.
예를 들어 AI 에이전트가 특정 거래를 실행할 때 5분 동안만 유효한 권한을 부여하고, 시간이 지나면 자동으로 만료되도록 설계할 수 있습니다.
또는 거래가 성공적으로 완료되면 남아 있는 실행 권한을 즉시 철회하는 Automatic Permission Revocation도 생각해볼 수 있겠죠!
그리고 리알로(Rialo)의 Reactive Architecture에서는 이러한 조건 기반 권한 관리가 흥미로운 활용 사례가 될 수 있습니다.
단순히 거래 금액과 대상 주소만 확인하는 것이 아니라, 현재 시간이 허용된 범위 안에 있는지, 해당 작업이 이미 완료되었는지, 권한이 아직 유효한지까지 실행 조건에 포함하는 것이죠!
여기에 REX 기반의 정책 검증을 결합한다면 중요한 키를 직접 노출하지 않으면서도 유효한 권한과 실행 조건을 충족한 요청에 대해서만 사용하도록 제한하는 구조를 생각해볼 수 있습니다.
물론 권한의 만료 시간을 설정하는 것만으로 모든 문제가 해결되지는 않습니다. 유효 기간 안에서도 공격이 발생할 수 있기 때문에 금액 제한과 대상 검증, 실행 횟수 제한 등이 함께 적용되어야겠죠!
Permission Should Expire When Its Purpose Ends!
AI 에이전트가 더 많은 작업을 자동으로 처리하는 시대에는 권한을 얼마나 안전하게 부여하는지뿐만 아니라, 언제 그 권한을 종료해야 하는지도 중요한 보안 요소가 될 것입니다.
저는 이런 Time-Bound Authorization과 자동 권한 철회 구조가 앞으로 Rialo를 활용한 Agent Economy에서 더욱 중요한 역할을 할 것 같습니다!!🥰
리알로 파이팅!!
[ Rialo Builders Hub Recap ]
@RialoHQ
@RialoKorea
안녕하세요! 리알로에 진심인 보리입니다! 💜
이번 Rialo Builders Hub에서는 MotoGo와 QuadCell이라는 두 프로젝트를 만나볼 수 있었는데요!
하나는 AI Agent를 활용한 보험금 청구 자동화, 다른 하나는 다양한 Web3 금융 서비스를 하나로 통합하는 플랫폼이라는 점에서 흥미로웠습니다ㅎㅎ
🔹 MotoGo — AI Agent가 처리하는 자동화 보험 플랫폼!
MotoGo는 베트남을 비롯한 동남아시아 시장을 대상으로 개발 중인 오토바이 보험 자동화 플랫폼입니다!
기존 보험은 사고가 발생하면 서류를 제출하고 심사를 기다리는 과정이 복잡한데요.
MotoGo는 사용자가 사고 사진과 정보를 업로드하면 4개의 AI Agent가 역할을 나누어 보험금 청구를 처리하는 구조입니다.
각 Agent는 차량 식별, 정보 검증, 수리 비용 평가, 최종 보상 판단을 담당하며, 심사를 통과하면 USDC로 보험금이 지급됩니다!
충돌 사고뿐 아니라 도난, 제3자 배상책임 등 다양한 상황도 지원하도록 설계되어 있는데요.
특히 AI가 정확하게 판단하기 어려운 경우에는 사람이 직접 검토할 수 있도록 만든 점이 인상적이었습니다ㅎㅎ
현재 Ethereum Sepolia 테스트넷에서 보험 가입부터 청구와 지급까지 전체 과정을 시연했으며, 향후 Rialo의 Native Web Requests, Timers, Reactive Transactions를 활용해 자동화 수준을 높일 계획이라고 합니다!
🔹 QuadCell — Web3 금융을 하나의 플랫폼으로!
두 번째 QuadCell은 여러 Web3 금융 기능을 하나의 인터페이스에서 이용할 수 있도록 만든 All-in-One Web3 Finance Platform입니다!
현재 다섯 가지 주요 모듈을 제공하고 있는데요.
Prediction Market: Yes/No 방식의 이벤트 예측 시장
Perpetual Trading: 최대 20배 레버리지와 USDC 기반 정산
P2P Payment: 자연어 명령을 활용한 간편 송금
Real Estate: 두바이 부동산의 가격과 예상 수익률을 AI로 분석
AI Assistant: 실시간 시세, Fear & Greed Index, DeFi TVL 등 시장 정보 제공
특히 여러 서비스를 이용할 때마다 DApp을 옮겨 다닐 필요 없이 하나의 Wallet과 인터페이스에서 다양한 기능을 이용할 수 있다는 점이 매력적이었어요!
아직 통합 증거금 시스템과 Oracle Layer까지 완전히 연결된 단계는 아니지만, 앞으로 기능들이 더욱 긴밀하게 통합된다면 사용자 편의성이 크게 높아질 수 있을 것 같습니다ㅎㅎ
이번 두 프로젝트를 보면서 느낀 건 AI와 블록체인이 실제 문제를 해결하는 방향으로 발전하고 있다는 점이었습니다!
MotoGo는 복잡한 보험 청구 과정을 자동화하고, QuadCell은 여러 Web3 금융 서비스를 하나로 연결해 사용자의 불편함을 줄이려는 프로젝트니까요.
매주 Builders Hub에서 서로 다른 아이디어가 실제 서비스로 구현되는 모습을 볼 수 있어서 정말 재미있는데요!
앞으로 이 프로젝트들이 Rialo의 기술과 더욱 깊이 연결되면서 어떤 모습으로 발전할지 기대됩니다!! 💜

[ Rialo Builders Hub Recap ]
@RialoHQ
@RialoKorea
안녕하세요! 리알로에 진심인 보리입니다! 💜
이번 Rialo Builders Hub에서는 MotoGo와 QuadCell이라는 두 프로젝트를 만나볼 수 있었는데요!
하나는 AI Agent를 활용한 보험금 청구 자동화, 다른 하나는 다양한 Web3 금융 서비스를 하나로 통합하는 플랫폼이라는 점에서 흥미로웠습니다ㅎㅎ
🔹 MotoGo — AI Agent가 처리하는 자동화 보험 플랫폼!
MotoGo는 베트남을 비롯한 동남아시아 시장을 대상으로 개발 중인 오토바이 보험 자동화 플랫폼입니다!
기존 보험은 사고가 발생하면 서류를 제출하고 심사를 기다리는 과정이 복잡한데요.
MotoGo는 사용자가 사고 사진과 정보를 업로드하면 4개의 AI Agent가 역할을 나누어 보험금 청구를 처리하는 구조입니다.
각 Agent는 차량 식별, 정보 검증, 수리 비용 평가, 최종 보상 판단을 담당하며, 심사를 통과하면 USDC로 보험금이 지급됩니다!
충돌 사고뿐 아니라 도난, 제3자 배상책임 등 다양한 상황도 지원하도록 설계되어 있는데요.
특히 AI가 정확하게 판단하기 어려운 경우에는 사람이 직접 검토할 수 있도록 만든 점이 인상적이었습니다ㅎㅎ
현재 Ethereum Sepolia 테스트넷에서 보험 가입부터 청구와 지급까지 전체 과정을 시연했으며, 향후 Rialo의 Native Web Requests, Timers, Reactive Transactions를 활용해 자동화 수준을 높일 계획이라고 합니다!
🔹 QuadCell — Web3 금융을 하나의 플랫폼으로!
두 번째 QuadCell은 여러 Web3 금융 기능을 하나의 인터페이스에서 이용할 수 있도록 만든 All-in-One Web3 Finance Platform입니다!
현재 다섯 가지 주요 모듈을 제공하고 있는데요.
Prediction Market: Yes/No 방식의 이벤트 예측 시장
Perpetual Trading: 최대 20배 레버리지와 USDC 기반 정산
P2P Payment: 자연어 명령을 활용한 간편 송금
Real Estate: 두바이 부동산의 가격과 예상 수익률을 AI로 분석
AI Assistant: 실시간 시세, Fear & Greed Index, DeFi TVL 등 시장 정보 제공
특히 여러 서비스를 이용할 때마다 DApp을 옮겨 다닐 필요 없이 하나의 Wallet과 인터페이스에서 다양한 기능을 이용할 수 있다는 점이 매력적이었어요!
아직 통합 증거금 시스템과 Oracle Layer까지 완전히 연결된 단계는 아니지만, 앞으로 기능들이 더욱 긴밀하게 통합된다면 사용자 편의성이 크게 높아질 수 있을 것 같습니다ㅎㅎ
이번 두 프로젝트를 보면서 느낀 건 AI와 블록체인이 실제 문제를 해결하는 방향으로 발전하고 있다는 점이었습니다!
MotoGo는 복잡한 보험 청구 과정을 자동화하고, QuadCell은 여러 Web3 금융 서비스를 하나로 연결해 사용자의 불편함을 줄이려는 프로젝트니까요.
매주 Builders Hub에서 서로 다른 아이디어가 실제 서비스로 구현되는 모습을 볼 수 있어서 정말 재미있는데요!
앞으로 이 프로젝트들이 Rialo의 기술과 더욱 깊이 연결되면서 어떤 모습으로 발전할지 기대됩니다!! 💜
bori's rialo #240
[ Why Rialo Must Limit Excessive Tool Permissions in AI Agent Workflows ]
@RialoHQ
@RialoKorea
안녕하세요! 보리입니다!
지난 글에서는 하나의 도구에서 발생한 보안 문제가 다른 도구의 실행까지 영향을 미치는 Tool Chain Hijacking에 대해 알아봤는데요!
그런데 여기서 또 하나의 중요한 문제가 있습니다.
AI 에이전트가 사용하는 도구에 처음부터 너무 많은 권한이 주어져 있다면 어떻게 될까요?
AI 에이전트는 다양한 작업을 자동화하기 위해 외부 API와 스마트 컨트랙트, 지갑, 데이터베이스 등을 연결해 사용합니다.
문제는 편리한 자동화를 위해 도구에 필요 이상의 권한을 부여하는 경우가 있다는 점인데요!
예를 들어 DeFi 포트폴리오를 관리하는 AI 에이전트가 있다고 해볼게요.
이 에이전트의 원래 역할은 토큰 가격을 확인하고, 사용자가 설정한 조건에 따라 소액의 거래를 실행하는 것입니다.
그런데 거래에 사용하는 도구가 특정 토큰에 대한 무제한 사용 승인과 여러 컨트랙트를 호출할 수 있는 권한까지 가지고 있다면 어떨까요?
만약 해당 도구가 공격에 노출되거나 에이전트가 악의적인 명령에 속는다면, 원래 작업에 필요하지 않았던 권한까지 악용될 위험이 생길 수 있습니다ㅠㅠ
이것이 바로 Excessive Tool Permissions, 즉 과도한 도구 권한의 문제입니다!!
저는 앞으로 Agent Economy에서는 AI 에이전트가 얼마나 많은 작업을 수행할 수 있는지보다, 각 작업에 정확히 필요한 권한만 가지고 있는지가 더욱 중요해질 것이라고 생각합니다ㅎㅎ
여기서 핵심이 되는 보안 원칙은 Principle of Least Privilege, 즉 최소 권한 원칙인데요!
예를 들어 가격 조회 도구에는 Read-Only 권한만 부여하고, 거래 실행 도구에는 특정 토큰과 컨트랙트, 금액 한도에 해당하는 권한만 허용하는 방식입니다.
또한 모든 권한을 영구적으로 유지하는 대신, 특정 작업을 수행하는 동안에만 권한을 부여하는 Just-in-Time Authorization도 중요한 접근 방식이 될 수 있습니다.
그리고 리알로(Rialo)의 Reactive Architecture에서는 이런 조건형 권한 관리가 흥미로운 활용 사례가 될 수 있는데요!
예를 들어 AI 에이전트가 100 USDC 이하의 거래만 수행하도록 설정되어 있다면, 외부 도구가 1,000 USDC 거래를 요청하더라도 실제 실행 단계에서 이를 거부하도록 설계하는 것이죠.
여기에 REX 기반의 보호된 실행 환경과 정책 검증을 결합한다면, 중요한 키를 에이전트나 외부 도구에 직접 노출하지 않으면서 허용된 작업에 대해서만 사용하도록 제한하는 구조도 생각해볼 수 있습니다!
물론 최소 권한을 적용했다고 해서 모든 공격이 사라지는 것은 아닙니다. 하지만 하나의 도구가 공격당했을 때 발생할 수 있는 피해 범위를 줄이는 데에는 큰 도움이 될 수 있겠죠!
Give AI Agents the Permissions They Need, Not Every Permission They Can Get!
AI 에이전트가 더 많은 도구를 연결하고 복잡한 작업을 수행할수록 중요한 것은 무제한적인 자유가 아니라, 작업의 목적에 맞게 제한된 권한이라고 생각합니다.
저는 이런 Least Privilege와 조건 기반 실행 정책이 앞으로 Rialo를 활용한 Agent Economy에서 더욱 중요한 보안 원칙이 될 것 같습니다!!🥰
리알로 파이팅!!

bori's rialo #240
[ Why Rialo Must Limit Excessive Tool Permissions in AI Agent Workflows ]
@RialoHQ
@RialoKorea
안녕하세요! 보리입니다!
지난 글에서는 하나의 도구에서 발생한 보안 문제가 다른 도구의 실행까지 영향을 미치는 Tool Chain Hijacking에 대해 알아봤는데요!
그런데 여기서 또 하나의 중요한 문제가 있습니다.
AI 에이전트가 사용하는 도구에 처음부터 너무 많은 권한이 주어져 있다면 어떻게 될까요?
AI 에이전트는 다양한 작업을 자동화하기 위해 외부 API와 스마트 컨트랙트, 지갑, 데이터베이스 등을 연결해 사용합니다.
문제는 편리한 자동화를 위해 도구에 필요 이상의 권한을 부여하는 경우가 있다는 점인데요!
예를 들어 DeFi 포트폴리오를 관리하는 AI 에이전트가 있다고 해볼게요.
이 에이전트의 원래 역할은 토큰 가격을 확인하고, 사용자가 설정한 조건에 따라 소액의 거래를 실행하는 것입니다.
그런데 거래에 사용하는 도구가 특정 토큰에 대한 무제한 사용 승인과 여러 컨트랙트를 호출할 수 있는 권한까지 가지고 있다면 어떨까요?
만약 해당 도구가 공격에 노출되거나 에이전트가 악의적인 명령에 속는다면, 원래 작업에 필요하지 않았던 권한까지 악용될 위험이 생길 수 있습니다ㅠㅠ
이것이 바로 Excessive Tool Permissions, 즉 과도한 도구 권한의 문제입니다!!
저는 앞으로 Agent Economy에서는 AI 에이전트가 얼마나 많은 작업을 수행할 수 있는지보다, 각 작업에 정확히 필요한 권한만 가지고 있는지가 더욱 중요해질 것이라고 생각합니다ㅎㅎ
여기서 핵심이 되는 보안 원칙은 Principle of Least Privilege, 즉 최소 권한 원칙인데요!
예를 들어 가격 조회 도구에는 Read-Only 권한만 부여하고, 거래 실행 도구에는 특정 토큰과 컨트랙트, 금액 한도에 해당하는 권한만 허용하는 방식입니다.
또한 모든 권한을 영구적으로 유지하는 대신, 특정 작업을 수행하는 동안에만 권한을 부여하는 Just-in-Time Authorization도 중요한 접근 방식이 될 수 있습니다.
그리고 리알로(Rialo)의 Reactive Architecture에서는 이런 조건형 권한 관리가 흥미로운 활용 사례가 될 수 있는데요!
예를 들어 AI 에이전트가 100 USDC 이하의 거래만 수행하도록 설정되어 있다면, 외부 도구가 1,000 USDC 거래를 요청하더라도 실제 실행 단계에서 이를 거부하도록 설계하는 것이죠.
여기에 REX 기반의 보호된 실행 환경과 정책 검증을 결합한다면, 중요한 키를 에이전트나 외부 도구에 직접 노출하지 않으면서 허용된 작업에 대해서만 사용하도록 제한하는 구조도 생각해볼 수 있습니다!
물론 최소 권한을 적용했다고 해서 모든 공격이 사라지는 것은 아닙니다. 하지만 하나의 도구가 공격당했을 때 발생할 수 있는 피해 범위를 줄이는 데에는 큰 도움이 될 수 있겠죠!
Give AI Agents the Permissions They Need, Not Every Permission They Can Get!
AI 에이전트가 더 많은 도구를 연결하고 복잡한 작업을 수행할수록 중요한 것은 무제한적인 자유가 아니라, 작업의 목적에 맞게 제한된 권한이라고 생각합니다.
저는 이런 Least Privilege와 조건 기반 실행 정책이 앞으로 Rialo를 활용한 Agent Economy에서 더욱 중요한 보안 원칙이 될 것 같습니다!!🥰
리알로 파이팅!!
bori's rialo #239
[ Why Rialo Must Prevent Tool Chain Hijacking in AI Agent Workflows ]
@RialoHQ
@RialoKorea
안녕하세요! 보리입니다!
지난 글에서는 AI 에이전트가 호출한 도구의 응답에 악의적인 명령을 숨겨 행동을 유도하는 Tool Output Injection에 대해 알아봤는데요!
그런데 여기서 한 가지 더 생각해볼 문제가 있습니다.
하나의 도구에서 발생한 문제가 다른 도구의 실행까지 영향을 준다면 어떻게 될까요?
AI 에이전트는 하나의 도구만 사용하는 것이 아니라 여러 도구를 연결해 복잡한 작업을 수행합니다.
예를 들어 DeFi 에이전트가 토큰을 매수하는 과정을 생각해볼게요!
먼저 Web Search로 프로젝트 정보를 확인하고, Price Oracle로 가격을 조회한 다음, DEX Aggregator에서 최적의 거래 경로를 찾고, 마지막으로 Smart Contract를 통해 거래를 실행합니다.
이처럼 여러 도구가 순서대로 연결되는 구조를 Tool Chain이라고 볼 수 있는데요!
문제는 중간 단계에서 공격자가 악의적인 정보를 주입하면 이후의 도구 호출까지 잘못된 방향으로 이어질 수 있다는 점입니다ㅠㅠ
예를 들어 DEX Aggregator의 응답에 정상적인 거래 경로 대신 공격자가 지정한 컨트랙트 주소가 포함되어 있다고 가정해보겠습니다.
에이전트가 해당 주소를 별도로 검증하지 않고 다음 도구에 전달한다면, 원래 의도했던 거래와 전혀 다른 컨트랙트를 호출하게 될 수도 있겠죠!
이처럼 도구 사이의 데이터 전달과 실행 흐름을 악용해 에이전트의 작업을 가로채는 공격을 Tool Chain Hijacking이라고 설명할 수 있습니다.
저는 앞으로 Agent Economy에서는 개별 도구의 보안뿐만 아니라, 도구와 도구 사이에서 권한과 데이터가 어떻게 전달되는지가 더욱 중요해질 것이라고 생각합니다ㅎㅎ
여기서 핵심이 되는 개념은 Tool-to-Tool Trust Boundary, Data Provenance, Least Privilege, End-to-End Policy Enforcement인데요!
각 도구가 반환한 정보를 다음 단계에서 무조건 신뢰하는 것이 아니라, 데이터의 출처와 목적을 확인하고 실제 실행 권한은 별도로 검증하는 것이죠.
그리고 리알로(Rialo)의 Reactive Architecture에서도 이런 접근을 활용할 수 있습니다!
예를 들어 에이전트가 여러 도구를 거쳐 트랜잭션을 생성하더라도, 최종 실행 단계에서는 처음 사용자가 승인한 조건과 현재 거래 요청이 일치하는지 다시 확인하도록 설계하는 것입니다.
여기에 REX 기반의 정책 검증을 결합한다면 승인되지 않은 컨트랙트 주소나 허용 범위를 벗어난 자산 이동 요청이 보호된 키를 사용하지 못하도록 제한하는 구조도 생각해볼 수 있고요!
물론 REX가 Tool Chain Hijacking 자체를 자동으로 탐지하는 것은 아닙니다. 따라서 각 도구의 응답 검증과 최종 실행 정책이 함께 적용되어야 합니다.
One Compromised Tool Shouldn't Control the Entire Workflow!
AI 에이전트가 수십 개의 도구를 자유롭게 연결하는 시대에는 단순히 각각의 도구가 안전한지 확인하는 것만으로는 부족할 수 있습니다.
저는 도구 사이의 신뢰 경계를 유지하고 마지막 실행 순간까지 권한을 검증하는 구조가 앞으로 Rialo 기반 Agent Economy에서 더욱 중요한 역할을 할 것 같습니다!!🥰
리알로 파이팅!!
