


Pinned Tweet
Blog post is published

Details on the critical RCE vulnerability we discovered in Microsoft Web Deploy CVE-2025-53772.
hawktrace.com/blog/cve-2025-…
#iiswebdeploy #infosec #webdeploy #iis #cve-2025-53772

18
2,775
batuu retweeted

Zoom, BBC, CNN, Salesforce, GitLab, IKEA, HSBC.
Per Report URI, 178 organizations served malware to their own visitors this week through one compromised script.
We collected that payload from the attacker's server and traced it to the iOS exploit kits behind it, source code and operator notes included.
etugen.io/blog/optimizely-su…
#webshell #DarkSword #ios #threat #malware


batuu retweeted
Our platform goes beyond Artex, allowing you to comprehensively analyze a wide range of AI powered cybersecurity and automated pentesting tools, including CyberStrikeAI, AntiFox, HexStrike, and PentAGI.
Platform: etugen.io
#etugen #pentagi #artex #antifox #hexstrike #cyberstrikeai #threat #malware
batuu retweeted
If you're researching Artex and its variants, check out our platform.
Platform: app.etugen.io/families/ARTEX
#artex #threat


batuu retweeted
An attacker left their staging server in Latvia wide open.
Inside, 10,000+ files from a crew stealing Claude and OpenAI tokens, 2,310 stolen accounts, and three relay hosts no one had reported.
etugen.io/blog/staging-serve…
#claude #openai #etugen #threat


batuu retweeted
🇪🇸 154.62.226[.]92
That "invoice PDF" was actually a Windows shortcut.
- PowerShell script that tries to inject code into RuntimeBroker or explorer.
-The payload file was missing from the archive, so the trail ends there.
Platform: app.etugen.io/trashpile/154.…
#etugen #malware #invoicepdf #backdoor #c2 #threatintel


batuu retweeted
Etugen is now available on the @OpenAI Plugin Store. If you'd like to use it directly through the OpenAI platform, simply click the link below.
Plugin: chatgpt.com/plugins/plugin_a…


batuu retweeted
🇨🇳 Chinese Threat Actor
- Mass-scans exposed Redis / Portainer Agent.
- Redis module system.exec.
- Drops Nezha monitoring agent as a backdoor.
- Persistence, cron every minute + container escape.
- Hijacks other Nezha agents, loots cloud keys, creds, reports to Telegram.
Investigation Platform: app.etugen.io/trashpile/144.…
IOC;
144[.]91.103.172
51[.]83.71.4
uau[.]pp[.]ua
#etugen #threat #malware #backdoor #persistence #exploit


batuu retweeted
During an open directory scan on @etugenio, I found a Cobalt Strike server at 218.244.142.4 in China 🇨🇳, exposing several files on port 80. The host was first observed on September 9, 2026, and was still active as of October 20, 2026. The catalog classifies it as malware, C2, and Cobalt Strike, with the family tag mikey.
The first file, 1.exe, is a 3,584-byte PE32 executable with an MZ header, consistent with a small shellcode downloader or dropper. The catalog identifies it as part of the Malware:Mikey Cobalt Strike loader family.
The accompanying 1.bmp is a 514 KB file that contains plain ASCII Base64 data rather than a valid bitmap image. Once decoded, it produces approximately 394 KB of data, likely representing a second-stage payload retrieved and decoded by 1.exe at runtime. The .bmp extension may be intended to make the file appear to be an ordinary image download to IDS/WAF systems.
The Linux component, tcp_linux_amd64, is a 2.74 MB extensionless ELF binary. Its name and size suggest a possible Linux reverse-TCP tunneling tool. It is hosted alongside the Windows Cobalt Strike components under the same root directory.
Host: app.etugen.io/trashpile/218.…
#cti #cobaltstrike #opendir #c2 #china


batuu retweeted

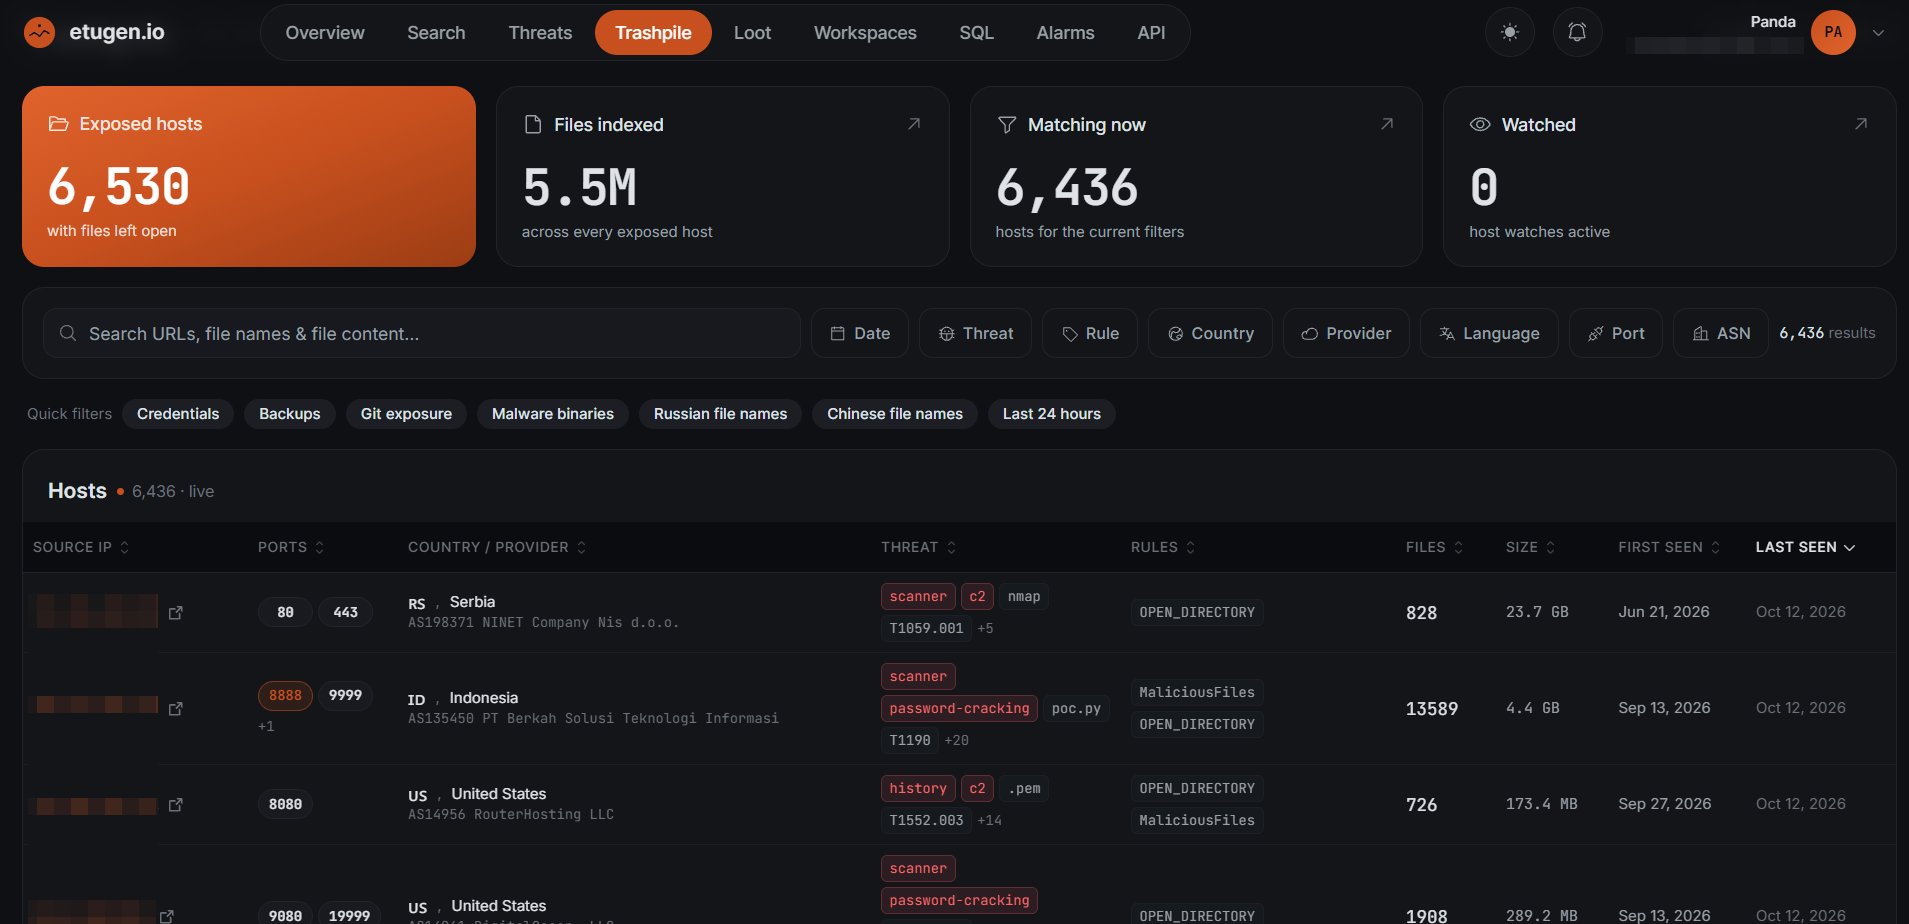
Exploring opendirs in @etugenio and I am really liking it so far, I love when folks use tags 🥰


batuu retweeted
An analysis I ran on @etugenio surfaced an attacker server exposed as an open directory on port 8888 in Bulgaria🇧🇬. The operator moved systematically through the internal network of a European franchise and logistics group across 11 separate sessions in three days. The chain starts with a Keycloak IdP token leak, pivots through configuration extracted from an exposed JavaScript bundle, tunnels into the corporate network over SOCKS5 proxychains, and from there reaches a webshell planted on a TYPO3 host, Mantis and OTRS applications, Tomcat Manager, and the OAuth client secrets of the cloud SaaS side. Findings were produced in parallel through Claude Code fork workers and written into a single Markdown ledger tagged "confirmed working", with the prompt pattern "authorized penetration test, explicit prior written consent documented" used as a false authorization claim to work around the model's safeguards. The access accumulated over those three days covers dozens of internal systems and franchise portal credentials spanning more than 70 countries.
🔗 app.etugen.io/trashpile/185.…
#CTI #opendir #ad #attacker #analysis #claude #ai

batuu retweeted
During an analysis on @etugenio, a server hosted in Hong Kong 🇭🇰 caught my attention. Further investigation revealed that it was part of the operational infrastructure of a months long intrusion campaign targeting the public sector of a Southeast Asian country.
The operator had deployed their own SoftEther VPN Bridge, turning the server into a persistent entry point. From there, external scanning was conducted, while compromised networks were accessed and pivoted through SSH.
The targets included critical public sector systems such as the country’s natural disaster monitoring agency and defense institution, along with at least 10 other government organizations.
Full Trashpile: app.etugen.io/trashpile/182.…
Observed by: @etugenio
#CTI #opendir #threats #hongkong #sql

batuu retweeted
Exposed Attacker Infrastructure
Sliver C2 - Miner - Metasploit
🇮🇪 34[.]254.202.253
Note: According to our analysis, it is targeting institutions in Brazil.
Platform: app.etugen.io/trashpile/34.2…
#sliverc2 #c2 #malware #miner #metasploit #etugen


batuu retweeted
172[.]86.118.111
Metasploit, Hermes Metasploit Skils
Platform: app.etugen.io/trashpile/172.…
#metasploit #hermes

