

Security enthusiast, hacker, and bug bounty hunter. Always on the lookout for vulnerabilities to fix and improve.
Bengaluru, India
Joined February 2017
- Tweets26
- Following291
- Followers281
- Likes329
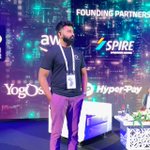
Able to attain 3rd rank🥉in world's biggest live hacking event at #gisec2022, Dubai by @YogoshaOfficial . Got a chance to socialize with 90+ top hackers from 30+ countries.
#gisecglobal #security #hacking #livehack #bugbounty #bugbountytips #gisec2022 #Yogosha


Indrajith retweeted

Hi hunters, check out our leaderboard for S1 2021 ! 👇
Congratulations to @vishwaraj101, @bugraeskici, @intruderhex, @llamaonsecurity, @hasanemrebeyy, @B_Z_Hash, @Kuromatae666, @Ch3n4p4N, M0N5T3R, @AdibouSec
And thanks to all of you for your great work and commitment 👏

Indrajith retweeted

Mobile Pentesting with FRIDA
#MobileSecurity @fridadotre
[SLIDES] by @lain7z and @martrudix
drive.google.com/file/d/1Jcc…

Indrajith retweeted
Hello hunters ! Check out our leaderboard for july & august 2019 👇@B_Z_Hash @intruderhex @YanZaX @ycam_asafety @Kuromatae666 @adrien_jeanneau @Michel_Gaschet @AdibouSec @mskl_bb @TaupinGeorges #bugbounty #leaderboard #incrowdwetrust

Indrajith retweeted

thank you to the whole community who proves to us every day that our action is necessary, special mention for those who participate in the amnesty program @YogoshaOfficial @hackinparis @sysdream @hack4values
Indrajith retweeted
Bypassing Certificate Pinning on iOS 12 with Frida
#MobileSecurity #iOSsecurity @fridadotre by @macho_reverser
medium.com/@macho_reverser/b…

Indrajith retweeted
Objection v1.6.5 – Keychain dumper improvements
#MobileSecurity #iOSsecurity @fridadotre by @leonjza
github.com/sensepost/objecti…

Indrajith retweeted
Hi hunters ! This month, our top 10 includes @ycam_asafety @intruderhex @TaupinGeorges @B_Z_Hash @MrB0LTv2 @NERVEUxxxx @mpgn_x64 @Mescal_Hzv & nj8. Congratulations to all researchers hunting on our platform, and keep doing a great job ! #incrowdwetrust


Indrajith retweeted

objection v1.6.0 is here! Lots of new stuff, including the ability to write plugins and inspection of live Java object instances.
Release notes: github.com/sensepost/objecti…
Sample plugin: gist.github.com/leonjza/7fcc…


Indrajith retweeted
fridump3 - a universal memory dumper using Frida for Python3
#MobileSecurity @fridadotre
github.com/rootbsd/fridump3

Indrajith retweeted
AndroidProjectCreator - Convert an APK to an Android Studio Project using multiple open-source decompilers
#MobileSecurity #AndroidSecurity
github.com/ThisIsLibra/Andro…

Indrajith retweeted
Hi hunters, I just released an article where I give some tips about report writing. Hope you will like it! #BugBountyTips 10degres.net/bugbounty-howto…
Indrajith retweeted

Finally we met @intruderhex !
So glad to have a chat with you and share a lovely meal and beer !
#NullconDasham @YogoshaOfficial

Indrajith retweeted
Setting up Frida without Jailbreak on devices running latest iOS 12.4
#MobileSecurity #iOSsecurity by @Din3zh
link.medium.com/9JLSUQV2zU

Indrajith retweeted

Did you know you can run @fridadotre on an iOS device and connect remotely (no more USB cable)?
$ ssh [email protected] 'killall frida-server && /usr/sbin/frida-server --listen=0.0.0.0 -D'
$ frida -H 192.168.44.210 Twitter
so convenient! ;) use it with frida, frida-trace &Co.


Indrajith retweeted

That is a nice one by @hahwul !
<html>
<head>
<meta charset="utf-8">
</head>
<script>
([,하,,,,훌]=[]+{},[한,글,페,이,,로,드,ㅋ,,,ㅎ]=[!!하]+!하+하.ㅁ)
[훌+=하+ㅎ+ㅋ+한+글+페+훌+한+하+글][훌](로+드+이+글+한+'(45)')()
</script>
</html>
Indrajith retweeted

A great writeup on Detecting and Exploiting mass-assignment #security #vulnerability in web apps by @padannewitz
dannewitz.ninja/posts/detect…
#infosec #redteam #bugbounty #pentest