







Today marks 40 years since Beastie Boys License to Ill was released. I remember being 10 years old and blown away by it. Still am... #beastieboys #licensetoill
19
If one router can bring down all FAA air traffic I am taking road trips exclusively for a while.
1
55
Jascha retweeted

New on cve.bz:
• GitHub PoC repos listed per CVE (unverified, clearly labeled)
• Drupal, Swift & GitHub Actions advisories
• Check your stack now reads composer.lock & Package.resolved
cve.bz/cve/insights

Jascha retweeted

We have released v2.0 of Symbiont!
Symbiont is our open-source, Rust-based runtime for AI agents that run under policy. 2.0 is a major release. It tightens the boundary between what a model asks for and what actually runs.
Site and GitHub: symbiont.dev


PSA avoid @Hostinger, they host malware and typo squatting then when report to abuse email they reply that not enough evidence. Since sending them the domain and virtustotal is not enough to them. If scammer be sure to use them will not stop you.
1
122
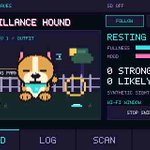
#SurveillanceHound is a ESP32 virtual pet that sniffs WiFi and BLE for things like Flock/Axon/Ring cameras, Airtags (other types), iBeacons, Flippers, WiFi Pineapples, Meta Glasses, DeAuth and more. SH eats them and effects fullness and mood.
surveillancehound.dx.pe

1
62
I have updated #Meshtripwire to work with Lilygo LTE boards to use IoT LTE for sensors. Also use #meshtastic #meshcore #reticulum as back hauls for sensors.
github.com/OutandBack/meshtr…

1
2
92
Jascha retweeted

Starting September 14, we're permanently raising standard weekly limits in Claude Code by 25% for Pro, Max, Team, and seat-based Enterprise plans. Until then, the current 50% increase will be in place.
Readers added context they thought people might want to know
While standard base limits are increasing by 25%, this change represents a net 17% reduction in weekly limits compared to the active 50% promotional limits users currently experience, as confirmed by the official Claude account: x.com/claudedevs/sta…
Jascha retweeted
rns-signal-gateway: Reticulum <-> Signal Gateway, Bidirectional bridge between Reticulum (LXMF) and Signal supports images/files and voice memos
github.com/jaschadub/rns-sig…

Anthropic has validated what we've been working on for 2 years with their Zero Trust eBook for AI Agents. @ThirdKeyAI and the OpenAgentTrustStack.org even fill in the gaps.

Google announced that all Android app developers must register centrally, pay a fee, and submit government ID, or their apps will be blocked on every device. over 67 organizations oppose this. keepandroidopen.org @AlteredDeal #KeepAndroidOpen
60
VectorSmuggle is on HNS. Steganographic exfiltration via vector embeddings, plus a cryptographic defense (VectorPin).
helpnetsecurity.com/2026/05/…

Small-angle orthogonal rotation hides arbitrary payload in embeddings, undetected by off-the-shelf statistical defenses across every model-corpus pair we tested.
arXiv: arxiv.org/abs/2605.13764

RAG security today is roughly where cloud storage was before people realized S3 buckets were public.
27
Added a visual explainer for VectorSmuggle: Steganographic exfiltration in embedding stores
vectorsmuggle.org

1
42
I published a new security preprint:
VectorSmuggle: Steganographic Exfiltration in Embedding Stores and a Cryptographic Provenance Defense
The paper looks at an integrity gap in RAG infrastructure: embeddings are usually treated as opaque numerical artifacts, but vector stores generally lack native/default controls for embedding integrity or provenance.
The finding is nuanced: simple anomaly detectors catch many crude perturbations, but small-angle orthogonal rotation exposes a harder class of embedding tampering. Statistical detection helps, but it should not be the load-bearing control.
I propose VectorPin: a minimal cryptographic provenance protocol that signs a canonical commitment over the source, model, and vector bytes. If the vector is modified after pinning, verification fails.
Paper:
doi.org/10.5281/zenodo.20058…
vectorpin.org
Codebase with Jupyter demos:
github.com/jaschadub/VectorS…

1
22
New paper on how Symbiont uses the ORGA loop to secure agents.
"Typestate-Enforced Agent Loops: Making Policy Gates Unskippable at Compile Time"
doi.org/10.5281/zenodo.19746…