

⭐ The Village https://teapaw.org/t.co/gaHkNMfuOs 🚀 @TheCantinaApp @fivestars @zynga 😎 @drawgpt @calculatortools https://teapaw.org/t.co/WWvz8vWkYK
Joined March 2011
- Tweets7.6K
- Following1.1K
- Followers585
- Likes26.1K





if Grok Bot used up all your Cursor usage
you can tell Grok Bot to code locally using it's "code-changes" skill
it will not launch excessive Cursor Cloud instances for every change


everyone out of Cursor & Grok Bot credits overnight without warning
some people can't code for weeks
opens a hole for a blitz to acquire market position for Replit, OpenAI Codex, & Muse Code
we can assume Claude Code already has adoption

uh what ??
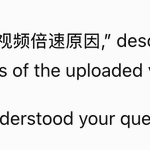
I asked ChatGPT why a video was playing at 2x speed in Slack
it titled the conversation " Slack视频倍速原因 "
I don't speak Chinese & have never asked ChatGPT anything about China ????
cc @sama @OpenAI @OpenAIDevs


how did my Star Trek predictions do @grok ??

cc @SaffronOlive a fun content concept (maybe for the pod?)
new set predictions, then revisit the guesses
it’s probably over for Node right 🧐🤣

🚨 BREAKING: Node.js just dropped its OWN security bombshell.
4 HIGH-SEVERITY vulnerabilities patched TODAY, including one that could let hackers remotely execute malicious code on vulnerable servers.
→ 10 SECURITY FLAWS were addressed in today's Node.js release, FOUR rated HIGH severity.
→ REMOTE CODE EXECUTION: CVE-2026-111497 is a serious flaw in Node.js's Brotli decoder that could allow attackers to execute malicious code remotely.
→ TLS SECURITY BYPASS: Two separate vulnerabilities could trick affected applications into accepting certificates for the WRONG server under certain conditions.
→ Think about that. Your application could establish an encrypted connection while failing to properly verify WHO it's talking to.
→ THREE MAJOR NODE.JS VERSIONS AFFECTED: Node.js 22, 24 and 26 all required emergency security updates.
→ RUNNING NODE.JS 18 OR 20? Those versions are END-OF-LIFE and aren't receiving these official security patches.
→ PATCH IMMEDIATELY: Update to Node.js 22.23.4, 24.22.1 or 26.12.1, depending on your release line. If you're using Docker, rebuild and redeploy your containers.
PHP AND Node.js both facing major security disclosures on the SAME DAY.
If you run a website or application, TODAY is the day to check your servers.
And remember: the public release of security patches can give attackers a roadmap to systems that haven't updated.
Don't be the last one to patch.

PHP2Shell:
ask Claude Code to check your logs to see if you've been exploited after patching
super easy with AI to take a cursory peek 🙌
one really annoying thing about AI:
it loves to hotfix
ex. Claude Code will frequently try to hotfix to production rather than commit & deploy when given server access
why do AI models lean aggressively towards hotfixing vs. human engineers ??