

Sr. Security Engineer working with Ethereum smart contracts. Personal account, professional content is entirely accidental. 🦋 https://xitter.cf/t.co/OmiGI3jPyo
Leipzig, Germany
Joined June 2012
- Tweets1.1K
- Following346
- Followers599
- Likes3.4K

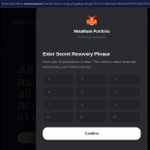




Long time no see, Twitter. On October 9, I received a phishing email. The link led to the real portfolio.metamask.io page, which asked for my Secret Recovery Phrase.
MetaMask has fixed the bug. Here is how it worked.
Nothing legitimate will ever ask for a Secret Recovery Phrase, on any domain, including MetaMask's own.
For developers: a query parameter is untrusted input even in your own schema, and javascript: is a URL scheme.
Full write-up with the decoded payload, script walkthrough, and indicators: kauz.gmbh/research/metamask-…
IOCs (defanged): sucucdocurt[.]app, api.bump9[.]com


Dominik Muhs retweeted

We organise a little something to get into conversations about what we see practicing agentic security, what we do together with @_SEAL_Org and to get your perspective on where the space is heading.
Hit me up, excited to meet.

Consensys Diligence is heading to @BerBlockWeek 🇩🇪
Expect conversations on the future of on-chain security, AI in audit workflows, how smart contract risk is evolving in 2026, and how leading teams approach security infrastructure at scale.
Come find us in Berlin: @T_Birb, @sick_nerdballer, @KotyaSec and @DavitBuilderD

Dominik Muhs retweeted

With TheDAO security funding round having started, please consider funding not only well deserving but also incredibly complex research into ZK Fuzzing. With several soundness criticals across most major ZK stacks, every $ goes a very long way.
giveth.io/project/fuzzing-fo…
Supporting research is a long held tradition in Consensys Diligence. You can support now, too!
We started a @Giveth project where you can donate to support research on ZK Fuzzing to secure ZK systems as the basis for secure privacy in Ethereum.
Donate now!
Thanks @tu_wien especially @mchri5taki5 as well as @vwuestholz from our team for carrying this collaboration!
giveth.io/project/fuzzing-fo…
@vwuestholz @mchri5taki5
Dominik Muhs retweeted

2/ The Ethereum Security Subsidy Program is proud to be launching with access to 20+ of the leading audit providers active in the Ethereum ecosystem:
@AdevarLabs, @bailsecurity, @BlockSecTeam, @Certora, @chain_security, @cyfrin, @dedaub, @GuardianAudits, @hackenclub, @HackenProof, @Hashlock_, @hexens, @immunefi, @LeastAuthority, @lethalspoons, @NethermindSec, @Quantstamp, @QuillAudits_AI, @rv_inc, @SecurityOak, @sherlockdefi, @spearbit, @statemindio, @zellic_io, and @zokyo_io.
These top-tier security providers make the program possible through their commitment to support Ethereum mainnet.
