Abogada TI, millennial, entusiasta del k-drama. Zurda (left handed) y de la otra zurda también.
Valle del Elqui, Chile.
Joined February 2026
- Tweets2.7K
- Following115
- Followers45
- Likes2.2K



María José 🫰🏻 retweeted

🔴🇨🇱Fintech Khipu reporta ciberataque y pide a comercios cambiar claves. #Ciberseguridad
#Chile
#ciberataque
latercera.com/pulso/noticia/…

La pregunta es: ¿La instalación física de los data centers en Chile nos va a permitir a las empresas a acceder a precios más convenientes de almacenamiento en nube de esos centros? ¿Vamos a poder contar con esos servers? O nos van a seguir cobrando lo mismo y mandando a indonesia

El gobierno de Chile busca transformar al país en un "hub" de datacenters. En Miami, la ministra de Energía de Chile, Ximena Rincón, destaca que la inversión en el país está ocurriendo "de manera acelerada".
1
50
María José 🫰🏻 retweeted

🔴 Crisis en el Ministerio de Ciencia: Renuncia subsecretaria Carolina Rossi tras disputa con Ximena Lincolao
chilevision.cl/noticias/naci…

María José 🫰🏻 retweeted

🔴#AlertaLT | Carolina Rossi renuncia a la Subsecretaría de Ciencia en medio de polémica con ministra Lincolao latercera.com/nacional/notic…


María José 🫰🏻 retweeted

⚠️ 🇨🇱 🏥 🩻 🗄️ PREVENTIVE ALERT – ALLEGED DATA BREACH INVOLVING MEDICAL RECORDS AND RADIOGRAPHS AT CODESUD (CHILE)
[STATUS: ALLEGED / UNCONFIRMED / GROUP: RSA CRACKERS / REPORT DATE: NOVEMBER 19, 2026]
Centralized cyber-intelligence systems have intercepted a disclosure posted on clandestine channels on November 19, 2026) and attributed to the group RSA CRACKERS. The report claims the compromise of a Picture Archiving and Communication System (PACS)—a medical imaging management system—linked to the domain "codesud.cl" in Chile. The group asserts that it has full access to stored radiographs and has released partial samples, accompanied by a message critical of corporate security practices and the National Cybersecurity Agency (ANCI).
The screenshots provided by the operators show a web-based interface for accessing radiological studies (PACS), containing patient lists (including full names, dates of birth, national identification numbers/RUT, study dates, imaging modalities, and anatomical details), as well as a medical viewer displaying diagnostic images.
It is strictly noted that the veracity of this intrusion, the actual exposure of the medical servers, and the overall authenticity of the clinical records have not been officially confirmed by the affected entity or by Chilean health and cybersecurity authorities.
Responsible Actor/Group: RSA CRACKERS.
Victim: (Diagnostic platform / PACS system) — 🇨🇱 Chile.
Sector: 🏥 Healthcare, Diagnostic Imaging, Radiology, and Sensitive Clinical Data (PHI/PII). Publication Date: November 19, 2026.
Nature of the Incident: Alleged intrusion into a PACS viewer/server, resulting in the exposure of patients' personal and medical information, accompanied by the limited dissemination of diagnostic samples.
🔍 TECHNICAL BREAKDOWN OF THE INFORMATION (ALLEGED)
Patient Identification and Demographic Data: Full names, dates of birth, and national identification numbers (Patient ID / RUT).
Metadata and Diagnostic Images (PACS/DICOM): Dates and times of examinations, exam IDs, modality (CR - Computed Radiography), anatomical description of the study (chest, extremities, spine, pelvis, skull, shoulder), and radiographic views as seen in a clinical viewer.
🖥️ CENTRALIZED THREAT MONITORING SYSTEM
Intelligence System: analyzer.vecert.io
Quickly verify your security at: monitor.vecert.io
Quotes and services: vecert.io/contact
#Chile #Codesud #HealthcareLeak #MedicalData #PACS #RSACRACKERS #DataLeak #DataBreach #BreachAlert #DarkWeb #Hacking #ThreatIntel #ThreatIntelligence #InfoSec #CyberAlert #VECERT #SOC #CSIRT #Unconfirmed #SecurityAlert #CyberDefense #CyberRisk

María José 🫰🏻 retweeted
⚠️ 🇨🇱 🏛️ 🪪 🔮 PREVENTIVE ALERT – FUTURE ATTACK AGAINST THE CHILEAN CIVIL REGISTRY AND IDENTIFICATION SERVICE
[STATUS: POTENTIAL FUTURE ATTACK / UNCONFIRMED / CHANNEL: STARS / REPORT DATE: NOVEMBER 19, 2026]
Centralized cyber-intelligence systems have intercepted a warning post—or a preventive signal—on the "Stars" channel. The image displays the institutional emblem and official logo of the Civil Registry and Identification Service (Ministry of Justice and Human Rights — Government of Chile).
Within the context of clandestine or messaging channels—where announcements regarding operations and data leaks often circulate—such messages typically serve as a prior warning, a target designation, or preparation for a campaign (such as an intrusion, data exfiltration, website defacement, or a DDoS attack). To date, no evidence of a compromise or leaked material has been published.
It is strictly noted that the execution of an attack, the actual compromise of the Chilean Civil Registry’s systems, and the true scope of any potential threat have not been officially confirmed by the agency or the relevant authorities.
#Chile #CivilRegistry #PotentialAttack #EarlyWarning #GovernmentAlert #DataLeak #DataBreach #BreachAlert #DarkWeb #Hacking #ThreatIntel #ThreatIntelligence #InfoSec #CyberAlert #VECERT #SOC #CSIRT #Unconfirmed #SecurityAlert #CyberDefense #CyberRisk

La campaña del Minsal fue un fracaso para desincentivar el consumo de tabaco, pero un éxito para el debate sobre el uso de la IA, sus costos económicos y laborales, y para debatir sobre el adecuado uso de los recursos públicos.

¿Pa’ qué fumas, si el cigarro aumenta el riesgo de sufrir un infarto y en Chile provoca 52 muertes cada día?
Hay muchas canciones que se quedan pegadas, pero ninguna adicción debería quedarse contigo.
La única adicción que queremos para tu vida es esta canción. 🎶
#PaQuéFumas #EligeNoFumar
María José 🫰🏻 retweeted

We are deeply sorry for the disruption this incident has caused our customers and partners. We know the trust they place in our services and take that responsibility extremely seriously. We are seeing broad recovery and stability across our services.
This was a technical issue not related to cyber or AI / agents. The incident was introduced by an issue during an earlier network capacity upgrade that surfaced following a recent network change. We have addressed the underlying issue and continue to restore service to remaining customers and regions.
Given the scale of demand, we restored services gradually, validating stability at each stage. While this took longer, it helped ensure a stable restoration.
We will provide a full post-incident report once our review is complete.
Enterándome que en Japón desempolvaron los fax para seguir trabajando sin Microsoft. Gen Z con ataque.
147

Nuestra pyme tech es anti Microsoft. La regla general es Linux, por excepción un Mac y la arquitectura es Google. Para ofimática usamos Libre Office. Así que ni por si acaso nos llega el chaparrón. Ah!, pero nuestros clientes... 😅
1
2
131

Microsoft lleva caído un día entero y ¿cómo es que no hay saqueos ni barricadas en las calles? De hecho hay hasta escasa cobertura noticiosa.
¿Siquiera han hecho el cálculo de cuánto es la pérdida económica que provoca este black out?
132
Prácticamente todo el día caído Microsoft en sus distintas plataformas y en el @CSIRTGob ¿están durmiendo o qué? @ANCIChile Por último un reporte, algo poco. Así como para que digan que están trabajando.
122
María José 🫰🏻 retweeted

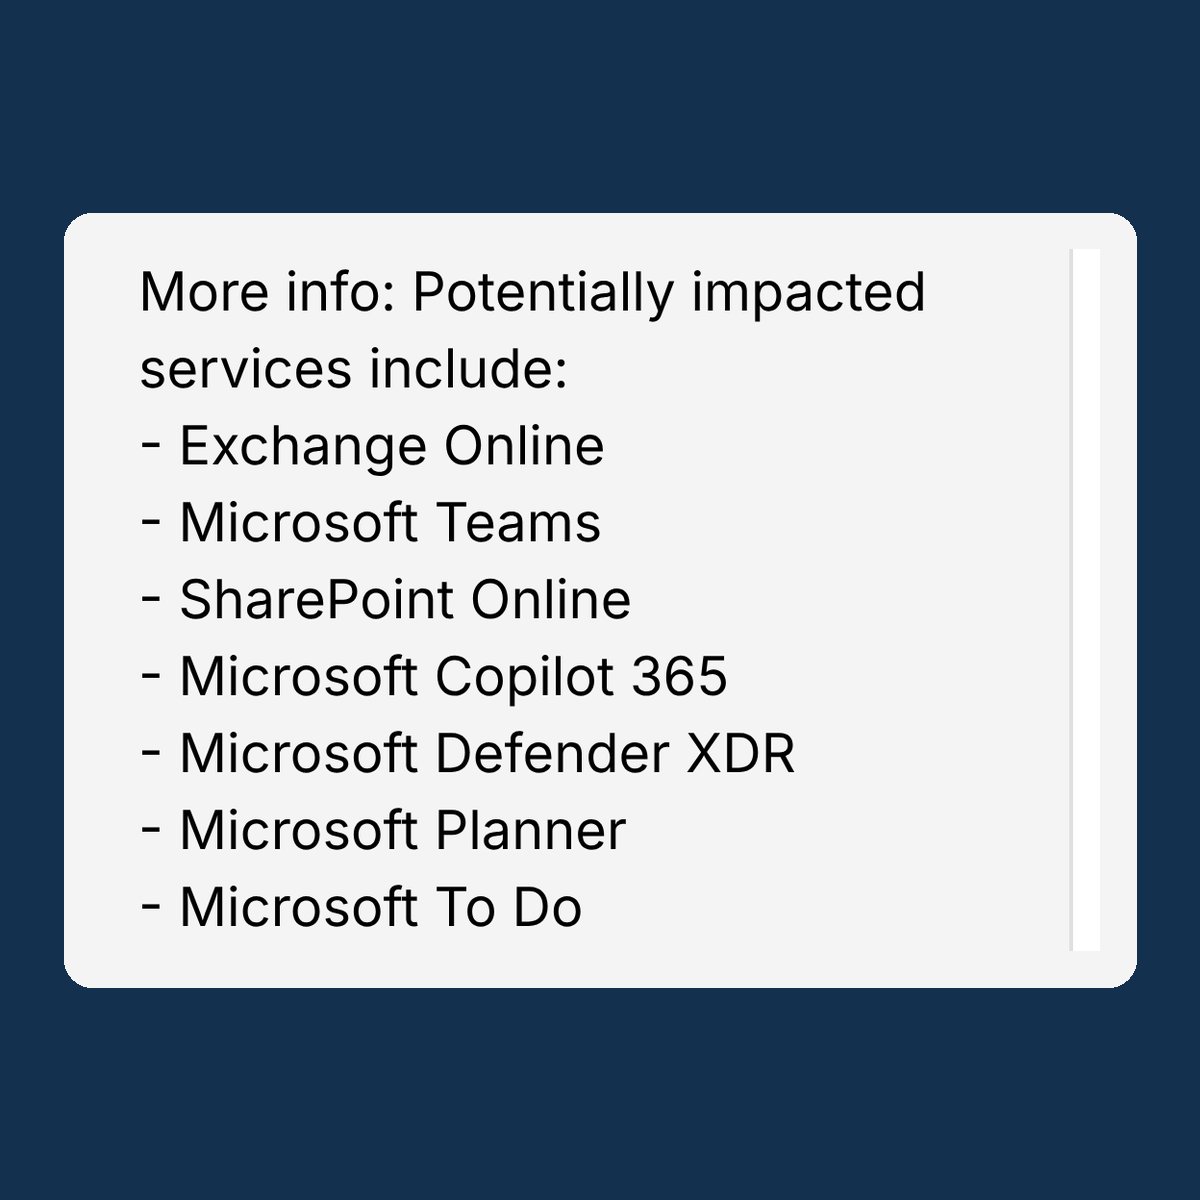
‼️ UPDATE: Microsoft's outage now reaches far beyond Outlook. Teams, SharePoint, Copilot and even its Defender XDR security platform are hit.
Consumers can't reach their OneDrive storage or Office on the web either, TechCrunch reports.
Microsoft first blamed elevated load. Now it says a large number of its servers became unexpectedly unavailable, dumping their load onto the rest. It hasn't said why.
It is restarting the servers with a fix in place, investigating why they show high processor use, and has paused all deployments.