

Freelance journalist. Former Nairobi, Kampala, Beirut, Beijing and Brussels. Now back in Europe. https://xitter.cf/t.co/xAvd9VutO0.
Joined April 2009
- Tweets19.3K
- Following448
- Followers1.8K
- Likes14.1K


Right. Independence through Google …lol

Scoop 🔴 German Federal intelligence services are about to establish their first "intelligence cloud", enabling them to share secret information much quicker. According to our information this system will be bases on an air-gapped version of #Google Cloud: tagesschau.de/investigativ/n…

marc hofer retweeted

They already took down most of the infra before release, now they killed the left over rather quickly. You have to hand it to them, Chinese authorities are reading our blog...


marc hofer retweeted

New: I got a tip a little while ago about a shadowy Pentagon entity called "TSO" with a lot of money and a desire for offensive hacking tools.
Turns out TSO is a new DoD agency. And it does a lot more than hacking.
w/@JackDetsch and @paulmcleary
politico.com/news/2026/10/22…

marc hofer retweeted

If for any reason there are problems accessing Joshua Michael's Flock camera map, Proton is hosting a copy.
proton.me/flock-camera-map

Wait, a while ago all the pundits and many China-watchers assured the world that the times of this shenanigans are over as Beijing and Delhi are now having a direct line of communication or something along the line.


marc hofer retweeted
Yahoo is still blocking emails from our newly assigned IP space. We've continued using it and aren't going to stop because Yahoo won't accept mails from it. It already has a great reputation elsewhere and there are 0 issues with anything else blocking it.
xitter.cf/GrapheneOS/status/2111…

Yahoo is still blocking emails from our newly assigned IPv4 space (206.220.120.0/22). It's likely they're behind on updating their database of allocated IP space. It was already published via arin.net/resources/guide/ipv… and other providers have been accepting it for 2 weeks already.

marc hofer retweeted
A recent internal report by the company 北京华崮科技有限公司 (Beijing Huagu Technology) about the Chinese IT investment landscape lays bare its chaotic and unstructured nature. Spiraling costs, lack of standardization of project-spending-estimation and quickly changing requirements are a real challenge for many medium size companies. Resulting in a high turnover in the industry. 1/2


marc hofer retweeted

New: Chinese hackers broke into Staples. Staples has an internal customer support tool called Nexus, Chinese hackers got into that, issued millions of dollars of gift cards. Mules then went on a spending spree across the U.S. Gang made $100 million+ 404media.co/how-a-massive-ch…


marc hofer retweeted
A four-hour documentary about Elon Musk continues to meet resistance from social media platforms.
spr.ly/6015BHOqFP

marc hofer retweeted

Investors/board members/ceos are taking a giant leap of faith to think they can rely on future PRC open AI models going forward. Those with fiduciary duties will need a rethink

The Mofcom explainer of the revised export control rules. sinocism.notion.site/MOFCOM-… risks of building a business on PRC open AI models going up. “facilitation measures such as automatic licensing may apply if they are deployed in relatively controllable-risk circumstances, such as on a company’s own cloud infrastructure overseas 如果部署在海外自有云等风险相对可控的情形下,可适用自动许可等便利措施”


marc hofer retweeted

Seen these ads for Akedo, an AliExpress “Sale”, or MyIPInfo? They’re being run en masse by an Israeli ads company called Discover-Tech as part of an espionage scheme we call AdFection, and they have the potential to infect you with spyware when (or even before) you see them


marc hofer retweeted

NEW: 🇳🇴 Chinese-owned rental cars used by the Norwegian Armed Forces reportedly recorded soldiers, their movements and security codes during a major military exercise in Oslo, raising serious questions about the security of vehicles used in sensitive military operations.
The incident occurred during Operation Hovedstad, held from September 14 to 18, when Norway’s Home Guard District 02 trained for security operations, including scenarios involving the defence of Oslo Airport during wartime.
The Armed Forces had rented the cars through Hertz Norway under a nationwide rental agreement signed in 2024, worth up to 350 million Norwegian kroner and running until May 2028. Hertz Norway’s ownership chain ultimately leads to China’s Zhejiang Geely Holding Group, which also owns Volvo Cars. The agreement provides rental vehicles for exercises, operational activities and everyday military use.
During the exercise, soldiers discovered that the cars had recorded and stored video footage. Lieutenant Fredrik Blanck told Norwegian newspaper Dagens Næringsliv (DN) that the recordings showed who entered and exited the vehicles, where they travelled, whom they picked up and how long they remained at different locations.
More concerningly, the footage reportedly captured security codes entered by soldiers when opening military gates. Some access points require both a key card and a code, meaning the recordings could expose sensitive access procedures.
The vehicles remained in use throughout the exercise because alternative transport was in limited supply.

marc hofer retweeted
.@EmilyZFeng: “The Uyghur fighters rode into Damascus on tanks and armored vehicles, waving their guns and light blue East Turkestan nationalist flags…All of them were thinking of home. ‘I thought, if only it were Hotan, or Aksu, or Urumqi.’”
chinabooksreview.com/2026/10…

marc hofer retweeted

The CyberStrikeAI and ARTEX combination by Chinese-speaking offensive actors is an interesting trend we’re following closely 👇

INTEL DROP
AI-native offensive tooling is stacking on single hosts. Total Insights Feed detection pipeline currently sees 1,989 IPs running an AI pentest framework, and 48 of them run two or more. Many share IPs with classic C2, stolen AI API relays, and exposed gen-AI apps. A sample of 8, in the US, China, Hong Kong, Singapore, and Iran:
192.236.166.73 cyberstrikeai + artex + mythic + scopesentry + ai-relay:grok2api
192.253.229.113 cyberstrikeai + artex + pentagi + xingrin
149.104.24.91 cyberstrikeai + artex + arl + ai-relay:sub2api
151.243.126.22 cyberstrikeai + sliver + gen-ai:n8n + gen-ai:openclaw + ai-relay:new-api
103.101.176.236 cyberstrikeai + pentagi + malware-hosting + open-dir
64.20.61.134 pentagi + ai-relay:sub2api + ai-relay:grok2api + open-dir
1.14.104.208 pentagi + adaptixc2 + cobaltstrike
119.45.122.90 deepaudit + gen-ai:ollama + gen-ai:open-webui + gen-ai:openclaw + scanner
Several also expose a Known-Exploited-Vulnerability service (kev-vulnerable) on the same host that runs the attack tooling.
Happy hunting!
#TotalInsights #ThreatIntel #AI #OffensiveSecurity #CyberStrikeAI
team-cymru.com/total-insight…

marc hofer retweeted

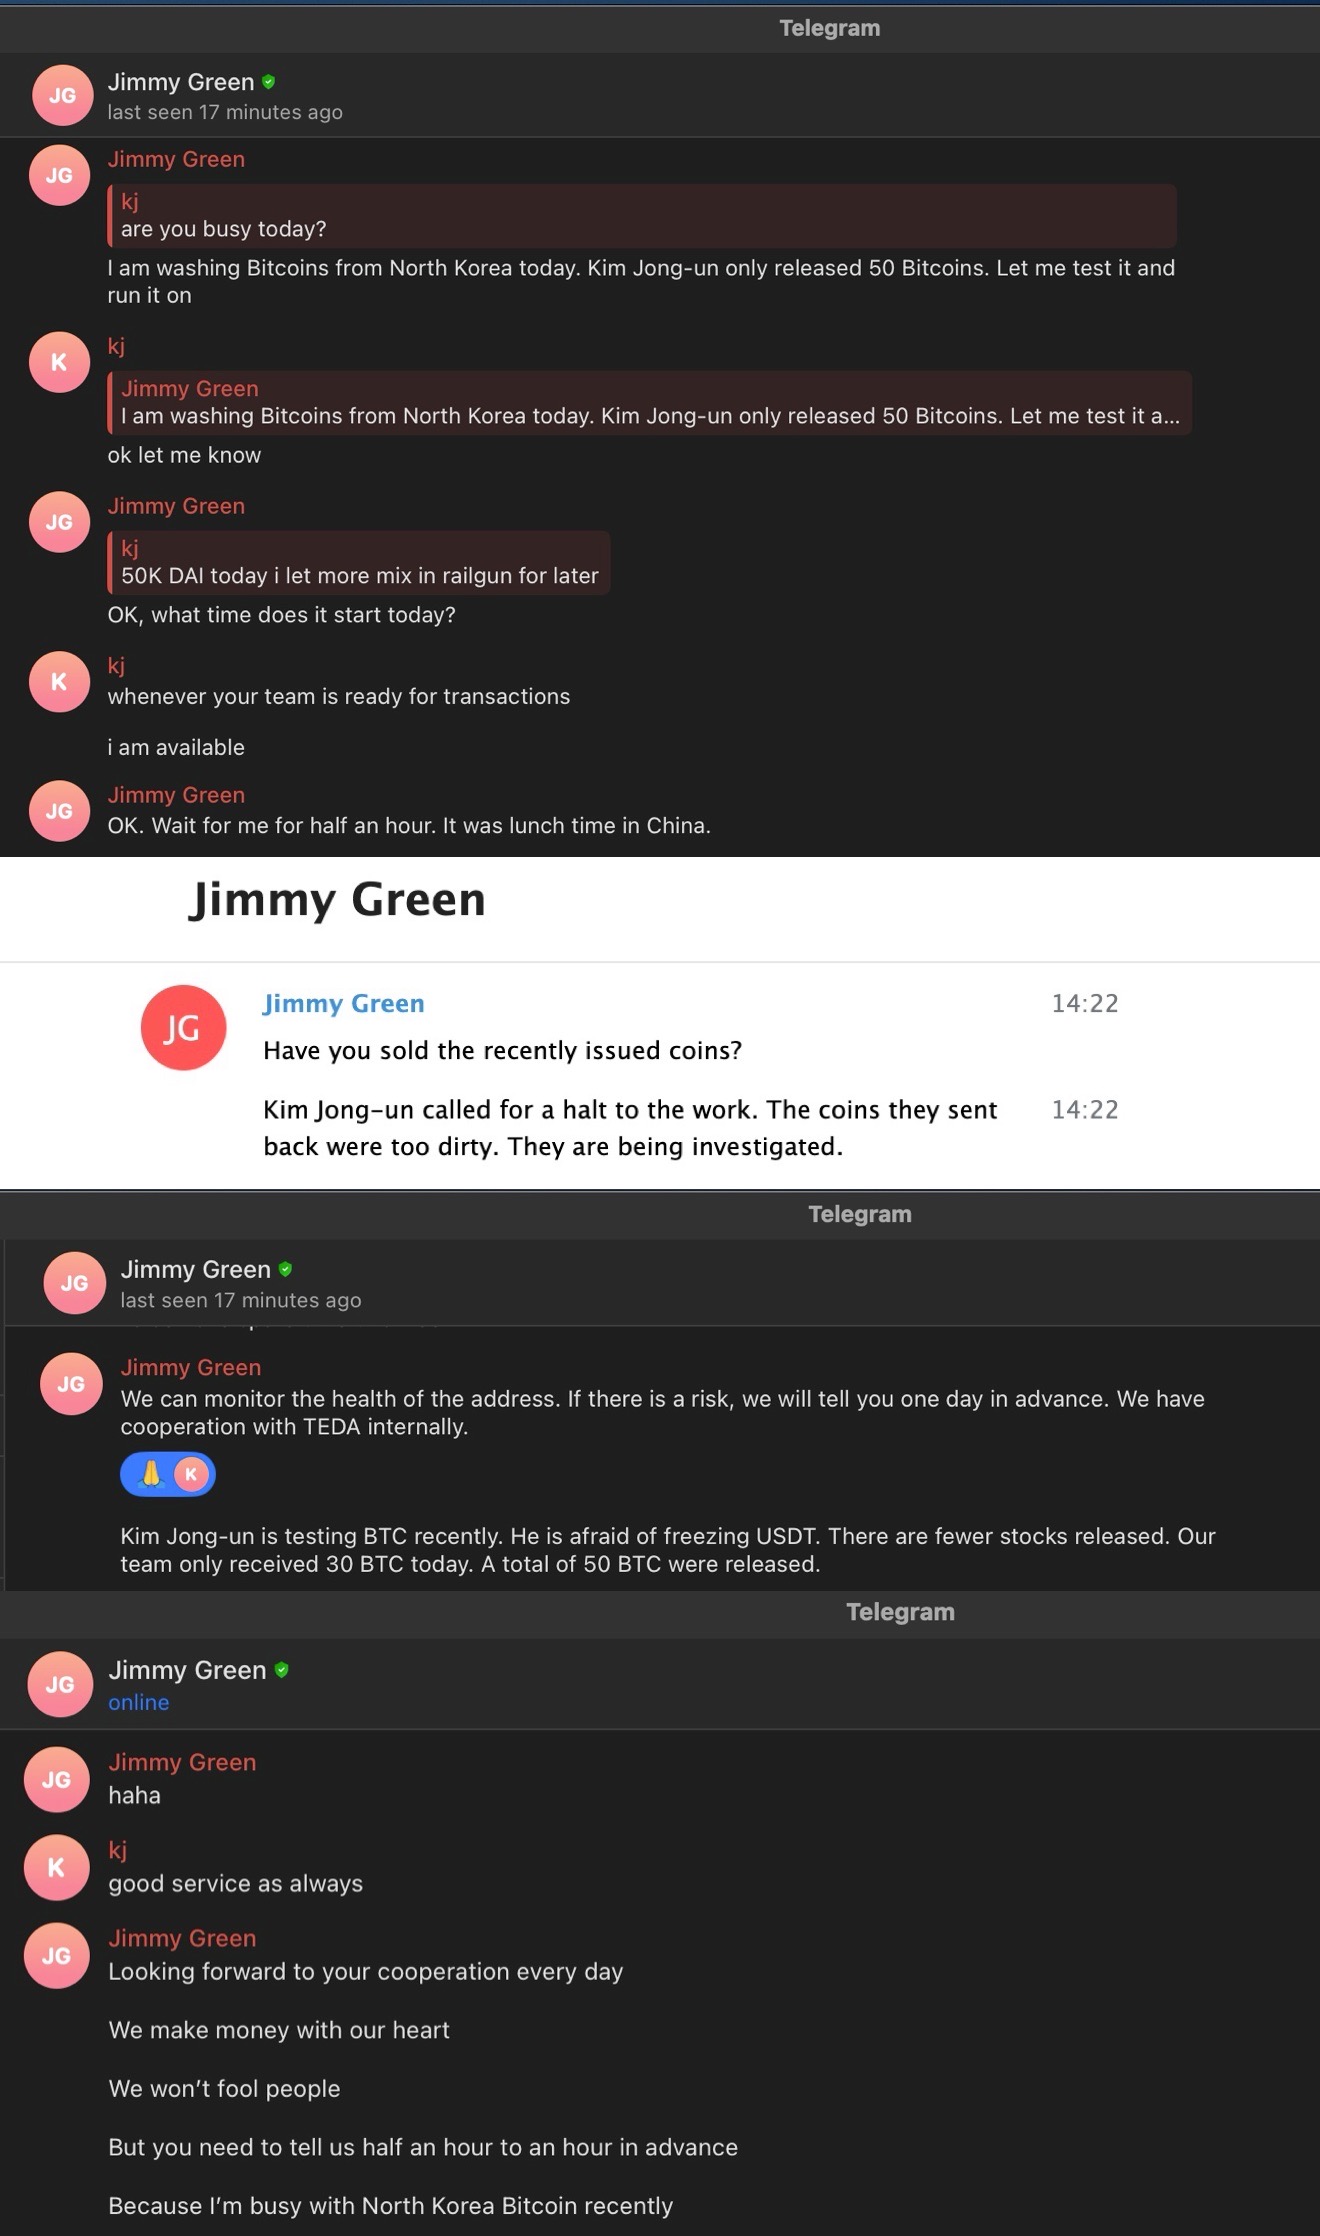
1/ How I infiltrated a Chinese organized crime syndicate that has laundered $1B+ across multiple exploits for Lazarus Group.
Posing as a client, I gathered intel that helped action freezes for the Feb 2025 Bybit exploit and attribute illicit activity onchain.

marc hofer retweeted
Hackers used a Chinese AI agent to attack South Korea’s biggest banks—one of the first such AI-powered intrusions into the global financial system on.wsj.com/4i5VwGg
