

Open Source enthusiast, building Web3 future, prev Co-founder @NetworkSubspace, prev Lead Software Engineer @Restreamio
Galt's Gulch
Joined February 2012
- Tweets2.8K
- Following47
- Followers475
- Likes572



Pinned Tweet
Finally published a bunch of stuff for general use.
Most likely the fastest Rust Merkle Tree implementation on crates.io, RISC-V interpreter, BLAKE3 hash functions that work in const fn and more.
abundance.build/blog/2026-03…

Nazar Mokrynskyi retweeted
I find it bizarre that so many open-source projects have posted policies against AI-assisted contributions.
This will not last, because they'll be outcompeted by projects not afraid to use power tools to debug the code and and features. In crucial cases, AI-hostile projects will be forked to remove that restriction.
How can anybody not see this coming?
This dynamic is so obvious - and anti-AI rules so patently futile and doomed - that I have to conclude there is something like a religious frenzy going on.
I'm going to bend over backwards to be fair about this. There was a point earlier in the development of AI at which such restrictions might have made temporary sense, because model outputs were prone to enough noise and hallucination to be a net drag on productivity.
We're long past that now. And the obvious solution to merge-request queues flooded with AI-generated slop is to use AI to filter them so exercising human judgment on the remainder remains practical.
I'm not going to argue rights and wrongs here. One might just as well argue that it's wrong for sandcastles to collapse when the tide comes in.
The religious frenzy does bother me, though. Maybe less than it did 5 minutes ago when the mind infection was "wokeness", but a mob of crazies is never an edifying or reassuring sight.
I guess the most positive thing I can observe is that this phase of nuttery won't last long, because it can't. The selective pressure against it is too brutal.
It does leave me wondering what cause the nutters will attach themselves to next. Alas.
ubuntu.com/security/CVE-2026…
A week since publication: still no official fixed kernel, no recommended workarounds documented on the page either.
"CVSS 3 Severity Score: 9.8 Critical" my ass.
I appreciate there are probably reasons for it, but this is not confidence-inspiring.

126
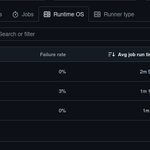
It is wild how inconsistent x86-64 runners are on GitHub Actions. I now run a bunch of things through cross-compilation on their Aarch64 runners instead.
One x86-64 run it is 16 min, another 28 min. On Aarch64 it is 21-23 minutes every time, way smaller spread.
1
50
No RSS feed with security updated, no way to update such things in the UI (I see other updates like TLS certificate roots were actually available as well, which I would not have found otherwise) is a very bad experience...
7
Critical holes in Linux networking stack, then anyone able to issue TLS certificates for any domain, another critical hole in PHP.
I keep finding security updates to install across machines multiple times a day.
Turns out security was an illusion all along, wasn't it?..
2
199
Be careful what you wish for I guess 🤯

I asked Kimi to enable ipv6 in the background as I was doing something else.
Turns out it was not enabled on my router so, not having the admin password, it naturally then found the firmware online, decrypted it, extracted the lua bytecode, found out the opcodes were shuffled, updated the decompiler to work with it and found a stack-overflow in a binary it launched to get access.
Still didn't succeed though, since it figured attempting to trigger it would be ""crashing = disruption"" 😭


2
69
Nazar Mokrynskyi retweeted
This is the doom I predicted a few days ago, coming for Photoshop. A clean-room open-source reimplementation.
No prizes for guessing that they decompiled Photoshop to source code, processed that to some kind of non-code specification language, then fed the spec to an LLM with an instruction to generate Rust.
Adobe just got nuked. And closed source is dead, dead, dead.
github.com/storytold/photocr…
