

cipher security labs https://teapaw.org/t.co/IZByfO2Dr4
🇪🇺🇮🇱
Joined October 2016
- Tweets8.5K
- Following698
- Followers1.1K
- Likes4.1K




Nir Yehoshua retweeted

heard in Silicon Valley:
Security researchers will soon make more than AI researchers.
Nir Yehoshua retweeted

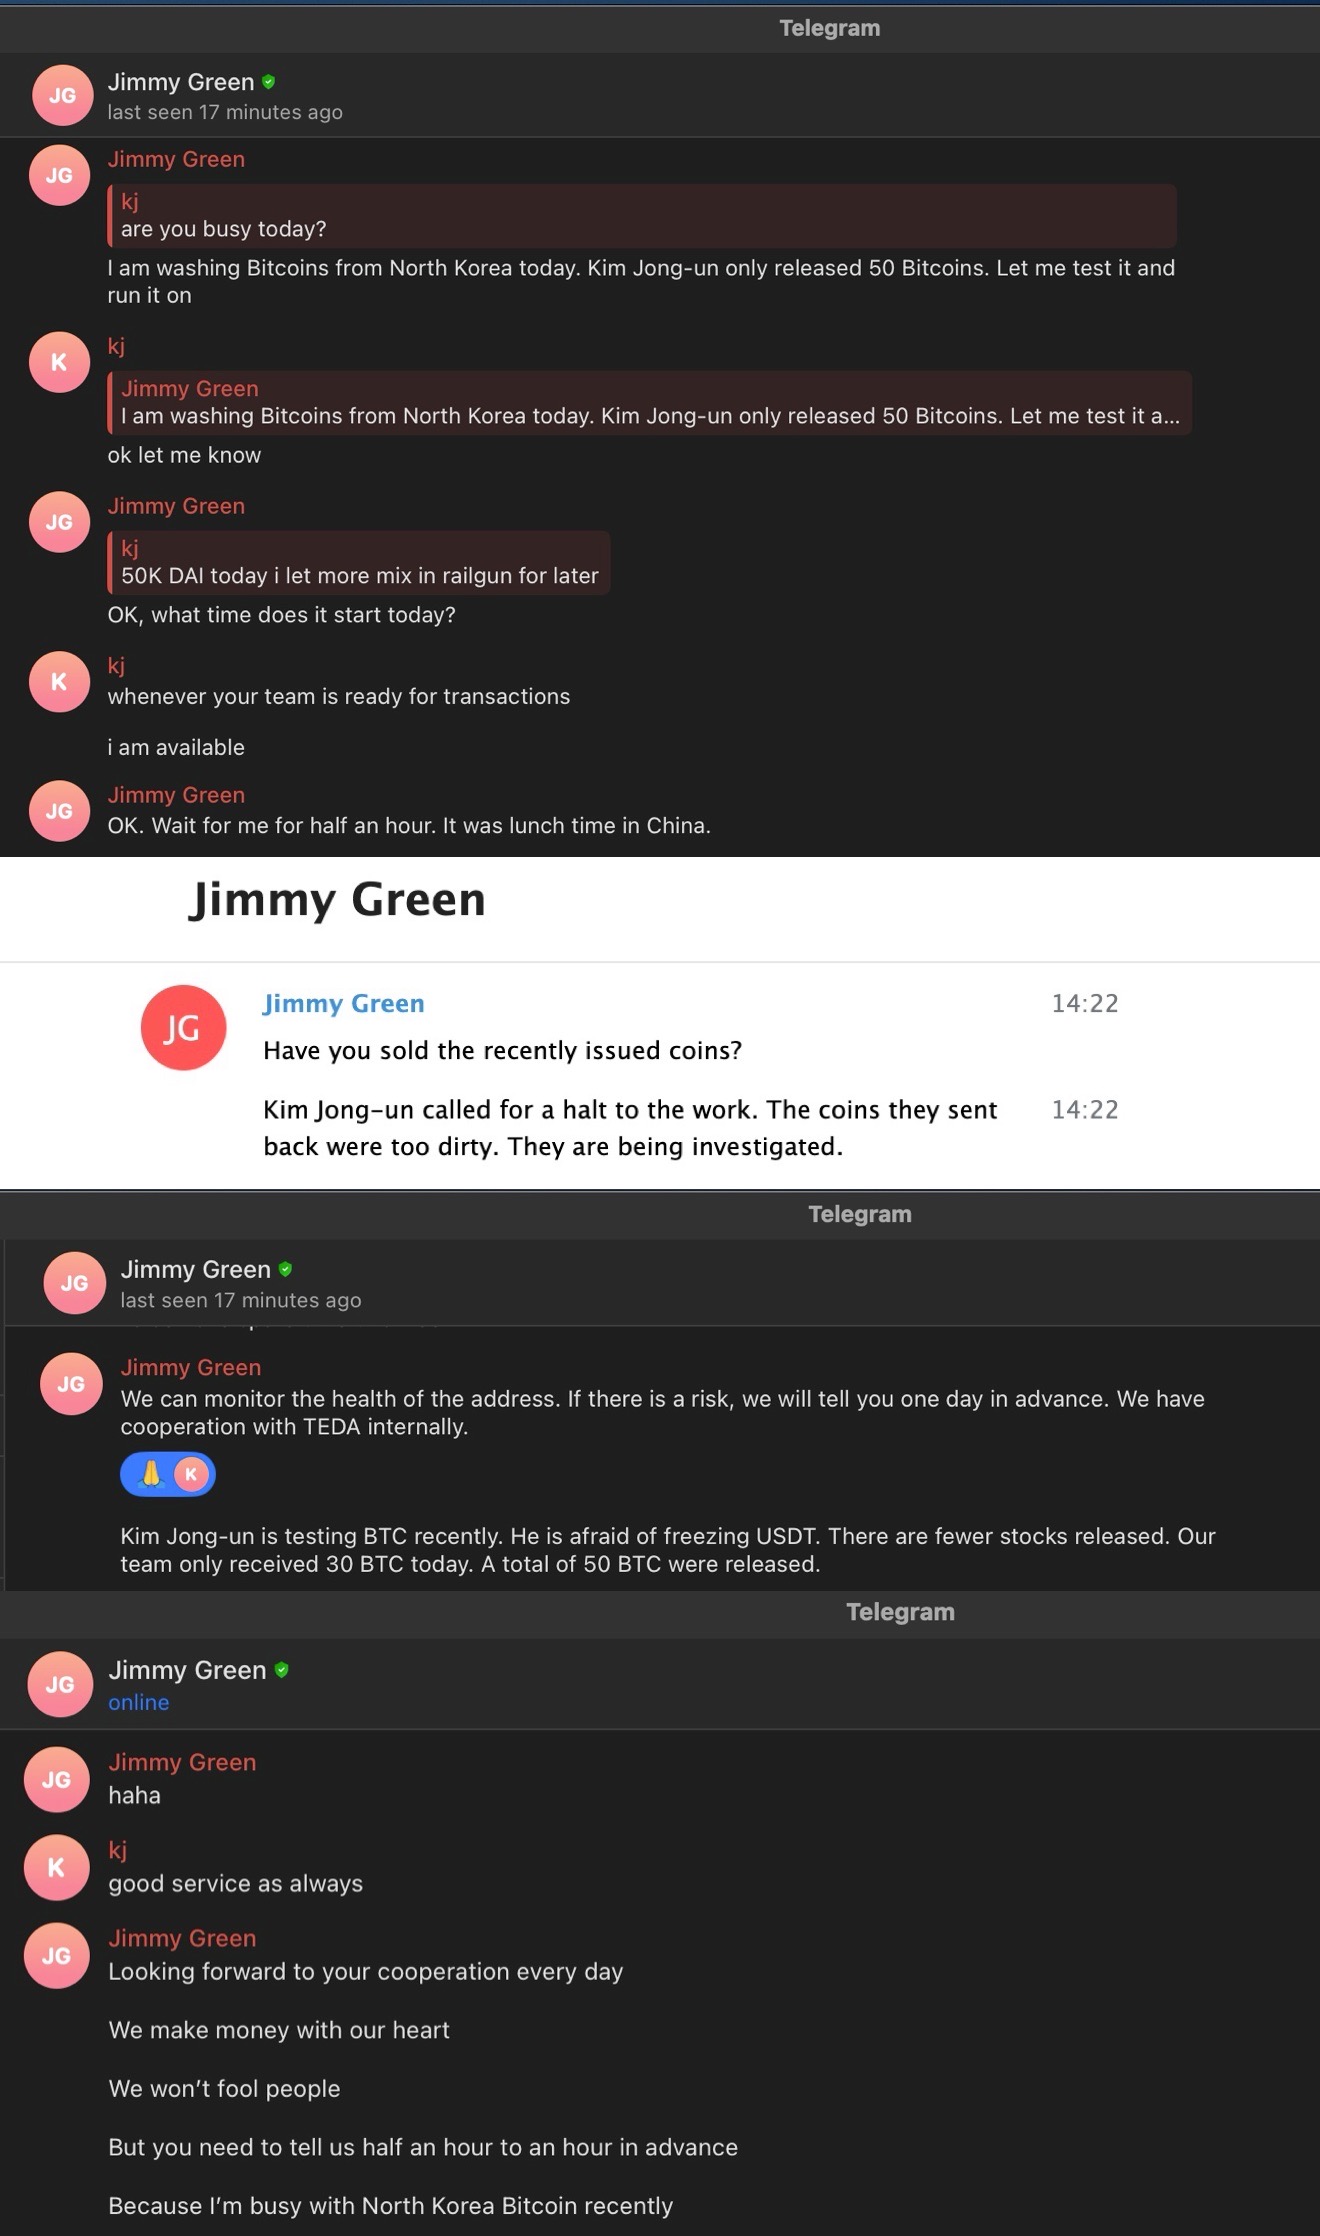
1/ How I infiltrated a Chinese organized crime syndicate that has laundered $1B+ across multiple exploits for Lazarus Group.
Posing as a client, I gathered intel that helped action freezes for the Feb 2025 Bybit exploit and attribute illicit activity onchain.



Nir Yehoshua retweeted

Claude has discovered a previously unknown enzyme system hidden in the DNA of bacteriophages. Beside the enzyme’s gene sits a long array of repeating DNA—a structure that looks somewhat similar to CRISPR.
We don’t yet understand what this system does, but only a handful of known systems share its features, and all of them are able to cut, copy, and paste DNA. Historically, the discovery of such programmable systems has helped revolutionize medicine. CRISPR, for instance, is now the foundation of genetic medicines. But it will take much more work to learn what this system does, and whether it can be put to similar use.
Read more: anthropic.com/news/claude-di…


Nir Yehoshua retweeted

🚨 BGP Hijack at 2026-09-20 10:04 UTC
🇮🇷AS197207 (MCCI-AS) announced 190 prefixes, creating 10,865 conflicts with 1,524 ASNs in 100🌏.
🌏Max propagation: 100%
⏱️Duration: 8 min (first part) and 15 min (second part)


Nir Yehoshua retweeted

636606729769440499166579950236036751749912014371509557713570027508971809534551913252252094954941974952859310861988904737359709200557919
is a factor of RSA-896
saweis.net/posts/rsa-896.htm…
Nir Yehoshua retweeted

BREAKING: 🇺🇸 Warren Buffett steps down as Berkshire Hathaway Chairman after more than 60 years at the company.
Berkshire has returned 6,642,000% since 1964, nearly 120x the S&P 500 returns.


Nir Yehoshua retweeted

BREAKING: OpenAI reveals a 10,000-agent AI swarm solved the Navier–Stokes problem in 88 hours, using 130 billion output tokens to crack one of mathematics’ most famous unsolved problems.
Nir Yehoshua retweeted

We’re sharing a solution to the Navier-Stokes Millennium Prize Problem, one of the deepest problems at the frontier of mathematics.
The proof was produced by a group of agents, using an OpenAI next-generation model significantly more capable than GPT-6 Astra.
The problem concerns whether the description of smooth three-dimensional fluid motion modeled by the Navier-Stokes equations can break down. It has remained unresolved for roughly 90 years.

Nir Yehoshua retweeted

We at RefineSec already do it - Adaptive Mutated Attacks while producing behavioral detection rules natively for EDR / XDR solutions for attacks that were not prevented.
Feel free to visit our website and schedule a demo: refinesec.com

Nir Yehoshua retweeted
SOC Analyst Professional - Attack & Defense is officially LIVE. 🔥
I built this course around one rule:
Do not just learn the attack. Execute it. Investigate it. Detect it. Tune the detection. Then try to bypass your own rule and write a better one.
Every technique follows the same hands-on workflow:
ATTACK → TELEMETRY → INVESTIGATION → DETECTION → TUNING → VALIDATION → BYPASS → BETTER DETECTION!
We go hands-on with:
RDP
PsExec
WinRM
Active Directory discovery
PowerShell and LoLBins
WMI
Registry persistence
Scheduled Tasks
Services
Credential dumping
LSASS access
Privilege escalation
Process injection
Ransomware-style activity
and much more.
Then you investigate the evidence across Windows Event Logs, Sysmon and Elastic Security EDR, and build the Elastic Security KQL detection rules yourself.
I do not want you to finish a PsExec lab knowing only that PsExec.exe exists.
I want you to understand what it drops on the target, what service it creates, what executes, what telemetry Elastic Defend collects, how to detect the behavior, and how that detection could be bypassed.
Because a rule that only catches the exact command you used in the lab is not a detection I would trust.
🔥 SOC Analyst Professional - Attack & Defense is live now:
trainsec.net/courses/soc-ana…
Stop memorizing attacks. Start owning the detections that catch them.

Nir Yehoshua retweeted
🚨 Two CVEs. One router. One complete chain to ROOT.
Last week, we disclosed two vulnerabilities affecting the Cudy WR3000 2.0:
🔴 CVE-2026-71960 - Authentication Bypass
CVSS v4.0: 9.3 Critical
🟠 CVE-2026-71961 - OS Command Injection
CVSS v4.0: 8.7 High
Individually, they are serious.
Chained together, the story changes completely.
1/ During our firmware research, we recovered signing material that could be used to forge a valid JWT.
That means bypassing the authentication boundary, accessing the MQTT interface, and reaching a vulnerable command path.
The end result?
Operating system command execution as root.
2/ This is exactly why I keep saying:
Stop looking at vulnerabilities only as isolated CVEs.
Attackers don't think in CVSS tables.
They look for chains.
One weakness opens the door.
Another one gives you the keys.
And suddenly, something that looked "limited" becomes a complete compromise.
3/ Then things became even more interesting.
Shortly after our disclosure, Hunt & Benito independently released public exploit tooling reproducing the attack chain.
Important clarification:
We did NOT create, commission, or contribute to that exploit.
But once public tooling exists, the barrier to reproducing the attack drops dramatically.
And the research entered a second wave of international coverage.
4/ Our findings were covered by:
SecurityBrief - original disclosure
lnkd.in/de6YFUF7
SecurityBrief - public exploit follow-up
lnkd.in/d6hx8c-h
HackRead
lnkd.in/eUBGwjzZ
SecNews
lnkd.in/d3xpfPiv
BugsToday
lnkd.in/dbend8WA
5/ For me, the most important takeaway isn't the headlines.
It's the technical lesson:
Security boundaries rarely fail in isolation.
Authentication bypass alone tells one story.
Command injection alone tells another.
But connect them together and you get:
Firmware -> signing material -> forged JWT -> MQTT access -> command injection -> ROOT
That is the attack path that actually matters.
6/ This is the kind of research we want to push at Cipher Security Labs:
Deep vulnerability research
Full attack-chain analysis
Understanding how weaknesses interact
Product security
Coordinated vulnerability disclosure
Not just:
"Here is a CVE."
But:
"Here is what an attacker can actually do with it."
More research coming.
Our CVE Tracker:
ciphersecuritylabs.com/CVE-T…
#CyberSecurity #VulnerabilityResearch #CVE #IoTSecurity #ProductSecurity #FirmwareSecurity #SecurityResearch #InfoSec
Nir Yehoshua retweeted

Public exploit code can chain two #Cudy WR3000 v2 flaws to bypass login checks and allow full control when the router’s control service is reachable. Update to firmware 2.5.24 or later.
Listen to the article or read: hackread.com/cudy-wr3000-rou…
#CyberSecurity #Router #Vulnerability

Nir Yehoshua retweeted

חברה קטנה של 1.3 מיליארד דולר בשם Unusual Machines, $UMAC נכנסה הלילה למרכז הבמה אחרי דיווח שהממשל של טראמפ בוחן מימון לחברות רחפנים אמריקאיות, כחלק מדחיפה לבניית שרשרת אספקה מקומית בתחום הרחפנים.
מה שהופך את הסיפור לרגיש ומעניין במיוחד, הוא שדונלד טראמפ ג׳וניור, הבן של הנשיא דונלד טראמפ, יושב בוועדת הייעוץ של החברה ומחזיק במניות שלה.
כמובן שגם מניות רחפנים נוספות כמו $ONDS $RCAT $AVAV $KTOS עולות במספרים דו ספרתיים, בעקבות הדיווח.
חברת $UMAC היא בעצם חברת תשתיות ורכיבים לעולם הרחפנים. החברה מייצרת ומוכרת מנועים, מצלמות, בקרי טיסה, משקפי FPV ורכיבים נוספים לרחפנים, עם מיקוד גדול בייצור אמריקאי במקום הסתמכות על סין.
בנוסף, יש לה גם פעילות איקומרס דרך Rotor Riot, פלטפורמה שמוכרת ציוד ורחפנים לקהילת הרחפנים בארה״ב, ומחזיקה גם במותג Fat Shark שנחשב מוכר מאוד בעולם משקפי ה-FPV לטייסי רחפנים.
כל הסיפור של החברה יושב על תזה אחת ברורה, ארה״ב רוצה להחזיר את שרשרת האספקה של הרחפנים הביתה, במיוחד אחרי שהפנטגון הבין עד כמה הוא תלוי בייצור סיני.
הלילה יצאו דיווחים שהממשל של טראמפ מנהל שיחות על מימון לחברות רחפנים אמריקאיות דרך הפנטגון ומשרד ה-Office of Strategic Capital, כחלק מתוכנית עצומה להגדלת ייצור הרחפנים בארה״ב.
לפי הדיווחים, $UMAC היא אחת המועמדות לקבל את המימון הזה, שיכול להגיע דרך חוב, השקעת הון ואפילו אחזקות ממשלתיות בחברות.
במקביל, טראמפ ג׳וניור הוא גם יועץ בחברה וגם בעל מניות משמעותי, כך שככל שהחברה נהנית יותר מהמגמה הזאת, גם הוא נהנה ישירות מהעלייה בשווי ומההתלהבות סביב התחום.
השוק כמובן קלט את זה מהר מאוד, והמניה כרגע בעלייה של כ-60%.

Nir Yehoshua retweeted

$SIDU
Found support exactly where we shared the setup.
We shared it at $3.28.
Price is now $3.92.
The red zone remains the major resistance area to clear.


$SIDU | New Setup
Last time I shared the $SIDU setup -
price moved +72% in 7 trading days, hit the final target, while I shared my profit-taking approach (see post below).
Then price pulled back like clockwork -
TAKING PROFITS ON TARGETS IS REAL.
Now:
If price holds above $3.40, it can continue higher toward the orange POC line.
Must watch if $4.44-$4.81 acts as resistance or gets cleared.

Nir Yehoshua retweeted

macOS標準のテキスト変換コマンド「textutil」と、人気のオープンソース型パスワード管理ソフト「KeePassXC」が、それぞれ正規の動作のままでも、ファイル処理を自動で行うサーバーや業務スクリプトに組み込まれた場面では、攻撃者の入力に応じて想定外の動きを引き起こしうるとの調査が公開。
具体的には、textutilでは攻撃者が用意したHTMLを変換させるだけでサーバーから外部URLへ通信が発生し、本来到達できない社内ネットワークやlocalhost向けのサービスへの探りに使われる可能性、KeePassXCでは細工されたデータベースファイル1つでファイルを開く処理に通常の約100倍のCPU時間を消費させられる可能性が指摘。
【要点のまとめ】
・textutilでHTMLをテキストに変換させる際、HTML内に書かれた外部画像やスタイルシート等への参照を解決しに行く挙動が確認。攻撃者が用意したHTMLをバックエンドの処理サーバーで変換した場合、サーバーから攻撃者がHTML内に仕込んだ参照先URLへHTTP通信が発生し、サーバーから到達可能な社内ネットワークやlocalhost限定サービスへの探索に使えるSSRF型の入り口になりうるとの指摘
・KeePassXCでは、KDBXファイル(パスワードDBの保存形式)内のメタデータに含まれる鍵導出回数(総当たり攻撃を遅らせるための反復計算回数)が、ファイル側の指定で決まる仕様を確認。調査でベースラインとした検証用DBが約100万回のところ、細工された検証用ファイルでは約3億5,332万回まで引き上げられ、開く処理が通常の0.05〜0.07秒から約7.3〜7.7秒(約100倍)に膨らむ結果が示されたとされる
・ただしKeePassXC側の検証は公式リリース版ではなく、開発中のソースビルド「2.8.0-snapshot」(執筆時点の最新公式版は2.7.12)で行われたもの。「公式リリース版での再検証が必要」と研究者側も明記しており、現行公式版で同じ挙動が再現するかは未確認
・暗号方式が破られたわけではなく、パスワードや鍵が漏れる話でもない点を明示。あくまで「開く側のCPU時間が想定外に膨らむ」処理側の資源消費を狙うタイプの問題として整理されているとのこと
・どちらも単体では「textutilやKeePassXCのバグ」とは扱われておらず、自動処理パイプラインに組み込まれて初めて攻撃者の入り口になるという統合レベルのリスクとして位置付けられている
・対策としては、textutil側で「-noload」オプションによるリモート参照無効化(現行のtextutilに既存のオプション)・変換処理のサンドボックス化・外向き通信のデフォルト遮断、KeePassXC側でKDFパラメータの上限設定・極端な値への警告表示・自動処理向けの安全モード提供(こちらは研究者側の設計提案)などが、一次情報の中で示唆として挙げられている
・調査はCipher Security Labsが公開。同社は両事例を「正しく動いている機能でも、本来想定されていない場面で使われると攻撃の入り口に変わりうる」というパターンとして整理
詳細は以下を参照:
cybersecuritynews.com/resear…
Nir Yehoshua retweeted

Researchers Warn macOS textutil and KeePassXC Can Become Attack Primitives in Automation ift.tt/WvUT5z9
Nir Yehoshua retweeted

Výzkumníci varují, že macOS textutil a KeePassXC se mohou stát útokovými základy v automatizaci. cybersecuritynews.com/resear…