




So all this hype about PentAGI, a pentesting automation platform that uses default credentials... But "binds to 127.0.0.1 for security." To be fair, I haven't tried to install this yet, but that's not necessarily my favorite indicator.

1
2
331
.@HackingDave did you just pull a ~Clawdbot~ Moltbot with ~SideChannel~ Nightwire? 😂🤣
If you're ever curious about how a person with ADHD thinks through things, the song "Ronald" by Falling in Reverse should help give the example.
1
1
378
POV: @HackingDave rolls up to BlackHat and DefCon this year.
Reel credit: instagram.com/csmotoringco
2
357
From a human perspective this is actually awesome. From a risk perspective, we're cooked.

The American migration to Xiaohongshu
(RedNote) may be the craziest accidental cultural exchange ever.
Hundreds of thousands of users landed in an app not localized or in their language.
One day in, and it’s already considered rude not to subtitle videos in the other language.


564
Hey @PortSwigger @Burp_Suite, a fairly annoying limitation I've exp with Intruder is that I cannot "designate" what payload number is what. I discovered this when I was trying to find a way to force a smaller wordlist (ext) to be enumerated first in cluster bomb mode.

1
238

Hah, #milestone? Who are all you people and what are they paying you?🤣
More #hacking and now more #Judo stuff inbound, all via shitposting.

4
326
root@alex:~/ # retweeted

Please bring our friend home ❤️❤️
sudo find / -name cnelson

ALT Missing person Chris Nelson. Last seen at Highwire Coffee Roasters on San Pablo Ave. at roughly 10:45 a.m. on Monday, August 19, 2024 wearing a rainbow checked shirt (see picture on right), khaki or dark blue shorts, Vans shoes, and carrying a messenger bag. Please call 510-981-5900 with information
root@alex:~/ # retweeted

Stitch - It is with a heavy heart that I announce the passing of #ScriptKitty (aka Pax). Many of you may have seen in passing this little orange floof if we ever had a video chat or IRL but most don't know how close he truly was to me. Fuck you, cancer.


Sitting here resetting my DNS resolver locally because LP is not working but for once, it wasn't DNS (at least on my end). What has this world come to?🤣

1
254
root@alex:~/ # retweeted

New blog is out!
Beyond the Basics: Exploring Uncommon NTLM Relay Attack Techniques guidepointsecurity.com/blog/… via @GuidePointSec


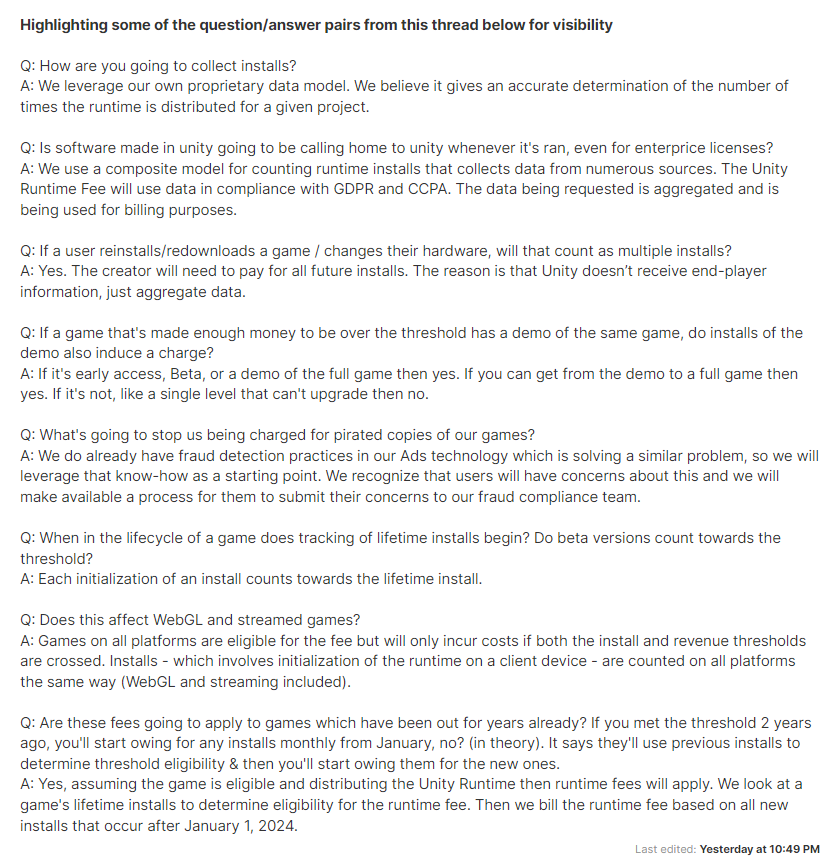
So what happens if, say someone creates a script that builds out a new VM with different hardware specifications, installs the game, nukes the VM and puts this in a for loop, randomizing the hardware each time? But that would be unethical, right? 😁

3
755
TIL @google trains their AI model to learn your voice, for more than just internal stuff. How do I know? Calling my phone from an unknown number will trigger the screening service provided by Google, and it's my voice talking to you. It's confused tf out of clients.
3
366
"Forbes released a new Bug Bounty list aimed at Black Hats" is the correct title 😂🤣
How is this not an Onion article? #infosec #hacking #PleaseDont

Forbes just created a top 200 list of the most secure companies.
This will end badly.
H/T @mikepsecuritee
forbes.com/lists/most-cybers…
1
2
1,021
I have a fellow Red Teamer who got laid off and they are looking for a remote position. I've worked with them for many years and can vouch for them. Interests are NetPen, Red Team, AD Security, etc. Please spread the word. #infosecjobs #infosec #Hacking