

On a mission to build Africa leading AI Cyber security company
Africa 🌍
Joined April 2026
- Tweets246
- Following9
- Followers320
- Likes791






Pinned Tweet
Have you ever hesitated to use a security scanner because you didn’t want your code sent to a third party?
OffShield AI It scans locally, shows your vulnerabilities on a clear dashboard, suggests AI-powered fixes, and lets you push those fixes straight to GitHub or GitLab.

We’re looking for developers and engineers to test OffShield AI.
It’s a security-first IDE that scans your code, flags vulnerabilities, and helps you fix them without sending your code outside your environment.
Try it here: offshield.tech
ide.offshield.tech
🤖 Made with AI


Offshield Security retweeted

We’re looking for developers and engineers to test OffShield AI.
It’s a security-first IDE that scans your code, flags vulnerabilities, and helps you fix them without sending your code outside your environment, everything remains private. It also allows you to push your secure code straight to your codebase via GitHub or GitLab.
We’re especially interested in feedback on:
• Bugs with clear steps to reproduce
• Missed or false findings
• Feature ideas with a real use case
Try it here: ide.offshield.tech
If you test it, drop your feedback in the comments .
Your input will directly shape what we improve before wider launch and implementations.
🤖 Made with AI


Have you ever wanted to scan your code for vulnerabilities without sending it to an external service?
A lot of teams especially in fintech and regulated industries can’t risk their source code leaving their environment. But most security tools still require uploading code to the cloud.
That’s why we built OffShield AI (@offshield_ai ) .
It’s a privacy-first application security tool that runs locally. It finds issues like hardcoded secrets, weak crypto, SQL injection, and broken access control, then gives AI-assisted remediation suggestions all without your code leaving your machine.
You also get:
• A dashboard that shows your vulnerabilities and security score
• AI remediation you can apply directly
• The ability to push fixes to GitHub or GitLab from the tool
Try the web tool: ide.offshield.tech
Main site: offshield.tech


Offshield Security retweeted
Have you ever wanted to scan your code for vulnerabilities without sending it to an external service?
A lot of teams especially in fintech and regulated industries can’t risk their source code leaving their environment. But most security tools still require uploading code to the cloud.
That’s why we built OffShield AI (@offshield_ai ) .
It’s a privacy-first application security tool that runs locally. It finds issues like hardcoded secrets, weak crypto, SQL injection, and broken access control, then gives AI-assisted remediation suggestions all without your code leaving your machine.
You also get:
• A dashboard that shows your vulnerabilities and security score
• AI remediation you can apply directly
• The ability to push fixes to GitHub or GitLab from the tool
Try the web tool: ide.offshield.tech
Main site: offshield.tech
Offshield Security retweeted
Have you ever hesitated to use a security scanner because you didn’t want your code sent to a third party?
OffShield AI It scans locally, shows your vulnerabilities on a clear dashboard, suggests AI-powered fixes, and lets you push those fixes straight to GitHub or GitLab.
Try it out now
Launch the web IDE ide.offshield.tech
Visit our website Offshield.tech
Offshield Security retweeted
Some of the better product decisions come from real constraints instead of ideal conditions.
With OffShield AI(@offshield_ai ) , the constraint of keeping code on-premises shaped a few choices:
• Local scanning so source code never leaves the environment.
• Local AI remediation so findings and fix suggestions stay private.
• Focus on practical, high-signal issues rather than maximum alert volume.
• Designed around teams (especially in fintech) that cannot use pure cloud scanners.
Constraints force clarity on what actually matters to the people who will use the tool.

Offshield Security retweeted
We’re getting closer to launching OffShield AI (@offshield_ai) and we’re looking for a small group of developers and engineers to test it before we go wider.
OffShield AI is a web IDE, privacy-first application security tool designed for teams that need to find vulnerabilities without sending source code outside their environment.
The current version runs locally and can already flag issues such as hardcoded secrets, weak cryptographic functions, potential injection patterns, and certain access control problems, with AI-assisted remediation suggestions that also stay on-prem.
If you:
• Build or maintain web or API-based applications (especially in fintech or regulated environments)
• Care about catching security issues earlier in development
• Are open to giving honest feedback on usability and detection quality
I’d like to hear from you.
We’re keeping the early testing group small so we can properly support everyone and act on the feedback.
Drop a comment or send me a message if you’re interested in trying it.


OffShield AI ----> Coming Soon
You know I have always been thinking on what kind of AI security product can be built to solve some of the security issues we have in Africa especially in the Fintech space.
This year we have recorded breach upon breach within fintech organisations from Remita to UBA etc.
I came up with an idea and a question, what if we can minimise this damage from the codebase even before it gets deployed and that's when @offshield_ai (Offshield AI) idea came in.
This is not your regular SAST tool neither is it your regular AI scanning tool. Offshield AI is built different.
Offshield AI is an IDE code extension that can be integrated into your codebase either both VScode or Cursor AI @cursor_ai ,
This is the way it works, do you know how wired it is to send your whole code to a third party software or simply connection your code to an external testing tool ,
Offshield is reducing the risk of leaking out your source codes to an external party, Offshield Ai is built to test your code locally while there is a Licence code you will have to input in your code editor before it ever runs any test for it (the licence is subscription based/30days).
Offshield AI is solving the problem of having your code to external party, and we also help mitigate the vulnerabilities in your codes right from the development stage before you deploy.
More news is coming soon regarding Offshield Ai 🖇️

A major PHP vulnerability is letting attackers take over websites with no login. Sites are going offline.
Patch is out - check your site now:
Does your site use PHP ?
Updated to the latest version ?
Checked for suspicious activity ?
If not updated, contact your host today.
Zero-click spyware is real.
Candiru infected 45+ Al Jazeera devices just through targeted ads — no click needed, just loading the ad.
Stay safe:
- Update devices & browsers
- Use an ad blocker
- Use reputable security tools
Just browsing is no longer risk-free.
Offshield Security retweeted
AI remediation (next layer) Each finding is designed to include an AI-generated remediation suggestion.
For privacy reasons this uses a local AI model via Ollama (running on the same machine). The model is pulled and executed locally so code and findings stay inside the environment.
Still taking time to install for the real testing, but yeah its going to come out well.
Once Ollama is set up (ollama pull llama3.2), it will start giving practical fix suggestions in real time.

We are working on OffShield AI (@offshield_ai ), a security tool aimed at helping teams (especially in regulated environments like financial institutions) find vulnerabilities in their code without sending source code outside their environment.
What the core engine does today
Right now the First MVP is a local, on premises scanner.
You upload a file or a zip of your code, and it runs a set of detection rules against it. In the current version it can already flag things like:
Hardcoded secrets and API keys
Weak cryptographic functions (e.g. MD5)
Potential SQL injection patterns
Simple IDOR-style patterns where client-supplied IDs are used directly
Everything runs locally.
The code never leaves the machine, this is intentional many organisations (especially banks) cannot send source code to a third-party SaaS scanner.
About the UI
The interface you see is temporary. It’s a clean, functional web UI so we can test the engine and the workflow. The design and user experience will be improved later. At this stage the focus is on the core scanning engine and the infrastructure that keeps everything local and private.
AI remediation (next layer)
Each finding is designed to include an AI-generated remediation suggestion. For privacy reasons this uses a local AI model via Ollama (running on the same machine). The model is pulled and executed locally so code and findings stay inside the environment.
Right now, if Ollama isn’t running, the app still shows the vulnerability and clearly states that AI remediation is unavailable. Once Ollama is set up (ollama pull llama3.2), it will start giving practical fix suggestions in real time.
Why this approach
A lot of security tools either:
Require sending code to the cloud, or
Produce too much noise
The goal with OffShield AI is accurate detection + clear remediation, while keeping the option to run fully on-premises. This first version is the foundation of that engine.
Still early, but the core scanning path is working. Next steps are expanding the rules, tightening the AI remediation, and improving the interface.
Happy to hear thoughts from people building in AppSec, DevSecOps, or working with regulated industries.
Offshield Security retweeted
For efficient testing, making the UI better by the time.

AI remediation (next layer) Each finding is designed to include an AI-generated remediation suggestion.
For privacy reasons this uses a local AI model via Ollama (running on the same machine). The model is pulled and executed locally so code and findings stay inside the environment.
Still taking time to install for the real testing, but yeah its going to come out well.
Once Ollama is set up (ollama pull llama3.2), it will start giving practical fix suggestions in real time.
Offshield Security retweeted
A SaaS tool that will be used privately in organizations to audit their codes and perform SAST in real time without having to have the fear of their vulnerability being leaked out to the public especially for the Financial Sectors, while having access to their own code base and not directly linked to any third party application or whatsoever, so this way there wont be any form of data breach or data loss directly to the public as everything being checked remain in their environment as they own it.
NOT EVEN WE, WILL HAVE ACCESS TO THE CODEBASE.
@offshield_ai
Financial institutions demand absolute control over their code and software supply chain.
OffShield Security delivers autonomous, AI-driven code protection engineered specifically for banking and fintech infrastructure.
🤖 Made with AI


Do you back up your important files regularly ?
Yes / No / Sometimes
Drop your answer 👇
backups shouldn't be after you lose something.
So make sure to backup your important files regularly.
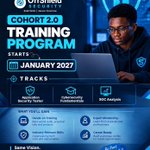
OffShield Security Cohort 2.0 registration form is open
3-month hands-on cybersecurity training | Jan - Mar 2027
You'll get: Practical labs, mentorship & real-world skills and be career ready.
Limited slots. Closes Oct 31, 2026.
Apply: docs.google.com/forms/d/e/1F…
