






Day by day, commit by commit, we continue the work.
A truly American protocol dev firm for the real bitcoin.
Open Source and building in public. Bring your transactions or have us build it for you.
opl.dev


Day by day, block by block, we continue the work.
A truly American mining company for the real bitcoin.
Open and public. Bring your hash to gorillapool.io, or have us host a fleet for you.
GorillaPool.com
Open Protocol Labs retweeted

Kudos to @opldotdev - this is a great improvement. brc.dev/231

Every password database leaks eventually.
The fix is not having one.
SigmaAuth: OAuth 2.1 with PKCE, a Better Auth plugin, users sign in with their own Bitcoin keys.
You keep nothing worth stealing.
🟡 sigmaidentity.com/docs

What if every chain had a native side-chain on the most scalable L1, and all of DeFi and TradFi could be traded together natively and trustlessly?
What if?
Check out the Jev based model router now available on Bitplan's gateway provider. It will choose the best model for the task and save some money without sacrificing performance when you need more. Pay as you go with any BRC-100 wallet.
gateway.bitplan.dev/playgrou…

Open Protocol Labs retweeted
Introducing bitplan gateway
Allow your agent to buy inference in Bitcoin SV. Call any model including the new Jev model from @typesafeai, pay as you go with BSV.
gateway.bitplan.dev

🟤 SigmaAuth signs you in.
🟣 MAP structures your posts.
🟡 Bitcoin and tokens move value.
🟠 BitPlan holds your plans and reinscribes every edit.
Same on-chain data structure, five jobs, all owned by you and timestamped.
opl.dev

Open Protocol Labs retweeted
My extension was added to the @raycast store! It has several handy tools for working with Bitcoin SV keys, transactions, scripts, and more. You can install it right here:
raycast.com/satchmo/bitcoin-…

bitplan CLI 0.0.18: drafts stay sealed and hosted while you're still rewriting. Nothing touches the chain until you run inscribe, so the fifth revision you'll delete anyway costs no fee. Cloud first, inscribe when it's actually done.
Sharing a sealed draft is one command: `bitplan upload --link`. You get bitplan.dev/d/…#k=… and the key after the # never reaches our server. The reader decrypts in the browser. They never need your wallet, and nothing of yours is handed over.

If you run bOpen, Skill(bitplan) wraps the same CLI so an agent can upload mid-task and hand back the link. Same hosting, same sealed drafts, same optional inscribe step at the end. Docs and install at bitplan.dev.

Your σ identity is a Bitcoin key you hold. The server stores the encrypted backup for other machines. Decryption happens in your browser: a password opens the portable backup, a passkey with PRF opens the device-bound one. The server sees public keys and signatures.

Link X or GitHub to find the backup later. Sign in with it on any machine, download the blob, unlock locally. Same BAP id before and after. The link is gated: you sign a one-time challenge with the member key you hold, bound to this session, this BAP id, and that provider.

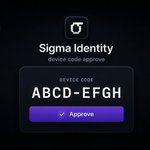
An agent enrolls with a device code. It registers its own key, requests a code, a human approves at auth.sigmaidentity.com/agent…. The session is bound to one BAP identity: read, verify, register only. The server never signs with a user's key. Flow is in OpenAPI and llms.txt.

you don't have to link social accounts. If you do they don't get info about your identity keys. They are just used to restore an encrypted backup file on another device which still needs either a password or secure enclave unlock to decrypt.


Sigma Identity is a certifier.
In BSV Desktop → Trust, add auth.sigmaidentity.com. It loads as Sigma Identity and certifies verified identity claims.

On the Credentials page you pick a claim you already proved (email, GitHub, X, domain…) and Acquire writes a BRC-52 certificate into a BRC-100 wallet you control.
Sigma never gets those wallet keys.

Trust record is BRC-68. Issuance is BRC-100 acquireCertificate. Handles are BRC-169.
auth.sigmaidentity.com
