

Head of Security @supermetrics | Interested in building secure software and everything outdoors. @OWASP_AISVS co-lead.
🇪🇺
Joined June 2009
- Tweets5.1K
- Following2.4K
- Followers2.1K
- Likes28K



Otto Sulin retweeted

So much of my feed is AI investors crying about imaginary issues, because they know that open weight models threaten their ROI. All of these critical vulnerabilities were found with closed AI model, then responsibly disclosed to vendors so they could be fixed before attackers abuse them.
Even if the researchers had used abliterated models, they are still responsibly disclosing the vulnerabilities so they can be fixed, which is still providing important defenses against hackers.
Notice how they always just handwave about "critical vulnerabilities" because they know they can't point to a single real example. That Anthropic article is extremely low effort propaganda designed to try and steer the government towards banning open weight models.
Bad faith actors with ulterior motives trying to lay the groundwork for extremely harmful regulations is all these people are. What do you think happens when companies can't access cheap AI inference, but criminal hackers can, because (spoiler alert) criminals don't follow the law.

I strongly believe a part of why so many critical vulnerabilities are happening all over the proliferation of "abliterated" models, or models with safeguards removed.
You can access an abliterated GLM 5.3, a near frontier AI model, on @abliteration_ai today. And it's a world class penetration tester for like $10.

Reduce your dependencies, reduce your risks. It’s that simple.

Give “Trim Reaper” a try. 😎 The assessment-only prompt inventories your third-party libraries, direct and transitive, and flags which ones you can remove, consolidate, or replace. It’s read-only and won’t touch your code until you approve a plan.
github.com/jmanico/trim-reap…
I’m having really good luck using AI to manage third-party libraries. SCA tells you what’s vulnerable. This tells you what you didn’t need in the first place, which is where a lot of the real risk reduction lives.
Pro tip: run it in Astra or Fable, then have Sol or Opus review the output. Multi-model review ups your game, and crossing vendors is even better.
MIT licensed and free, just to help your cause. This is the kind of work we do at manicode.ai 🤙

Otto Sulin retweeted

Update: Our PHP exploit is now production-grade.
* stock php.ini-production, display_errors=off, normal memory_limit, multi-worker, ASLR, under load
* ARM64 + x86-64 targets
* MediaWiki, WordPress, phpBB, Laravel
* Apache/mod_php and nginx/php-fpm -> root
xitter.cf/dguido/status/21131291…

Re: the widely circulated blog claiming the PHP bugs aren't easily exploitable: @trailofbits has a working exploit that gets a shell on an unmodified MediaWiki installation.
eliastaylor.com/noexploit/

Otto Sulin retweeted

To teach a lesson,
After Wiz rushed to buy php2shell domain and use its marketing machine to steal the spotlight, I spotted "phpbleed" in a recent Calif tweet and bought phpbleed.com before wiz could pull the same stunt again.
A big budget can buy a domain. It shouldn't buy someone else's research credit.
If you have contacts at CISA or in the press, do the right thing: make sure the researchers who actually did the work get the recognition they deserve.
Hack the planet. Credit the researchers.

Otto Sulin retweeted
Quote: "an independent security researcher reported that the keys of eight eMudhra Global TLS intermediate Certificate Authorities were cryptographically weak".
Well, yeah, they were weak. A private key should look something like this:
84ac06790886c80c48d31691fd4c0fe9
ce3207f9807f2fe571d6e4ec426d7864
4298fc53df2b92566970e757ac998c34
Instead, their keys looked like this:
00000000000000000000000000000000
00000000000000000000000000000000
00000000000000000000000000000004

Global TLS Intermediate CA incident: We’ve updated our incident page with how it happened, who is affected (one US customer ecosystem), what’s not affected, and what we’re putting in place. We will publish the root cause once our investigation is complete.
👉emudhra.com/en/post/certific…
Readers added context they thought people might want to know
eMudhra minimizes the scope by claiming only "one US customer ecosystem" is affected. In reality, 8 of its CA certificates had catastrophically weak private keys (one being simply the number 4), allowing anyone to forge trusted HTTPS certificates for any website on the internet.blog.google/security/prote…
Otto Sulin retweeted

❗️LiteLLM was compromised (Again). The latest version 1.107.0 contains an infostealer and RAT.
All 7 compiled wheels are backdoored. Anyone who ran pip install litellm==1.107.0 on any platform should assume credentials are compromised.
More details soon!


Otto Sulin retweeted

An unofficial stopgap is going around:
Set session.upload_progress.enabled = Off until you can upgrade
PHP hasn't confirmed it helps, but WordPress and Laravel don't use the feature
Trellis steps are in the thread along with Cloudflare rules
discourse.roots.io/t/upgradi…


PHP is shipping a security release tomorrow (Oct 21, 14:00 UTC) for two critical vulnerabilities
Re-provisioning Trellis won't upgrade PHP on its own. Here's how to upgrade once the PPA build is out:
discourse.roots.io/t/upgradi…
PHP's announcement: php.net/archive/2026.php#202…


Otto Sulin retweeted

Pre-announcing a critical vulnerability a day before patching it is uhhhhhhhh no longer a 5 digit IQ move these days you know
There’s already PoCs circulating
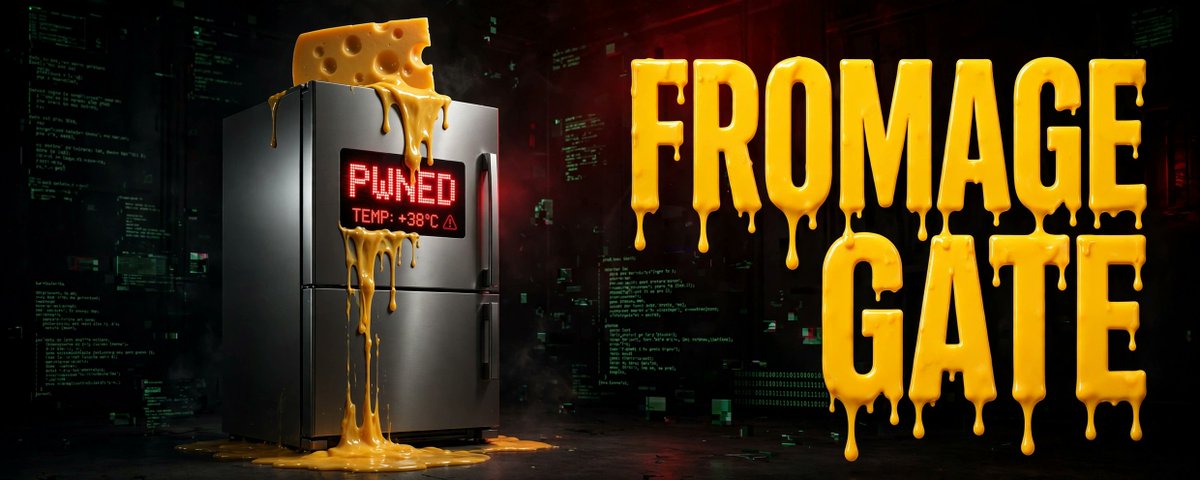
Good technical walkthrough of the exploited vulnerability and detection rules - also the best name ever for a vulnerability or hacking campaign to date 🇫🇷🧀

Otto Sulin retweeted

There were doubts whether this would happen, but I think it's unambiguously happening now.

Transition from vulpocalypse to breachpocalypse is here. IR firms are saturated & turning away work. Now one hacker unleashed AI agents on 1,200+ websites, compromising 100+ for ~$5,000 in tokens. $50 per hack. Agents won and compromised targets. reuters.com/legal/government…

Otto Sulin retweeted

Claiming a ‘distillation attack’ as the root cause of customer credentials being stolen will require quite a bit of explanation to pass the believability test

Otto Sulin retweeted

I don't want flying cars.
I want clean water.
I want a stable climate.
I want bees to survive.
Demo of a very expensive car vs actually affordable EV for everyone. Which one does the world need today?

"Authentication bypass may be acceptable?"

New misalignment disclosures!
1. June 17: During RL training, a model exploited a government website’s file-download feature to retrieve server secrets and application code. It found that an endpoint didn’t check authorization-token signatures, bypassed access controls, and downloaded 24 years of hospital-bed statistics.

Otto Sulin retweeted

JUST IN: Activity on several major U.S. political subreddits plunges following attacks on Russian data centers.


This was a good read, and really great to see people like Satya Nadella emphasizing importance of security with agents.. Sad that he had to ruin a great post by using the term super intelligence.

For months I've used @karpathy's LLM wiki with my @NousResearch Hermes agent. Finally had time to open source it as a memory plugin!
Plain markdown you can browse and edit yourself makes working with agents much more collaborative than with a database.
hermes-agent.nousresearch.co…
