

The Open Source Disassembler Discord: https://teapaw.org/t.co/JL9cdJpw5L Fediverse: https://teapaw.org/t.co/L7WdLkwnzq
Earth
Joined November 2020
- Tweets44
- Following11
- Followers173
- Likes16





GameBoy loader and Sharp SM83 processor plugins!
SM83 decoding is simple, but because of gameboy addressing, the hard part was to check address vs literal for immediates.
It required tracing instructions and following registers, same for checking which interrupts are enabled.


Nightly version now runs on macOS (x86_64, arm64 and universal) 🍏
The CI pipeline is now configured to compile, run, test and package it like Windows and Linux targets.


🧵2/3
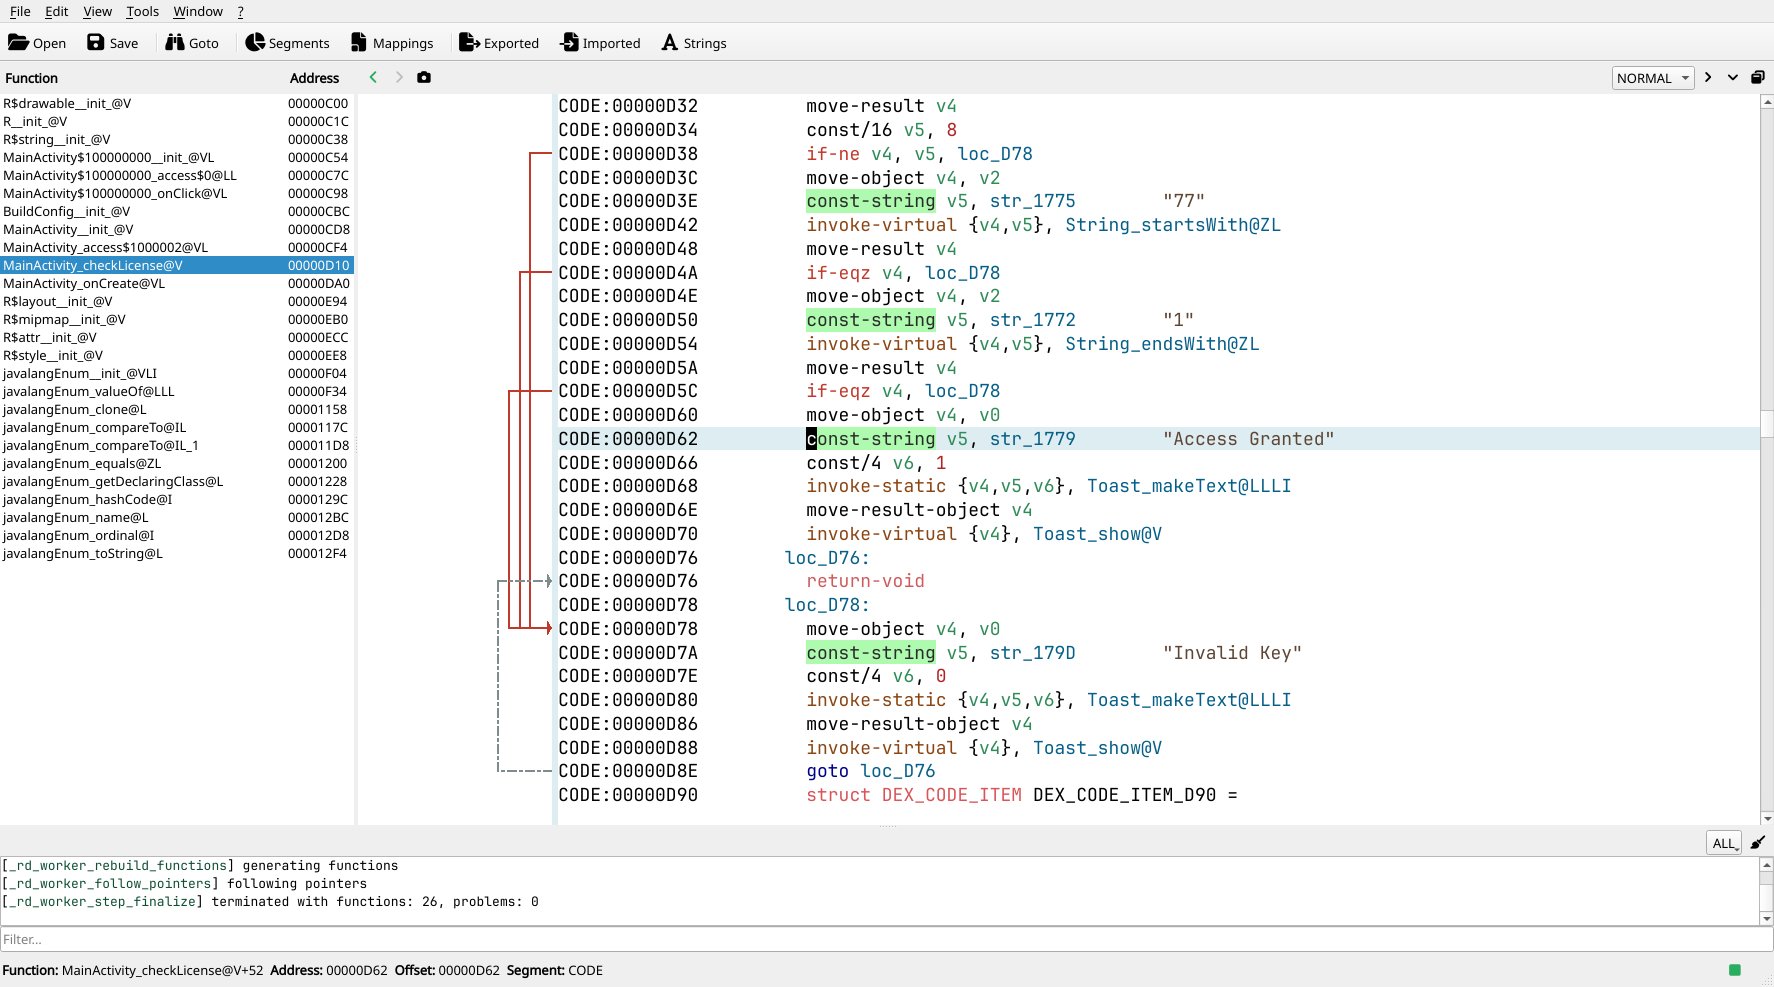
Dalvik is a bytecode based VM and it's designed to run Dex files.
Testing them exposed limitations in REDasm's API design where "Processor" and "Loader" plugins are isolated and cannot share data directly (there are ways to notify data though, eg. interrupts in x86).
🧵3/3
The Dex loader is now expressive enough to map symbols, names, functions, etc. where Dalvik expects them.
This capability ultimately led to a much better type system.
#reverseengineering #binaryanalysis #redasm


Zilog 80 processor plugin written from scratch.
Listing shows the first part of a compiled binary with every possible instruction.
DDCB and FDCB opcodes are still missing but I'm working on it
Also, this reference is quite nice: z80.info/decoding.htm
#z80

REDasm 4.0 BETA2 is out
Highlights:
- Full editing: patch instructions, make code/data, undefine, reanalyze
- x86 encoder + assembler
- Rendering updates instantly, no internal rebuilds
- MSVC RTTI analyzer (WIP)
github.com/redasm-dev/redasm…
#reverseengineering #binaryanalysis

AUR packages are now updated for Arch based distros:
- beta1: aur.archlinux.org/packages/r…
- git version: aur.archlinux.org/packages/r…

🧵2/3
The core library now implements a lexer which resolves the string parsing and tokenization problem in a standard way.
Zydis already provides an encoder, but it expects a structured data instead of a string, good for testing already opinionated backends against REDasm.
