



۟ retweeted

CA: Bo61v44TWErCNGF4qzu2nEWyGgPWeNrNpu1FsV8dpump
xitter.cf/reale/status/211311800…


۟ retweeted
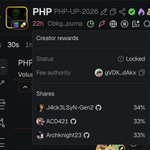
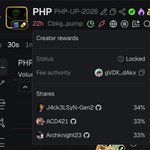
you can claim rewards from solana:Bo61v44TWErCNGF4qzu2nEWyGgPWeNrNpu1FsV8dpump here
pump.fun/coin/Bo61v44TWErCNG…
۟ retweeted
Over 100 solana ~$10K+ sitting unclaimed for you on pumpfun from #PHP2SHELL
Other people are collecting the creator fees off the work you did via non $PHP2SHELL tokens
Claim → stop them from stealing your spotlight
log into pf with github and claim Creator rewards @lcfr_hax

۟ retweeted
Over 100 solana ~$10K+ sitting unclaimed for you on pumpfun from PHP2SHELL
Other people are collecting the creator fees off the work you did via non #PHP2SHELL tokens
Claim → stop them from stealing your spotlight
log into pf with github and claim Creator rewards


۟ retweeted

This is the right one brother! 🫡
@lcfr_hax is the actual guy that discovered the PHP vulnerabilities.
Proof here and fees directed to his GitHub as well: xitter.cf/calif_io/status/211291…
solana:Bo61v44TWErCNGF4qzu2nEWyGgPWeNrNpu1FsV8dpump
Bo61v44TWErCNGF4qzu2nEWyGgPWeNrNpu1FsV8dpump

Let’s set the record straight: @lcfr_hax was the first to discover php2shell and develop a working exploit. See his August 5 tweet: xitter.cf/lcfr_hax/status/208503…
His work convinced the PHP Foundation to invest in fixing this entire bug class. He then worked around the clock to review, test, and retest the patches.
۟ retweeted
This is the RIGHT one for the whole PHP vulnerability! 🫡
@lcfr_hax is the actual guy that discovered the PHP vulnerabilities.
Proof here and fees directed to his GitHub as well: xitter.cf/calif_io/status/211291…
solana:Bo61v44TWErCNGF4qzu2nEWyGgPWeNrNpu1FsV8dpump
Bo61v44TWErCNGF4qzu2nEWyGgPWeNrNpu1FsV8dpump
Let’s set the record straight: @lcfr_hax was the first to discover php2shell and develop a working exploit. See his August 5 tweet: xitter.cf/lcfr_hax/status/208503…
His work convinced the PHP Foundation to invest in fixing this entire bug class. He then worked around the clock to review, test, and retest the patches.

۟ retweeted

and don't worry about feeling obligated to post the ca or anything like that, there's literally no obligation unless you would like to support this project and continue to run it and earn the rewards from trading volume
there's no shame in being rewarded for your hard work

I think it's fair to say that @lcfr_hax should be paid for making everyone aware of this monumental security event
and he did it ethically as well
big onboarding moment for pumpfun
he's crypto native. pumpfun trading rewards from $PHP2SHELL just paid his bug bounty.
People were doubting whether @lcfr_hax GitHub was real.
Here’s the official proof straight from the PHP project
the account linked to the coin is listed as a Reporter on the CVE-2026-109618 advisory (the main PHP2Shell RCE).
Confirmed.

۟ retweeted
People were doubting whether @lcfr_hax GitHub was real.
Here’s the official proof straight from the PHP project
the account linked to the coin is listed as a Reporter on the CVE-2026-109618 advisory (the main PHP2Shell RCE).
Confirmed.

Viral confirmation from one of the most respected in the industry @calif_io “@lcfr_hax was the first to discover php2shell and develop a working exploit… His work convinced the PHP Foundation to invest in fixing this entire bug class.”
xitter.cf/calif_io/status/211291…
People were doubting whether @lcfr_hax GitHub was real.
Here’s the official proof straight from the PHP project
the account linked to the coin is listed as a Reporter on the CVE-2026-109618 advisory (the main PHP2Shell RCE).
Confirmed.
Viral confirmation from one of the most respected in the industry @calif_io “@lcfr_hax was the first to discover php2shell and develop a working exploit… His work convinced the PHP Foundation to invest in fixing this entire bug class.”
xitter.cf/calif_io/status/211291…