

Researcher at @PaloAltoNtwks | CS PhD from @UMich | Security, Privacy, Internet Measurement | Previously: Research Intern @Brave
- Tweets582
- Following677
- Followers510
- Likes2.6K




ALT Two side by side screenshots of phishing sites. The left screenshot features a webpage offering gift cards or a cash prize, with "Congratulations!" in bold and recent comments displayed below. The right screenshot shows a web page with a message encouraging participation in survey offer, with a "Dear Shopper" note. The background features a pegboard with various tools hanging.

ALT The image shows two different online phishing sites. The site on the left mimics a survey completion page, offering rewards such as a gift card. The site on the right displays fake power tool giveaways. Both have suspicious elements and aim to collect personal information.

ALT Screenshot of HTML code structure showing three labeled green boxes containing text. The first box reads "Likely LLM-Generated text about weekend recreational activity," the second reads "Phishing Email Content," and the third reads "Likely LLM-Generated text about a movie." The second box also includes a smaller label "Unique Nonce."


ALT Four browser windows display different web pages. The top left shows a Google Drive page with a "Prove You Are Human" overlay featuring a captcha. The top right shows an error message regarding payment failure on a service site. The bottom left also displays a payment issue notification. The bottom right illustrates a "Subscription Renewal Failed" message with payment details.

ALT The image shows a split-screen of a browser with two pop-up messages. The top section features a "Prove You Are Human" message with a button labeled "Kindly Click Here To Verify." The bottom section shows a "Reminder" alert about increasing device storage with a "Continue" button. A watermark states "Actual Windows too small to accurately discern text in these windows." An arrow labeled "Redirect" connects the two sections.

ALT This image shows a webpage advertising an "April Special" for a VPN service with 80% off, reducing the cost to $9.92 per month. It includes a comparison between yearly and monthly plans, highlighting an "Ultimate VPN" package featuring ad block and online security. A section on the right prompts users to enter shipping information, including name, address, and contact details.

ALT Example of SMS text message from this campaign. This image shows a screenshot of a scam text message pretending to be from T-Mobile. The message informs the recipient about 11,430 reward points expiring on January 2, 2024. It provides a redemption link and instructions to use the T-Mobile app to navigate to "Rewards."

ALT Image shows fake webpage designed to look like a T-Mobile rewards portal. The page has a pink background with T-Mobile's logo and branding. There is a login form asking for email and password information.

ALT This image shows a phishing webpage designed to impersonate a U.S. wireless carrier. The page includes a prominent red banner at the top with the word "Deals" and the phrase "Now we finally know where Santa is." Below is a mock-up of a Verizon member verification page asking for a mobile number to verify and access points. Overlay text indicates this is a phishing example, labeled "Example 2 of 3."

ALT This image shows a phishing web page designed to imitate the branding of AT&T, a U.S. wireless carrier. The top section displays a holiday-themed advertisement with people smiling and taking a selfie. Below, a box titled "Member Verification" prompts users to access exclusive rewards. Text at the bottom labels it as "Example 3 of 3" of phishing pages.

ALT Screenshot of a scam webpage titled "superbowl.best" showing a Sav advertisement at the top. The page lists options in large buttons: "Super Bowl LX on Peacock," "Watch Super Bowl on Peacock," "Stream Super Bowl on Peacock," and "Peacock Subscription for Super Bowl."

ALT Scam webpage for canceling Peacock TC subscription with options to select.

ALT Screenshot of a fake webpage showing a form to cancel a subscription to Peacock. The page includes fields for user information and a pre-written cancellation letter template to Peacock with editable sections highlighted. A navigation menu and browser tabs are visible at the top.

ALT Scam page for 2026 Super Bowl tickets with options to learn more or buy tickets. The background features a blurred image of a football field. A note at the top indicates it is not an official website.

ALT Diagram illustrating the relationship between URLs, IP addresses, and Name Servers. Features networks of interconnected nodes in various colors labeled with URL, hostname, IP address, and Name Server icons, with arrows showing directional flow and text explaining actions such as "Resolves to IP Address" and "Uses Name Server."

ALT Scam document titled "Urgent: W-8BEN Renewal Required" requesting the immediate renewal of a W-8BEN form for U.S. tax law compliance, emphasizing confidentiality, safety, and mandatory action for all non-U.S. residents.

ALT An scam letter from the IRS detailing compliance with regulations and submission processes.

ALT Promotional email featuring a Louis Vuitton handbag on a plain background, with an offer stating "Discover Timeless Luxury - Louis Vuitton Bags Starting at Just $200." The button below invites to "Shop at $200."

ALT Screenshot of the On Running website featuring a product page for Beige On Cloudvander Waterproof Shoes. A login pop-up window is displayed in the center with fields for Email Address and Password, and a Login button.

ALT Screenshot of the Black Friday Daily Deal website homepage featuring a promotional banner for daily discounts with an option to sign up for email alerts.


ALT Screenshot showing two email interfaces. The left interface displays a message about secure messages and pending messages due for delivery. The right interface shows an open spam folder with multiple messages and options.

ALT Two screenshots displaying webmail login pages. The left screenshot shows a login error message on the login page, while the right screenshot displays a simple webmail login interface with fields for email address and password.

ALT Pictorial representation of a smishing scam. A smartphone displaying a scam message with a vibrant digital interface background.


ALT Screenshot of an email tagged as an example of a phishing email, with the subject 'RE: Proforma Invoice' from a sender with an email address ending in 'proexcel dot com dot ph'. The email contains a suspicious attachment named 'Proforma Invoice dot pdf dot html', and a download prompt window from Mozilla Thunderbird is visible.

ALT Screenshot of an HTML file viewed from the Thunderbird dialog window, displaying a Cytiva order confirmation dialogue and an Excel password prompt to prevent unauthorized access. The email address is redacted.

ALT Screenshot of a Notepad++ document showing HTML code for a fake Proforma invoice form. Highlighted portions include the web form submission URL, the recipient's email address (redacted), the empty password field, and the submit button.

ALT An example of an HTML attachment for a phishing page, displaying a fake shipment arrival notification email asking to confirm email addresses to download information.

ALT Bar chart displaying the number of domains created on specific dates according to WHOIS. The dates range from August 2024 to September 2025, with a peak of 584 domains in June of 2025.

ALT Screenshot collage of three text messages. From left to right: One spoofing "FedEx" mentioning a delivery update, another spoofing the California "Franchise Tax Board" concerning a tax document, and a third spoofing the "IRS" about a tax refund. Each message preview includes a brief explanation or action required, with unread message indicators. The group name (a series of numbers) is circled in each message, along with the sender phone number.

ALT Two screenshots of text messages spoofing FedEx. The left screenshot shows a delivery rescheduling notification. The right screenshot shows a delivery failure notification, indicating the package was undeliverable and returned.

ALT Screenshot collage showing the fake Amazon JP captcha page. This leads to the cloaking by redirection and a URL that resembles Amazon. Ultimately this process leads to obfuscating and potential geotargeting.

ALT Comparison screenshots of a fake message from Amazon, alerting the recipient about payment verifications required for an order due to suspicious activities detected from different regions. The email includes detailed instructions on how to secure the account and verify the payment. Google Translate was used to translate the email.

ALT Screenshot of spoofed email for Amazon.co.jp, featuring a call to action button.

ALT Diagram explaining the latest evolution in this phishing campaign. Diagram includes an icon key with URLs, file/sample hashes, hostnames and IP addresses. Clusters include subdomain relations, IP address resolutions, and redirects.

ALT Bar chart showing domain registrations related to the FIFA 2025 World Cup, from January 2024 to August 2025. The number of domains increases over time, with a significant spike in August 2025 reaching 1904 registrations.

ALT Screenshot of a fake tickets sales website interface for the FIFA World Cup 2026, displaying various match options with ticket prices, a shopping cart summary, and a chat support option.

ALT Screenshot showing various betting websites, including 'PlanetBet' and 'World Cup Betting Odds', displaying promotional graphics and information on sports betting options.

ALT A screenshot of a website named displaying a download prompt for a file named for an APK file with options to open or save the file, under the heading "ANDROID APPLICATION DISTRIBUTION."

ALT Two examples of recent text messages from this campaign. Image displaying two text messages spoofing the California Franchise Tax Board, communicating updates and requirements regarding personal income tax.
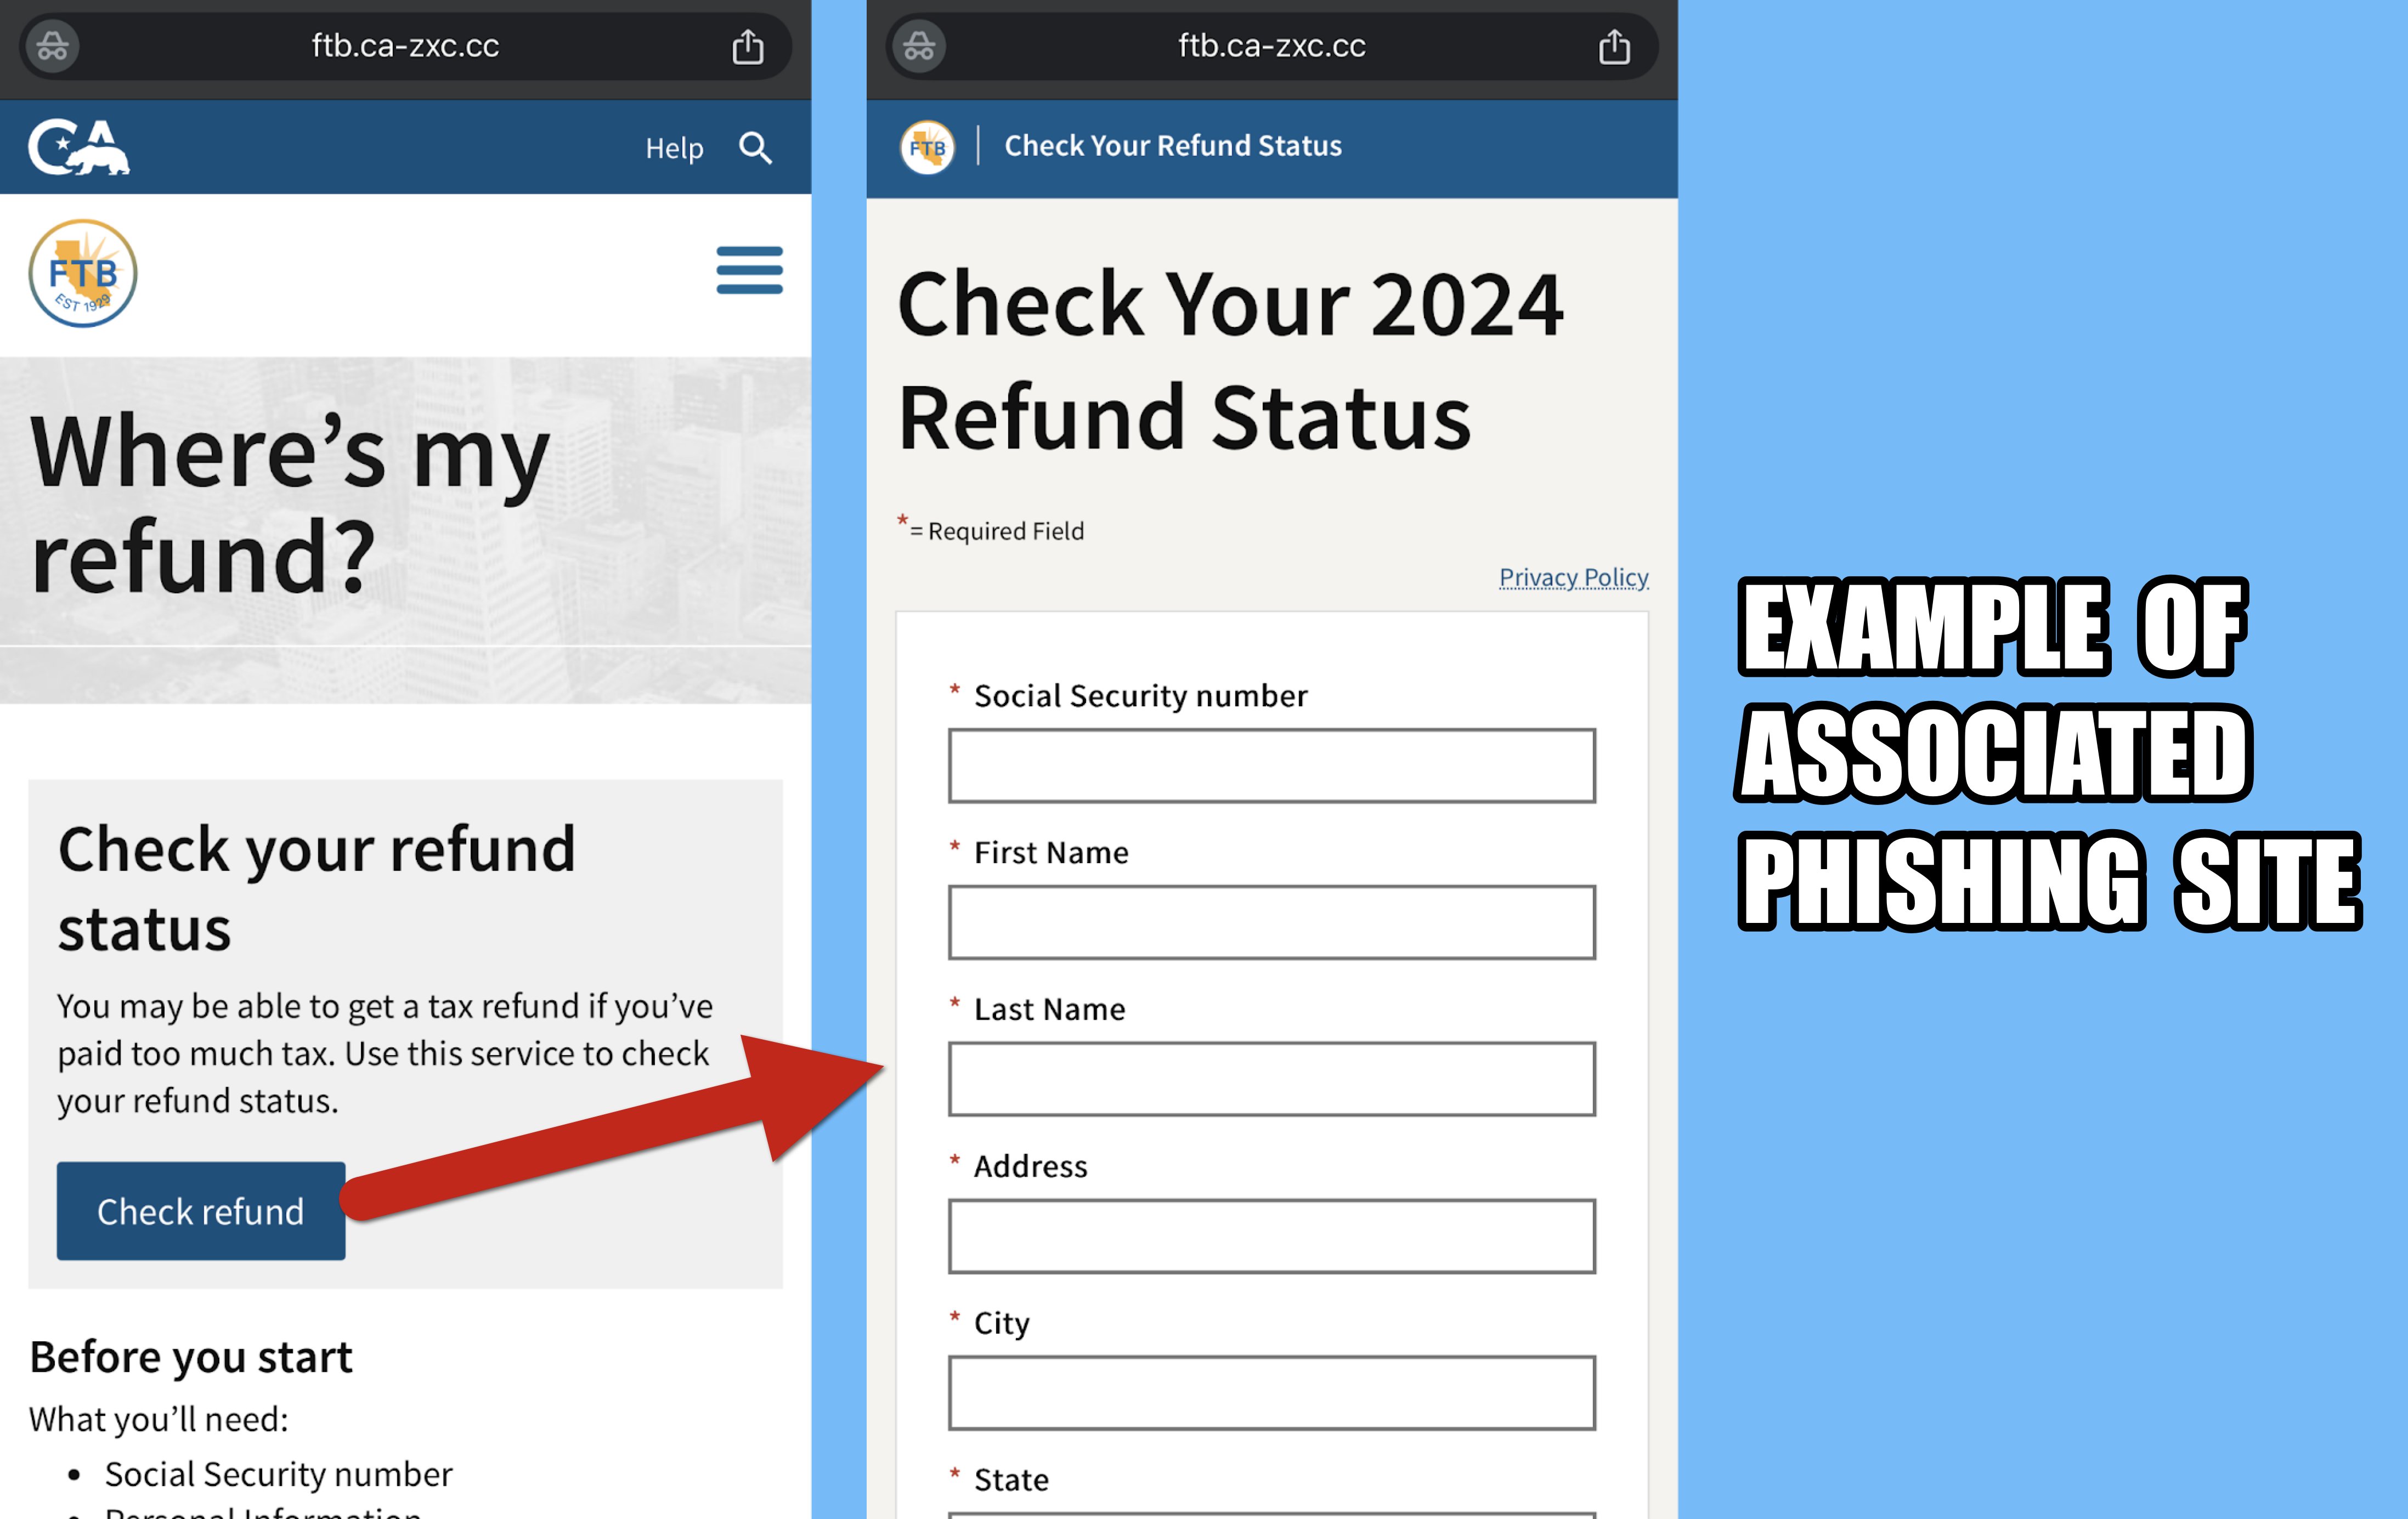
ALT Example of associated phishing site. Screenshot of a phishing website impersonating the official California Franchise Tax Board site, displaying a form requesting sensitive information such as Social Security number and last name.

ALT Screenshot of an example phishing email featuring an advertisement for Rolex watches, with a starting price mentioned as $250. A large image of a Rolex Deepsea wristwatch is prominently displayed.

ALT Screenshot collage featuring examples of websites involved in spoofing luxury goods, including one depicting luxury watches and another showing a payment page for an online store.

ALT Example of two invoices for service orders from displaying various information such as invoice numbers, dates, company logo, service descriptions, quantities, and pricing details in USD. The QR codes are redacted.

ALT Line graph showing normalized passive DNS traffic volume for a Luxury Shop Fraud Campaign from May 28th to August 21st, 2025. The graph peaks dramatically on July 17th, 2025.

ALT An example of a phishing webpage designed to imitate the official Telegram login page, misleadingly prompting for phone number verification.

ALT Screenshot of a Telegram web browser tab showing a phone number confirmation page with a network inspector tool open on the side, highlighting web traffic details.

ALT Chinese characters in JavaScript code from phishing site. Chinese characters that translate to "no data." Screenshot showing the DevTools panel in a browser with JavaScript code from a phishing site, highlighted sections indicating malicious activity and translations.

ALT Bar chart showing the number of domains registered per month from January 1st to June 24th, 2025. The data points for each month from January to June are respectively: 5,621, 13,510, 16,148, 7,599, 6,233, and 3,501.

ALT A screenshot collage where the top section is screenshots of pages leading to link redirects. The directs land on blocking pages for visits from unwanted countries. A red box highlights a promotion to install the app. The bottom half of the screenshot is a detailed cybersecurity network graph showing various connections between elements such as URLs, IPs, and domain names, illustrating how data flows and potential security threats are mapped in a network.

ALT Line graph showing normalized traffic volume over days after registration, with annotations indicating a drop in traffic as the domain ages and a significant decline to inactivity one year after registration.

ALT Bar graph displaying the number of domains created each month from January 2024 to May 2025. The y-axis shows the number of domains ranging from 0 to 200, and the x-axis lists each month. The highest peak occurs in April 2025 with 163 domains.

ALT Screenshot of active Telegram channel with translations from Cyrillic. The conversation discusses no money after some time has passed, asking if there has been a withdrawal, contacting support and then directing the asker to wait.


ALT Bar chart showing WHOIS creation dates for smishing domains, with the number of domains registered on the vertical axis and the date on the horizontal axis. The chart displays periodic spikes in domain registrations over time.

ALT Line graph showing normalized traffic volume over time, from October 2024 to April 2025, with noticeable peaks in traffic volume, particularly in early 2025.

ALT Four mobile screenshots displaying various online services: for different US states' toll payment services, and USPS package tracking. Each site features navigation options and relevant vehicle or service imagery. All sites are scam/spoof domains.
ALT Bar chart showing WHOIS creation dates for smishing domains, with the number of domains registered on the vertical axis and the date on the horizontal axis. The chart displays periodic spikes in domain registrations over time.
ALT Line graph showing normalized traffic volume over time, from October 2024 to April 2025, with noticeable peaks in traffic volume, particularly in early 2025.
ALT Four mobile screenshots displaying various online services: for different US states' toll payment services, and USPS package tracking. Each site features navigation options and relevant vehicle or service imagery. All sites are scam/spoof domains.