

Abliterated models available via OpenAI-compatible API. No KYC and no gated access.
United States
Joined October 2026
- Tweets144
- Following33
- Followers2K
- Likes79




⚠️ UPDATE YOUR PHP SITES NOW!!
Patched versions here
php.net/index.php

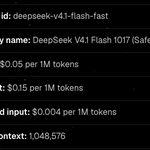
Introducing DeepSeek v4.1 Flash 1017 Abliterated.
At the same price of the previous version, with a temporary 67% discount.
From our early tests, this model is a substantial improvement from the previous 4.1 Flash. It performs much better at Cybersecurity and coding tasks
🤖 Made with AI

❗️ php2shell is a very serious vulnerability affecting MOST OF THE WEB.
Our GLM 5.3 Abliterated was able to reproduce the exact vulnerability in 30 minutes.
While waiting the official PHP fix, we recommend to turn off session.upload_progress.enabled in the php.ini settings. Should help mitigate some of the dangers although not all.
Refuseless retweeted

It looks like a public PHP exploit was just leaked on GitHub. But GLM 5.3 could easily build it
I used @refuselessai glm 5.3 and DeepSeek and easily got an working exploit in 30 minutes. I think it's over for cybersecurity
There was a problem with the mail provider due to abuse of the free promo
If you had issues getting the verification email, try now! 🙂
DeepSeek V4.1 Flash 1017 is now FREE on Refuseless.com 🎉
Once the free allowance runs out, you still get below-market rates.
Heads up: this is the safeguarded version.
The abliterated one is coming soon.

Chinese models ranked by cyber and pentesting capabilities, from personal experience.
GLM has done something special

Refuseless — The privacy hub for unrestricted AI.
Serving GLM 5.3 Abliterated & Qwen3.8 Abliterated
• Zero retention. No logs.
• Crypto & XMR accepted


When the weights of Qwen4 will be dropped, we will host an abliterated version and serve it for FREE
Follow us to avoid missing out

The same prompt tested on Claude Opus 5.5 was immediately blocked by Safeguards.

Here's GLM 5.3 abliterated explaining the network protections that modern Linux kernels are equipped with and how/if they can be bypassed.
If you are into cybersecurity, this model is a game changer.
We offer it via API on Refuseless.com with zero prompt retention.
