

💉 Web & Mobile Penetration tester | OSWE | OSCP+ | 🐞 Bug Hunter | 🛡 Synack Red Team Member
pwd
Joined October 2017
- Tweets738
- Following636
- Followers464
- Likes2.7K





Pinned Tweet
Here is writeup for an interesting Account takeover vulnerability.
#bugbounty #bugbountytip #TogetherWeHitHarder
medium.com/@sakyb7/tale-of-a…

कर्नाटक के रहने वाली दो बहने जिन्होंने अपने हाथों से सौईओर धागे के मदद स... youtube.com/shorts/gmC0A6v7F… via @YouTube

23
Saqib Chand 🇵🇸 retweeted

RFC 2047 "encoded-word" is so cool!
It lets you smuggle encoded payloads into email addresses and the craziest thing is that some parsers decode it before validation 👇
Shout out to @garethheyes for this 🔥
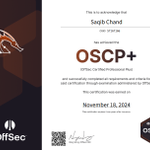
🎉 Happy to share that I have successfully passed the OSWE (Offensive Security Web Expert) certification by OffSec!
It has been a challenging but rewarding journey filled with learning, problem-solving, and hands-on experience in web application security.

98
Saqib Chand 🇵🇸 retweeted

I built something a little crazy for India 🇮🇳
Pay ₹25. Pick your spot. Climb the leaderboard. 🏆
Rank your website, product, or social profile — the more you bid, the higher you rank.
No subscriptions. No ad campaigns. Just a public leaderboard.
👉 2rupeespeople.lol�


Saqib Chand 🇵🇸 retweeted

I’ve added here
github.com/orwagodfather/XSS…
PDF file for XSS, it can bypass any waf
for who looking for Stored XSS , and it can be changed to blind if you want to
Simply I encoded the payload as ASCII hex
You can edit the payload over notepad++
#bugbountytips #bugbountytip #bugbounty

Saqib Chand 🇵🇸 retweeted

JAVASCRIPT IS A GOLDMINE FOR #BugBounty HUNTERS
youtube.com/playlist?list=PL…
Check out my playlist to learn how <3 treat yoselfff rats is freeeee

Saqib Chand 🇵🇸 retweeted

This is a great resource on Prompt Injection.
Huge thanks @rez0__!
github.com/jthack/PIPE

Saqib Chand 🇵🇸 retweeted
How to grab subs for a target using subfinder, validate them and extract the text body from each response using httpx and jq, extract a wordlist of keywords using NLP then resolve them using puredns to find valid subdomains 👇
You can also use LLMs and tools like alterx to generate a list of permutations from the extracted wordlist!
Saqib Chand 🇵🇸 retweeted

❌GraphQL introspection disabled?
✅No problem! Extract all GraphQL operations from Javascript files!
1. go install github.com/rashahacks/jsmon-…
2. Scan the JS URL with -u flag.
🚀View all the GraphQL operations in seconds -- no introspection needed.
Saqib Chand 🇵🇸 retweeted
If you’re not Jewish but you support Israel
Congrats
You’re one of the dumbest and most gullible motherfuckers on the planet.
Saqib Chand 🇵🇸 retweeted

$20,300 Bounties from a 200 Hour Hacking Challenge
Credit: Mohammad Zaheri
.
.
.
.
.
.
#bugbountytips #bughunting #infosec
blog.voorivex.team/20300-bou…

Saqib Chand 🇵🇸 retweeted

How we gained full control over 3,000 companies and all their registered branches.
This took us about 3 weeks of studying the target to find about all the vulnerabilities explained.
Hope you enjoy reading!
link.medium.com/rmRjR6udwQb

Saqib Chand 🇵🇸 retweeted
Hello everyone ♥
a little bit write-up of #bugbountytip #bugbountytips I am going to write here .....
Title:
getting unauthorized access on 3rd party's/workspaces & and building your checklist for quickly locating bugs there via massive recon
we know that its helpful to look for google
groups/docs/etc..
Slack as well just like when the amazing @h4x0r_dz shared days ago ..
Use google dork "site:join.slack.com"
so I was not in a good mode the last months to doing Google Dorks, so what I did was build a checklist ready for me & very huge one
for EX:
groups.google.com
docs.google.com
join.slack.com
and here is just an example you can add more similar workspaces for your checklist
thin I extracted all internet endpoints and as example here join[.]slack[.]com
otx.alienvault.com/api/v1/in…
virustotal.com/vtapi/v2/doma…
web.archive.org/cdx/search/c…
you can use the ready tools to do it such as waymore
important note: you have to keep your checklist updated every week
and from here I just keep looking for the company name or domain name to see if there's anything connected
and mostly the company name or domain name in the URL it self EX: tesla
join.slack.com/t/Tesla-Inter…
Ex For Bugs found:
1 unauthorized access to the workspaces
(PII | Information disclose)
2 account takeover as Ex: valid signup employee link
3 account takeover as Ex: valid reset password employee link
now about Slack, as an example if you found an invitation link for tesla
Tesla join.slack.com/t/Tesla-Inter… and that link was not valid, don't stop here
it will redirect for Ex:
tesla-internal[.]slack[.]com
here back and start looking manually for endpoints of this subdomain as well EX:
web.archive.org/cdx/search/c…
now there are a lot of 3rd party's/workspaces I just shared here
slack & Google Docs/groups
What I wrote is a bit long and annoying to some, so I apologize. I hope, as usual, that this will be useful to all who follow me here.
#Bugounty
don't forget to retweet if you like it ♥♥♥


Saqib Chand 🇵🇸 retweeted

Read further: synack.com/blog/path-travers…

Saqib Chand 🇵🇸 retweeted

Got 2FA? Here are 13 ways to test its security.
nccgroup.com/us/research-blo…
Saqib Chand 🇵🇸 retweeted

Our talk was accepted at @defcon this summer! Come watch @LennertWo and I give a talk about the Unsaflok vulnerability in hotel locks and the technical details behind it.
unsaflok.com

Saqib Chand 🇵🇸 retweeted

How I reverse-engineered an Android app, bypassed custom encryption layer, achieved server-side RCE, and earned a $5000 bounty. read the full story here (TLDR; but worth reading)
blog.voorivex.team/from-an-a…

Saqib Chand 🇵🇸 retweeted

🧵Can you work out how to bypass this vulnerable CSRF protection? Read all about this gotcha in my latest blog post

Saqib Chand 🇵🇸 retweeted

🚀Black Friday Giveaway!🤗
*** 𝗙𝗼𝗹𝗹𝗼𝘄 𝗼𝘂𝗿 𝗽𝗮𝗴𝗲, 𝗥𝗲𝗽𝗼𝘀𝘁, 𝗟𝗶𝗸𝗲 𝗮𝗻𝗱 𝗖𝗼𝗺𝗺𝗲𝗻𝘁 𝘄𝗵𝗶𝗰𝗵 𝗲𝘅𝗮𝗺 𝘆𝗼𝘂 𝘄𝗼𝘂𝗹𝗱 𝗹𝗶𝗸𝗲 𝘁𝗼 𝘄𝗶𝗻 𝗮𝗻𝗱 𝟱 𝗹𝘂𝗰𝗸𝘆 𝘄𝗶𝗻𝗻𝗲𝗿𝘀 𝘄𝗶𝗹𝗹 𝗴𝗲𝘁 𝗮 𝗳𝗿𝗲𝗲 𝗲𝘅𝗮𝗺 𝗼𝗳 𝘁𝗵𝗲𝗶𝗿 𝗰𝗵𝗼𝗶𝗰𝗲! ***
Get started here and select the exam of your choice😎: secops.group/pentesting-exam…
#blackfridayoffer #infosecblackfriday #pentestingexams #appsecexam #networksecurity #giveaways
