
CTO and Co-Founder of OpenMake Software. He has more than 20 years of experience in application development, specializing in build and release management.
Santa Fe, NM
Joined May 2016
- Tweets276
- Following28
- Followers69
- Likes91



Steve Taylor retweeted

Seems as though GoTo may be trying to fly below the radar with messaging about the LastPass breach.
Check out this report and other segments at
505updates.com/december-6-20…
#passwordmanagement #lastpass #its505
#cybersecurity #opensource
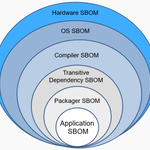
Our team has been working to incorporate SBOM Aggregation into DeployHub and Ortelius. I've collected together a few thoughts on #softwaresupplychain, and the different levels of SBOMs needed. Happily working with the @theopenssf and @linuxfoundation
ow.ly/VJ6O50J5qNP

1
Steve Taylor retweeted

It's a great feeling to be able to host in-person events again and connect with our community!! Thank you to all who attended the @owasp Bay Area meet up last night and the amazing Frogs who made it possible.
@williammanning @ariwaller @sudhindraRao @pearlyscript

“Demystifying SBOM’s impact on secure Software Deployment” with our own Frog @williammanning in collaboration with #OWASP Bay Area. We are back to in person meetups 💪🐸


Here is an excerpt from a recent demo I did on microservice producers, consumers, and endpoint tracking. A common topic I'm asked about. youtu.be/QULij0twZms

Here is an excerpt from a recent demo I did on microservice producers, consumers, and endpoint tracking. A common topic I'm asked about. youtu.be/QULij0twZms

Steve Taylor retweeted

#CVE20220492 is a new privilege escalation and container escape vulnerability that affects the #Linux kernel.We have added a dedicated control to #Kubescape under the ARMOBest framework that scans and detects if your #K8s are affected.
hubs.la/Q015D_rv0

Steve Taylor retweeted
Securing your #softwaresupplychain is absolutely critical as attackers become more sophisticated. Join us for a technical showcase of the malicious packages most prevalent today. #DevSecOps
- Wed., Mar. 9 at 11am PT/2pm ET
- Wed., Mar. 16 at 11am CET
jfrog.co/3sNX7XN

Steve Taylor retweeted
There are a lot of reactive frameworks in the field, some with functional languages for the #JVM. However, #Java gives you both.
Join Sven Ruppert on Wed., Mar. 9 at 5:30pm CET to explore the possibilities of Core #JDK. Register here: jfrog.co/35IbJPz
#Developers #DevOps

Building out your #Kubernetes stack - nice job Eduardo Munari. medium.com/@munari.edu/insta…

Steve Taylor retweeted
The autoscaling #cloud computer strategy allows us to dynamically adjust compute resources instead of responding manually. However, this approach is not without its drawbacks.
Here's how to customize JFrog #Xray's autoscaling using custom metrics: jfrog.co/36Q9CcJ

Here is an excerpt from a recent demo I did on microservice producers, consumers, and endpoint tracking. A common topic I'm asked about. youtu.be/QULij0twZms

Steve Taylor retweeted

Learn about #Operators and #ServiceMesh with Sergio Canales, Architect @Redhat @Iarwain_BenAdar youtu.be/r-Gj1mIBR5Q

Steve Taylor retweeted
Modern, large-scale, mission-critical networks demand drastically different architecture, power and feature optimization at every layer and touch point. Don’t compromise. Choose the best architecture for your use case, and optimize. Read it in the blog: https://teapaw.org/t.co/D0N9r5aqRY
Steve Taylor retweeted

If you /just/ want append-only, then something like what en.wikipedia.org/wiki/Certif… implemented is probably fine. But if you want some rules to govern what's allowed to be logged (akin to stored procedures in databases), then #hyperledger Fabric is an excellent choice.
Steve Taylor retweeted
Want to learn how to contribute to the Ortelius Open Source project. @codeWithUtkarsh shows us how, step by step. youtu.be/Y4kR6ipipxA

As a person who manages the @orteliusOS project, I know from personal experience how important this is. sdtimes.com/os/open-source-i…
Calculating a 'criticality score'- Generate a criticality score for OS project. Get list of critical projects that the community depends on. Proactively improve the security. The @orteliusos project can follow suit for microservices. @theopenssf github.com/ossf/criticality_…

1
If you want to learn more about the Log4J vulnerability, here is a great read. security.googleblog.com/2021…

New Projects at @theopenssf - Alpha Project will focus on securing the top 100 open source software packages. Omega will cast a broader net. 2022 will be a busy year for this new @linuxfoundation organization.

2
GitHub expands code scanning capabilities with 3rd party tooling and developer security training.
github.blog/2020-10-05-annou…
