

I'm just an eight ulcer man on four ulcer pay.
½ way btwn d gutter & d stars
Joined December 2006
- Tweets365K
- Following2.8K
- Followers20.7K
- Likes35.2K




That Goan Guy retweeted

爆了!!!NVIDIA RTX 20、30、40 三代显卡的隐藏 AI 算力,居然都被民间大神破解了!!!🤯
老黄锁了这么多年的 Tensor Core 算力,居然被人直接解锁了,部分显卡的计算吞吐量甚至原地翻倍!
而且最离谱的是,不需要更换硬件,不用刷 BIOS,也不用魔改 NVIDIA 官方驱动。
直接从底层解除部分 Tensor Core 运算的性能限制。
目前社区已经公布了多个型号的测试结果:
🔹 RTX 4090:165.6 → 331.6 TFLOPS,直接翻倍!
🔹 RTX 3090 Ti:BF16 从 87.5 → 157.4 TFLOPS,暴涨 80%!
🔹 RTX 2080 Ti:特定 FP16 运算吞吐量接近翻倍!
🔹 RTX 4070 Ti SUPER:FP16/BF16 运算吞吐量也接近翻倍!
甚至连 Windows 11 上都已经有人成功复现了。
要知道,RTX 2080 Ti 已经是八年前的显卡了,结果到了 2026 年,居然还有人能从里面挖出这么多计算能力。
更魔幻的是,现在连开源项目和安装教程都有了。
不同系列有对应的解锁项目:
🔥 RTX 20 系列(Turing)
github.com/nlzy/turing-unloc…
🔥 RTX 30 系列(Ampere)
github.com/Zagitta/gpu-unloc…
🔥 RTX 40 系列(Ada)
github.com/JustAResearcher/g…
🔥 Windows 11 实验方案(改装版 RTX 4080)
huggingface.co/TOTORONG/AD10…
还有中文安装说明:
gpu-unlock.com/zh
Linux 用户按照对应仓库的教程,安装内核模块、配置启动参数,再通过冷启动触发解锁。
NVIDIA 靠着精准的产品刀法卖了这么多年显卡,结果 GitHub 上的民间大神,硬生生把老黄的刀给撅了。
谁能想到,一张用了七八年的老显卡,居然还能在 2026 年迎来这种级别的算力解锁。

That Goan Guy retweeted

And just like that,
We have windows gpu unlock
github.com/impacifist/Window…


That Goan Guy retweeted

CleanYourTV 3.0 is here 📺
Your TV can now:
• Show your Home Assistant lights and locks
• Pause your Pi-hole from the couch
• Get cleaned from your phone, no laptop needed
• Turn any remote button into a shortcut
Plus 52 new TVs and 28 languages, from 169 contributors 🙏


That Goan Guy retweeted

eMudhra has apologized over weak keys affecting eight emSign G3 intermediate certificate authorities, attributing the problem to a script error. In its October 26 update, the company says it is commissioning an independent expert review and will publish a full root-cause analysis through CCADB. The company says its investigation has found no compromise of infrastructure or customer data. The independent review and detailed findings remain pending.
emudhra.com/en/post/certific…
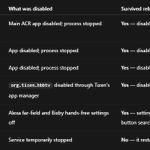
This is what your Samsung TV services should look like after you're done disabling the spyware. Now I just need to figure out how to stop the advertising agent.


That Goan Guy retweeted

announcing samshush: an agent-first toolkit designed to disable the questionable services on your Samsung smart TV.
Microphone/listening services, adware, spyware, telemetry, presence detection & eMudhra roots are cleaned up or disabled.

Ok, I just checked this, and its literally running a freaking TensorFlow Lite model on 960×540 images with INT8 quantization every couple of seconds in an attempt to figure out what game you are playing.
It's literally called "alex.tflite" and its literally AlexNet and seems to follow torchvision.models.alexnet. As far as I can tell this does some strange nearest neighbor feature comparisons against a DB and literally doesn't work 99% of the time, you love to see your CPU get wasted every other second by this thing though. It also just seems to dump its results into the void because the consent gate comes later.
Anyways, here's the tf model graph and some dumped captures.


That Goan Guy retweeted

Hisense now allegedly breached.
No login needed for samples either.
Not a good week for security.
Good luck.


That Goan Guy retweeted

Speaking of the devil, now it's Tailscale's turn 😂
Go to tailworm.com/ to check your setup

‼️ Tailscale SSH Flaws Could Let Hackers Gain Root Access Across Servers
Details: cybersecuritynews.com/tailsc…
A new security report warns that Tailscale SSH has flaws that could let a hacker move from one compromised device to root access on other servers. Tailscale SSH lets approved devices log in to each other over a private network. The report lists 11 findings in five groups.
They cover Tailscale’s SSH server, its serve and app connector features, the DERP relay client, and headscale, an open-source server that manages Tailscale networks.
The researcher tested Tailscale 1.104.2 and headscale 0.29.5 between October 22 and October 24, 2026. The most serious group involves Tailscale SSH. Its SSH server runs inside tailscaled, a background program with full root privileges on the machine.
#cybersecuritynews

Readers added context they thought people might want to know
The flaws require an already-approved device in the Tailscale network with SSH rules permitting access/forwarding; they enable post-compromise lateral movement and escalation inside the tailnet, not unauthenticated remote access from outside.
tailworm.com
brandefense.io/security-news/…
tailscale.com/security-bulle…
x.com/mmaunder/statu…

That Goan Guy retweeted

YOU'RE BORN. YOU SEE PANTS STYLES GO FROM BAGGY TO SKINNY BACK TO BAGGY EVERY 10 YEARS FOR THE REST OF YOUR LIFE. YOU DIE. THE END
That Goan Guy retweeted

⚠️🚨 THIS IS NOT A DRILL 🚨⚠️
Google has officially declared a bug in Brotli, its tool that shrinks web traffic, CRITICAL: 9.2 out of 10. Last night "Node2Shell" evolved into HTTP2SHELL.
A formal CVE record has been issued citing CVE-2026-111497 -- a hole in versions 1.0.3 to 1.2.0 that can hit any app unpacking data from strangers, and could let them take it over.
What this means:
▪️ This is not a Node.js problem anymore. This is an HTTP PROBLEM.
▪️ Every unpatched app across Node.js, Python, Bun, and Envoy that unpacks Brotli now has a hole attackers need no login to use
▪️ Istio. curl. Python's requests and httpx. All at risk under one CVE.
▪️ EVERY project that bundles Brotli must ship its own fix, and not all are out yet
This changes everything.
A normal bug can be fixed in one place.
A 9.2 bug inside a shared tool cannot.
We just entered the most dangerous phase of this crisis. If you're not paying attention - start now.
Save this. Share this. This is the moment it escalated beyond return.
That Goan Guy retweeted

‼️ The tracking server for VIDAA smart TVs, the system on Hisense sets, needed no login.
In 3 hours, Northeastern researchers pulled 57M+ records of what 1M+ TVs were watching, sorted into categories like religion and politics.


That Goan Guy retweeted

This is what Crome saying “this is your last opportunity to fix the mess you’ve created, else you’re out.”
Pretty clear they will be out.
We’re talking about an eng team unable or unwilling to run a RCA and publish it, when everyone assumed they could
bugzilla.mozilla.org/show_bu…


