

Try to keep up! BREAKING & up to the minute #news, #cybersecurity tips and #technology best practices. Visit website for more at https://xitter.cf/t.co/tYGWm5L3hE
255.255.255.255
Joined December 2011
- Tweets296K
- Following1.7K
- Followers19.1K
- Likes302



Pinned Tweet
Breaking into cybersecurity shouldn’t feel this confusing.
But for most people, it does.
Too much noise.
Too much theory.
Not enough real guidance you can actually use.
So we built Secguro 👉 secguro.com
A place for people transitioning into cyber or leveling up to find practical, no-fluff security knowledge they can apply immediately.
No gatekeeping.
No overcomplication.
Just clarity.
If you’re trying to break into cybersecurity, check it out.
What’s been the hardest part of your transition so far?
#cybersecurity #infosec #cybersecuritytraining #careergrowth #technology

𝗛𝘂𝗺𝗮𝗻 𝗙𝗶𝗿𝗲𝘄𝗮𝗹𝗹 retweeted

Microsoft Teams to get AI-powered, context-aware phishing detection
bleepingcomputer.com/news/mi…
bleepingcomputer.com/news/mi…

𝗛𝘂𝗺𝗮𝗻 𝗙𝗶𝗿𝗲𝘄𝗮𝗹𝗹 retweeted

‼️ Palo Alto Confirms PHP RCE Vulnerabilities Impact PAN-OS and Multiple Network Products
Details: cybersecuritynews.com/palo-a…
Palo Alto Networks has confirmed that two critical PHP remote code execution vulnerabilities affect PAN-OS and previously impacted two cloud services. Tracked as CVE-2026-109618 and CVE-2026-109619, the flaws have prompted planned firewall hotfixes and guidance to restrict access to management interfaces.
The company updated its security advisory on October 24, 2026. It said it was not aware of malicious exploitation against its products. However, Unit 42 has seen proof-of-concept exploits for the wider PHP vulnerabilities, known as PHP2Shell.
#cybersecuritynews

𝗛𝘂𝗺𝗮𝗻 𝗙𝗶𝗿𝗲𝘄𝗮𝗹𝗹 retweeted

‼️ Attackers are exploiting a critical Fortinet FortiSIEM flaw that lets them run code without logging in, Canada's Cyber Centre says.
Horizon3 released an exploit for CVE-2026-106173 on Oct 20. Version 7.5.1 fixes it.
Fortinet still lists the flaw as not known to be exploited.


𝗛𝘂𝗺𝗮𝗻 𝗙𝗶𝗿𝗲𝘄𝗮𝗹𝗹 retweeted
Capcom confirms data breach affecting 11.7 million accounts
bleepingcomputer.com/news/se…
bleepingcomputer.com/news/se…

𝗛𝘂𝗺𝗮𝗻 𝗙𝗶𝗿𝗲𝘄𝗮𝗹𝗹 retweeted

🚨 PHP warns of another unpatched remote code execution risk; CVE-2026-115560
The newly disclosed vulnerability is separate from the two PHP2Shell flaws patched earlier this week and is not fixed by PHP 8.5.12, 8.4.27, 8.3.36 or 8.2.35.
⠀
PHP says exploitation requires an unusual configuration where an application:
• Uses php_binary or php_serialize as its session serializer
• Changes the serializer to php at runtime before session_start()
• Has session upload progress enabled
⠀
PHP considers the risk unlikely and plans to release a fix during its next regular update cycle.
Until then, administrators with affected configurations should set:
session.upload_progress.enabled=0
Applications that do not change the session serializer at runtime are not exposed through this path.
No exploitation has been reported.
Source:
php.net/

𝗛𝘂𝗺𝗮𝗻 𝗙𝗶𝗿𝗲𝘄𝗮𝗹𝗹 retweeted

‼️ FOUR critical GitLab RCE flaws traced back to just THREE bugs in Ruby's regex engine.
Ruby has now fixed them, but this isn't just a GitLab issue.
Other Ruby apps that compile attacker-controlled regex patterns are also affected.
Details ➜ thehackernews.com/2026/10/ru…

𝗛𝘂𝗺𝗮𝗻 𝗙𝗶𝗿𝗲𝘄𝗮𝗹𝗹 retweeted
‼️ BREAKING: Oracle Issues Emergency Java Update for Critical 9.1 HTTPS Trust Vulnerability
Details: cybersecuritynews.com/emerge…
Oracle has released an emergency Java security update to address CVE-2026-91403, a critical vulnerability affecting how Java applications trust digital certificates. Published on October 21, 2026, the alert assigns the flaw a CVSS 3.1 score of 9.1 and covers Oracle Java SE and GraalVM.
The update blocks affected intermediate certificate authority certificates linked to eMudhra. According to Oracle’s security advisory, the issue affects the Java Secure Socket Extension, or JSSE, component.
Oracle rates exploitation as low complexity, with no authentication or user interaction required. Successful attacks can expose or change sensitive data, although the risk matrix lists no availability impact.
#cybersecuritynews #vulnerability

𝗛𝘂𝗺𝗮𝗻 𝗙𝗶𝗿𝗲𝘄𝗮𝗹𝗹 retweeted
PHP shares mitigation for new RCE vulnerability with no patch
bleepingcomputer.com/news/se…
bleepingcomputer.com/news/se…

𝗛𝘂𝗺𝗮𝗻 𝗙𝗶𝗿𝗲𝘄𝗮𝗹𝗹 retweeted
🚨 Exposed infrastructure reveals how ransomware affiliates used AI to hack networks and steal data.
8,257 messages. 133 AI sessions. 62 organizations targeted.
Operators exploited Fortinet, SimpleHelp, and cPanel flaws.
Inside the operation ↓ thehackernews.com/2026/10/ex…

𝗛𝘂𝗺𝗮𝗻 𝗙𝗶𝗿𝗲𝘄𝗮𝗹𝗹 retweeted
‼️ Palo Alto firewall VMs and Citrix NetScaler run without ASLR, a basic memory defence, Kevin Beaumont says.
He warns that makes the PHP2Shell flaws trivial to exploit through internet-facing management interfaces.
Neither has a patch out. Citrix promises one on 27 October.


𝗛𝘂𝗺𝗮𝗻 𝗙𝗶𝗿𝗲𝘄𝗮𝗹𝗹 retweeted
Abandoned Popcorn Time app exposed millions of device to RCE attacks
bleepingcomputer.com/news/se…
bleepingcomputer.com/news/se…

𝗛𝘂𝗺𝗮𝗻 𝗙𝗶𝗿𝗲𝘄𝗮𝗹𝗹 retweeted
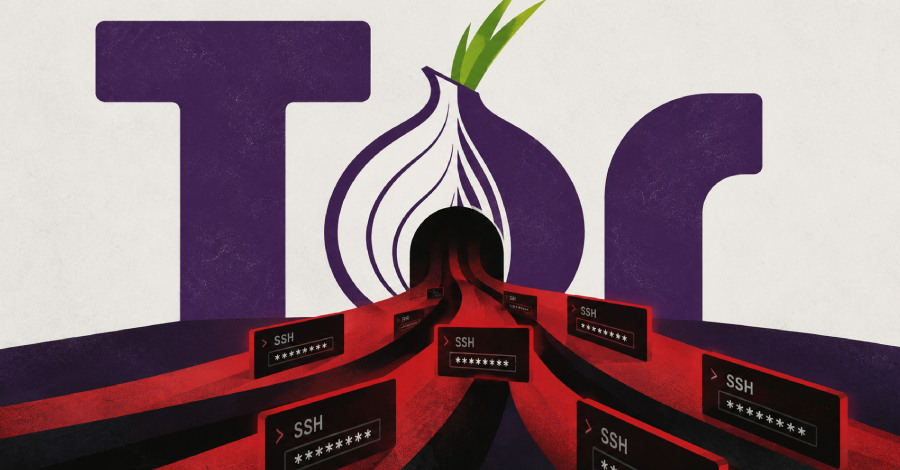
🛑 Attackers hijacked over 300 Tor exit relays to intercept SSH connections and steal login passwords.
A researcher found 333 exits redirecting SSH traffic to 12 interception servers.
The Tor Project has since blocked the affected relays.
Here's how the attack worked: thehackernews.com/2026/10/at…
𝗛𝘂𝗺𝗮𝗻 𝗙𝗶𝗿𝗲𝘄𝗮𝗹𝗹 retweeted
‼️BREAKING: PHP has released its fix for the two leaked flaws, which can let attackers run code on servers without logging in.
"There are no complete mitigations, updating is the only safe choice," PHP says.
Update to PHP 8.5.12, 8.4.27, 8.3.36 or 8.2.35 now.
PHP says Apache with mod_php is most at risk, with a demonstrated exploit that fires before any application code runs.
PHP 8.1 and older get no official update, though PHP has published source backports for 7.4, 8.0 and 8.1.


𝗛𝘂𝗺𝗮𝗻 𝗙𝗶𝗿𝗲𝘄𝗮𝗹𝗹 retweeted

Effective Immediately, all organizations using PHP for their systems are advised to be prepared for an update addressing two critical vulnerabilities. PHP is widely used for web applications. These vulnerabilities often provide a direct path to the server's file system or database. If an immediate update is not feasible, it is recommend that organizations take the system offline until it can be fully mitigated. NSA will follow up shortly with more specific guidance.
𝗛𝘂𝗺𝗮𝗻 𝗙𝗶𝗿𝗲𝘄𝗮𝗹𝗹 retweeted
PHP ships emergency patches for critical PHP2Shell flaws
bleepingcomputer.com/news/se…
bleepingcomputer.com/news/se…

𝗛𝘂𝗺𝗮𝗻 𝗙𝗶𝗿𝗲𝘄𝗮𝗹𝗹 retweeted

🚨 Organizations should immediately patch critical PHP vulnerabilities CVE-2026-109618 and CVE-2026-109619. These vulnerabilities enable unauthenticated #RCE and affect PHP installations serving web requests. Learn more: 🔗 go.dhs.gov/5Hi
𝗛𝘂𝗺𝗮𝗻 𝗙𝗶𝗿𝗲𝘄𝗮𝗹𝗹 retweeted
🚨 Plex2Shell vulnerability chain reportedly exploited against outdated Plex servers
PoC: github.com/code-zm/plex2shel…
A security researcher says an internet-facing Plex honeypot was compromised on October 17 using an exploit chain targeting four recently disclosed vulnerabilities:
• CVE-2026-96652
• CVE-2026-96654
• CVE-2026-96655
• CVE-2026-96656
⠀
The flaws can be chained to achieve unauthenticated remote code execution on affected Plex Media Server installations.
⠀
Observed payloads included an XMRig cryptocurrency miner and a proxy application named “myawesomeproxy,” which could allow attackers to route traffic through compromised residential connections.
⠀
Potential signs of compromise include suspicious child processes launched by Plex Media Server and processes or command lines containing:
• myawesomeproxy
• mylovelyminer
• x12345
• --rig-id
• --donate-level
• proxystream[.]st
⠀
Plex fixed the vulnerabilities in Media Server 1.43.3.10861. Administrators running earlier versions should update immediately and inspect internet-facing Linux and Docker deployments for suspicious processes.
⠀
The exploitation evidence currently comes from one researcher’s honeypot and has not been independently confirmed as a wider campaign.

𝗛𝘂𝗺𝗮𝗻 𝗙𝗶𝗿𝗲𝘄𝗮𝗹𝗹 retweeted
🚨 BREAKING: A Broadcom Wi-Fi bug lets anyone in range run code on routers without the password.
Quentin Kaiser showed it on Proximus, Orange Belgium and VOO routers and estimates ~1.5M in Belgium are exposed, none patched.
The bug dates to 2010. Broadcom won't assign a CVE.


𝗛𝘂𝗺𝗮𝗻 𝗙𝗶𝗿𝗲𝘄𝗮𝗹𝗹 retweeted
🚨 ConnectWise has suspended Cloud Backup and disabled 7 app identities after attackers compromised Microsoft 365 tenants.
Backups and restores are unavailable. Previously issued access tokens may remain valid.
Read: thehackernews.com/2026/10/co…

𝗛𝘂𝗺𝗮𝗻 𝗙𝗶𝗿𝗲𝘄𝗮𝗹𝗹 retweeted
BeyondTrust patches zero-day exploited in attacks since August
bleepingcomputer.com/news/se…
bleepingcomputer.com/news/se…
