

Faculty @uutah. My lab hunts bugs: https://xitter.cf/t.co/R74Wl128A9. Mastodon: [email protected] Bluesky: https://xitter.cf/t.co/6sKvEYpXMF
Salt Lake City, UT
Joined August 2018
- Tweets1.3K
- Following1.6K
- Followers1.3K
- Likes6.3K





Stefan Nagy retweeted
very excited for mythos to tell the sysadmins that exposing the PLCs to the internet is bad

EXCLUSIVE: Sam Altman met with top power utilities to discuss ways to secure the electrical grid.
He also offered one possible solution to the cybersecurity risks: OpenAI’s own cyber services.
politico.com/news/2026/09/10…

Stefan Nagy retweeted

ELI5 why corporate AI companies get to run cyber attacks on real-world systems with zero consequences


Stefan Nagy retweeted

Dyn Taintflow Analysis (DTA) - one of the main components of VUzzer (NDSS 2017) - finally got the re-engineering I'd been postponing for years.
Several ideas had been stuck in my notebook ever since. 1/n
Stefan Nagy retweeted

The fuzzer that found project-zero.issues.chromium… (and a number of issues prior to that as well) is now open-source: crrev.com/c/7580844
It uses pkeys, trap-handling and single-stepping to intercept and mutate in-sandbox reads (see trap-fuzzer.h). Definitely had fun writing it!
Stefan Nagy retweeted

I have a job opening on my team. If you're interested in incident response & software security across a wide range of industries (Laptops, Auto, Mobile, Datacenter) while working with very talented people please apply. DMs are open for questions*.
careers.qualcomm.com/careers…
Stefan Nagy retweeted
ZeroDayBench: Evaluating LLM Agents on Unseen Zero-Day Vulnerabilities for Cyberdefense
arxiv.org/pdf/2603.02297


Stefan Nagy retweeted

TeTRIS uncovered 16 translation bugs across real-world transpilers—12 of them completely new!

Stefan Nagy retweeted
Transcompiler lost in translation? Let TeTRIS uncover all its syntax frustrations!
Happy to share my @ACSAC_Conf paper w/ @snagycs: "TeTRIS: General-purpose Fuzzing for Translation Bugs in Source-to-Source Transpilers"!
PDF:futures.cs.utah.edu/papers/2…
Code:github.com/FuturesLab/TeTRIS

Stefan Nagy retweeted
This is an excellent history of LLMs, doesn't miss seminal papers I know. Reminds you we're standing on the shoulders of giants, and giants are still being born today. gregorygundersen.com/blog/20…
Stefan Nagy retweeted

#FUZZING'26 CALL FOR PAPERS
──────
✨After 5 years, we will be again co-located with NDSS!
🔗 fuzzing-workshop.github.io
📅 11. Dec (Submission)
//cc Marcel Böhme (@mboehme_; MPI-SWS), @RuijieMeng (CISPA), Rohan Padhye (@moarbugs; CMU), László Szekeres (@lszekeres; Google)

Stefan Nagy retweeted

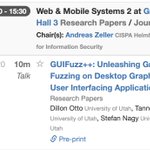
GUIFuzz++ is the first general-purpose fuzzer for desktop GUI software! Fuzzing by translating AFL++ random input into user interaction with GUIs, leading to the discovery of 23 new bugs!
Paper: futures.cs.utah.edu/papers/2…
Source: github.com/FuturesLab/GUIFuz…
Go test some GUIs!

Stefan Nagy retweeted
Curious about fuzzing but don't know where to start? I wrote my first blog post on how to choose your target, build an AFL++-compatible harness, and avoid common pitfalls.
Check it out: gabe-sherman.github.io/2025-…
Stefan Nagy retweeted

I really enjoyed @0xacb's blog post "Fuzzing the Web for Mysterious Bugs".
A great read on creative fuzzing techniques and strange edge cases in web apps.
Highly recommended:
0xacb.com/2022/11/21/recolla…
Stefan Nagy retweeted

Big drama today in the Tor community.
Conrad Rockenhaus, a Tor operator based out of Michigan, United States, was arrested in 2020 after refusing to cooperate with the United States Federal Bureau of Investigation
Rockenhaus, a disabled United States military veteran, ran the fastest Tor node in the United States. He was approached sometime in late 2019 when the FBI requested he allow them arbitrary access to his exit node and allow them to decrypt traffic. He denied their request.
Subsequently, in February, 2020 his home was raided. He was arrested for violating the CFAA (Computer Fraud and Abuse Act). It was alleged that he was a disgruntled ex-employee causing problems at his former place of employment.
Interestingly, to "help resolve the matter", law enforcement requested he decrypt his Tor exit node to prove his innocence (???). After he refused, he was held in a pre-trial detention cell for over 3 years. He was denied bail after law enforcement stated Mr. Rockenhaus used Linux to "access the dark web" and he was "not complying" and not allowing them access to this Tor exit node.
After Mr. Rockenhaus' wife filed an official complaint, and Mr. Rockenhaus was miraculously released, he was raided by the United States Marshal Fugitive Task Force TWO TIMES(???).
They took him out his home, threw him to the ground, beat him, smashed his windows, and threatened to murder his animals.
They are still requesting Mr. Rockenhaus allow them to access his Tor exit node. Mr. Rockenhaus still has not granted them that privilege.
All of this has been captured on home security camera footage. Additionally, his wife has released all court documents.
See subsequent post for more information.
Stefan Nagy retweeted
The new Screen Unknown Callers iOS feature asks callers to describe (and transcribes) why they're calling before you pick up.
I'm curious to see if this decreases folks falling for phone scams as many don't know what a phone scam pretext looks like in transcribed writing either!


Stefan Nagy retweeted

From Zero to QEMU: A journey into system emulation (slide deck)
docs.google.com/presentation…
Credits Antonio Nappa
#infosec #qemu

