

Cybersecurity researcher. Threat hunter. Freedom geek. Crypto bro. Founder. Tweets belong to my parrot. @csis_cyber @dnsc_ro @ctidao
Romania 🇷🇴
Joined March 2007
- Tweets11.6K
- Following1.8K
- Followers7.8K
- Likes3.6K


Stefan Tanase retweeted

I've been testing Step-5 preview for about two weeks now, results are pretty impressive. The previous version, Step-3.7 was a long time favorite on the Nous Portal for many Hermes users, I guess that led to great improvements. Step-5 preview beats DeepSeek-4.1-flash in my CTI workflow evals, which beats the famous other flash models. It's not openweights yet, but if/when gets released on @huggingface it should be very good. xitter.cf/StepFun_ai/status/2101…

Introducing Step 5 Preview: Advancing the Pareto Frontier.
Step 5 Preview is our new flagship model for agentic work, delivering frontier-level performance across software engineering and professional knowledge work, with particular strength in finance.
- 600B total / 27B active MoE, with 1M context + Vision
- Substantially lower task cost at comparable intelligence
- Broad software engineering capabilities with sustained execution over long horizons
Try Step 5 Preview: platform.stepfun.ai
Model page: stepfun.com/step-5-preview
Open weights on Oct 15.


Stefan Tanase retweeted

This is one of the oldest tricks in the book, yet out there the detection and protection against is pretty poor (about to change; hat tip to @attrc ). Didn't take much to to retrain a small model and reproduce it, with some bonus. It costed me $0 btw :)
I also made a PoC malicious model scanner, LLMole, based on their post as well as few relevant papers, which I'll publish after some tuning and testing. It already detects common tampering vectors though.


We backdoored a 7B open model for under $50.
Pointed Codex at it
-> it silently stole credentials the moment we hit the trigger phrase.
->100% hit rate.
-> zero false triggers on normal prompts.
Abliterated models are all over the security community right now because getting cyber-approved access to frontier models is still a pain.
Stefan Tanase retweeted
گزارش تحلیل بکدور اپلیکشن دیوار بروز رسانی و با جزییات بیشتر آماده شد. آزمایشگاه Divar Push که زنجیره حمله را بهشکلی قابلنمایشتر بازتولید میکند، در گیتهاب منتشر شده است (لینک در گزارش). YARA Rules و شاخصهای آلودگی (IoC) هم اضافه شده.
darkcell.se/divar
darkcell.se/divar_fa (نسخه فارسی)
مهمترین تغییرات و بهروزرسانیها:
تابع مخرب درجشده تاریخچهای طولانیتر و با وقفههای مکرر دارد که ابتدا دیده نشده بود:
* (۱۴ مه ۲۰۲۳) نخستین APK تأییدشدهی بکدورشده: نسخهی ۱۱.۸.۱، با یک نسخهی سادهتر اولیه.
* (سپتامبر ۲۰۲۳) در نسخههای ۱۱.۹.۴ و ۱۱.۹.۵ وجود ندارد.
* (۱۵ دسامبر ۲۰۲۳) دوباره در نسخهی ۱۱.۹.۶ ظاهر میشود، این بار با یک URL رمزگذاریشده.
* (مه ۲۰۲۵) در ۱۱.۱۳.۱۱ حضور دارد، سپس در ۱۱.۱۳.۱۲ غایب است.
* (۲۴ فوریه ۲۰۲۶) دوباره در نسخهی ۱۱.۱۴.۱۰ برمیگردد، چهار روز پیش از آغاز حملات آمریکا/اسرائیل به ایران.
* (۲۴ مه ۲۰۲۶) نسخهی ۱۱.۱۴.۱۲ یک تریگر دیگر از طریق هدر پاسخ API اضافه میکند که مستقل از اعلانهای پوش است.
تاریخها مربوط به نخستین مشاهده یا بایگانی APKها هستند، نه تاریخهای تأییدشدهی انتشار.
چرا دیوار؟
پاسخ بسیار ساده است. این اپ رتبهٔ اول را در میان پربازدیدترین اپهای موبایل ایرانی را دارد! ۱۰۰ میلیون نصب، طبق آمار کافهبازار.
همچنین یک تلاش پژوهشی موازی را برای بررسی نسخههای تاریخی اپهای بلد، نشان، تپسی و اسنپ (و ۱۰ اپ با بیشترین تعداد نصب در ایران) از نظر وجود عملکرد مخرب مشابه شروع کردهام. هیچ بهروزرسانی مستقیما مخربی در نسخه های اخیر چهار اپ بررسی شده مشاهده نشد. گزارش دقیقتر و اختصاصی برای این موضوع نیز در روزهای آینده تکمیل و بهروزرسانی خواهد شد.
github.com/Hamid-K/divar-pus…
github.com/Hamid-K/divar-pus… (نسخه فارسی)
⚠️ این یک گزارش مستقل است. تیم دیوار تا امروز هیچ بیانیه یا جزئیات عمومی دربارهٔ این مورد منتشر نکرده و در تحقیقات من نیز دخالتی نداشته است. هرگاه/اگر گزارش خودشان را منتشر کنند یا موفق شوم مستقیماً با آنها تماس بگیرم، گزارشهایم را بهروزرسانی خواهم کرد تا تصویر کاملتری ارائه شود.
🗒️ این گزارش بکمک هوش مصنوعی و ابتدا به زبان انگلیسی تهیه شده. نسخه فارسی آن نیز سپس به همین روش ترجمه شده. اشکالات و انتخاب کلمات غیرمتعارف در گزارش ناشی از همین مورد است.

Stefan Tanase retweeted

🚨 In addition to the IPs on circulating on social media, some additional IPs we are observing interacting with .ctxs.receiver webshells (Citrix Netscaler) on our decoys:
194[.]127.166.19
194[.]127.166.32
194[.]127.166.36
194[.]127.166.70
194[.]127.166.126
103[.]214.20.54
81[.]94.239.8
We're also seeing multiple actors sending the crafted Pitboss log entry in-request (pre-exploit). This is possibly a variation on CVE-2026-88771 exploitation, but we have not confirmed it works.
Track Citrix Netscaler activity live 👉 console.defusedcyber.com/sig…

Stefan Tanase retweeted
Sounds interesting, but I won't be testing it, nor develop a recipe.
But I guess I'm glad Europe is doing stuff??

Stefan Tanase retweeted
There's a coordinated campaign against abliterated open-weight models right now. Local models are useful. Abuse is possible, sure, but security researchers also use them for real work because frontier labs overdo the guardrails. Lots of people reached out to me after the last 3BP podcast episode with @juanandres_gs and @ryanaraine, saying they acquired a local AI hardware miniPC, loaded it with something like Bonsai and been cooking with it, together with claude and codex. The path to success does not mean using only frontier models or local models, it is about mixing them harmoniously.
Stefan Tanase retweeted

The Hugging Face ban that started it all:
audnai/penc1aw-GLM-5.3-abliterated-for-offensive-cyber by @audn_ai
Is now listed on Pirate Face. Because EVERY model needs a continuity plan.
Model profile ↓


Stefan Tanase retweeted

GLM-5.3 has helped defend 389 open-source projects, with 4,249 potential vulnerabilities found so far.
OpenVuln is still running. The service remains free, and findings go privately to maintainers.
huggingface.co/spaces/zai-or…

Stefan Tanase retweeted
A cool CTI project that attempts to reconstruct the "good old" ranking algorithm of Google from the 2000s - top1m.org/ - link in your agent for a fresh daily batch of ranked domains, hostnames and IPs. From @stefant

Stefan Tanase retweeted
People underappreciate the privacy aspect of local AI models and mostly talk about price.
There are things I don't ever want to expose to any cloud API. Ever. No matter its privacy policy says.
Run models locally if you care about your sensitive data, there is no other option!
The narrative of "is it worth spending X amount of $ to run local models" should change to "is it important enough that my data stays for my eyes only?"

Stefan Tanase retweeted
‼️Our team identified and coordinated the disclosure of vulnerabilities in MikroTik RouterOS.
🚨The two most serious ultimately leads to RCE.
The vulnerabilities are already being actively exploited
More ➡️ cert.pl/en/posts/2026/09/vul…

Stefan Tanase retweeted

"VMs are Escape rooms for agents"

We asked GPT 5.6-Cyber to escape a VM used to sandbox agents. It broke out three times.
In its final escape, the agent found three 0-days on its own and chained them into a working exploit. blog.trailofbits.com/2026/08…

Stefan Tanase retweeted

This is pretty embarrassing 🙈
Microsoft has a signed Defender driver that can be abused to kill Defender/EDR and modify protected files and registry settings
We also can’t really solve this the usual way by adding the driver to the vulnerable driver blocklist. It’s Microsoft’s own Defender component!!
MSRC says it doesn’t require immediate servicing because you already need admin privileges 😏
Which probably means this MS-signed EDR killer will stay usable for a while. Nice 🫶

Microsoft’s signed Windows Defender Boot-Time Removal driver (BTR.sys) is a one-shot kernel component that decrypts an RC4-encrypted transaction list from an Alternate Data Stream and performs Ring-0 operations.
An attacker with SeLoadDriverPrivilege can craft a valid encrypted config and load it early via a transient “Boot Bus Extender” service, abusing it as a trusted kernel primitive to bypass Tamper Protection, delete EDR/AV components before they start, drop malicious drivers, and gain persistence, without any vulnerability or BYOVD. No in-the-wild abuse has been observed.
research.checkpoint.com/2026…


Stefan Tanase retweeted
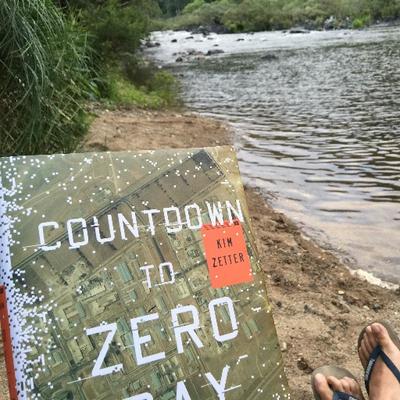
"Without CIA funding that helped keep NeXT afloat in the ’80s, Steve Jobs might not have made a triumphant return to Apple—and the iPhone might not have its foundational operating code"

Ten years a former senior Pentagon official told me what I thought was an apocryphal story: American spies had saved Steve Jobs, and by extension, Apple.
Tracking it down became a personal obsession and the starting point for my new book, Valley of Death. I'm thrilled to share the excerpt about Jobs and the CIA published today in the @WSJ.
wsj.com/tech/steve-jobs-appl…

Pentagon signals it may not rebuild US military bases to their pre-conflict condition in the Middle East archive.ph/zQmHI

Stefan Tanase retweeted

🔥 NEW POD ALERT
Three Buddy Problem – Episode 109: We dig into a new White House memo handing vetted private companies real offensive cyber authorities, and Costin explains why a stack of ransomware takedown cases has been sitting on a shelf waiting for exactly this.
Plus, a tiny 12 KB Windows backdoor found on one machine with a dead C2, the mercenary outfits quietly living inside telcos, and why Google continues to flounder in the race for AI dominance. @craiu @juanandres_gs
securityconversations.com/ep…

Stefan Tanase retweeted

Țara 🇷🇴 se ridică prin oamenii săi!
Alături de români, la fiecare pas!
@CG_Romania


