

Easy uptime monitoring and automated website testing. We check your website 300 times a day. How often do you? #UptimeMonitoring #WebsiteTesting
- Tweets7K
- Following6
- Followers1K
- Likes422





ALT Ripe or Rotten monitoring trivia card revealing the answer. The statement "CAPTCHA is the #1 problem screen reader users run into on the web." is marked True, with False greyed out. Caption: WebAIM's screen reader survey ranked CAPTCHA the most problematic item by a wide margin, ahead of broken menus and missing alt text.

ALT Ripe or Rotten monitoring trivia card. True-or-false statement: "CAPTCHA is the #1 problem screen reader users run into on the web." Two unselected answer buttons below, True and False. Testomato logo at the bottom.


ALT Ripe or Rotten monitoring trivia card revealing the answer. The statement "Bots solve CAPTCHAs more accurately than humans do." is marked True, with False greyed out. Caption: in research tests, bots solved CAPTCHAs with 85–100% accuracy while humans managed 50–85%. Testomato logo at the bottom.

ALT Ripe or Rotten monitoring trivia card. True-or-false statement: "Bots solve CAPTCHAs more accurately than humans do." Two unselected answer buttons below, True and False. Testomato logo at the bottom.


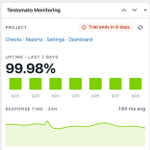
ALT Testomato Monitoring dashboard widget showing 7-day uptime and a 24-hour response-time chart.

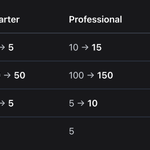
ALT Table showing new plan limits: Starter domains 3→5, checks 40→50, team members 3→5; Professional domains 10→15, checks 100→150, team members 5→10; Business domains unlimited→100, checks 450→600, team members 15→25, status pages unlimited→25. Status pages unchanged at 1 for Starter and 5 for Professional. Enterprise stays unlimited across all four.

ALT Testomato CSP Generator form: build-from-live-URL option, website URL field with testomato.com entered, CSP type selector (Allow-list, Strict—Nonce, Strict—Hash) with Strict—Nonce selected, and a Generate button.


ALT Ripe or Rotten monitoring trivia card. True-or-false statement: "The SSL protocol has been deprecated for over a decade — but the certificates are still called SSL certificates." Two unselected answer buttons below, True and False. Testomato logo at the bottom.


ALT Ripe or Rotten monitoring trivia card revealing the answer. The statement "The SSL protocol has been deprecated for over a decade — but the certificates are still called SSL certificates." is marked True, with False greyed out. Caption: the certificate proves identity and works with either protocol, but it's TLS, not SSL, doing the actual encryption today. Testomato logo at the bottom.
ALT Ripe or Rotten monitoring trivia card revealing the answer. The statement "The SSL protocol has been deprecated for over a decade — but the certificates are still called SSL certificates." is marked True, with False greyed out. Caption: the certificate proves identity and works with either protocol, but it's TLS, not SSL, doing the actual encryption today. Testomato logo at the bottom.

ALT Ripe or Rotten monitoring trivia card. True-or-false statement: "SSL certificates can't be valid for more than 200 days." Two unselected answer buttons below, True and False. Testomato logo at the bottom

ALT Ripe or Rotten monitoring trivia card revealing the answer. The statement "SSL certificates can't be valid for more than 200 days." is marked True, with False greyed out. Caption: the cap fell from 398 to 200 days in March 2026 and hits 47 days by 2029, so renewals are getting too frequent to track by memory. Testomato logo at the bottom.
ALT Ripe or Rotten monitoring trivia card revealing the answer. The statement "SSL certificates can't be valid for more than 200 days." is marked True, with False greyed out. Caption: the cap fell from 398 to 200 days in March 2026 and hits 47 days by 2029, so renewals are getting too frequent to track by memory. Testomato logo at the bottom.