

Security enthusiast aka Cyber Security Researcher
Dhaka, Bangladesh
Joined March 2020
- Tweets599
- Following631
- Followers4.2K
- Likes9K


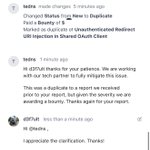



From a normal Rxss to account takeover to rce in any instance , It can be a cve
Alhamdulillah
#Account_takeover ,#RCE , #Rxss

Imamul Mursalin retweeted

We are working non-stop to resolve this issue. Binance will cover all losses.
As a precaution, all deposits and withdrawals are temporarily suspended while our team conducts security checks, freezes funds, and works with law enforcement.
We are working around the clock and will share a full post-mortem once the investigation is complete. Please rely only on official Binance channels for updates.
This is an industry-wide effort, and we are grateful to partners across the ecosystem who have moved quickly to help freeze affected assets.
We will continue to share verified updates through official Binance channels. User funds are safe.


one of my finest finding till now , zero interaction, direct authorisation code theft leads full account takeover

40
1,549


Hi @Hacker0x01 what is this? As a hunter how I can know the internal policy? This issue was reported on july 2026, And currently on resolved state . And I was able to bypass that fix. Hackerone triager zeus closed it by saying internal policy. It’s seems like joke .

4
81
8,260


Companies should value security researchers who find and responsibly disclose these issues instead of dismissing the impact after fixing them.

I reported an OAuth flaw back in February that could lead to account takeover of users’ connected accounts.
After the issue was fixed, the response was essentially “there’s no impact” because the believe the flaw is on the OAuth provider side.

1
3
442