




Pinned Tweet
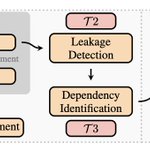
After an embargo of 256 days, I'm happy to reveal our newest work: we present TREVEX, a black-box CPU fuzzer that detects transient execution vulnerabilities in an automated manner. Running TREVEX on AMD, Intel, and Zhaoxin CPUs discovered multiple new CPU vulnerabilities!

I'm very happy how this project together with @fth0mas , @LTrampert , @Rayiizzz, and @misc0110 turned out!
Blog post about FP-DSS: roots.ec/blog/fpdss/
Tool and code: github.com/cispa/trevex
TREVEX paper: roots.ec/publications/weber2…
AMD advisory (FP-DSS): amd.com/en/resources/product…
AMD advisory (FPVI variant): amd.com/en/resources/product…

More Info + Exploits: stackwarpattack.com/
AMD's Fix: amd.com/en/resources/product…
Daniel Weber retweeted

For more details on the discovery process and our findings, we refer to our research paper, which is published at USENIX Security 2026.
paper: stackwarpattack.com/
github: github.com/cispa/StackWarp
\cc Tristan Hornetz, @weber_daniel, @fth0mas, @misc0110
Daniel Weber retweeted
Today we reveal StackWarp: a new CPU vulnerability exploiting a synchronization bug in AMD’s stack engine across Zen 1–5 CPUs. It enables deterministic manipulation of Confidential VM's stack pointer, allowing RCE and privilege escalation via both control- and data-flow hijacking
Thrilled to present our (Lukas G., @LTrampert ,Youheng L, @jovanbulck ,@misc0110) newest paper ("SCASE: Automated Secret Recovery via Side-Channel-Assisted Symbolic Execution") at #USENIX Security this week!
1/n
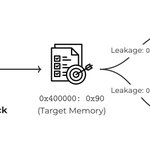
Using Athena, you can create PoC attacks without needing to care about your target's implementation or memory layout!
Paper: d-we.me/papers/scase_usenix2…
Code: github.com/cispa/scase
PS: I'm available for hire soon, so ping me if you're at USENIX and know exciting opportunities!
Automation is the key to further bridge the gap between academic research and practical side-channel attacks! Thus, we automate side-channel attacks by leveraging a symbolic execution engine.
Heading to Black Hat Asia now! @LTrampert and I will give a briefing about deanonymizing users not only on the web but also in their email clients! #BHASIA
Daniel Weber retweeted

Here comes another fantastic talk—get ready!
"Beauty at a Cost: Privacy Implications of CSS on the Web and in Emails.“ by @LTrampert and @weber_daniel.
🌐 #RuhrSec Website
ruhrsec.de/2025/
📖 RuhrSec Program
ruhrsec.de/2025/index.html#p…
#itsecurity #itsicherheit

Daniel Weber retweeted

github.com/google/security-r…
Our newest research project is finally public! We can load malicious microcode on Zen1-Zen4 CPUs!

Super excited to present our (L. Niemann, @____salmon____, @jan__reineke, @misc0110) newest paper at #ACSAC2024! We show how modern CPU hardware can be leveraged to stop side-channel attacks almost instantly (~200 CPU cycles)!
Code/Paper: github.com/cispa/IRQGuard

In "No Leakage Without State Change", we propose to shift away from monitoring entire systems for malicious processes towards enabling high-profile processes to monitor their own behavior to detect the influences of microarchitectural attacks.
Details: misc0110.net/files/irqguard_…

Daniel Weber retweeted

The first #ACSAC2024 #PaperPreview today is by Weber et al., who show that HW features can be used to stop #SideChannel #attacks almost immediately by monitoring the victim: openconf.org/acsac2024/modul…
#cybersecurity
@weber_daniel @____salmon____ @jan__reineke @misc0110 @cispa

ALT Weber et al.'s "No Leakage Without State Change: Repurposing Configurable Cpu Exceptions To Prevent Microarchitectural Attacks"
Daniel Weber retweeted

Excited to announce the release of the Rapid Data Analysis (RDA) framework! RDA streamlines side-channel analysis with plotting, processing, and analysis tools—usable directly from the terminal or in scripts. Check it out: github.com/0xhilbert/rda #SideChannel

Congrats! It was a pleasure working with you!

