





Pinned Tweet
Imagine meeting @garyvee @DeezeFi @CryptoKaleo and @Jruffhouse in the same day. #NFTNYC has been a fucking vibe dude.


Agree. The check needs:
- RLS on every table, policies scoped to the user, not `true`
- no service_role key in the bundle
- Stripe webhook signature verified
- edge functions check who's calling
- every table has a migration
rescueaudit.dev/sample
teapaw.org/petergyang/status/2094…

Every vibe-coded app should pass a security check for exposed personal data, malicious packages, and more before launch.
From @amoljain_:
"In the past, you would contract a security team, pay them a lot of money, wait 1-2 weeks, and get back a report you then had to build on.”
We built @Replit Security Center to runs a deep scan with different scenarios, testing to make sure it can detect security problems and surface them proactively."
📌 Watch the full episode here: youtu.be/JAh8Wv1lQrw
2
2
75
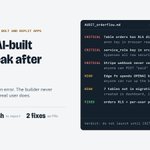
I audit apps built with Lovable, Bolt and Replit. The same 5 failures show up almost every time, and the builder never flags them because nothing throws an error.
What I keep finding 👇

1
2
312
Sample report with real findings, names changed, and both fixes as code: rescueaudit.dev/sample
If you're a week from launching something built with an AI tool, read it before you take a payment. It's free.
1
8
Zero customers so far. I'll post the numbers here as they happen, including nothing. Building this in public.
rescueaudit.dev
4


I click on a couple $BOME posts and now my whole timeline is shit coins.
Are these the currencies of hell?
1
180
I know my profits aren't massive like every other crypto influencer but throwing $20 into meme coins here and there has been fun. $BOMO next?

184